
cve-lfi-lab
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
ctfeducationincident-response+5
thecyberfairy/cve-lfi-labA hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
 sirbuvladste/bind-9-cache-poisoning-poc---cve-2025-40778
Proof of Concept for CVE-2025-40778: BIND 9 DNS Cache Poisoning via unsolicited Additional Section records.
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 nullwhisper/cve-2026-14840
Proof-of-concept exploit for a WordPress plugin vote-limit bypass using spoofed X-Forwarded-For headers; ships a Docker lab to validate…
 daemon-404/poc-cve-2025-24071
Python PoC for CVE-2025-24071 that crafts a .library-ms file to coerce Windows Explorer into leaking NetNTLMv2 hashes over SMB for capture and…
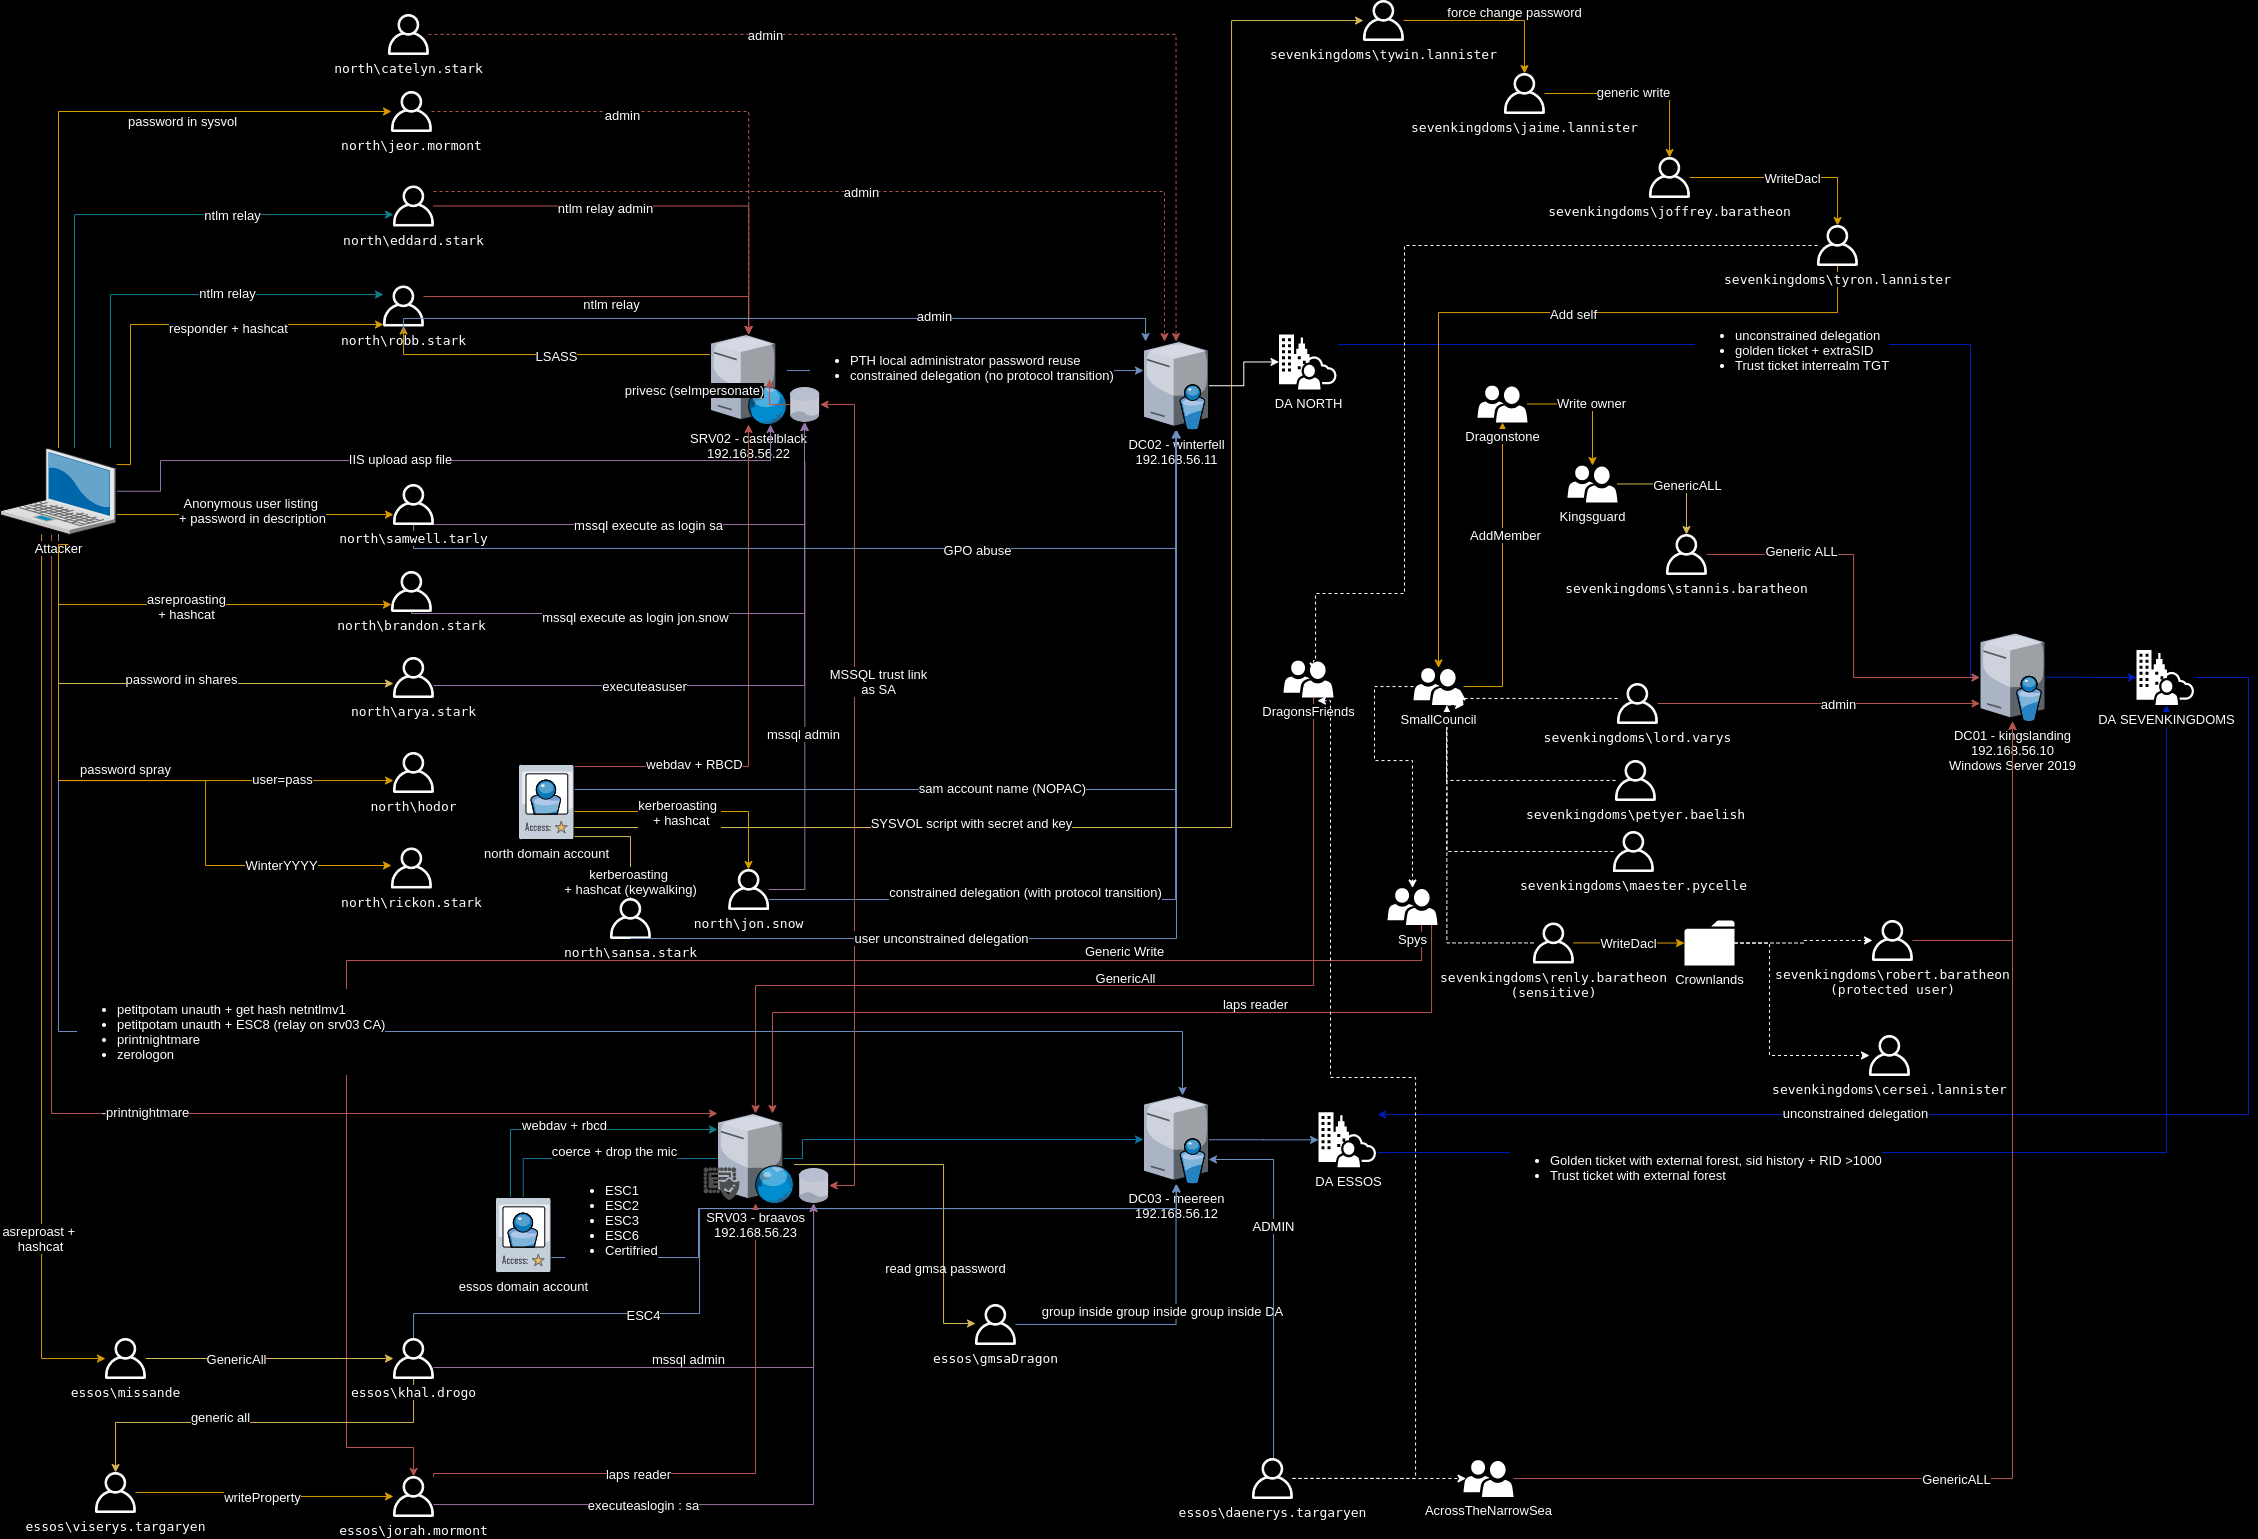 lkarlslund/deploy-goad
Script to install prerequisites for deploying GOAD on Ubuntu Linux 22.04
 americooo/pentest-writeups
Kioptrix Level 1 writeup - CVE-2003-0201 Samba trans2open
 zeyad-azima/cve-2022-1388
F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB
 kondordevsecuritycorp/cve-2026-34197
Exploit for Apache ActiveMQ RCE via Jolokia API (CVE-2026-34197) with command output capture, mass scanning, and auto-exploitation.
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
 cyberharsh/shellbash-cve-2014-6271
Docker-based lab environment for exploiting Shellshock (CVE-2014-6271) via CGI scripts, demonstrating remote command injection through crafted HTTP…