
PwnzzAI
 owasp/pwnzzai
Hands-on AI security learning platform with intentionally vulnerable LLM applications. Explore OWASP Top 10 for LLMs through interactive pizza shop…
ai-securityctfcurated-resources+6
7329 days ago
owasp/pwnzzaiHands-on AI security learning platform with intentionally vulnerable LLM applications. Explore OWASP Top 10 for LLMs through interactive pizza shop…
 dhmosfunk/http3onsteroids
PoC and lab environment for CVE-2023-25950: HTTP request smuggling via malformed header fields in HAProxy's HTTP/3 implementation, enabling DoS and…
 abhisek3122/cve-2025-23167
Working exploit for CVE-2025-23167 – HTTP request smuggling in vulnerable Node.js 20.x versions before 20.19.2
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 ianxtianxt/cve-2015-7501
Educational lab for understanding Java deserialization vulnerabilities with PoC exploits for JBoss CVEs, gadget chain analysis, and a vulnerable HTTP…
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 swabird/cve-2025-7775-poc
Hypothetical RCE proof-of-concept for NetScaler ADC/Gateway. Simulates command injection via HTTP POST for detection validation, IR drill training,…
 emaar1x/cve-2021-41773
Educational Docker lab for Apache HTTP Server 2.4.49 path traversal and RCE (CVE-2021-41773) with CVE research, PoC exploit, testing evidence, and…
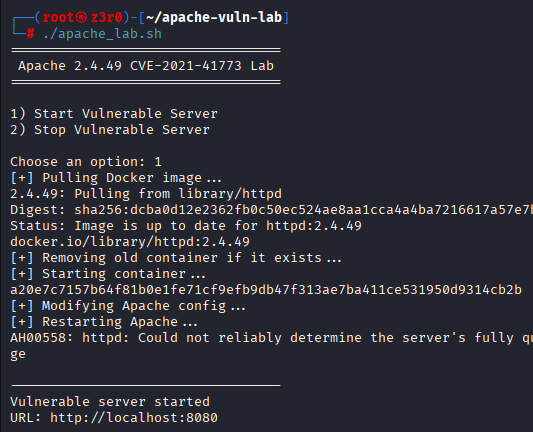 zubairahm3d/apache-cve-2021-41773-lab
Vulnerable Docker lab and exploit for Apache HTTP Server 2.4.49 path traversal vulnerability (CVE‑2021‑41773)
 mightysai1997/cve-2021-41773-i-
Proof-of-concept exploit for Apache HTTP Server 2.4.49 path traversal (CVE-2021-41773) with Docker-based lab environment and patch diff analysis.
 mightysai1997/cve-2021-41773-poc
Proof-of-concept exploit for Apache HTTP Server path traversal vulnerability CVE-2021-41773, with Docker-based demonstration environment for security…
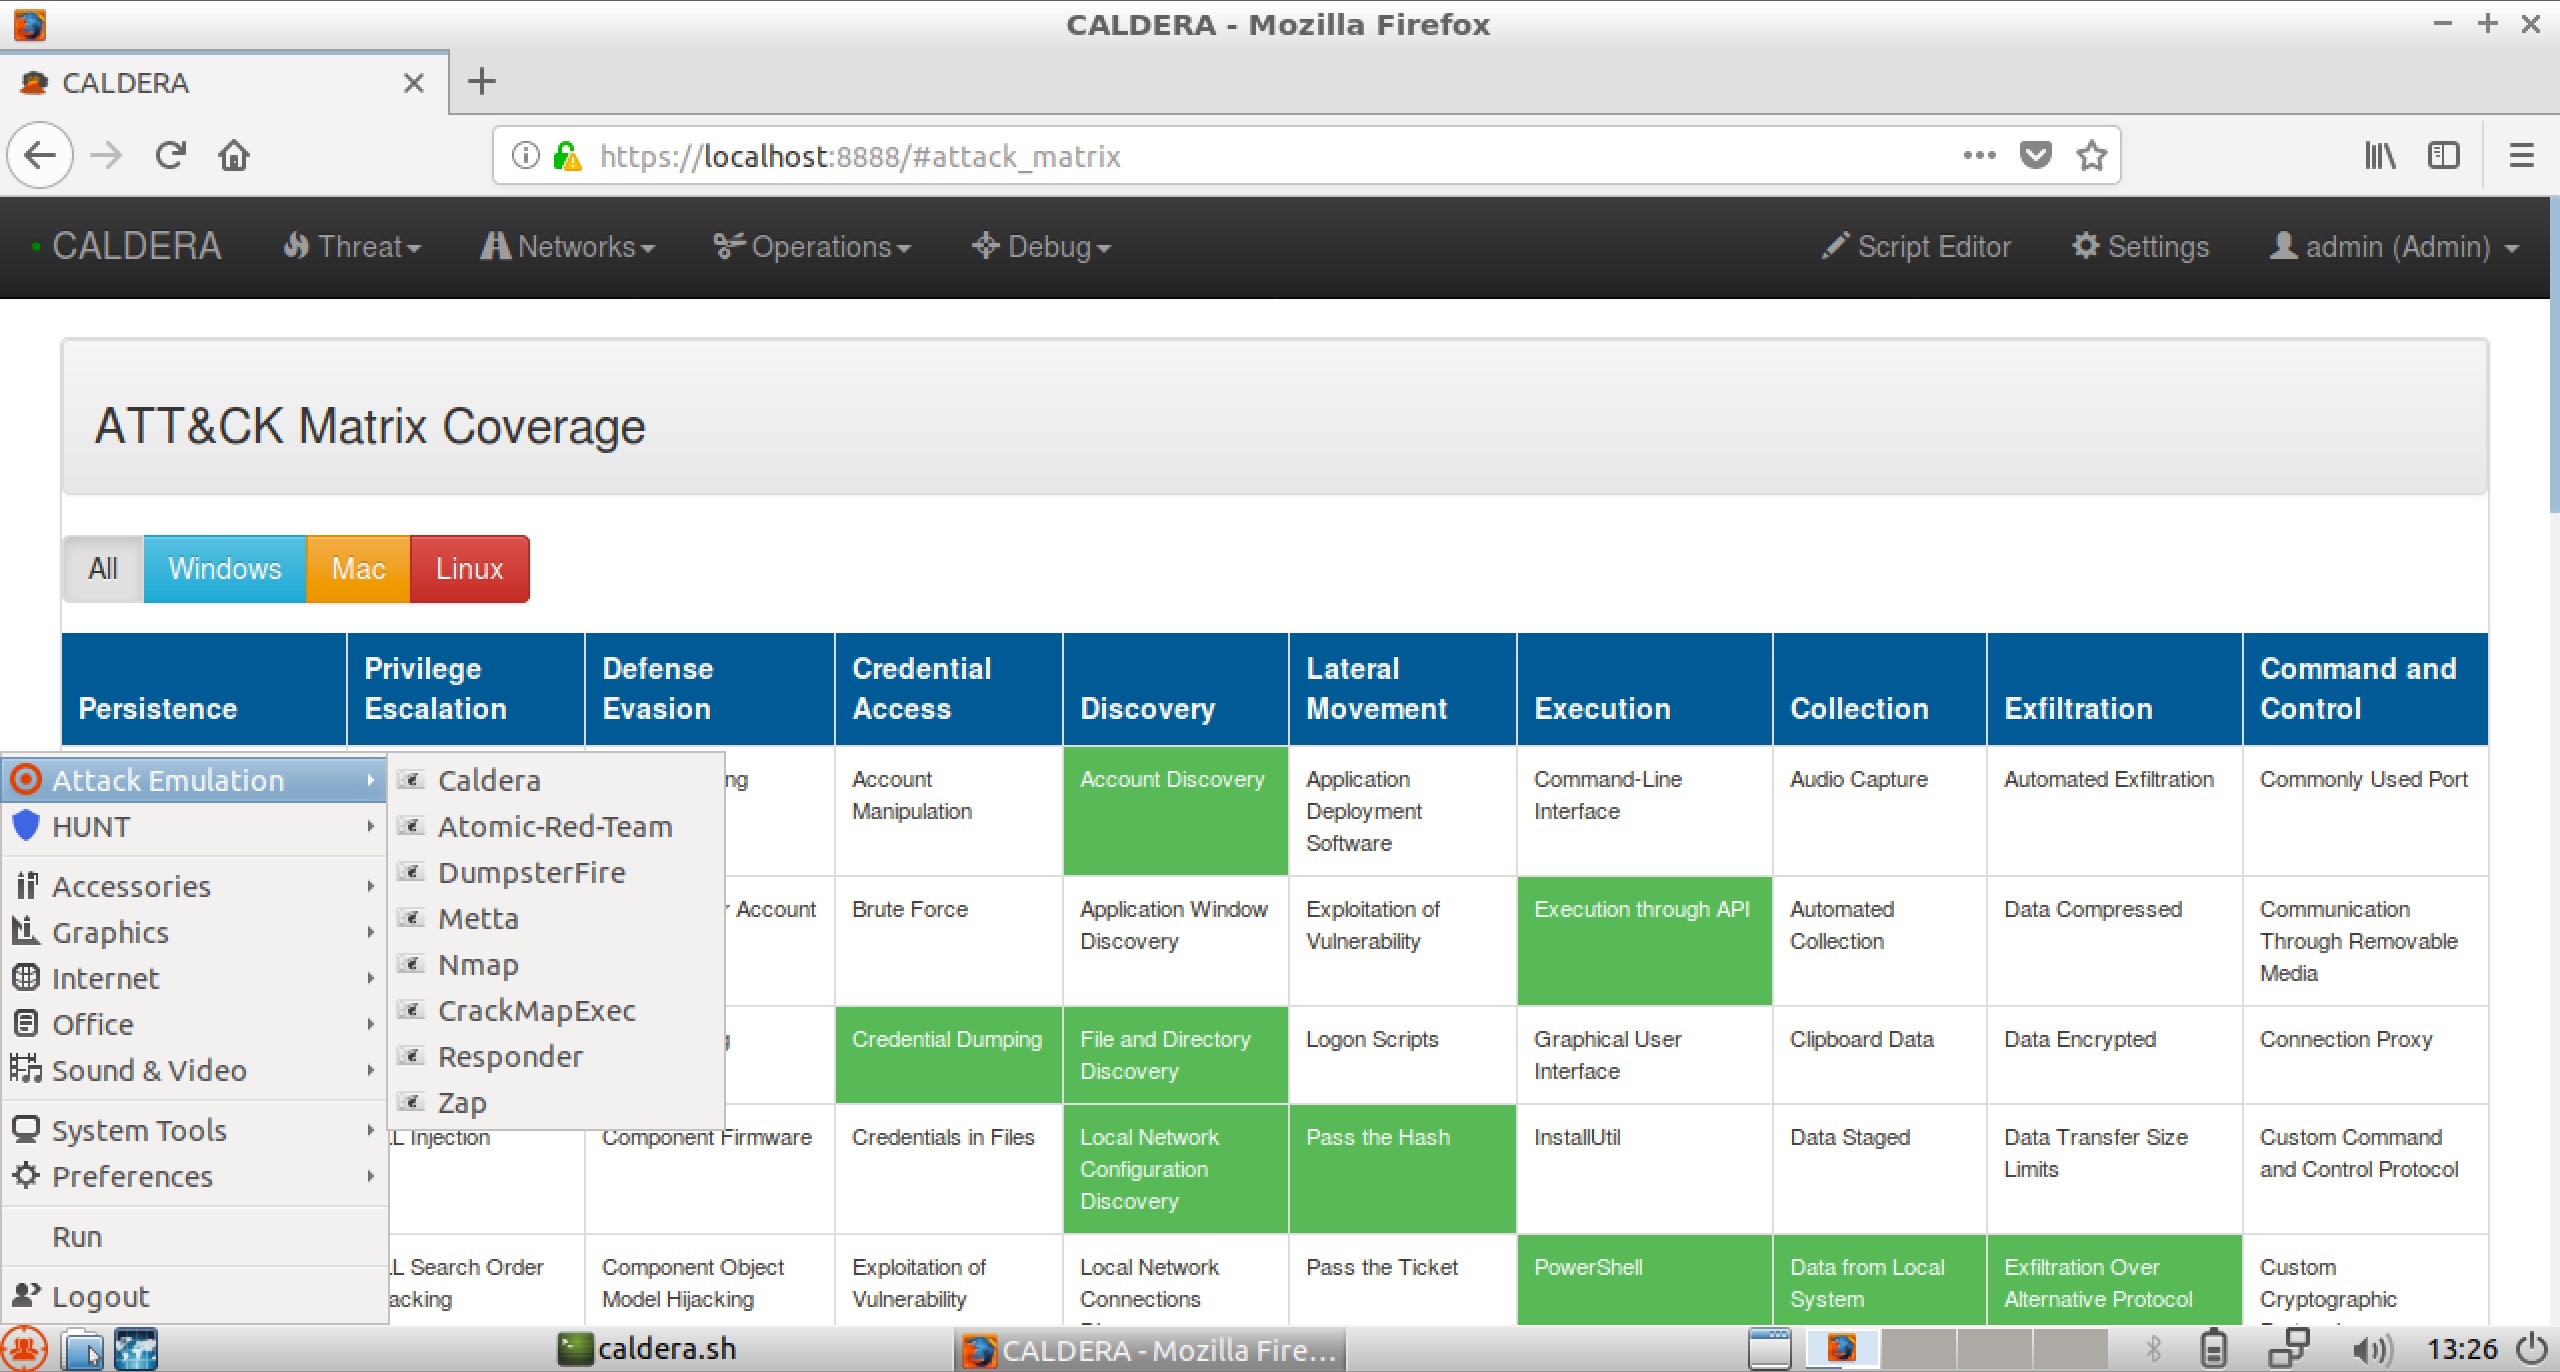 redhuntlabs/redhunt-os
Virtual Machine for Adversary Emulation and Threat Hunting
 joe-shenouda/awesome-cyber-skills
A curated list of hacking environments where you can train your cyber skills legally and safely
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 jas9reet/cve-2021-42013-lab
Docker-based lab environment for exploiting Apache HTTP Server 2.4.50 path traversal and RCE vulnerability (CVE-2021-42013) with automated exploit…
 layarkacasiber/cve-2021-41773
Docker-based lab environment for CVE-2021-41773 (Apache HTTP Server 2.4.49) path traversal and RCE exploitation with step-by-step setup instructions.
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 eunho87/cve-2021-42013
Proof-of-concept exploit for CVE-2021-42013 Apache HTTP Server path traversal and remote code execution vulnerability, with Docker-based lab…