
POC_CVE-2026-35037
 fineman999/poc_cve-2026-35037
Local isolated reproduction lab for CVE-2026-35037, an unauthenticated SSRF vulnerability in Ech0's GET /api/website/title endpoint. Includes Docker…
educationexploitationlabs-practice+3
fineman999/poc_cve-2026-35037Local isolated reproduction lab for CVE-2026-35037, an unauthenticated SSRF vulnerability in Ech0's GET /api/website/title endpoint. Includes Docker…
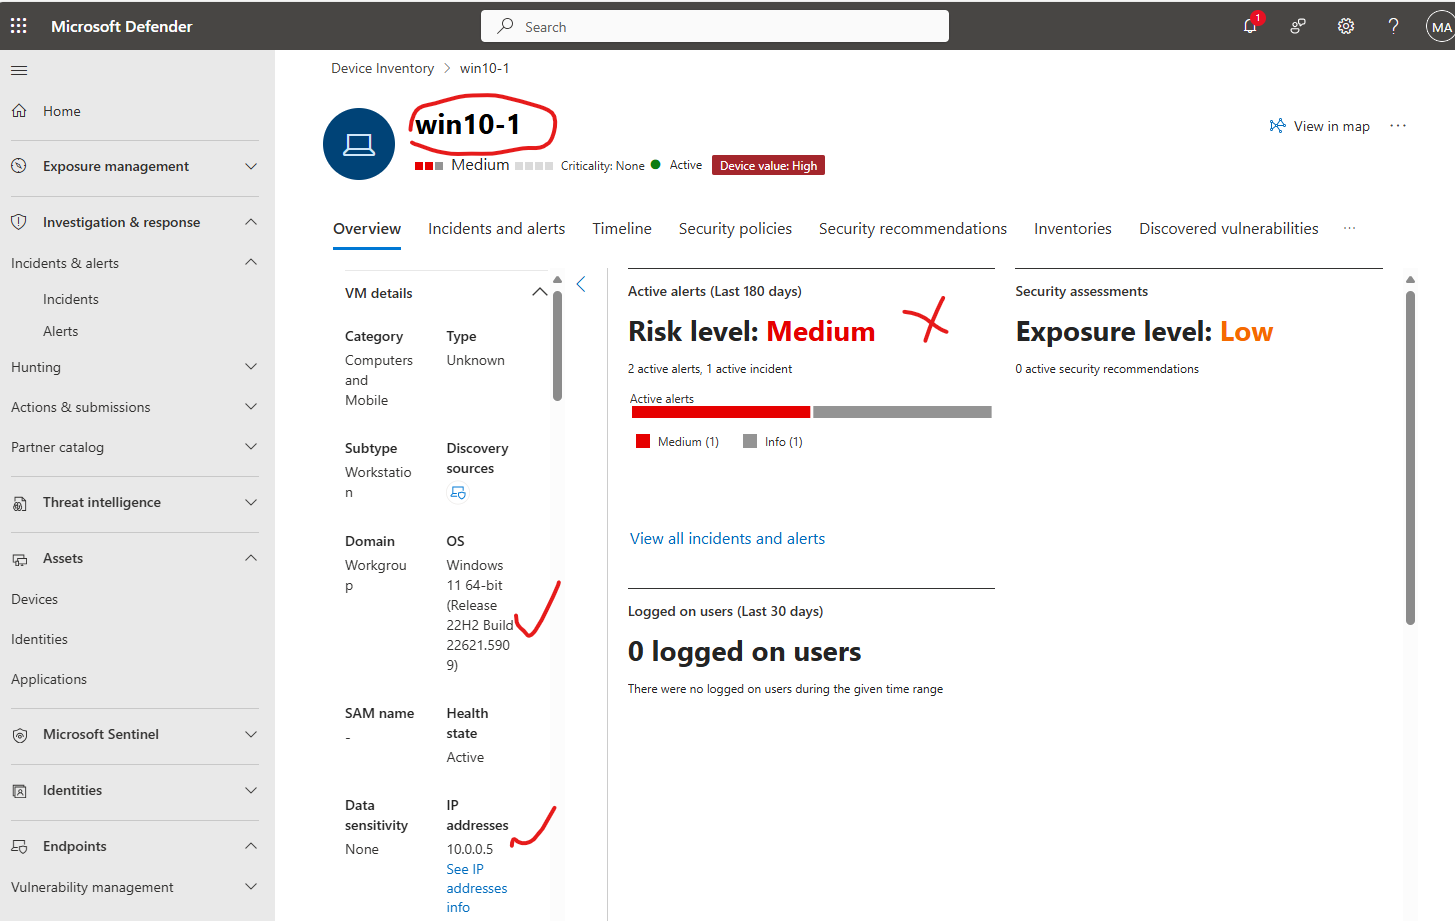 kamalideenak/microsoft-defender-for-endpoint-deployment-on-windows-10-11-device
This repository documents how deployment of Microsoft Defender for Endpoint on a Windows 11 device, including onboarding via local script, enabling…
 kasunpriyashan/y2s1-project-linux-exploitaion-using-cve-2016-5195-vulnerability
Educational Linux privilege escalation exploit targeting CVE-2016-5195 (Dirty COW) to demonstrate kernel vulnerability exploitation and root access…
 sjitech/test_struts2_vulnerability_cve-2017-5638
test struts2 vulnerability CVE-2017-5638 in Mac OS X
 malone5923/cve-2018-6574-go-get-rce
CVE-2018-6574: go get RCE solution for pentesterlab challenge
 astrowmist/poc-cve-2016-10033
Proof Of Concept for the CVE-2016-10033 (PHPMailer)
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
 athena-os/athena
Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 instantbox/instantbox
📦 Get a clean, ready-to-go Linux box in seconds.
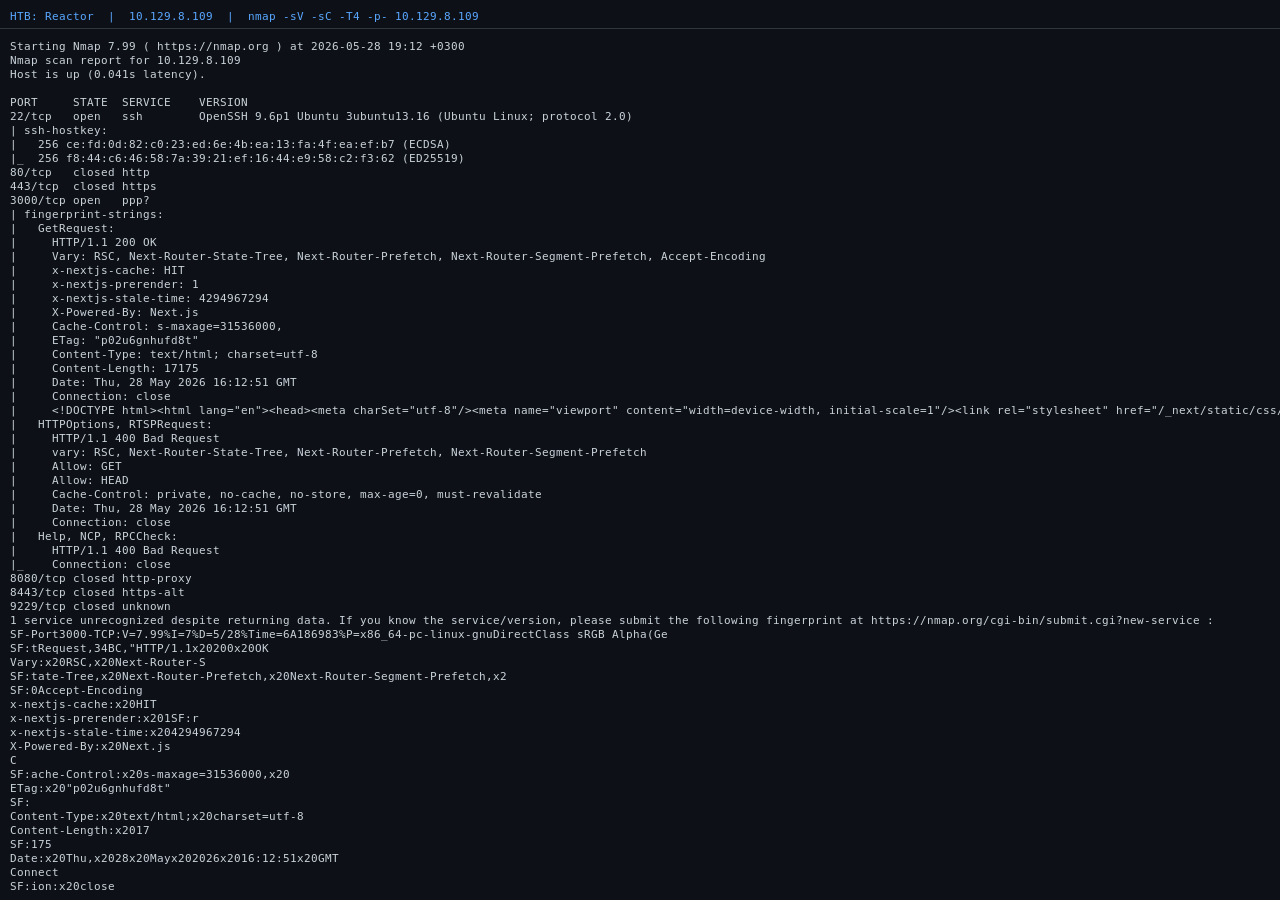 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 tulhan/commons-text-goat
An intentionally vulnerable webapp to get your hands dirty with CVE-2022-42889.
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.