
CVE-2022-1388
 zeyad-azima/cve-2022-1388
F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB
exploitationlabs-practicepenetration-testing+3
13
zeyad-azima/cve-2022-1388F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 walnutsecurity/cve-2021-42013
cve-2021-42013.py is a python script that will help in finding Path Traversal or Remote Code Execution vulnerability in Apache 2.4.50
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
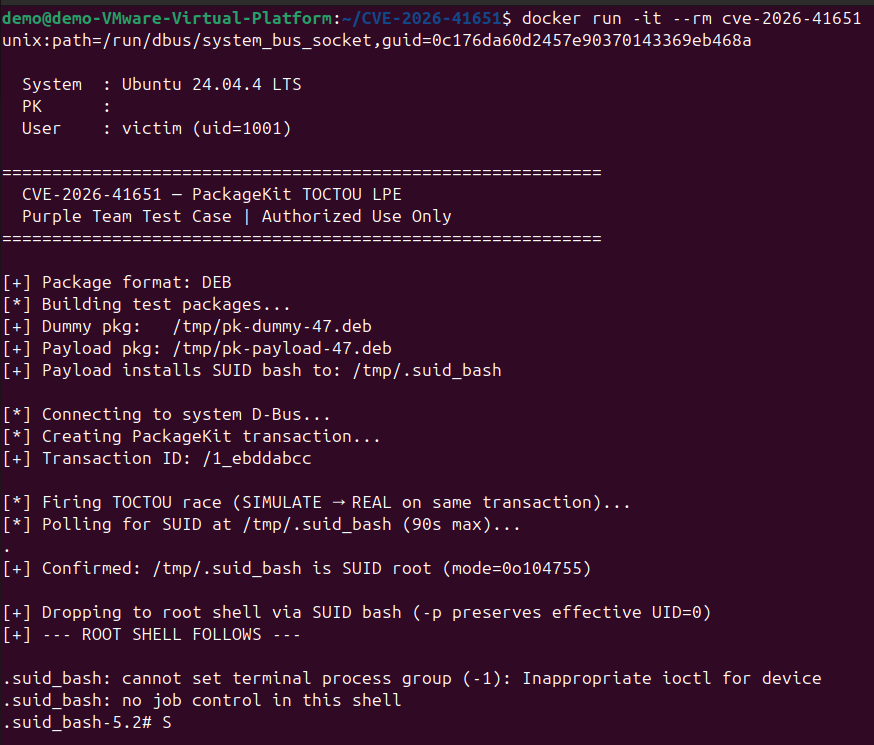 baph00met/cve-2026-41651
Proof-of-concept exploit for CVE-2026-41651, a PackageKit TOCTOU local privilege escalation, with technical analysis, detection logic, and…
 abraxas/pfsense-logs-filter-xss
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - XSS - logs filter JSON as HTML
 abraxas/pfsense-unbound-acl-crlf
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - Unbound ACL CRLF include
 hassham1/cve-2026-12227-visualcomposer-lfi-poc
Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…
 hassham1/cve-2026-89274-wp-recipe-maker-poc
Docker validation lab and Python PoC for CVE-2026-89274, proving arbitrary shortcode execution in WP Recipe Maker <= 10.8.1 via rating-comment…
 nextco/wordpress-cve-2026-87902
Proof-of-concept exploit for CVE-2026-87902, an unauthenticated WordPress Core LFI leading to RCE via pearcmd.php, with a Docker lab and curl/Python…
 abraxas/pfsense-voucher-expire-sqli
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - SQLi - voucher_expire WHERE
 abraxas/opencart-reward-free-checkout
Proof-of-concept exploit and lab for an OpenCart 4.1.0.4 reward points plus Free Checkout payment bypass, letting an authenticated customer keep…
 abraxas/gitlab-webhook-0net-ssrf
Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…
 abraxas/gitea-hostmatcher-0000-ssrf
Proof-of-concept lab demonstrating an authenticated SSRF in Gitea's hostmatcher allow-list, where a webhook to http://0.0.0.1 reaches loopback…
 abraxas/stirling-storage-folder-idor
Stirling-PDF v3.2.0 - High - Remote - IDOR - processing-folder storage root lists and overwrites peer PDFs
 abraxas/gitea-git-redir-ssrf
Proof-of-concept and lab for an authenticated SSRF in Gitea's repo migrate endpoint, where git follows HTTP redirects into loopback git HTTP and…
 abraxas/gitlab-gitea-import-ssrf
GitLab - High - Gitea HTTPS import SSRF - UrlBlocker pin drop
 abraxas/phpmyadmin-setup-validate
phpMyAdmin 5.2.3 - High - Remote - leftover - setup/validate still reachable