

CVE-2026-43494-PinTheft-PoC
 letsr00t/cve-2026-43494-pintheft-poc
Proof-of-concept for CVE-2026-43494 (PinTheft): Linux kernel local privilege escalation exploiting an RDS zerocopy reference-count bug with io_uring…
binary-exploitationctfeducation+4
letsr00t/cve-2026-43494-pintheft-pocProof-of-concept for CVE-2026-43494 (PinTheft): Linux kernel local privilege escalation exploiting an RDS zerocopy reference-count bug with io_uring…
 jayhutajulu1/cve-2026-43494-pintheft-poc
Proof-of-concept for CVE-2026-43494 (PinTheft): Linux LPE via RDS zerocopy refcount bug + io_uring fixed buffers → SUID page-cache overwrite.…
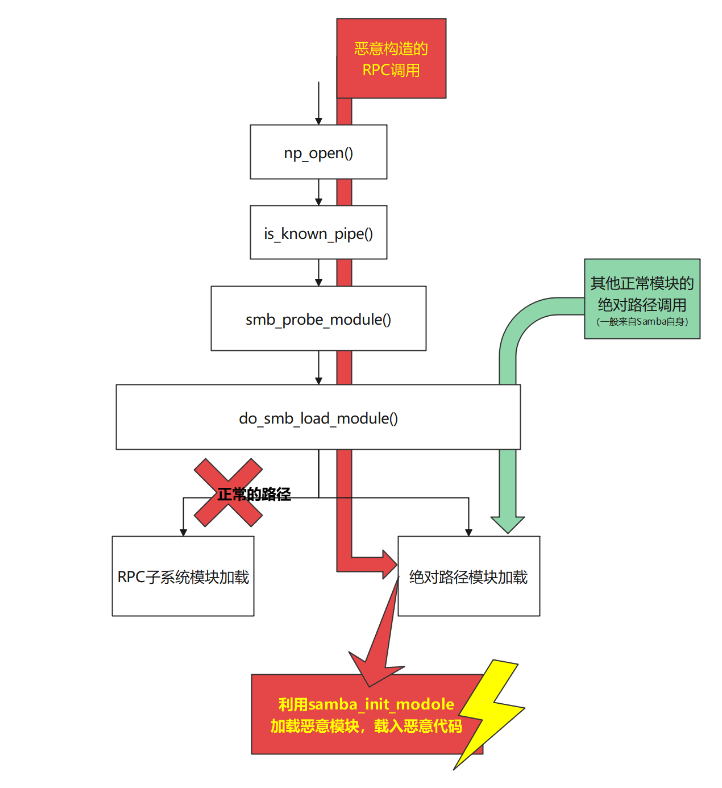 i-rinka/bit-eternalblue-for-macos_linux
Exploit CVE-2017-7494 for Net Security course final Assignment. This would reveal the vulnerability of services that run in administrative priority…
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
 yfelipecruvinel/tryhackme-moniker-link
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.
 vulhub/vulhub
Pre-Built Vulnerable Environments Based on Docker-Compose
 rana-ali93/cve-2021-3156-sudo-buffer-overflow-linux
Red Team exploitation of CVE-2021-3156 (Baron Samedit) – Heap Buffer Overflow in Sudo leading to Local Privilege Escalation on Ubuntu 20.04

 centisgood/duo-agentflow-auditor
AI Code Security — four agents that catch what SAST misses in AI-generated code. Built on GitLab Duo Agent Platform.
 indiquarks/vsftpd-cve-2011-2523-lab
Pen Tesing Lab exploiting VSFTPD 2.3.4 backdoor via Metasploit Framework
 jwillyamz/ezemu
See adversary, do adversary: Simple execution of commands for defensive tuning/research (now with more ELF on the shelf)
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071

 ahmedshamsddin/n8n-rce-cve-2025-68613
n8n RCE (CVE-2025-68613)
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 wolf1892/cve-2019-7609
docker lab setup for kibana-7609
 arkha-corvus/letsdefend-soc173-follina-0-day-detected
We are presented with a security alert indicating the detection of the Follina (CVE-2022-30190) vulnerability. A malicious Word document triggered…