
MASTG-Hacking-Playground
 owasp/mastg-hacking-playground
Collection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…
android-securityeducationios-security+5
owasp/mastg-hacking-playgroundCollection of intentionally insecure iOS and Android apps for learning mobile security testing, reverse engineering, and vulnerability analysis,…
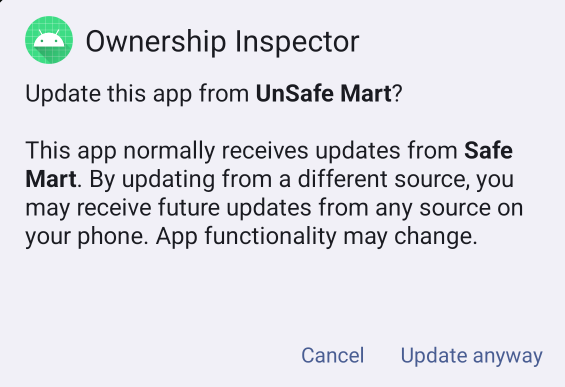 qm4rs/cve-2026-0023-update-ownership-poc
Proof-of-concept demonstrating CVE-2026-0023, an Android Update Ownership trust bypass that suppresses the ownership warning during app updates.…
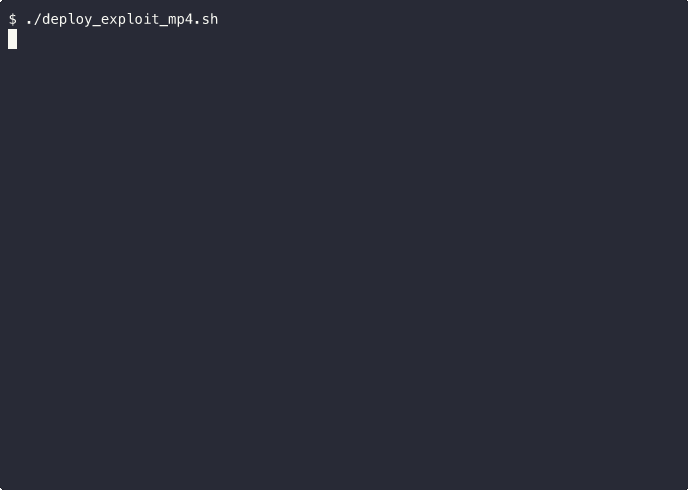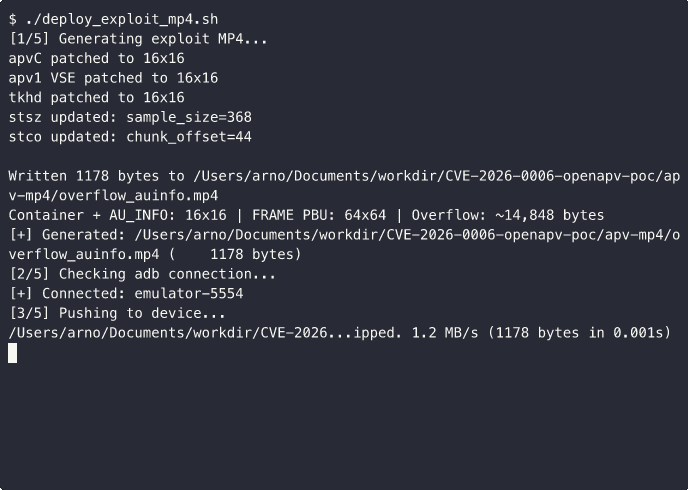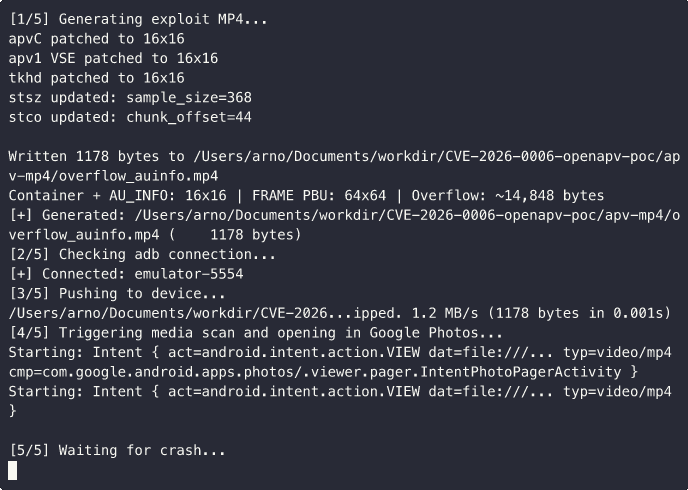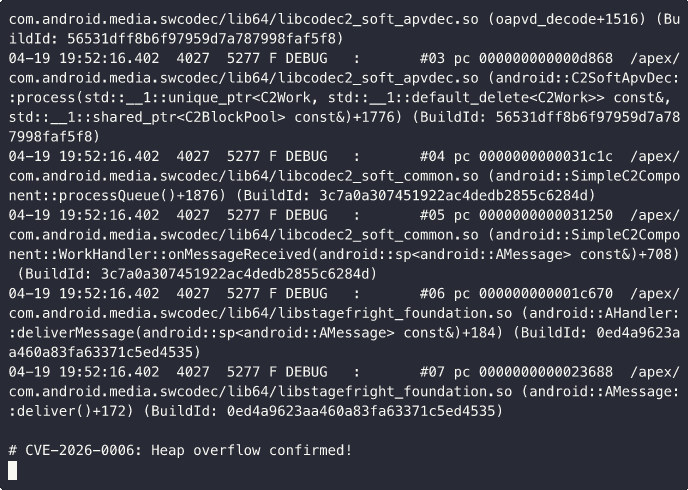 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
 mythicaltree/cve-2019-2215
Proof-of-concept exploit for CVE-2019-2215 (Bad Binder) targeting Android 10 x86_64 emulator. Designed for isolated kernel exploitation research and…
 lazybear8372/cve-2020-23349_lab
Educational Android lab for CVE-2020-23349 in Sina Weibo SDK 4.2.7
 lazybear8372/cve-2023-31014_lab
Educational Android lab for CVE-2023-31014 implicit intent hijacking
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 owasp/securityshepherd
Web and mobile application security training platform
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 owasp/igoat
OWASP iGoat - A Learning Tool for iOS App Pentesting and Security by Swaroop Yermalkar
 jailbreakdotparty/dirtyzero
Simple customization toolbox, utilizing CVE-2025-24203. Supports iOS 16.0 - iOS 18.3.2.
 owasp/igoat-swift
OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
 johackim/docker-hacklab
My personal hacklab, create your own.
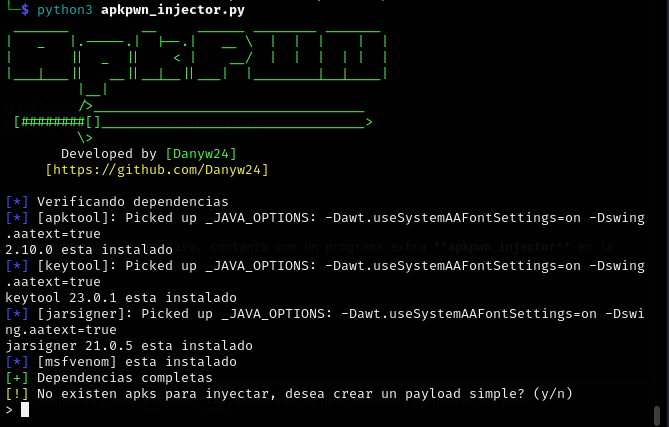 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 qre0ct/android-kernel-exploitation-ashfaq-cve-2019-2215
android-kernel-exploitation-ashfaq-CVE-2019-2215 docker setup for mac users
 lamaper/cve-2026-52199
Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…