
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
84 results
wp2shell preview

wp2shell

GitHubikow/wp2shell

wp2shell — WordPress Core Pre-Auth RCE (CVE-2026-63030 + CVE-2026-60137). Exploit toolkit + remediation.
educationexploitationlabs-practice+4
10
1 month ago
wp2shell-scanner preview

wp2shell-scanner

GitHubbahartanir/wp2shell-scanner

CVE-2026-63030 / CVE-2026-60137 - WordPress pre-auth RCE scanner
exploitationlabs-practicepayload-development+5
81 month ago
CVE-2025-7384 preview

CVE-2025-7384

GitHubdungsocool/cve-2025-7384

Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
educationexploitationlabs-practice+2
1 month ago
CVE-2024-28000-Exploit-Lab preview

CVE-2024-28000-Exploit-Lab

GitHubshawnng078-ops/cve-2024-28000-exploit-lab

Hands-on reproduction of CVE-2024-28000 in LiteSpeed Cache using an isolated WordPress lab. Includes reconnaissance, vulnerable hash recovery,…
educationexploitationlabs-practice+5
24 days ago
SSI-CVE-2022-21661 preview

SSI-CVE-2022-21661

GitHubwellingtonespindula/ssi-cve-2022-21661

Study and exploit the vulnerability CVE-2022-21661 that allows SQL Injections through plugins POST requests to WordPress versions below 5.8.3.
educationexploitationlabs-practice+3
62 years ago
WordPress-Path-Traversal-CVE-2019-11447 preview

WordPress-Path-Traversal-CVE-2019-11447

GitHubcapivara-research/wordpress-path-traversal-cve-2019-11447

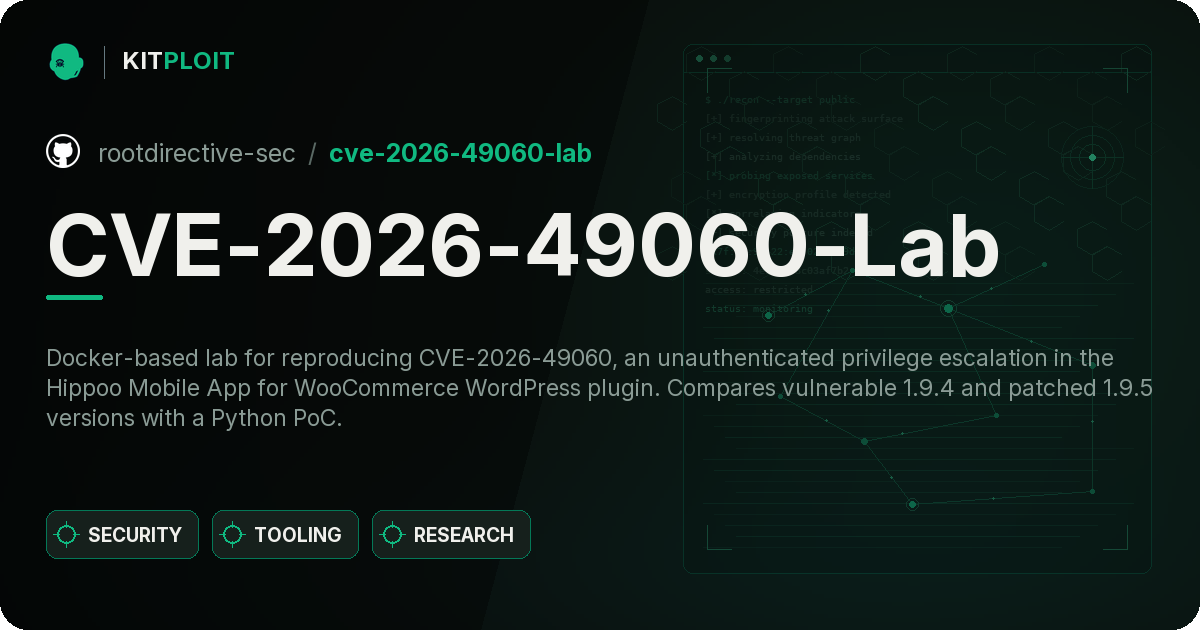
Detailed penetration test report demonstrating unauthenticated path traversal (CVE-2019-11447) in WordPress Simple Backup plugin, including…

educationexploitationlabs-practice+3
24 days ago
CVE-2026-63030-CVE-2026-60137 preview

CVE-2026-63030-CVE-2026-60137

GitHubgiangdurian/cve-2026-63030-cve-2026-60137

Pre-auth RCE exploit for WordPress (CVE-2026-63030 + CVE-2026-60137) chaining route confusion and SQL injection into full shell access. Includes…

ctfeducationexploitation+4
1 month ago
CVE-2024-1813-POC preview

CVE-2024-1813-POC

GitHubmobetasec/cve-2024-1813-poc

PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
ctfeducationlabs-practice+4
2 months ago
CVE-2026-49060-Lab preview

CVE-2026-49060-Lab

GitHubrootdirective-sec/cve-2026-49060-lab

Docker-based lab for reproducing CVE-2026-49060, an unauthenticated privilege escalation in the Hippoo Mobile App for WooCommerce WordPress plugin.…
educationlabs-practicepenetration-testing+3
3 months ago
CVE-2026-60137_CVE-2026-63030 preview

CVE-2026-60137_CVE-2026-63030

GitHubdungsocool/cve-2026-60137_cve-2026-63030

WordPress unauthenticated RCE exploit combining route confusion and SQL injection. Automated script, lab setup, and detailed vulnerability analysis…
educationexploitationlabs-practice+3
1 month ago
EXPLOIT-CVE-2026-63030 preview

EXPLOIT-CVE-2026-63030

GitHubjoaovicdev/exploit-cve-2026-63030

Docker-based vulnerable WordPress lab with Python exploit demonstrating pre-auth route confusion and SQL injection chain (CVE-2026-63030 +…
ctfeducationexploitation+3
11 month ago
CVE-2015-9357-POC preview

CVE-2015-9357-POC

GitHubsaretawa/cve-2015-9357-poc

Proof-of-concept exploit for CVE-2015-9357: stored XSS in WordPress smiley parser that bypasses wp_kses, chains nonce forgery to create admin…

educationexploitationlabs-practice+3
2 months ago
CVE-2026-14840 preview

CVE-2026-14840

GitHubnullwhisper/cve-2026-14840

Proof-of-concept exploit for a WordPress plugin vote-limit bypass using spoofed X-Forwarded-For headers; ships a Docker lab to validate…
exploitationlabs-practicepenetration-testing+3
1 month ago
CVE-2026-56011-Lab preview

CVE-2026-56011-Lab

GitHubrootdirective-sec/cve-2026-56011-lab

Docker-based lab for reproducing and validating CVE-2026-56011, an unauthenticated XSS vulnerability in MapPress Maps for WordPress, with vulnerable…

educationlabs-practicepenetration-testing+3
2 months ago
CVE-2016-10033 preview

CVE-2016-10033

GitHubchipironcin/cve-2016-10033

Exploit PoC for CVE-2016-10033 targeting WordPress 4.6 with Docker-based vulnerable container for reverse shell without authentication.
educationexploitationlabs-practice+3
19 years ago
CVE-2022-21661-Demo preview

CVE-2022-21661-Demo

GitHubdaniel616/cve-2022-21661-demo

Demonstration of the SQL injection vulnerability in wordpress 5.8.2
database-securityeducationlabs-practice+3
23 years ago
CVE_2026_2576_PoC preview

CVE_2026_2576_PoC

GitHubsowatkheang/cve_2026_2576_poc

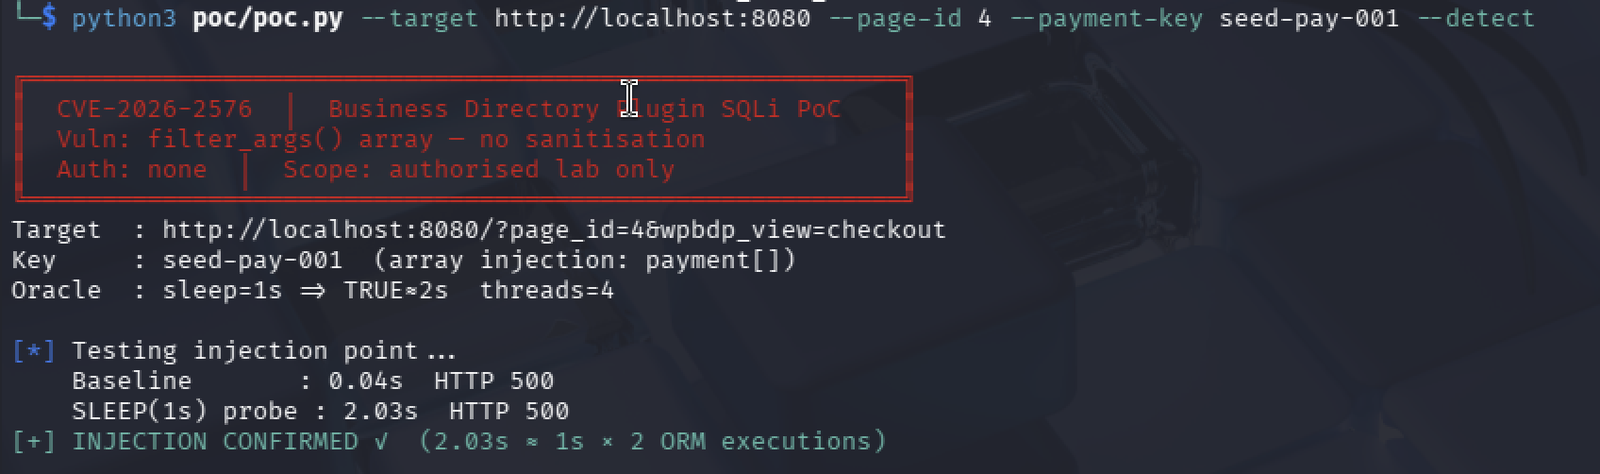
CVE-2026-2576 — Business Directory Plugin SQLi PoC (Local Setup). Unauthenticated Time-Based Blind SQL Injection Business Directory Plugin for…
educationexploitationlabs-practice+3
25 months ago
CVE-2026-14282 preview

CVE-2026-14282

GitHubnullwhisper/cve-2026-14282

GoDAM WordPress plugin <= 1.12.2 unauthenticated file upload RCE (CVE-2026-14282)

exploitationlabs-practicepenetration-testing+3
11 month ago
Previous12345Next