
CVE-2025-8110
 xdezen/cve-2025-8110
Python proof-of-concept for CVE-2025-8110, demonstrating arbitrary file write to RCE in Gogs via symlink and API, with educational lab usage.
educationexploitationlabs-practice+3
xdezen/cve-2025-8110Python proof-of-concept for CVE-2025-8110, demonstrating arbitrary file write to RCE in Gogs via symlink and API, with educational lab usage.
 dhiaelhak-rached/cve-2026-39987-lab-or-marimo-cve-lab
Educational Docker lab demonstrating CVE-2026-39987, a pre-auth RCE via WebSocket authentication bypass in marimo, with exploit script and patch…
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
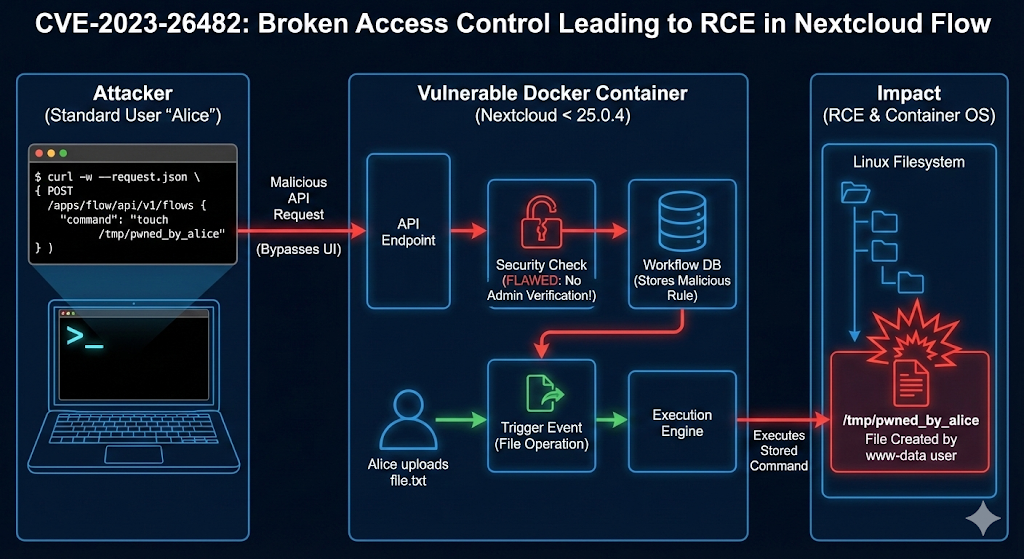 isabbii/poc---cve-2023-26482-rce-lab-nextcloud
Docker-based lab reproducing CVE-2023-26482 (Nextcloud RCE) with automated exploit script for educational vulnerability analysis and exploitation…
 ritinify/cve-2025-29927-poc
Proof-of-concept exploit for CVE-2025-29927, a Next.js middleware authorization bypass. Includes a vulnerable target lab and Python script to verify…
 gvmyz/cve-2012-2982_python
PoC Python script as an exercice from tryhackme.
 spydomain/cve-2023-22809-automated-python-exploits
Automates vulnerability check for sudo versions and privilege escalation via sudoedit if exploitable, helping users test and gain root access.
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 george0papasotiriou/cve-2026-11119-padding-oracle-attack-on-cbc-mode-encryption
Demonstrates a padding oracle attack against AES-CBC encryption using a vulnerable Flask decrypt endpoint and a Python exploit script to decrypt…
 eunho87/cve-2021-42013
Proof-of-concept exploit for CVE-2021-42013 Apache HTTP Server path traversal and remote code execution vulnerability, with Docker-based lab…
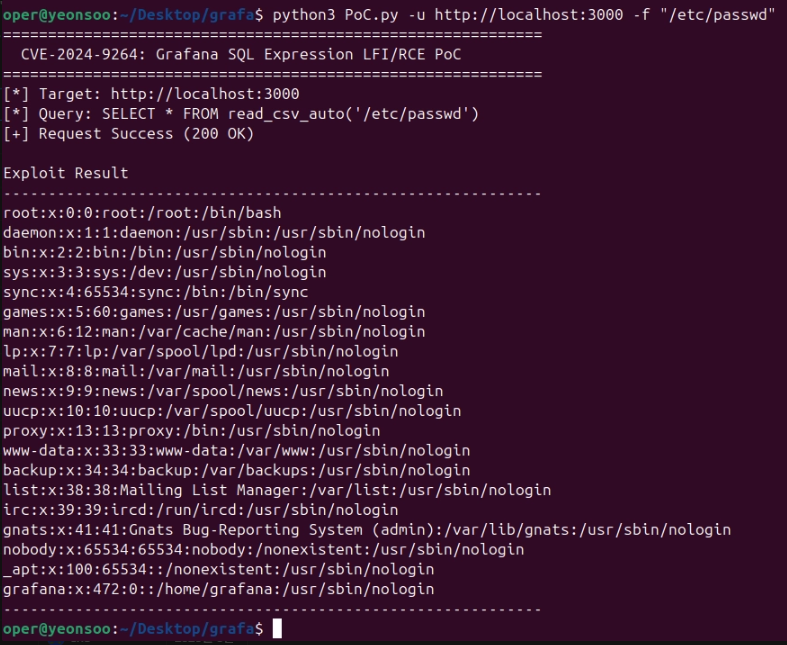 yeonchoda/cve-2024-9264
PoC exploit for CVE-2024-9264: Grafana SQL Expression vulnerability enabling local file inclusion and remote code execution via DuckDB SQL injection.…
 caihuar/joomla-cve-2015-8562
Docker-based environment for testing Joomla RCE (CVE-2015-8562) with an included Python exploit script for command execution and reverse shells.
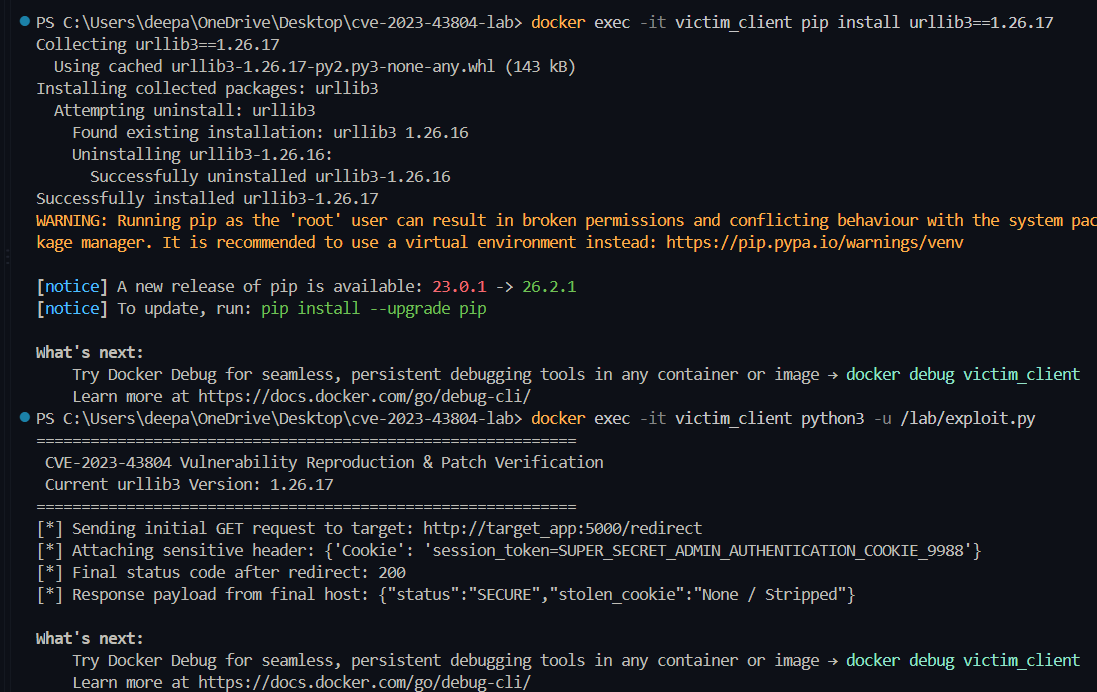 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
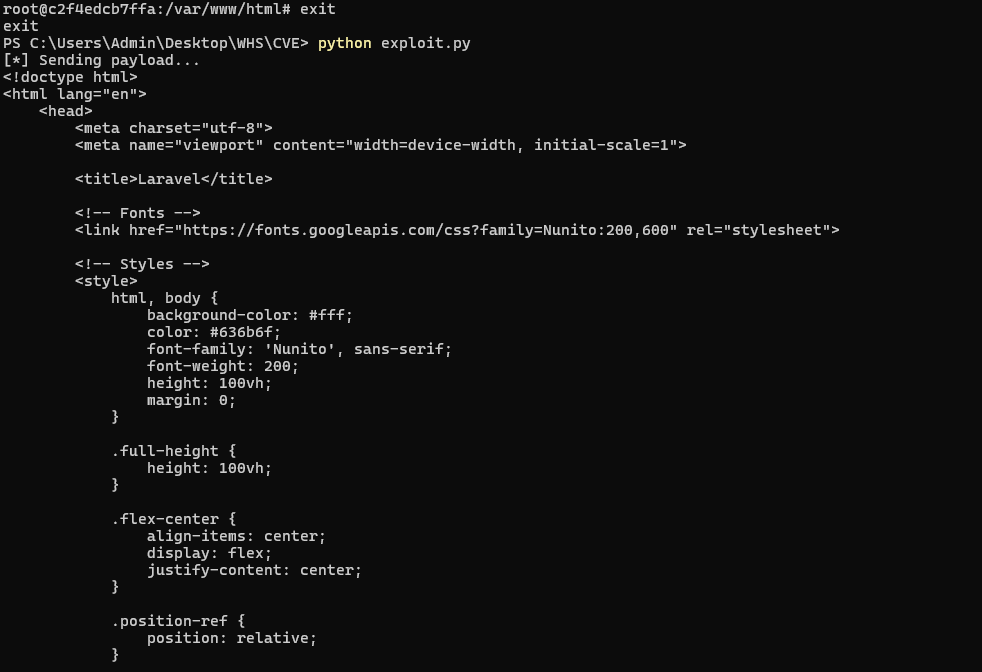 yeahhbean/laravel-cve-2018-15133
Docker-based PoC environment for CVE-2018-15133 Laravel APP_KEY unserialization vulnerability. Includes exploit script to verify remote code…
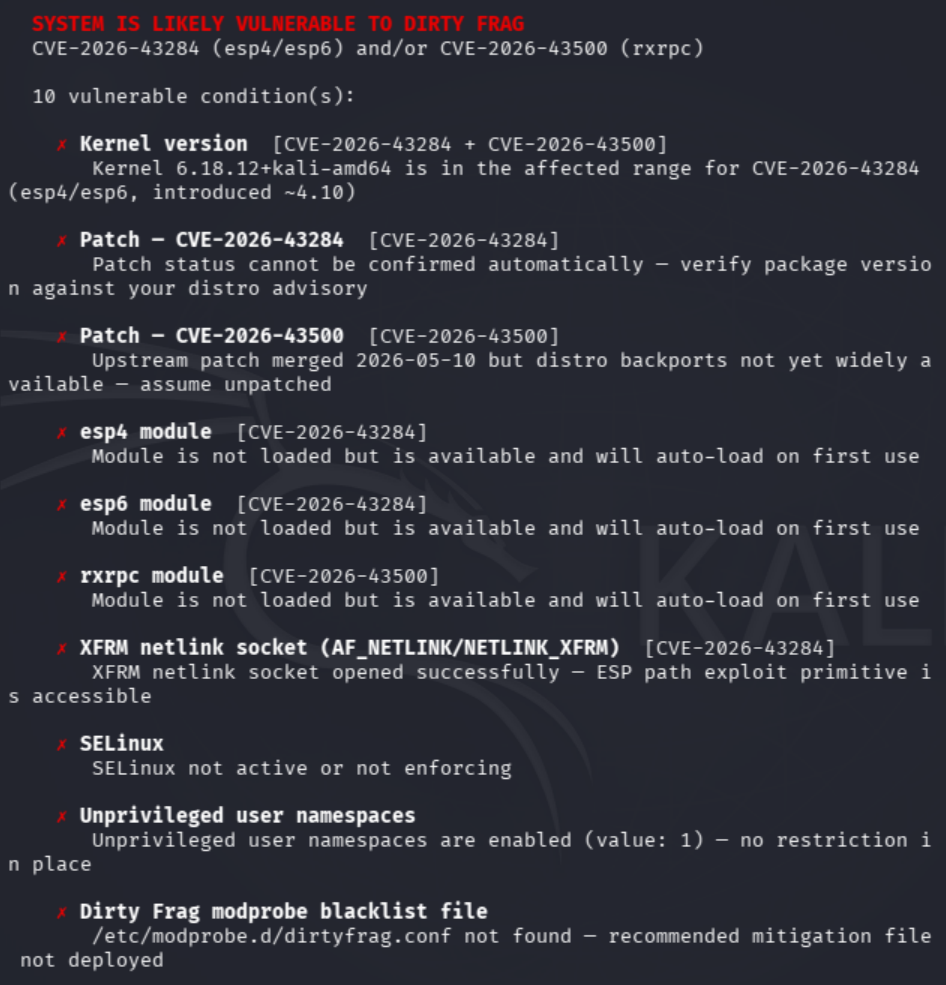 dylanclaudio/reporte-de-escalada-de-privilegios-local-dirty-frag
Se realizó una evaluación de vulnerabilidades sobre una máquina virtual con Kali Linux utilizando un script detector para la vulnerabilidad Dirty…
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…