
Juiceshopgl
 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…
ctfeducationlabs-practice+5
mbrandner-group/juiceshopglIntentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…

 eesshq/cve-2017-0144---etneralblue-ms17-010-remote-code-execution
Step-by-step guide to exploiting MS17-010 EternalBlue vulnerability on Windows Server 2008 R2, including reconnaissance, exploitation,…
 nyambiblaise/exfiltrated-machine-walkthrough---subrion-cms-cve-2021-2220-
Step-by-step walkthrough for exploiting Subrion CMS via CVE-2021-2220 on an OffSec lab machine, covering web application exploitation and flag…
 bibo318/kali-cve-2019-0708-lab
Lab environment for exploiting CVE-2019-0708 (BlueKeep) vulnerability on Kali Linux, providing hands-on practice for penetration testing and…
 navya240/intel471-threat-hunting-cve-2023-46604
My first hands-on Intel 471 threat hunting workshop experience investigating CVE-2023-46604 using Elastic SIEM, vulnerability intelligence, and…
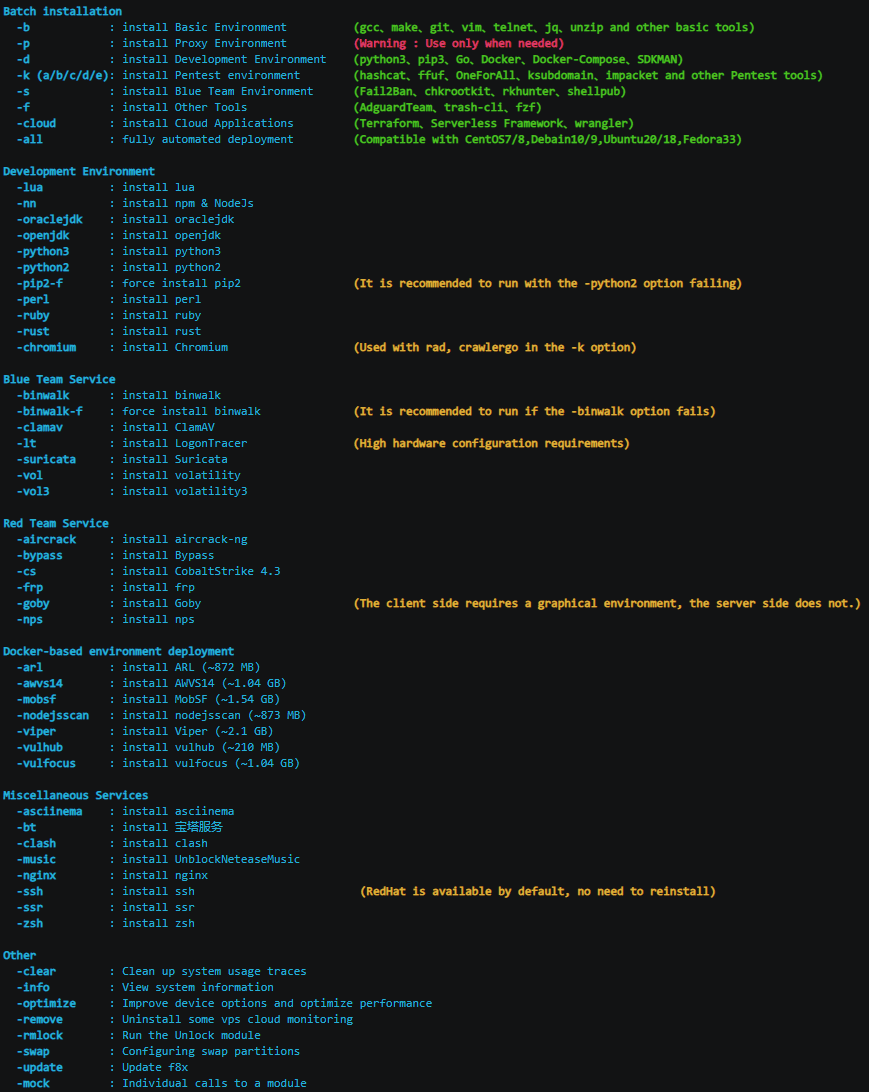 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool
 lamaper/cve-2026-52199
Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…
 hotpotcookie/cve-2021-44228-white-box
Log4j vulner testing environment based on CVE-2021-44228. It provide guidance to build the sample infrastructure and the exploit scripts. Supporting…
 xxxtectationxxx/react2shell-cve-lab
A self-hosted vulnerable Next.js environment running on Docker for simulating CVE-2025-55182. Built for educational security research and CTF…
 cyprianatsyor/cve-2024-24919-incident-report.md
Detailed incident report analyzing CVE-2024-24919 arbitrary file read exploit on Check Point Security Gateway, including technical analysis, response…
 maaythm/cve-2025-32462_32463-lab
Docker PoC for CVE-2025-32462 & CVE-2025-32463 (sudo), based on Stratascale CRU research.
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 i3r1h0n/grafanascimalform
Exploit and test stand for CVE-2025-41115
 cxiao/rust-reversing-workshop-recon-2024
Slides and files for the Reversing Rust Binaries: One step beyond strings workshop at REcon 2024, presented on June 28, 2024.
 ibondarenko1/azure-sentinel-detection-engineering
9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…
 dexsemon/cve-2026-35194
Proof-of-concept exploit and Docker lab for CVE-2026-35194, an Apache Flink SQL code injection enabling remote code execution on TaskManagers via the…
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
 alphatin123/cve-2024-49113
FYP: Reproduced CVE-2024-49113 PoC on Windows Server 2019 (ref. SafeBreach); assessed Windows EDR detection gaps and produced ISO 27001-aligned…