
CVE-2021-3456
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
command-and-controleducationexploitation+8
mrk336/cve-2021-3456A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 yusufdalbudak/cve-2026-42945
Dockerized lab for training on NGINX rewrite vulnerability (CVE-2026-42945) with vulnerable and patched instances, benign test scripts, and…
 p1rat3r00t/why-so-serious-sam
PoC malware that uses exploit CVE-2021-36934 (improper ACLs on shadow copies) using a fileless red team method on Windows 10/11 with LOLBins,…
 jolynngsc/efs_cve-2021-43217
Educational lab demonstrating EFS bypass (CVE-2021-43217) on Windows 10 using Kali Linux, Metasploit, and custom Python shellcode for penetration…
 wizardy0ga/thm-steel_mountain-cve-2014-6287
A write up on the Steel Mountain box from TryHackMe.com and exploit for CVE-2014-6287
 mantvydasb/redteaming-tactics-and-techniques
Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…
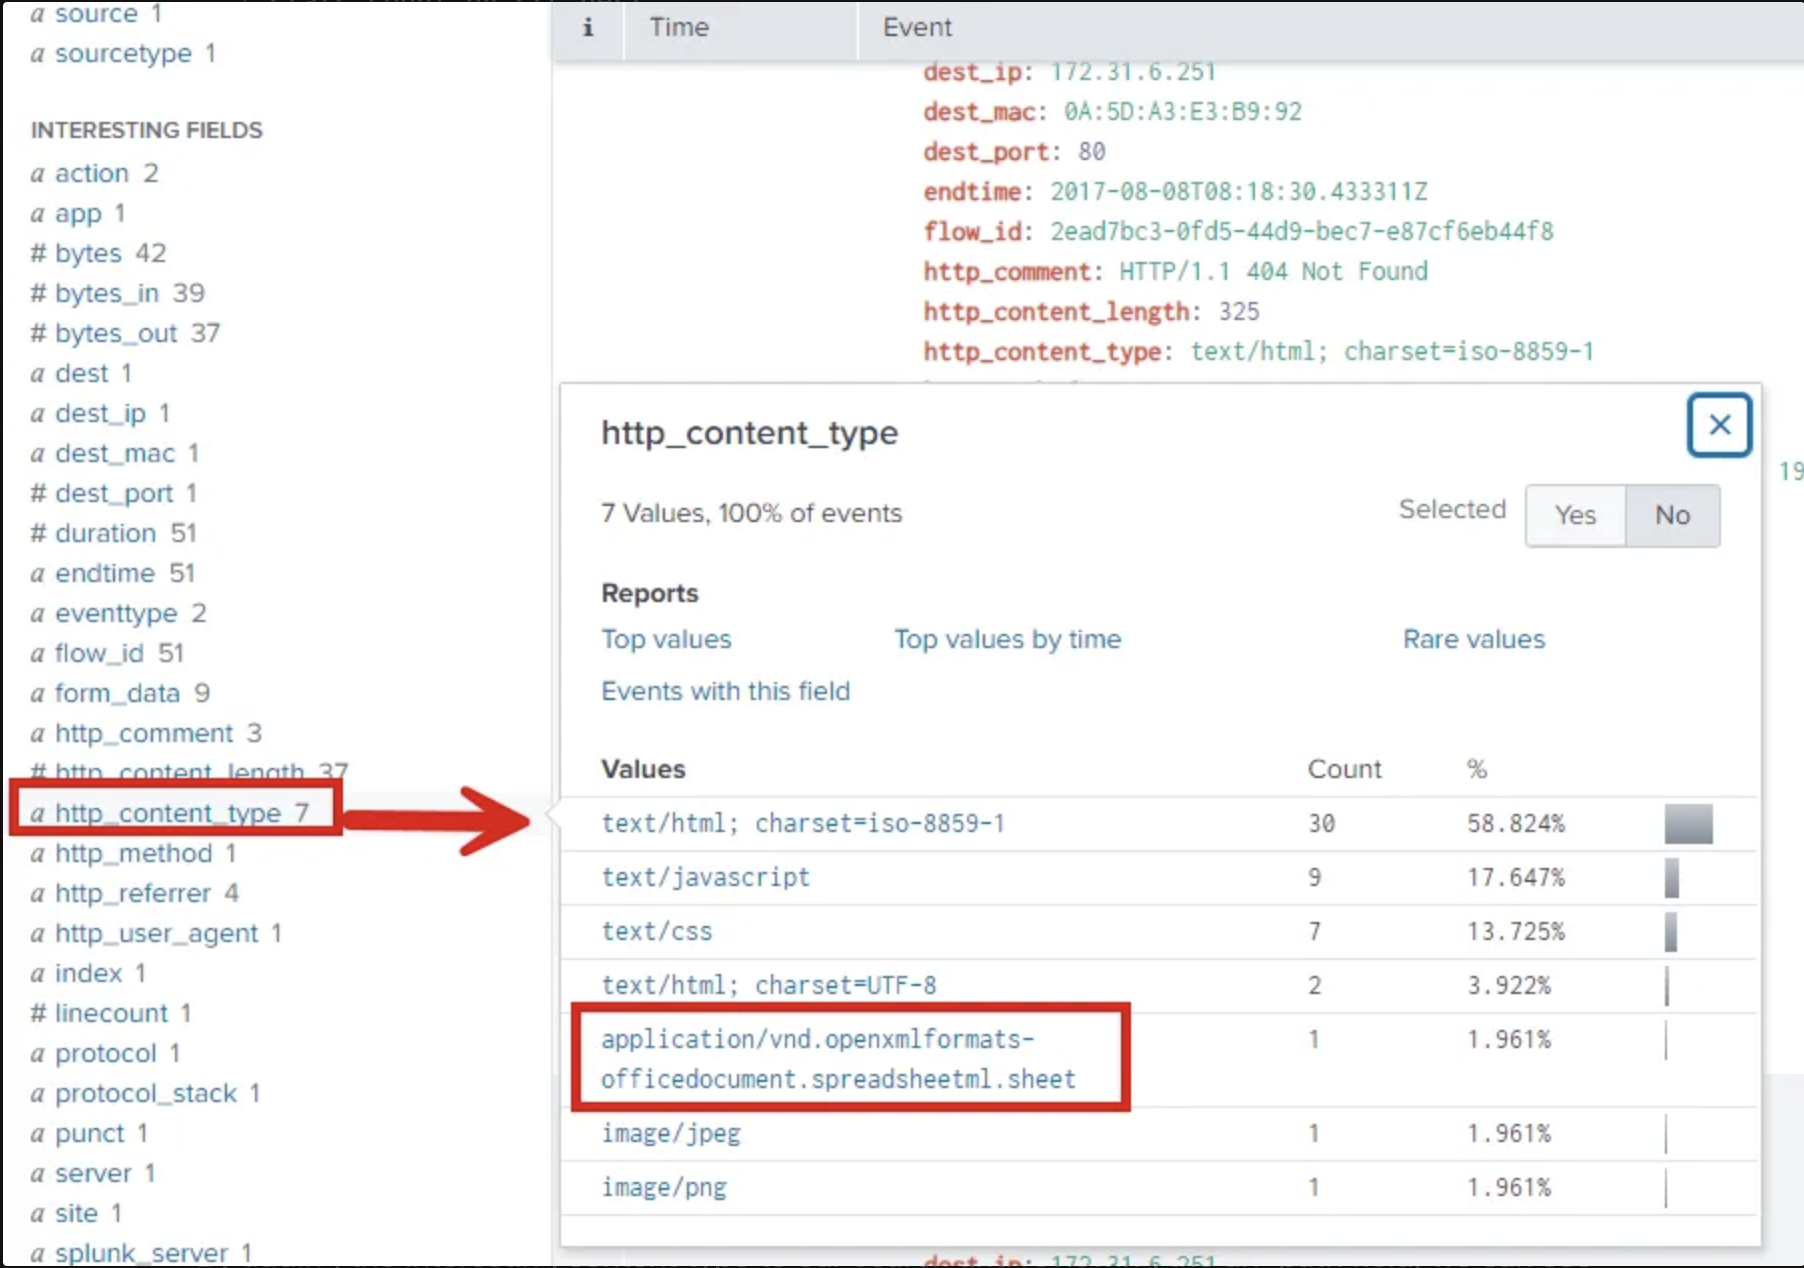 0x0allenace/soc-analyst-portfolio
A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…
 tafloh/cve-2019-1388-privilege-escalation--2021-
CVE-2019-1388 Lab Analysis: Documented local privilege escalation via Windows UAC certificate dialogs on Windows 7.
 dexsemon/cve-2026-27495
Proof-of-concept exploit and lab environment for CVE-2026-27495
 bohemian-miser/cve-2025-65018_exploit_challenge
CTF challenge exploiting a heap overflow in libpng's png_image_finish_read to overwrite a function pointer and spawn a shell, with build scripts and…
 bossnick98/-soc342---cve-2025-53770-sharepoint-toolshell-auth-bypass-and-rce
An activity to train analysis skills and reporting
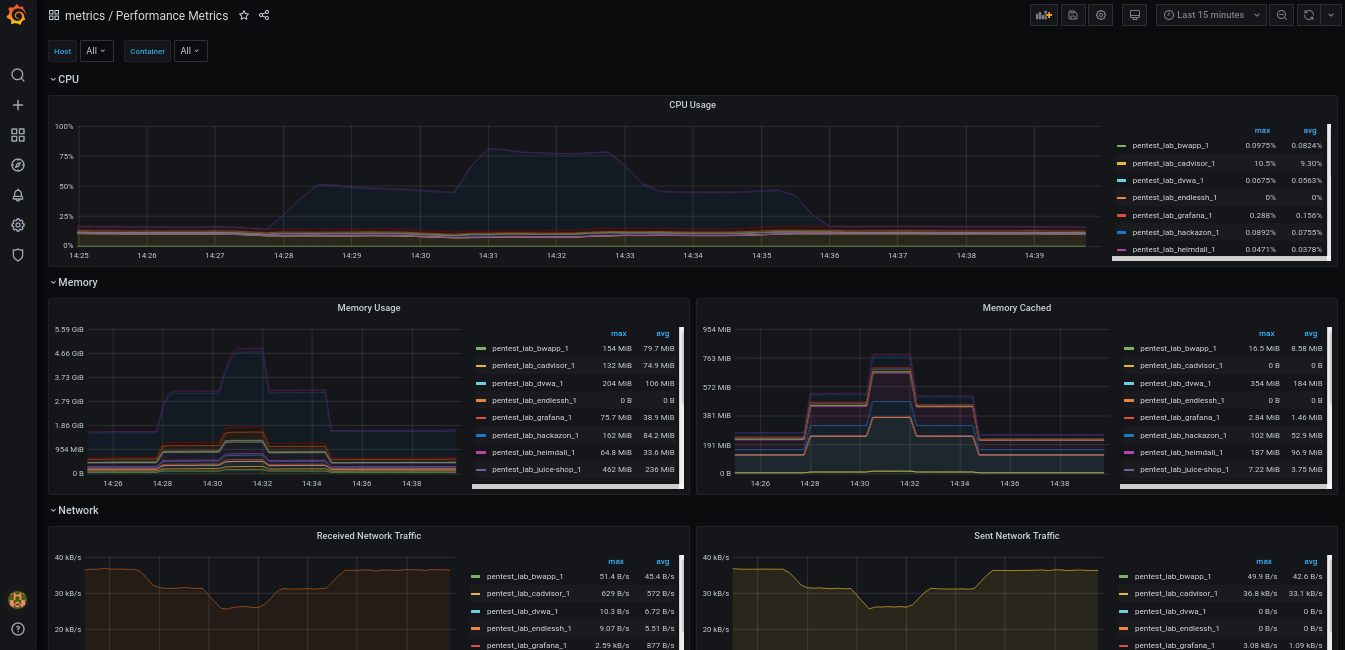 oliverwiegers/pentest_lab
Local penetration testing lab using docker-compose.
 dinosn/cve-2026-10053-lab
Reproducible lab for CVE-2026-10053 (GitLab npm package-registry path traversal -> arbitrary file write as git). Vulnerable 19.2.1 vs patched 19.2.2,…
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
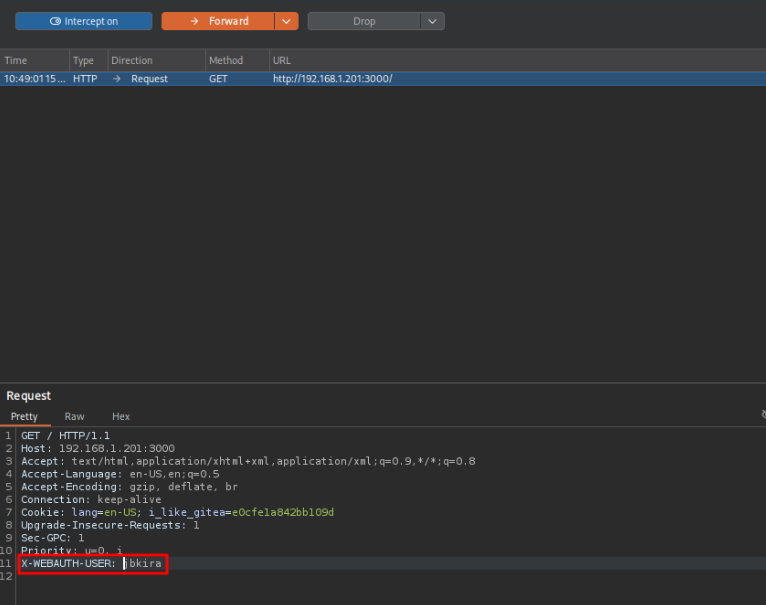 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 dawnsmithcyber/azure-vulnerability-remediation-project
End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…
 ahmedmansour93/event-id-217-rule-name-soc254-apache-ofbiz-auth-bypass-and-code-injection-0day-cve-2023-51467-
🚨 Just completed an incident report on Event ID 217: Apache OFBiz Auth Bypass and Code Injection 0-Day (CVE-2023-51467). This critical vulnerability…
 owasp/ai-vulnerabilities-playground
Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…