
CVE-2021-23394
 0xnemian/cve-2021-23394
Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
container-securityeducationlabs-practice+3
0xnemian/cve-2021-23394Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
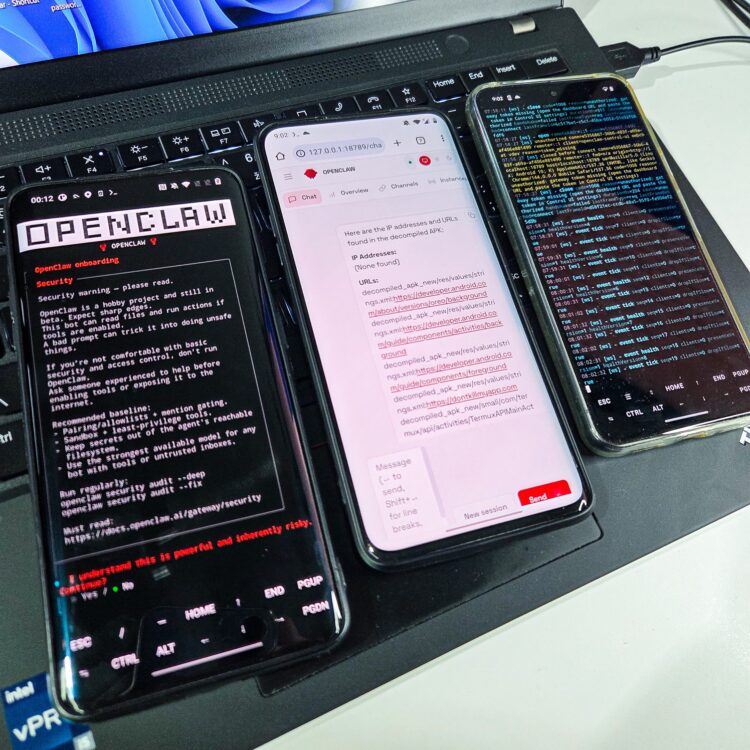 androidmalware/openclaw_termux
How to Install OpenClaw on an Android Phone and Control It via WhatsApp
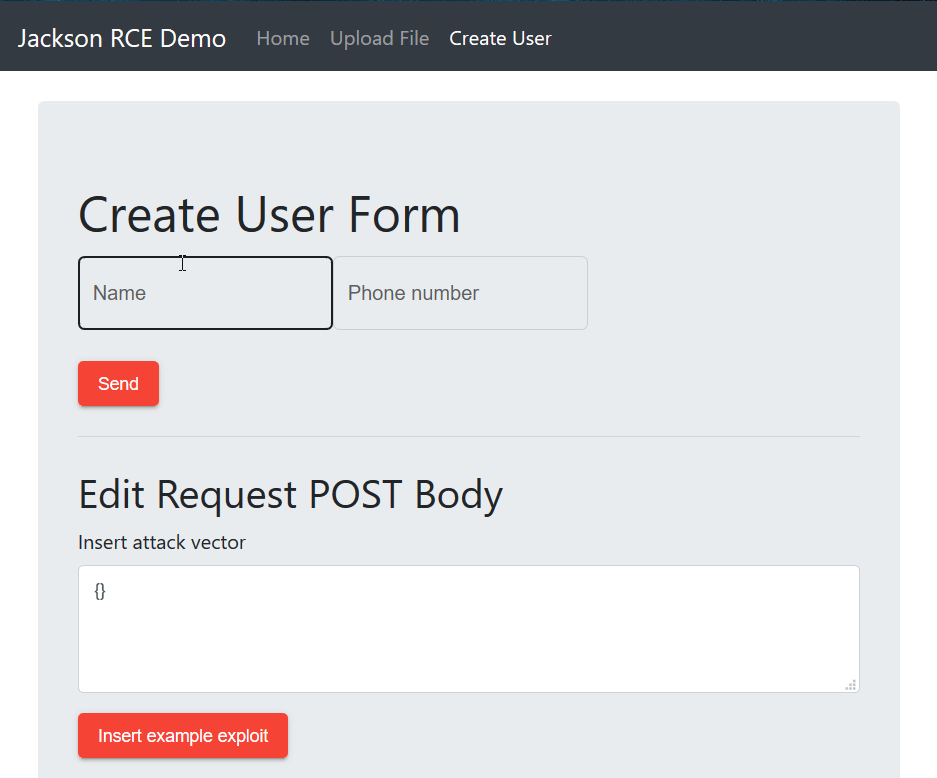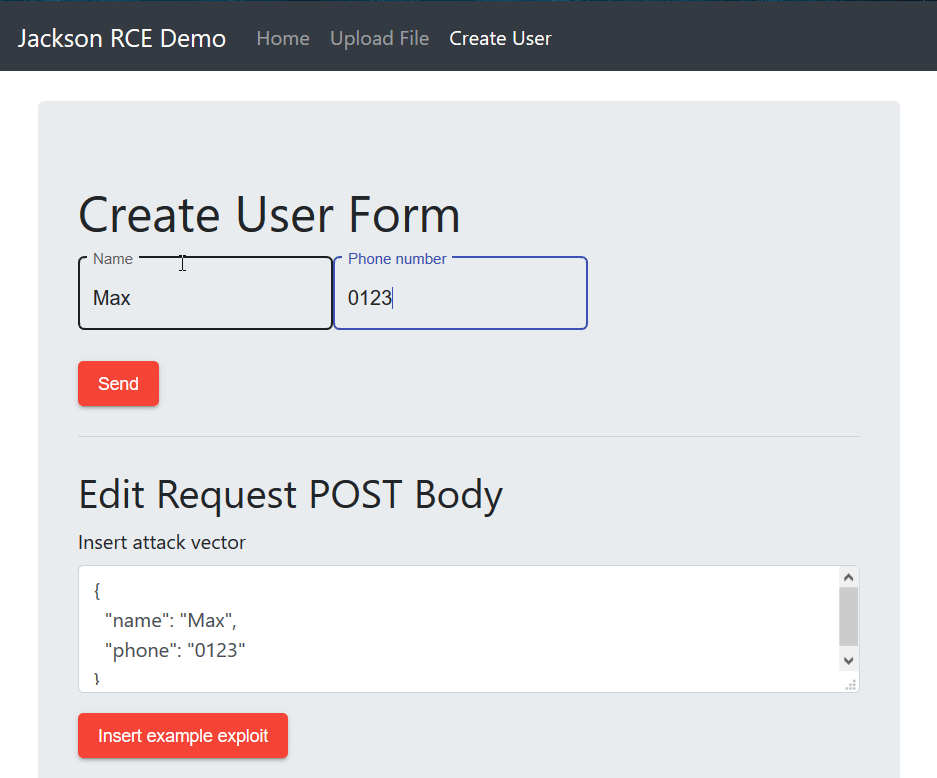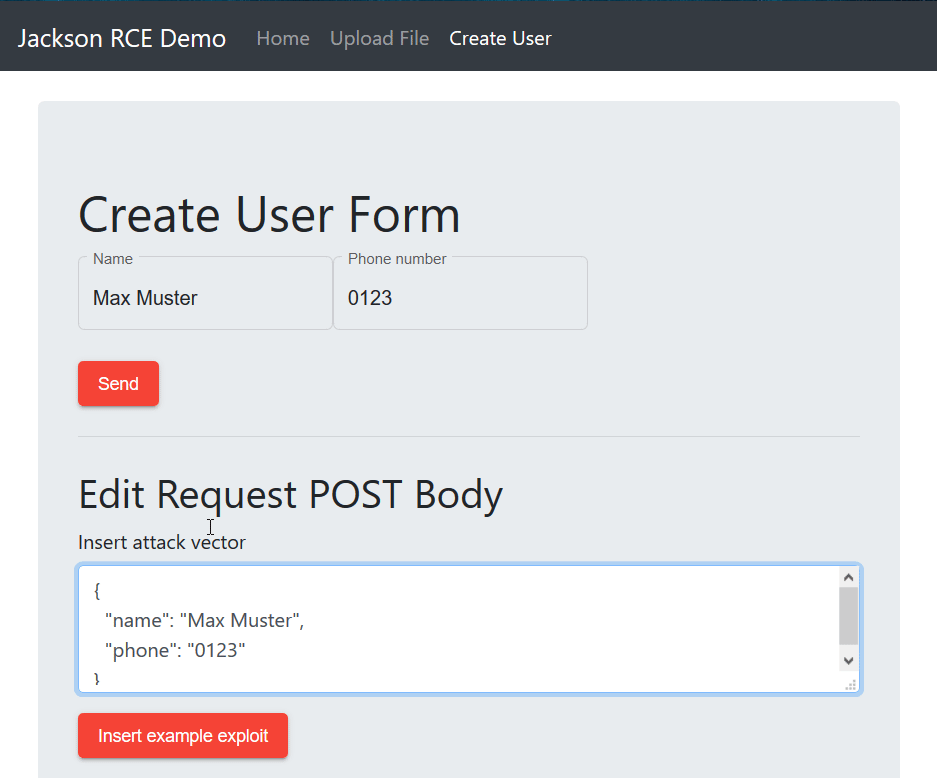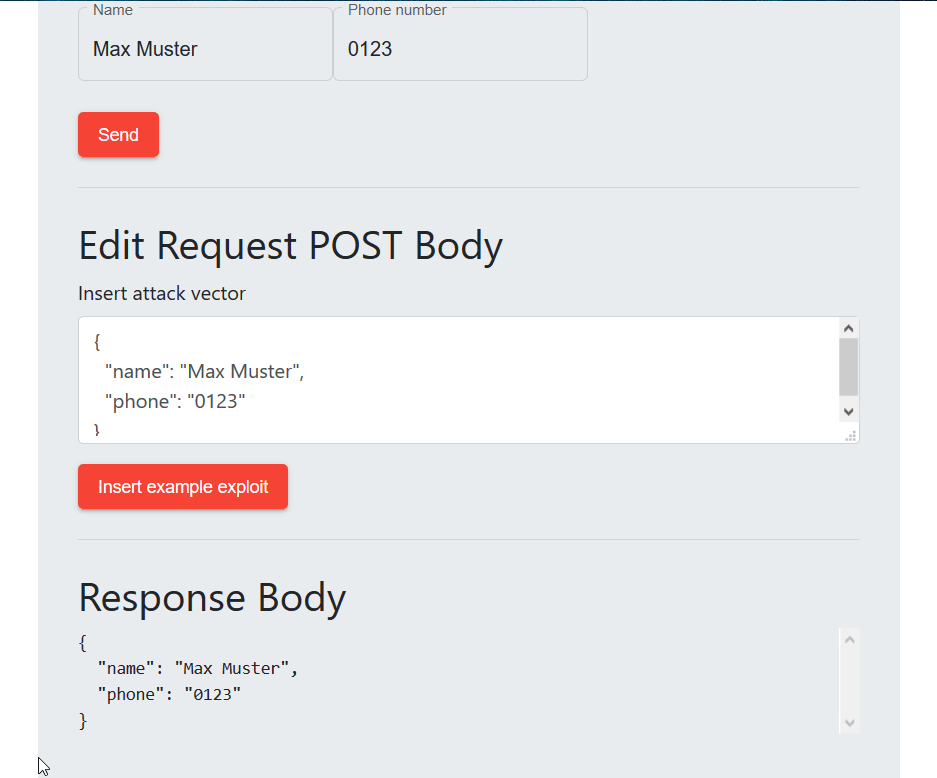 javanxd/demo-exploit-jackson-rce
Exploiting CVE-2017-7525 demo project with Angular7 frontend and Spring.
 jhatchi/nexacorp-dfir-inc-2026-001
DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…
 rajmadhusankha/shellshock-cve-2014-6271-exploitation-and-analysis
Educational lab demonstrating Shellshock (CVE-2014-6271) exploitation using Metasploit against Metasploitable 2, including scanning, exploitation,…
 rawfilejson/awesome-osint-arsenal
OSINT & recon toolkit // 100+ tools, one-command installer, SOCMINT, GEOINT, network recon, dark web, forensics & more.
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 athena-os/athena
Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 badsectorlabs/ludus_xz_backdoor
An Ansible Role that installs the xz backdoor (CVE-2024-3094) on a Debian host and optionally installs the xzbot tool.
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 olowostandard1/cve-2023-38831-winrar-vulnerability-analysis
This project is a cybersecurity research and analysis project focused on CVE-2023-38831, a critical WinRAR vulnerability that allows attackers to…
 mauricelambert/labautomationcve-2021-43798
This script implements a lab automation where I exploit CVE-2021-43798 to steal user secrets and then gain privileges on a Linux system.
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
 pedrorichil/cve-2025-49844
Educational lab environment demonstrating CVE-2025-49844 (RediShell) in Redis. Includes Docker setup, exploit PoC script, and security…
 rauljvc8/exploit-dirty-cow
Privilege escalation lab reproducing the DirtyCow kernel exploit (CVE-2016-5195) in a controlled environment. Includes vulnerable setup, exploit…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
 m0d0ri205/wargame_re-ls
CTF challenge exploiting CVE-2025-0184 DOCX SSRF vulnerability to access internal admin service and retrieve a flag. Includes exploit generator and…