

roundcube-cve-2025-49113-lab
 ankitpandey383/roundcube-cve-2025-49113-lab
Hands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.
code-analysisctfeducation+7
ankitpandey383/roundcube-cve-2025-49113-labHands-on exploitation lab for Roundcube Webmail CVE-2025-49113 (authenticated PHP object deserialization → RCE) to read /secret.txt.
 deepakkcybersec-eng/kioptrix-level1-vulnerability-analysis
Technical audit of Kioptrix Level 1. Focus: Samba 2.2.1a exploitation (CVE-2003-0201), manual enumeration, and internal infrastructure hardening.
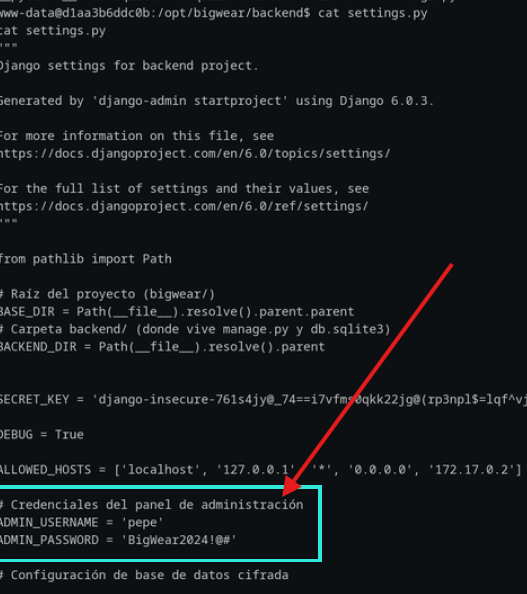 salimelh94/web-penetration-test
Exploiting WordPress vulnerabilities (CVE-2025-34077), authentication bypass via cookie injection, and privilege escalation to root. Part of my…
 gopeshkachhadiya/windows-2
A hands-on Windows 7 lab designed to demonstrate the real-world impact of the BlueKeep (CVE-2019-0708) vulnerability through practical exploitation…
 100hnomeunome/zerologon-cve-2020-1472-lab
Explicação e demonstração da vulnerabilidade ZeroLogon (CVE-2020-1472)
 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
 alexs18/cve-2021-4773
Step-by-step tutorial demonstrating how to set up a vulnerable Apache 2.4.49 environment and exploit CVE-2021-41773 path traversal using Kali Linux…
 artemcyberlab/project-exploitation-of-webmin-authentication-vulnerability
Research Objective: To conduct a comprehensive analysis and successful exploitation of a Remote Code Execution (RCE) vulnerability in Webmin version…
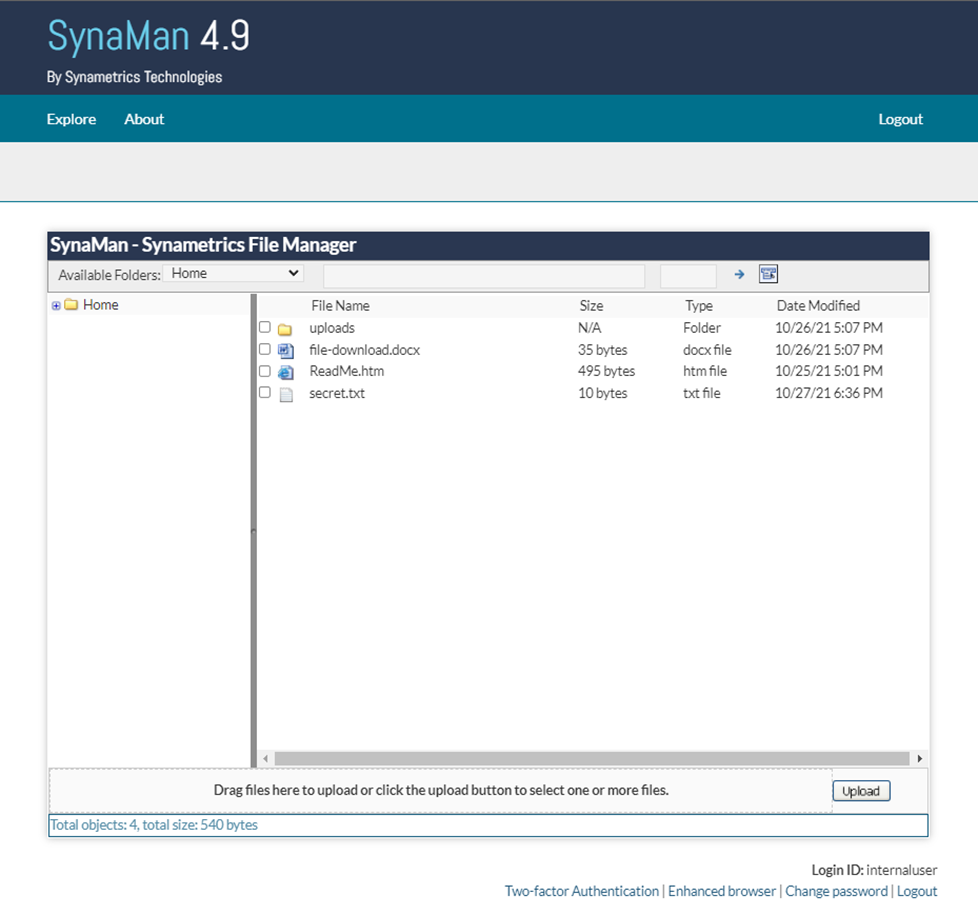 videnlabs/cve-2022-22828
Write-up of CVE-2022-22828
 youngmin0104/cve-2017-7529-
Docker-based reproduction environment for CVE-2017-7529 Nginx integer overflow vulnerability, demonstrating information disclosure via crafted Range…
 denizse/cve-2021-34527
Small Powershell Script to detect Running Printer Spoolers on Domain Controller
 hklabcr/cve-2011-2523
Manual and automated exploitation walkthrough for vsftpd 2.3.4 backdoor (CVE-2011-2523) with custom reverse shell payload and Metasploit integration…
 rajmadhusankha/shellshock-cve-2014-6271-exploitation-and-analysis
Educational lab demonstrating Shellshock (CVE-2014-6271) exploitation using Metasploit against Metasploitable 2, including scanning, exploitation,…
 guigui237/exploitation-de-la-vuln-rabilit-cve-2015-5254-
Step-by-step exploitation guide for Apache ActiveMQ CVE-2015-5254 deserialization vulnerability using jmet, with Docker-based lab setup and…
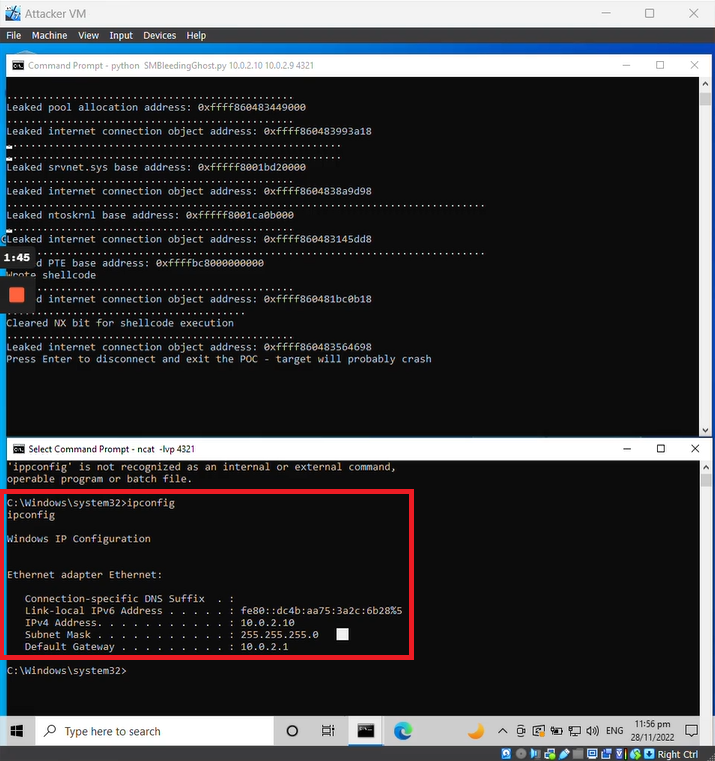 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.