
CVE-2026-22599
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
database-securityexploitationlabs-practice+5
1
abraxas/cve-2026-22599Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
 abraxas/cve-2026-77635
Disclosure pack and Python PoC for CVE-2026-77635, an unauthenticated SQL injection in CakePHP's jsonValue() with PostgresDriver, including a…
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 imbas007/cve-2026-67401
Proof-of-concept for CVE-2026-67401, a cPanel/WHM EmailTrack SQL injection enabling arbitrary file write and root RCE, with SQLi detection probes and…
 isaca0315/cve-2026-44840-poc
Docker lab reproducing CVE-2026-44840, a DQL injection in Dgraph's checkUserPassword GraphQL query, with exploit script and vulnerable vs patched…
 686f6c61/poc-aiowpm-cve-2026-19949
Reproducible Docker-based proof-of-concept for CVE-2026-19949, a second-order SQL injection in All-in-One WP Migration <= 7.109 that leaks the…
 flx-0x00/cve-2026-59550
Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.
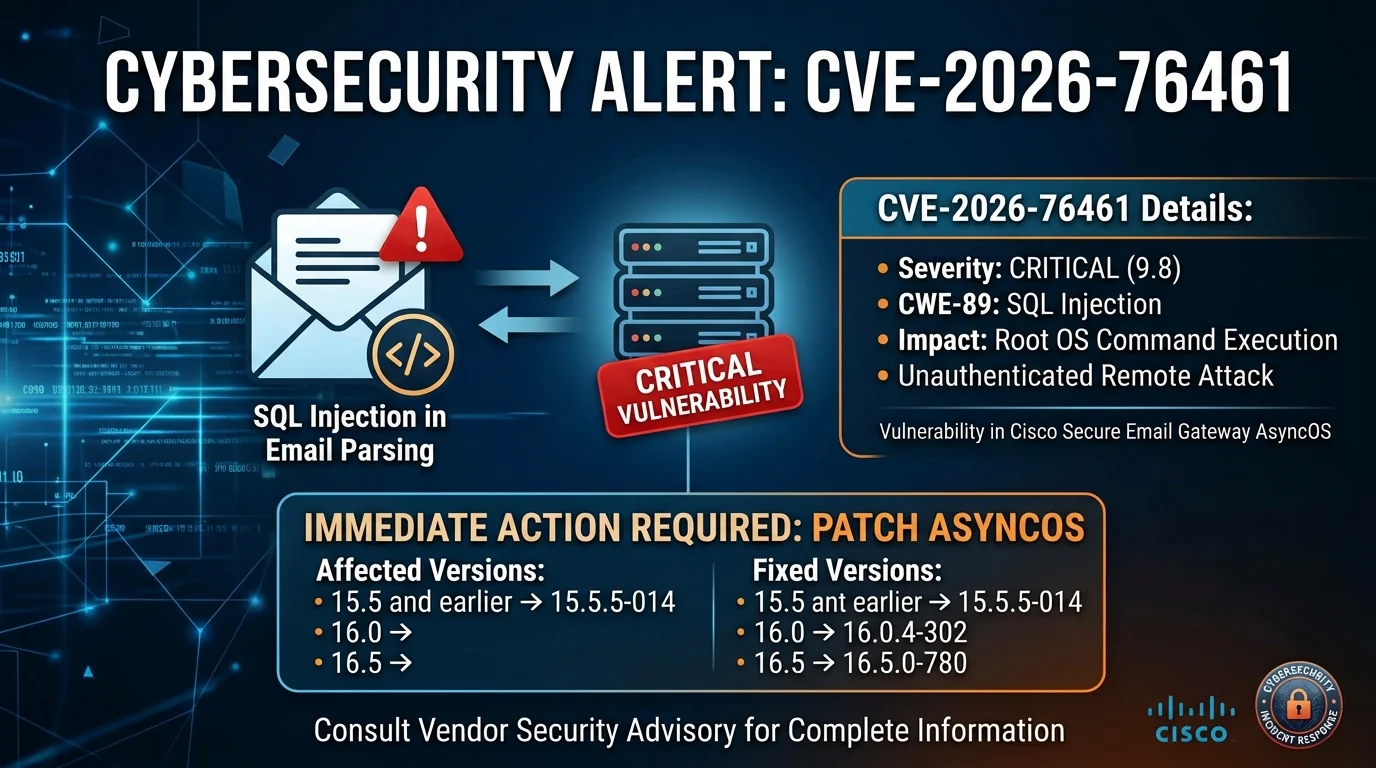 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
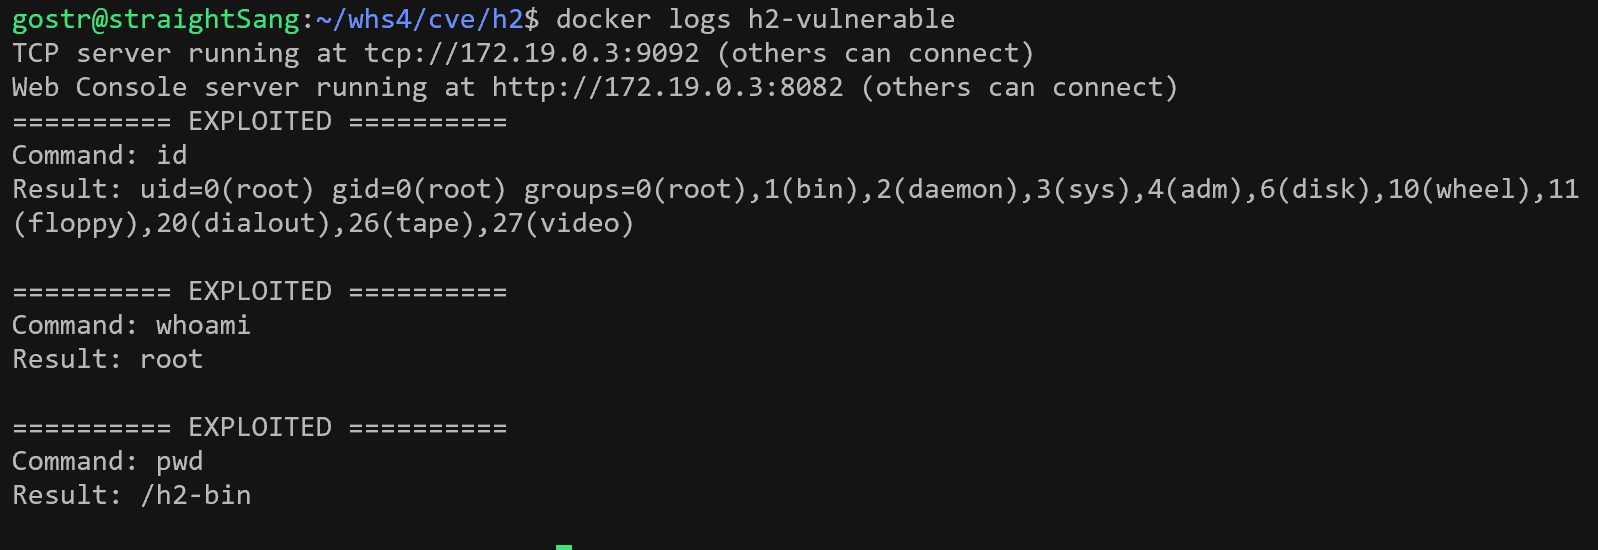 straightsang/h2-database-cve-2022-23221
vulhub/H2-database/CVE-2022-23221
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 hackspeak/cve-2026-14669
Proof-of-concept exploit for CVE-2026-14669, a PostgreSQL to_char() timezone abbreviation heap buffer overflow enabling RCE through information leak…
 686f6c61/poc-geoleak-cve-2026-52715
PoC funcional de CVE-2026-52715 (GeoLeak): SQLi no autenticada en GEO my WordPress <= 4.5.5 via swlatlng/nelatlng. Laboratorio Docker + exploit…
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 imbas007/poc-cve-2026-58048
Security research project