
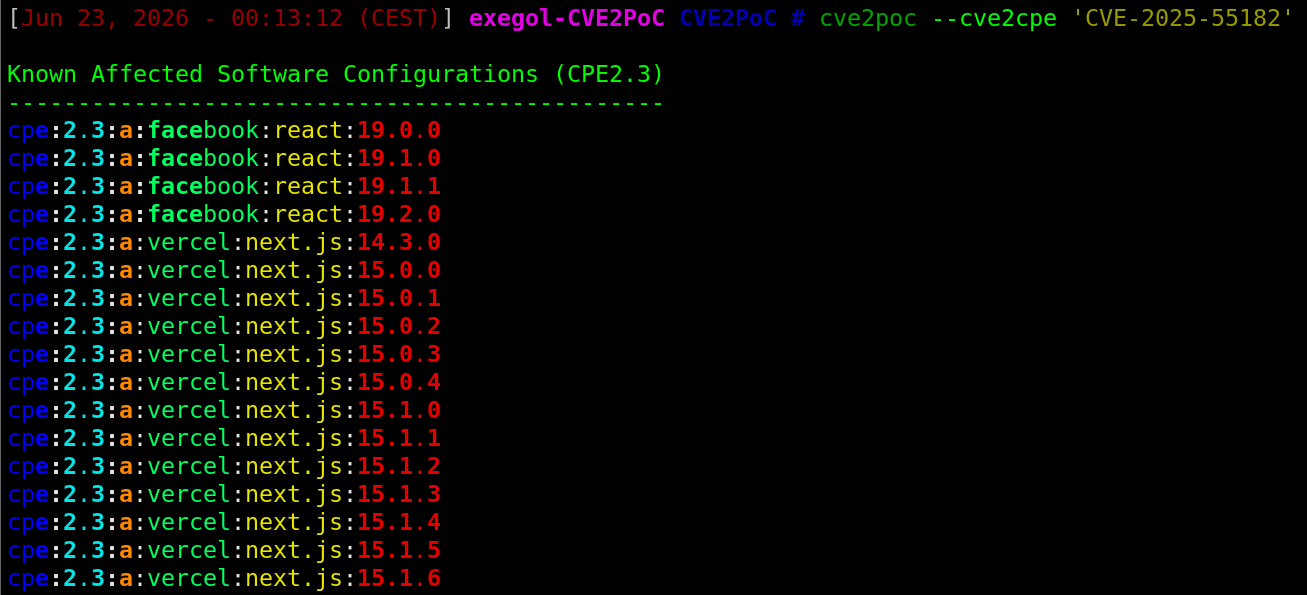
CVE2PoC
 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
educationexploitationinformation-gathering+5
145
0liverflow/cve2pocCVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
 ccchme/cve-2018-1058
Reproducible Docker-based demonstration of CVE-2018-1058 PostgreSQL privilege escalation via uncontrolled search path, with vulnerable and patched…
 80ottanta80/cve-2024-32019-poc
Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)
 trex96/vulnerable-bsr-lab-cve-2023-6933
Hands-on lab for CVE-2023-6933, a PHP Object Injection vulnerability in Better Search Replace WordPress plugin, with Docker deployment, nuclei…
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
 t0kx/exploit-cve-2015-1427
Elasticsearch 1.4.0 < 1.4.2 Remote Code Execution exploit and vulnerable container