
screenpipe
 screenpipe/screenpipe
YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
ctfcurated-resourceseducation+8
20.9k
screenpipe/screenpipeYC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
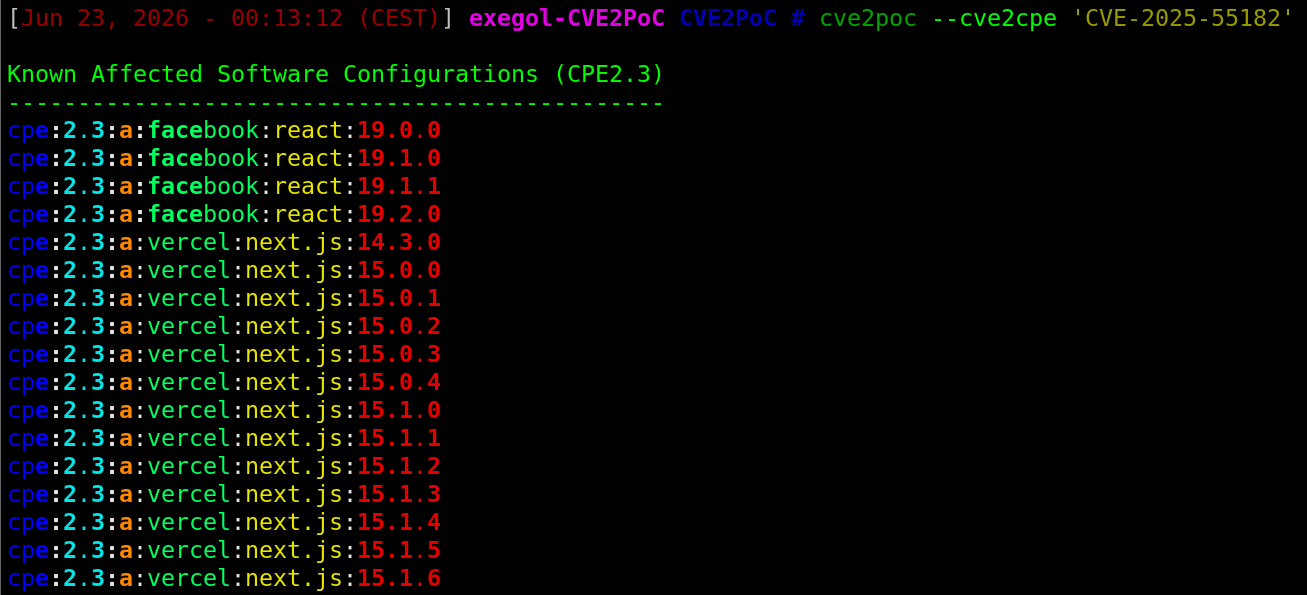 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 rdelasierra-uy/rag-seguridad
CyberRAG — RAG 100% local (Ollama) sobre apuntes y libros de ciberseguridad: recuperación híbrida, respuestas con citas, asistente de pentest por…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 abraxas/vsftpd-deny-file-brace-child
vsftpd 3.0.5 - High - Remote - Privilege leftover - brace deny_file misses .private/secret
 abraxas/sqlite-wal-pagesize
SQLite 3.53.4 - High - Local - Info leak - WAL/DB page-size mismatch uninitialized page tail
 abraxas/spark-rpc-stream-unauth
Apache Spark 4.2.0 - High - Remote - File read - unauth RPC StreamRequest File join
 abraxas/prometheus-unix-socket-dial
Prometheus v3.15.0 - High - Remote - SSRF - http_sd __unix_socket__ unsanitized Dial leftover of UDS scrape
 abraxas/openmeetings-wb-fileid-idor
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - WHITEBOARD fileId plant then room file resource serves bytes
 abraxas/openmeetings-kms-unauth
Apache OpenMeetings 9.1.0 - High - Remote - Unauth KMS - docs docker publishes Kurento JSON-RPC on 8888
 abraxas/openmeetings-invite-recording-acl
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - Type.USER invitation recording MP4 ACL
 abraxas/openmeetings-calendar-save-idor
Apache OpenMeetings 9.1.0 - High - Remote - IDOR - LOGIN calendar save overwrites appointment and closes public room
 abraxas/openlitespeed-dup-cookie-litespeed-role
OpenLiteSpeed 1.9.3 - High - Remote - Privilege leftover - HTTP/1 duplicate Cookie skips litespeed_role 403; lsphp still gets HTTP_COOKIE
 abraxas/nextcloud-federated-ocm-token
Nextcloud 35.0.0 — federated share secret is an unscoped app password for the sharer's whole Files tree
 abraxas/mysql-mysqldump-tab-path
MySQL Community Server 26.7.0 - High - mysqldump --tab path leftover - client file write
 abraxas/nextcloud-calendar-sharee-publish
Nextcloud 35.0.0 — a calendar edit-sharee can publish the owner's calendar to an unauthenticated URL
 abraxas/n8n-databricks-path-join
Proof-of-concept for an n8n path-traversal (CWE-22) in Databricks nodes: unauthenticated webhook input escapes the Genie path to leak workspace PAT…