
wrongsecrets
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
cloud-securitycontainer-securityctf+5
owasp/wrongsecretsVulnerable app with examples showing how to not use secrets
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
 athena-os/athena
Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
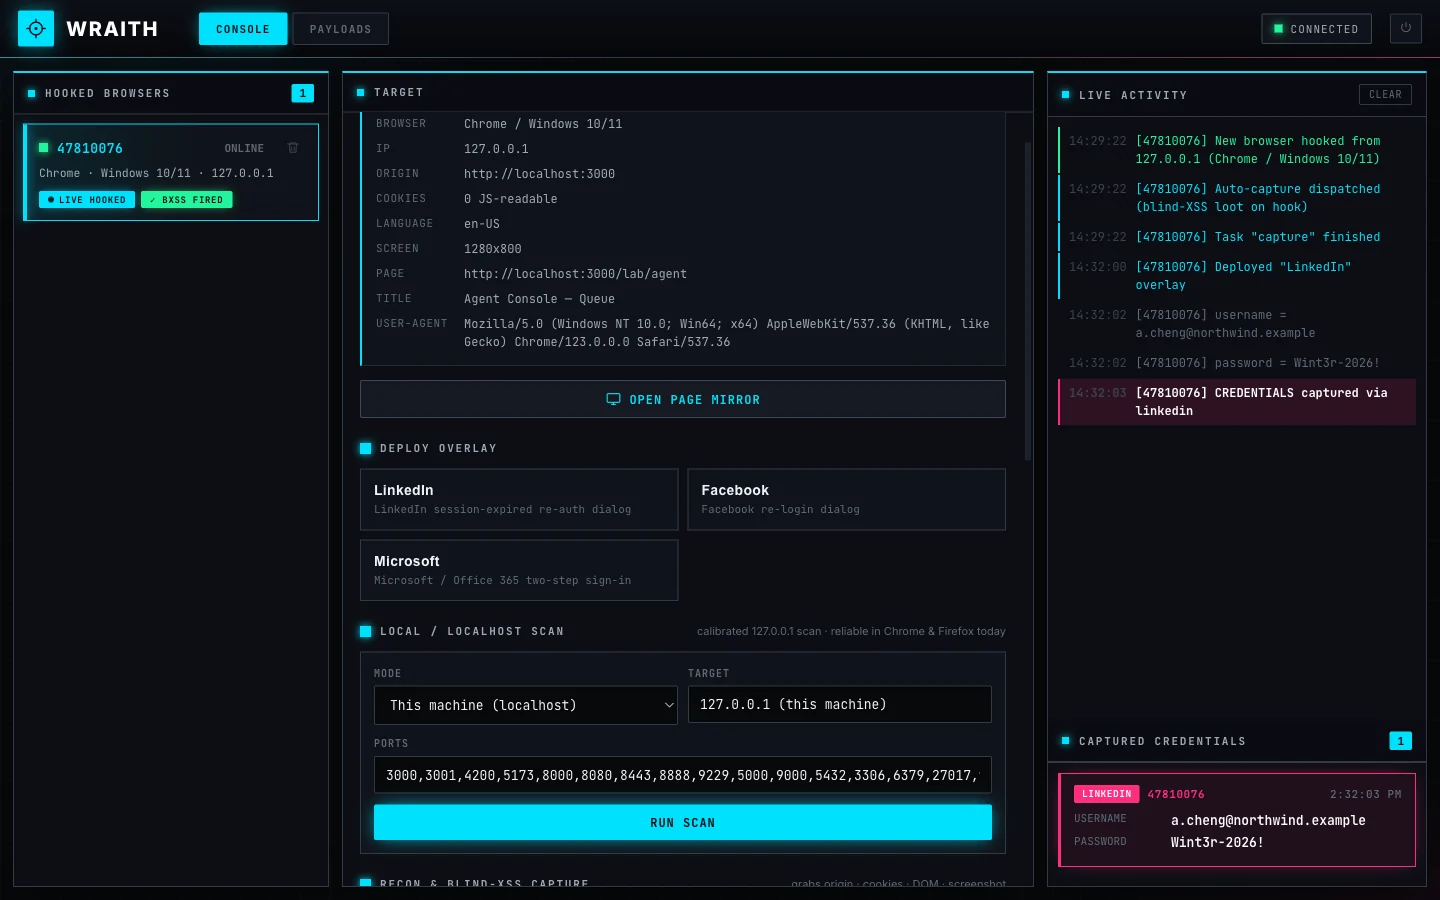 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
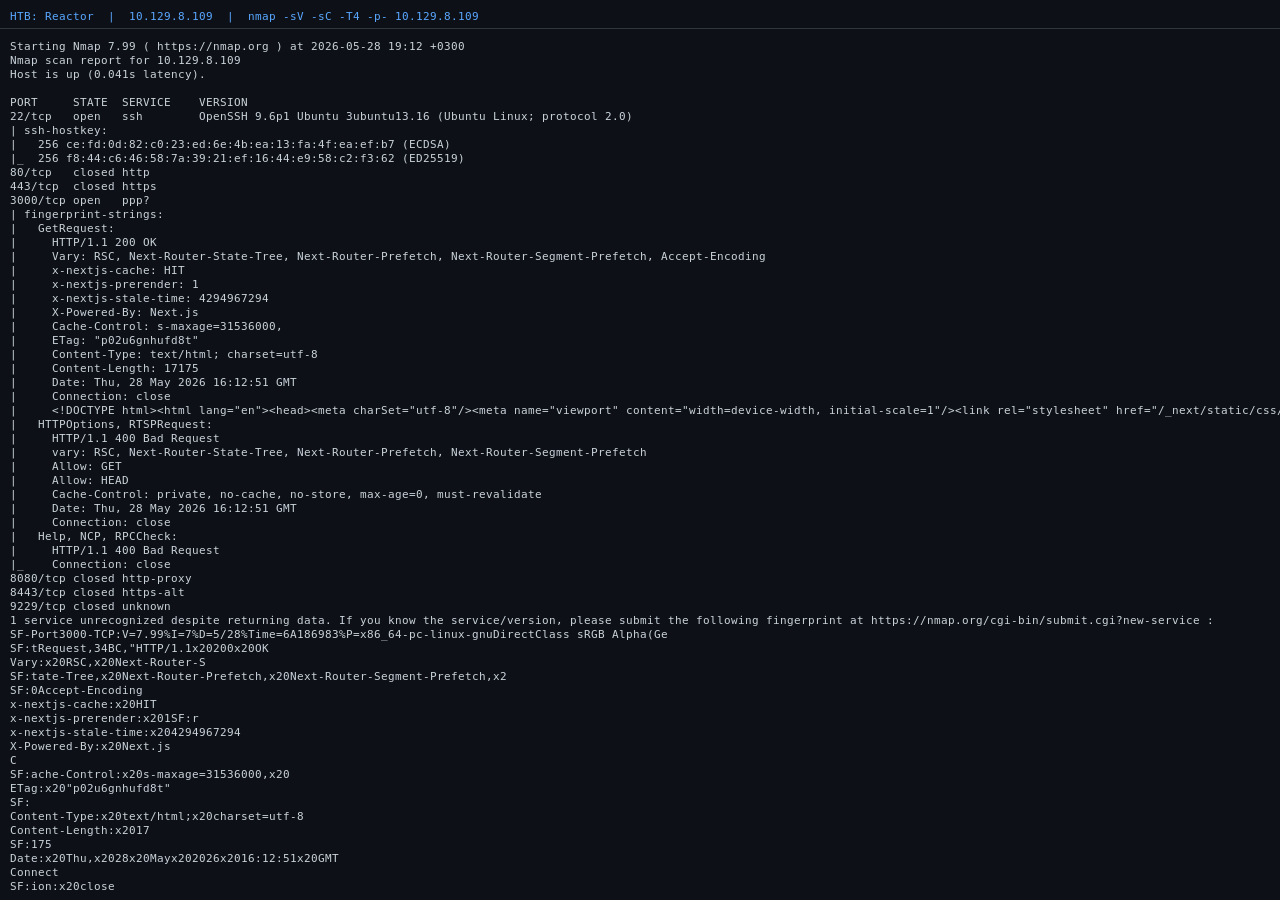 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 fineman999/poc_cve-2026-35037
Local isolated reproduction lab for CVE-2026-35037, an unauthenticated SSRF vulnerability in Ech0's GET /api/website/title endpoint. Includes Docker…
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
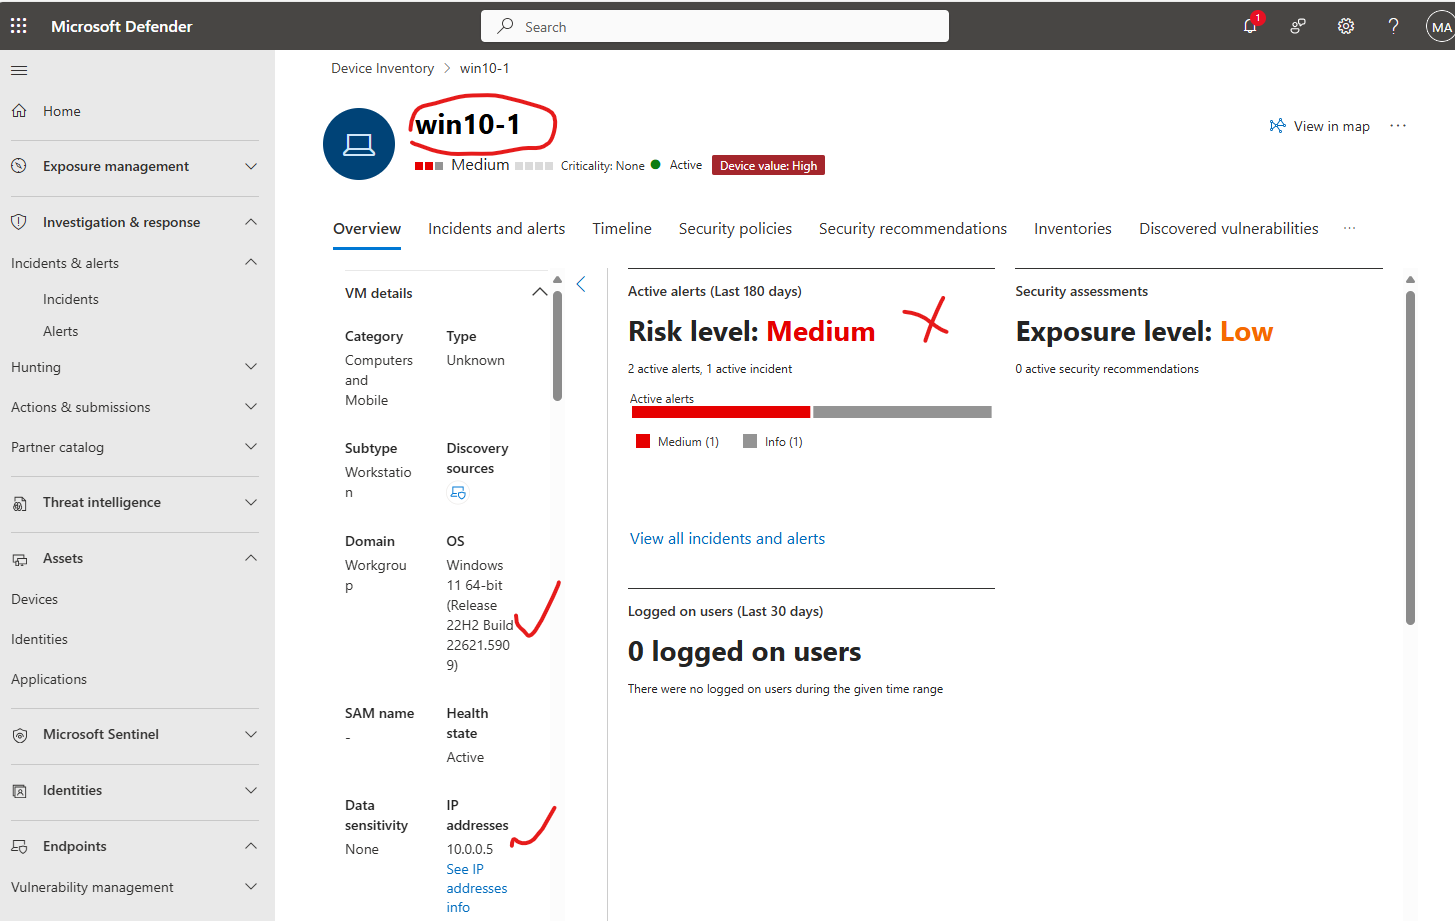 kamalideenak/microsoft-defender-for-endpoint-deployment-on-windows-10-11-device
This repository documents how deployment of Microsoft Defender for Endpoint on a Windows 11 device, including onboarding via local script, enabling…
 elw0od/pentesterlab
OrangeBadge - Exercise CVE-2018-6574: go get RCE
 astrowmist/poc-cve-2016-10033
Proof Of Concept for the CVE-2016-10033 (PHPMailer)
 mandiant/threatpursuit-vm
Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…
 tulhan/commons-text-goat
An intentionally vulnerable webapp to get your hands dirty with CVE-2022-42889.
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 kasunpriyashan/y2s1-project-linux-exploitaion-using-cve-2016-5195-vulnerability
Educational Linux privilege escalation exploit targeting CVE-2016-5195 (Dirty COW) to demonstrate kernel vulnerability exploitation and root access…