
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
CVE-2025-32433-LAB preview

CVE-2025-32433-LAB

GitHubdamnkrishna/cve-2025-32433-lab

A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
container-securityeducationexploitation+6
7 days ago
CVE-2026-85706 preview

CVE-2026-85706

GitHubsolivaquaant/cve-2026-85706

Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
data-exfiltrationexploitationinformation-gathering+7
15 days ago
CVE-2026-54433 preview

CVE-2026-54433

GitHubaramosf/cve-2026-54433

Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…

data-exfiltrationemail-securityexploitation+6
1 month ago
CVE-2026-11119-Padding-Oracle-Attack-on-CBC-Mode-Encryption preview

CVE-2026-11119-Padding-Oracle-Attack-on-CBC-Mode-Encryption

GitHubgeorge0papasotiriou/cve-2026-11119-padding-oracle-attack-on-cbc-mode-encryption

Demonstrates a padding oracle attack against AES-CBC encryption using a vulnerable Flask decrypt endpoint and a Python exploit script to decrypt…
cryptographyeducationexploitation+3
1 month ago
flowise-arbitrary-file-read-getFileFromStorage preview

flowise-arbitrary-file-read-getFileFromStorage

GitHubmajpuv/flowise-arbitrary-file-read-getfilefromstorage

Unauthenticated arbitrary file read in Flowise (< 2.2.4) via path traversal in getFileFromStorage (storageUtils.ts). Caused by un-sanitized file path…

data-exfiltrationexploitationinformation-gathering+4
1 month ago
sqlsure preview

sqlsure

GitHubsqlsure/sqlsure

Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…

code-analysiscurated-resourcesdatabase-security+5
992 months ago
CVE-2026-56782-Gorse-Auth-Bypass preview

CVE-2026-56782-Gorse-Auth-Bypass

GitHubbiitts/cve-2026-56782-gorse-auth-bypass

CVE-2026-56782 — Gorse <0.5.10 unauthenticated DB dump/restore (admin_api_key fail-open). Lab + PoC, verified e2e.

authenticationctfdata-exfiltration+6
12 months ago
metasploitable2-exploitation-metasploit preview

metasploitable2-exploitation-metasploit

GitHubethicalhackinglabs/metasploitable2-exploitation-metasploit

Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
command-and-controldata-exfiltrationeducation+9
3 months ago
cve-2026-54316-lab preview

cve-2026-54316-lab

GitHubinertfluid/cve-2026-54316-lab

Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)
ctfdata-exfiltrationeducation+5
13 months ago
CVE-2026-46300-Fragnesia---TryHackMe-Lab-Project preview

CVE-2026-46300-Fragnesia---TryHackMe-Lab-Project

GitHubbenedictejepu/cve-2026-46300-fragnesia---tryhackme-lab-project

The project documents the completion and analysis of the Fragnesia (CVE-2026-46300) TryHackME lab, which demonstrates a Linux kernel page -cache…
binary-exploitationeducationexploitation+3
3 months ago
DumpBrowserSecrets preview

DumpBrowserSecrets

GitHubmaldev-academy/dumpbrowsersecrets

Extracts browser-stored data such as refresh tokens, cookies, saved credentials, credit cards, autofill entries, browsing history, and bookmarks from…
data-exfiltrationdigital-forensicseducation+8
8143 months ago
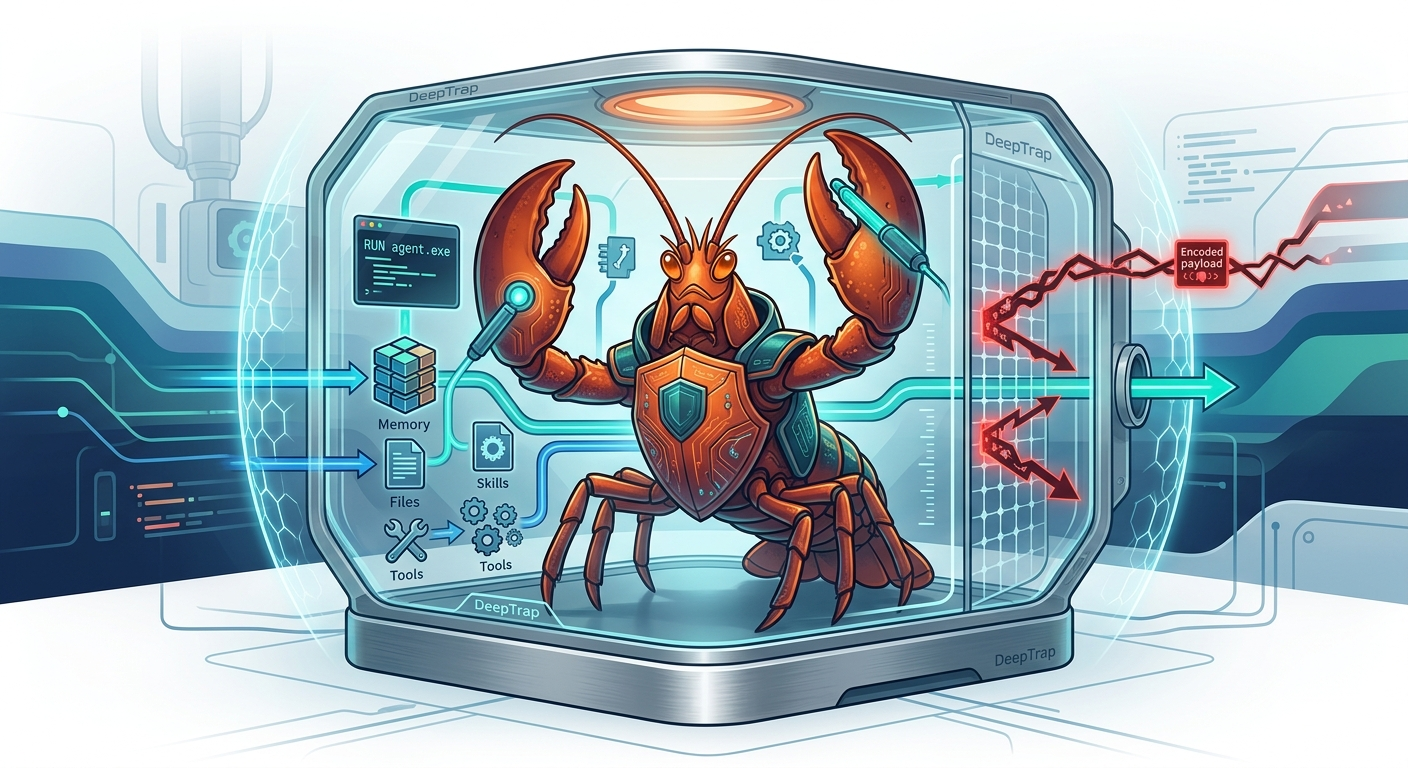
CVE-2017-10271 preview

CVE-2017-10271

GitHubdungsocool/cve-2017-10271

Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
binary-exploitationdata-exfiltrationeducation+7
4 months ago
DeepTrap preview

DeepTrap

GitHubzjuicsr/deeptrap

Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
adversarial-attackai-securitycommand-and-control+8
104 months ago
CVE-2026-35029-PoC preview

CVE-2026-35029-PoC

GitHublearner202649/cve-2026-35029-poc

The code for personally reproducing the corresponding vulnerability
data-exfiltrationeducationexploitation+4
4 months ago
C2-and-Post-Exploitation-Framework preview

C2-and-Post-Exploitation-Framework

GitHubjacobtaylor3/c2-and-post-exploitation-framework

CVE-2021-21220 Exploitation infrastructure
command-and-controldata-exfiltrationeducation+8
4 months ago
ghost-cve-2026-26980 preview

ghost-cve-2026-26980

GitHubdinosn/ghost-cve-2026-26980

CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
database-securityeducationexploitation+5
195 months ago
Drupal-Exploit-Lab preview

Drupal-Exploit-Lab

GitHubtea-celikik/drupal-exploit-lab

Demonstration on exploitation on Drupal 7.57 (CVE-2018-7600) with and without WAF(Web Application Firewall)

educationexploit-frameworkslabs-practice+3
7 months ago
CVE-2023-27372 preview

CVE-2023-27372

GitHubkiroloskhairy/cve-2023-27372

Safe PoC scanner and Docker lab for CVE-2023-27372, an RCE in SPIP CMS before 4.2.1. Verifies vulnerability via password recovery endpoint without…

educationexploitationlabs-practice+3
8 months ago
Previous123Next