

Web-App-PenTesting
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
educationlabs-practicepenetration-testing+4
sarthak4126/web-app-pentestingWeb application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 trailofbits/not-slithering-anywhere
The Python Version of our Not Go-ing Anywhere Vulnerable Application
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 srkyn/nginx-map-risk-audit
Defensive NGINX CVE-2026-42533 map regex risk audit with config scanner, Splunk/Defender notes, and lab evidence.
 owasp/serverless-goat
OWASP ServerlessGoat: a serverless application demonstrating common serverless security flaws
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
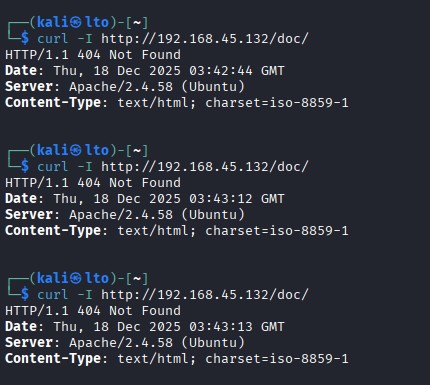 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 xxxtectationxxx/react2shell-cve-lab
A self-hosted vulnerable Next.js environment running on Docker for simulating CVE-2025-55182. Built for educational security research and CTF…
 cybervixy/vulnerability-management
NGINX Security Hardening & Vulnerability Remediation Analysis of critical CVEs (CVE-2021-23017, HTTP/2 DoS flaws) in outdated NGINX versions, with…
 soksofos/wazuh-nginx-cve-2026-42945-sca-lab
Centralized Wazuh SCA Assessment for CVE-2026-42945 on NGINX Servers
 zack0x01/vuln-app-cve-2025-55182
Intentionally vulnerable Next.js application demonstrating CVE-2025-55182 RCE via unsafe deserialization in React Server Components. Includes exploit…
 securekomodo/text4shell-poc
Proof of Concept Appliction for testing CVE-2022-42889
 m3ssap0/springbreakvulnerableapp
WARNING: This is a vulnerable application to test the exploit for the Spring Break vulnerability (CVE-2017-8046). Run it at your own risk!
 luisdalmolin/recon-test-livewire
Test target: fresh Laravel 12 app with Livewire pinned to vulnerable 3.6.3 (CVE-2025-54068) for recon scanning
 subzer0x0/react2shell
React2Shell (CVE-2025-55182) – An intentionally vulnerable Next.js application created for educational and research purposes.
 lhotari/log4shell-mitigation-tester
Test and validate Log4Shell (CVE-2021-44228) mitigation approaches with a sample vulnerable Log4j app, including JNDI exploitation, environment…
 limxuan/ehir-vuln-enterprise-login
Deliberately vulnerable web application portal with a containerized backend, designed for practicing exploitation of CVE-2021-44228 and container…