
PixelSmash
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
binary-exploitationeducationexploitation+6
se1ims/pixelsmashProof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
 superman-l/cve-2026-16723
Reproduces fastjson 1.2.83 @JSONType RCE with a vulnerable Spring Boot target and ASM-based payload generator using HTTP or file protocol jar chains.
 yuimamur/cve-2024-4367-hands-on-01
Hands-on lab for CVE-2024-4367, demonstrating PDF.js font rendering vulnerability exploitation in Firefox. Includes PoC generator, vulnerable and…
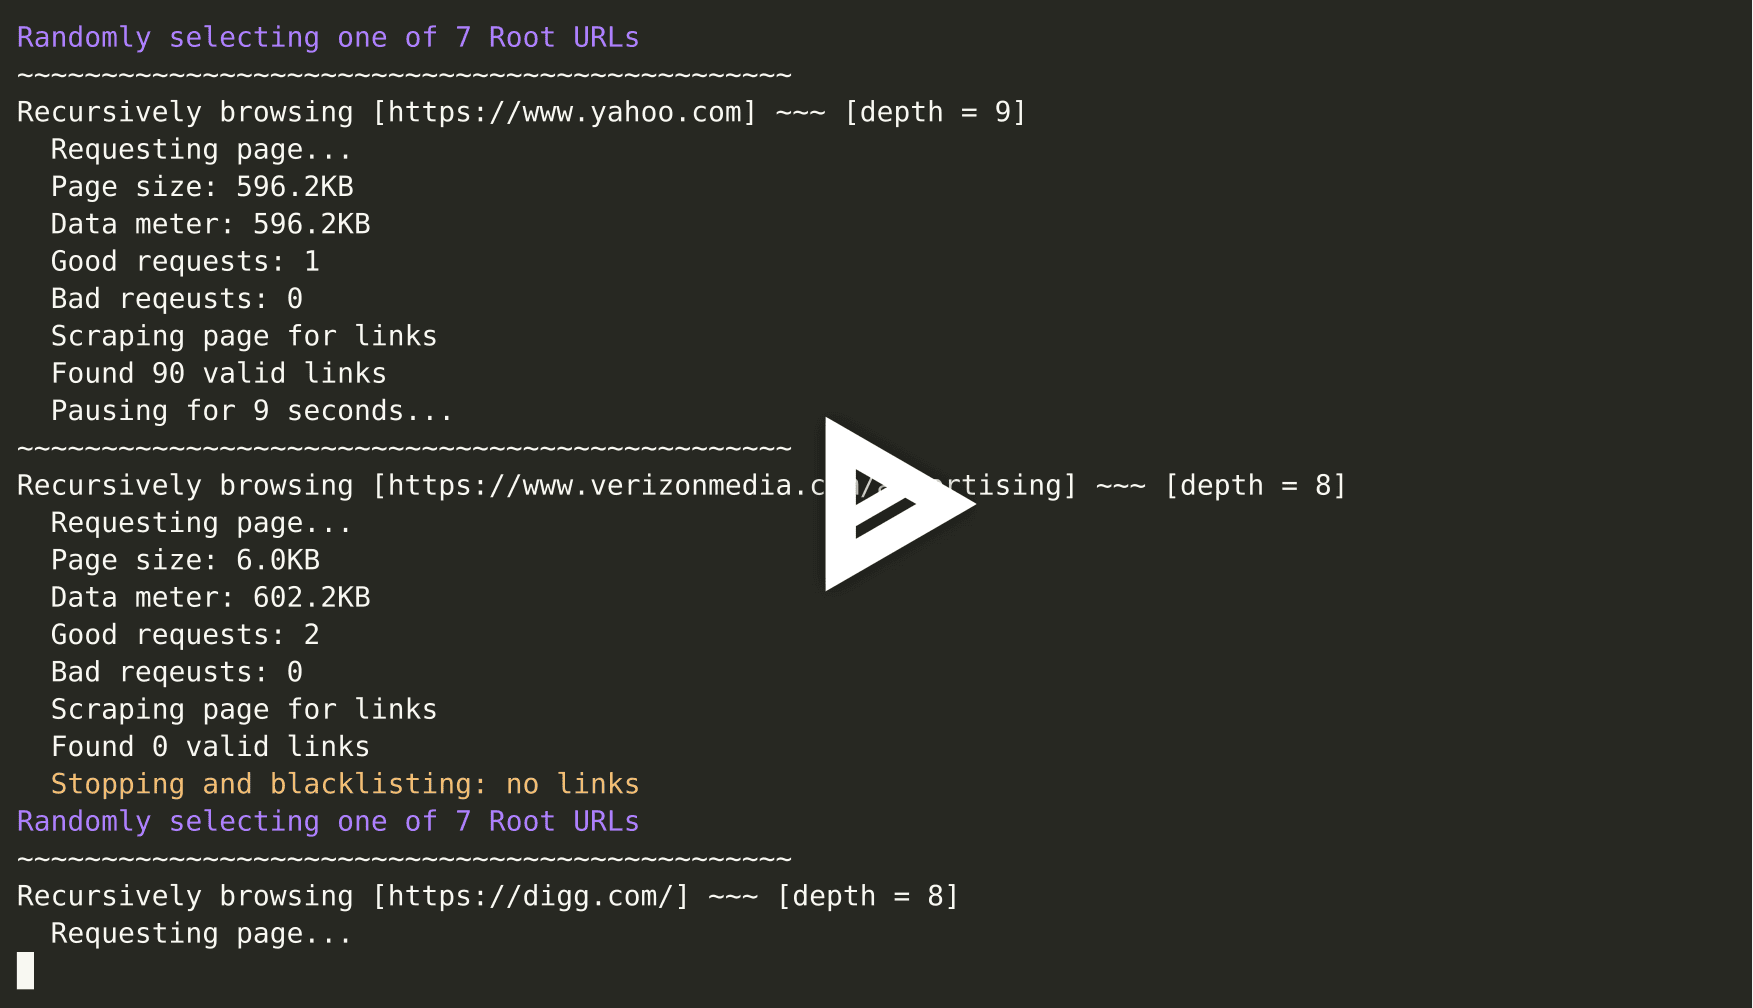 reconinfosec/web-traffic-generator
A quick and dirty HTTP/S "organic" traffic generator.
 m0d0ri205/wargame_re-ls
CTF challenge exploiting CVE-2025-0184 DOCX SSRF vulnerability to access internal admin service and retrieve a flag. Includes exploit generator and…
 qafdevsec/cve-2019-9081_poc
PoC exploit for CVE-2019-9081 targeting Laravel deserialization RCE. Includes a pre-built vulnerable Laravel 5.7.x application and payload generator…
 llamaonsecurity/cve-2018-12533
Payload generator and proof-of-concept exploit for CVE-2018-12533 (Richfaces deserialization/EL injection) with Docker-based vulnerable environment…
 bohemian-miser/cve-2025-65018_exploit_challenge
CTF challenge exploiting a heap overflow in libpng's png_image_finish_read to overwrite a function pointer and spawn a shell, with build scripts and…
 cs4239-u6/node-pdf-generator-ssrf
An example of CVE-2020-7740
 quevatech/challenge_repo
Structured challenge repository offering bounties for breaking a neural-network-based random number generator validated against NIST SP 800-22 and SP…