
CVE-2026-24841_Range
 otakuliu/cve-2026-24841_range
Simulation environment for CVE-2026-24841, providing a realistic vulnerable setup for security testing and educational purposes, especially for…
educationexploitationlabs-practice+2
otakuliu/cve-2026-24841_rangeSimulation environment for CVE-2026-24841, providing a realistic vulnerable setup for security testing and educational purposes, especially for…
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
 ooooooo-q/cve-2022-32224-rails
Proof-of-concept exploit for CVE-2022-32224: Rails ActiveRecord serialized column RCE. Demonstrates YAML deserialization leading to arbitrary class…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 matiasarenhard/rails-cve-2017-17917
Educational demonstration of CVE-2017-17917 SQL injection in Rails, with step-by-step replication and secure coding mitigation using parameterized…
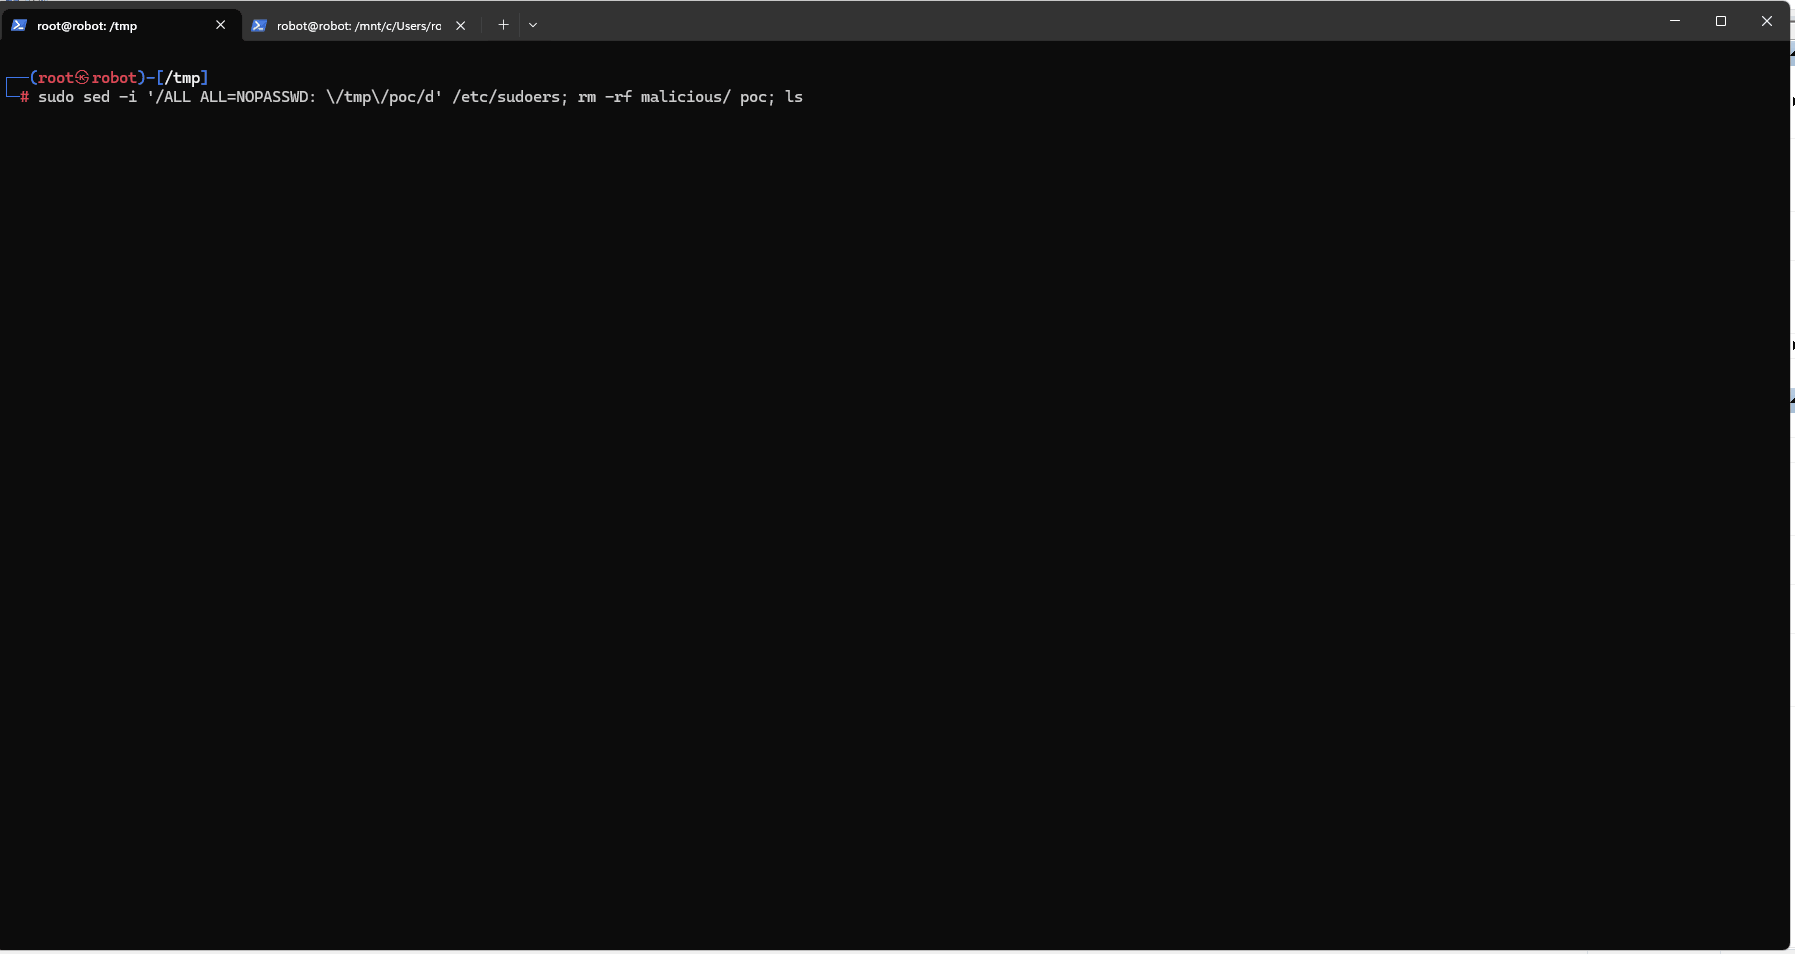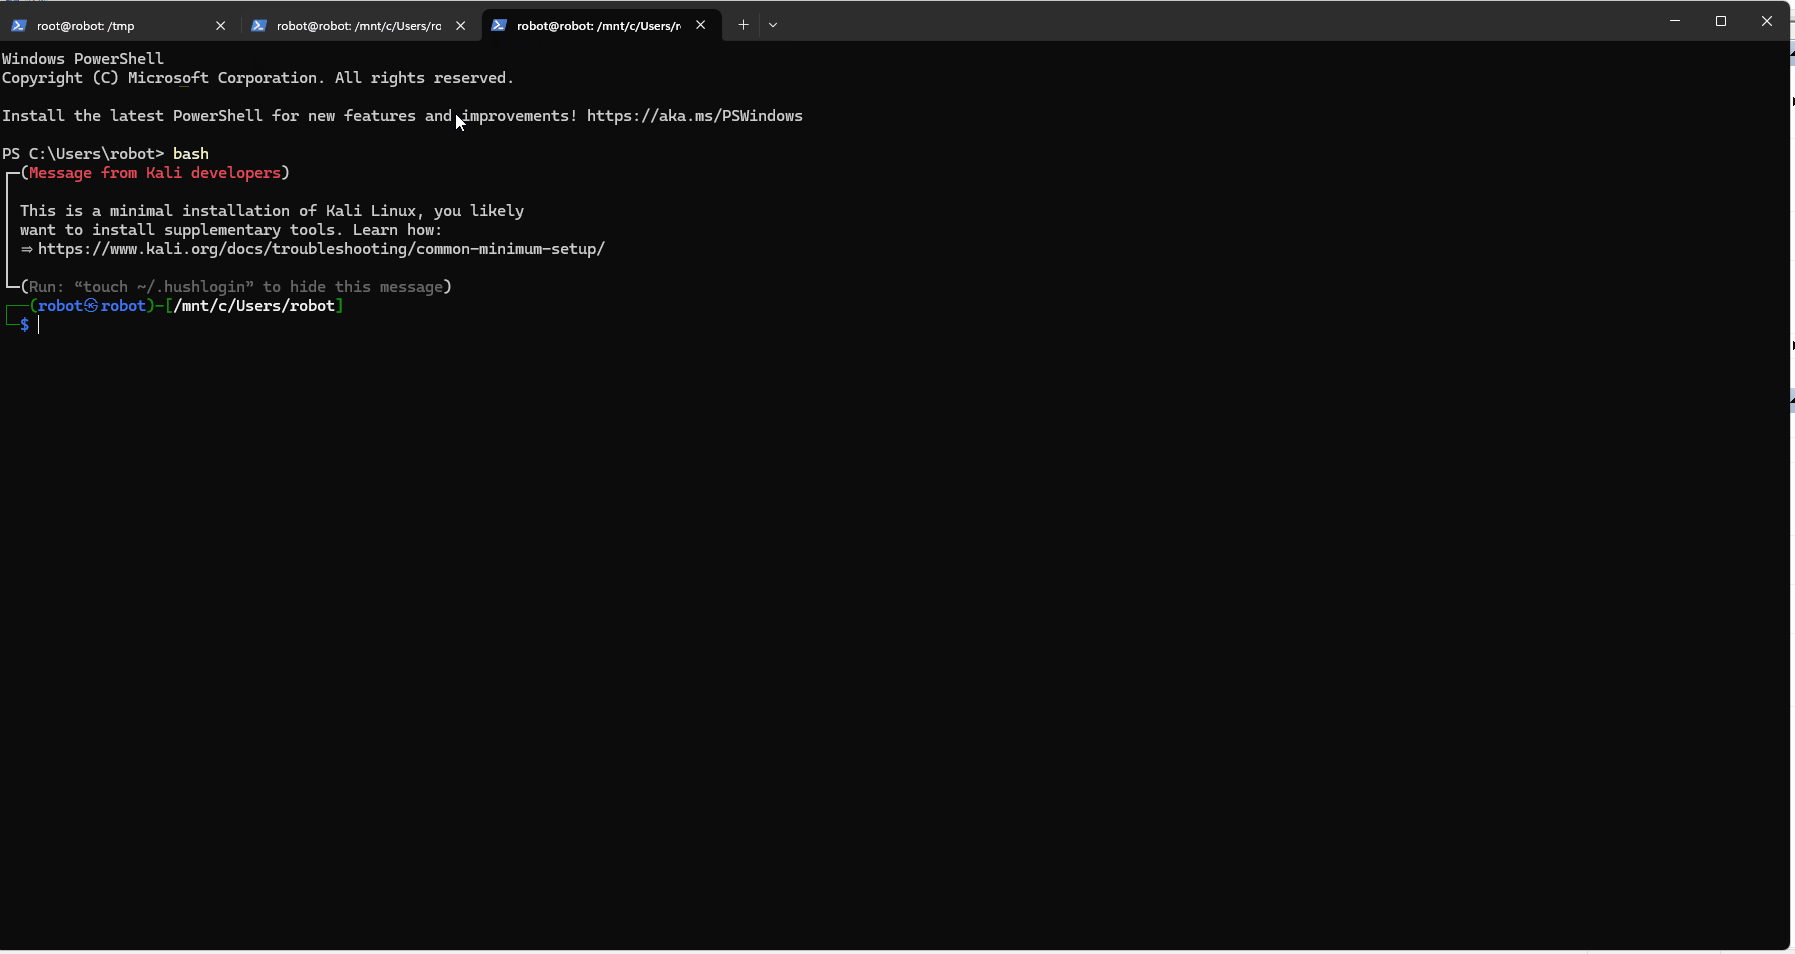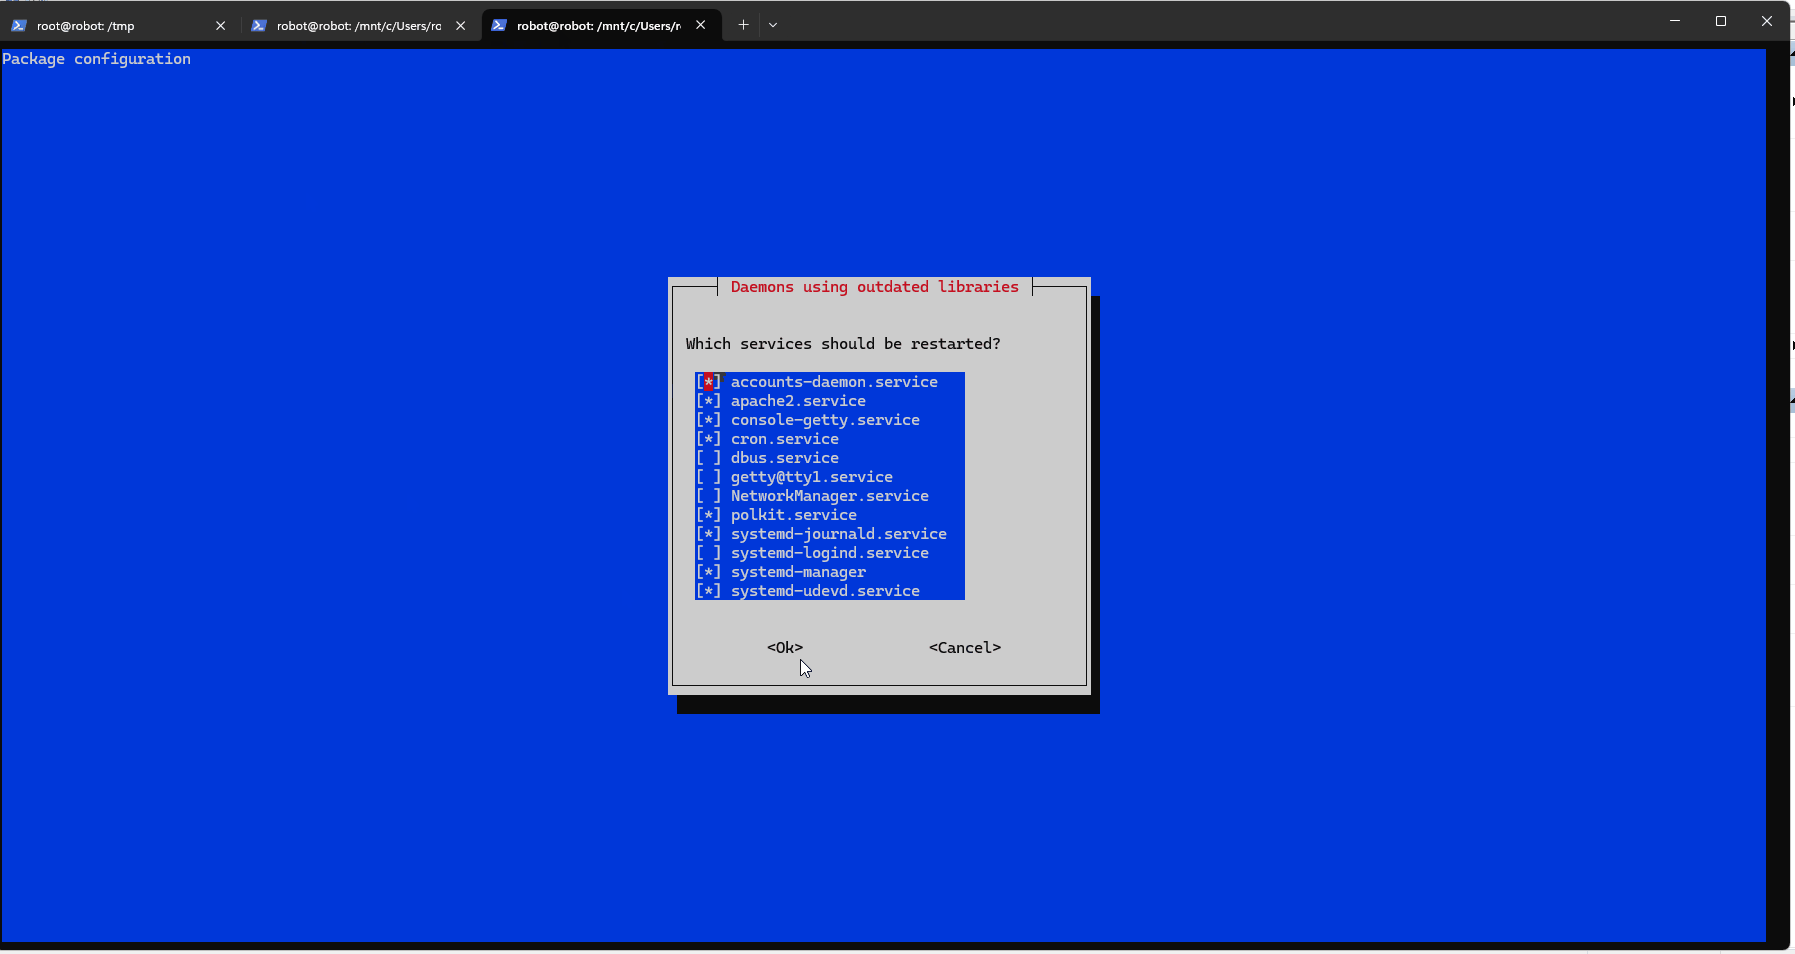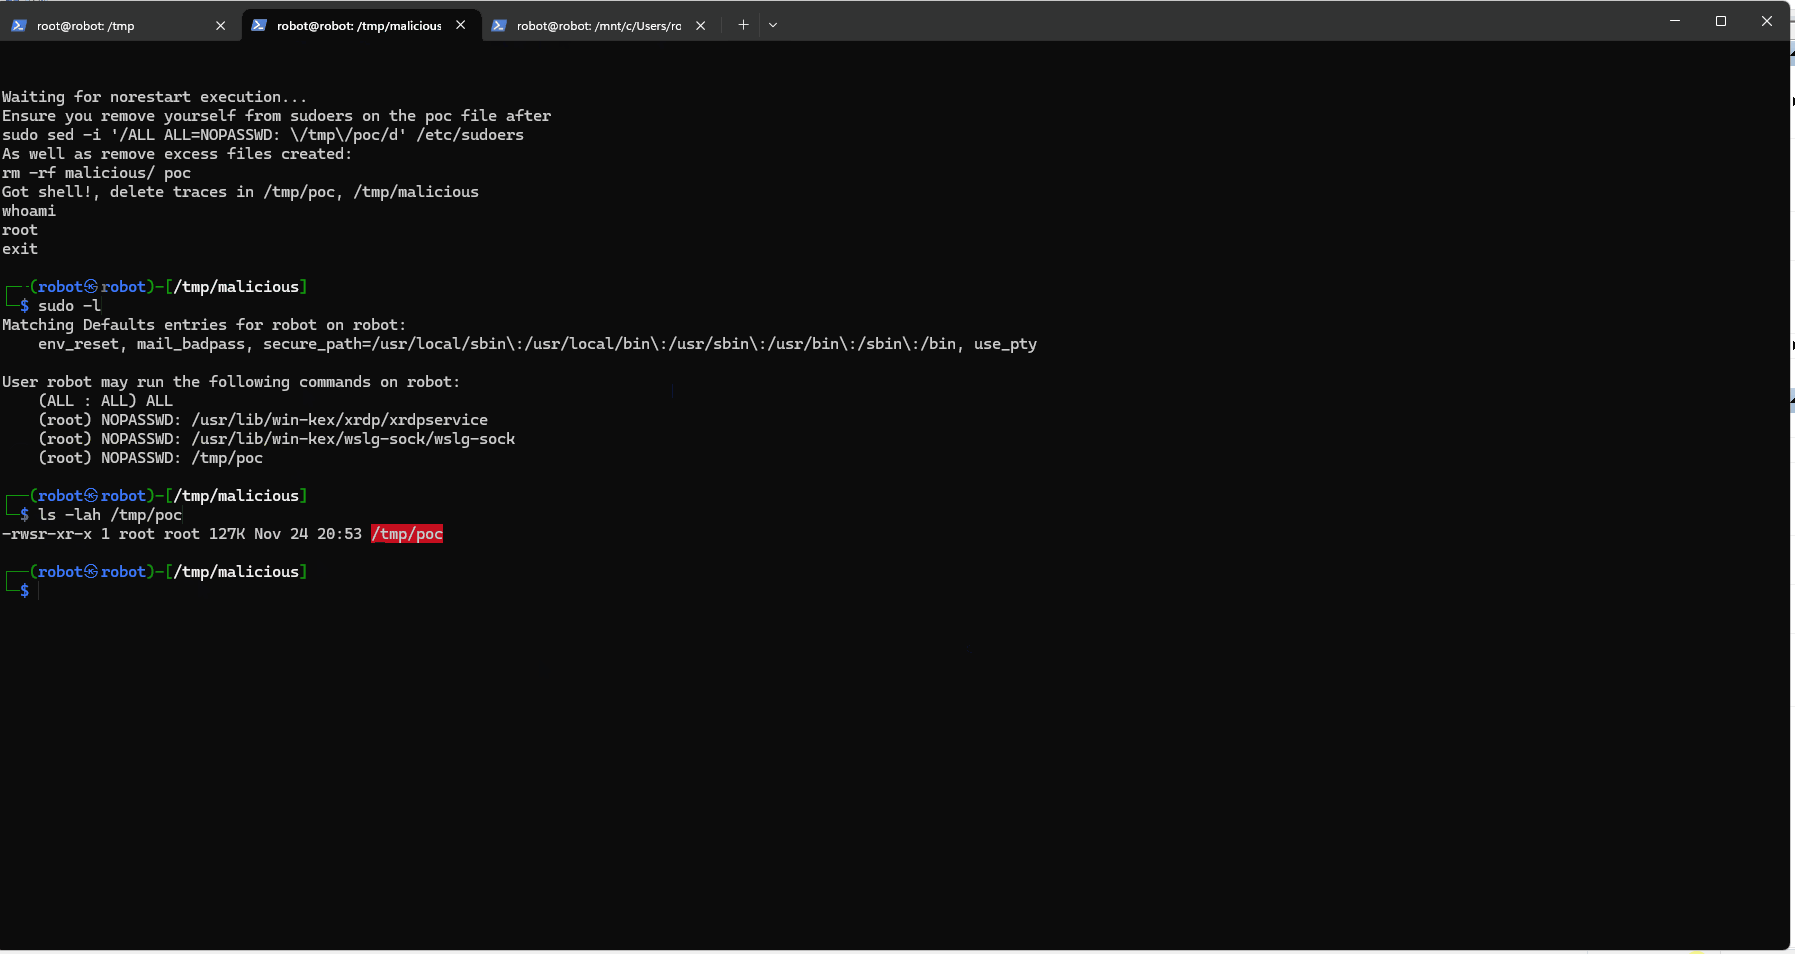 pentestfunctions/cve-2024-48990-poc-testing
Testing POC for use cases
 lucasamorimca/cve-2020-8163
CVE-2020-8163 - Remote code execution of user-provided local names in Rails
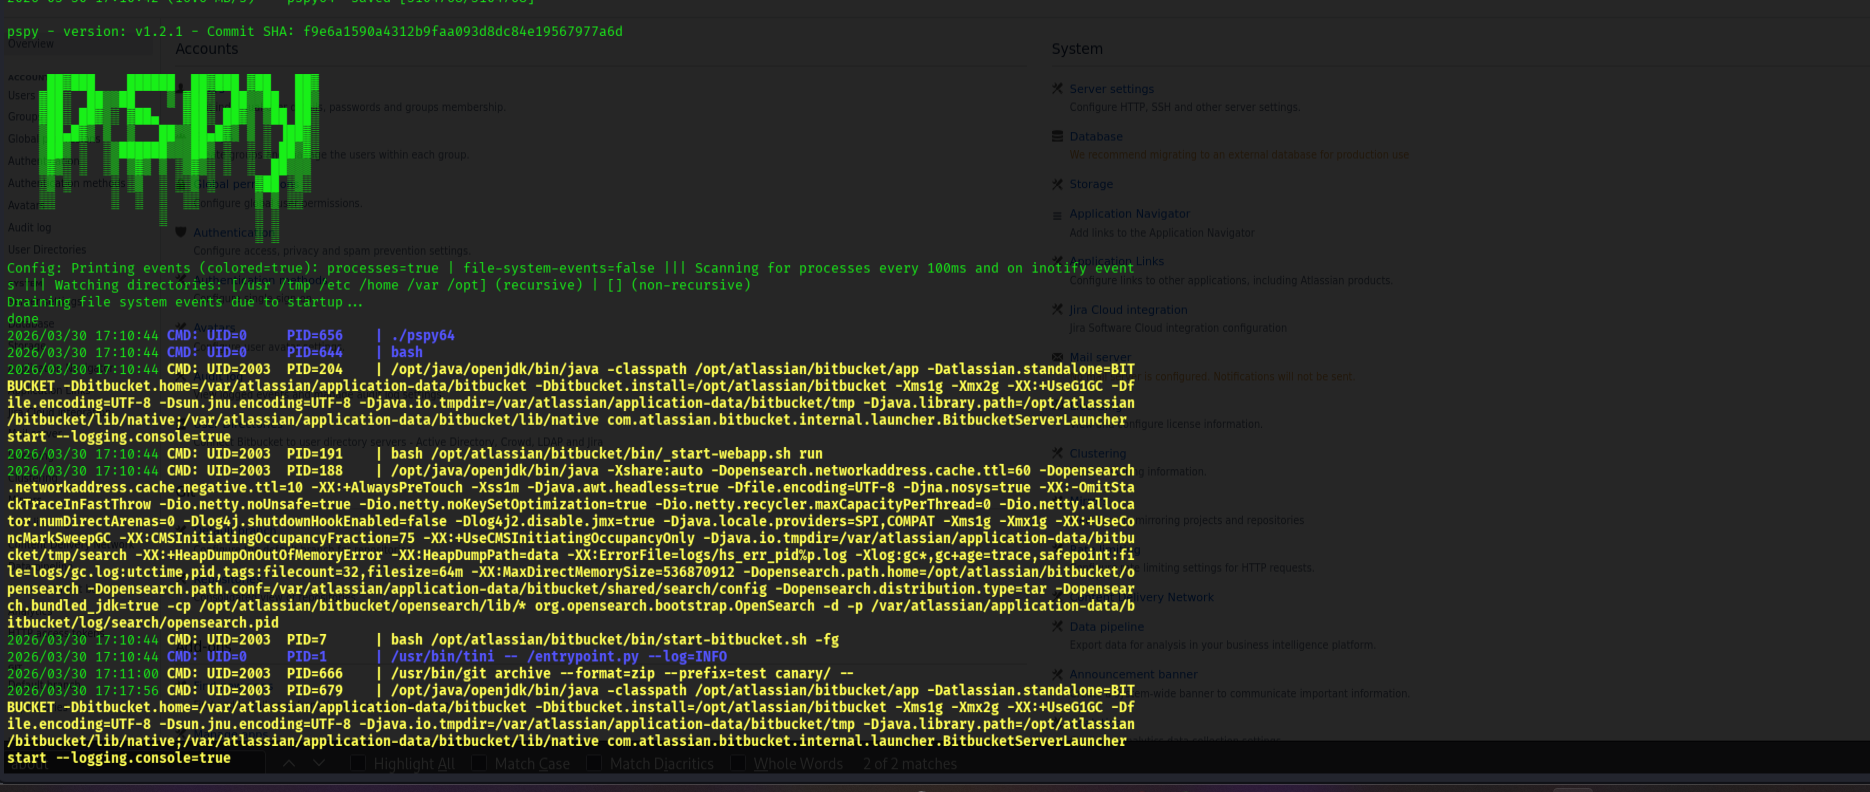 johangabrielson/bitbucket-test
Investigating CVE-2022-36804
 h4ms1k/cve-2020-8163
Docker-based lab environment and exploit script for CVE-2020-8163, a blind remote code execution vulnerability in Rails versions before 5.0.1 and…
 dhmosfunk/http3onsteroids
PoC and lab environment for CVE-2023-25950: HTTP request smuggling via malformed header fields in HAProxy's HTTP/3 implementation, enabling DoS and…
 daehyeok0618/cve-2019-5418
Docker-based lab environment for CVE-2019-5418 Ruby on Rails path traversal exploit, with PoC curl commands to read arbitrary server files via…
 cyberharsh/ruby-on-rails-path-traversal-vulnerability-cve-2018-3760-
Docker-based lab demonstrating CVE-2018-3760 path traversal in Ruby on Rails Sprockets, with POC and environment setup for security testing and…
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
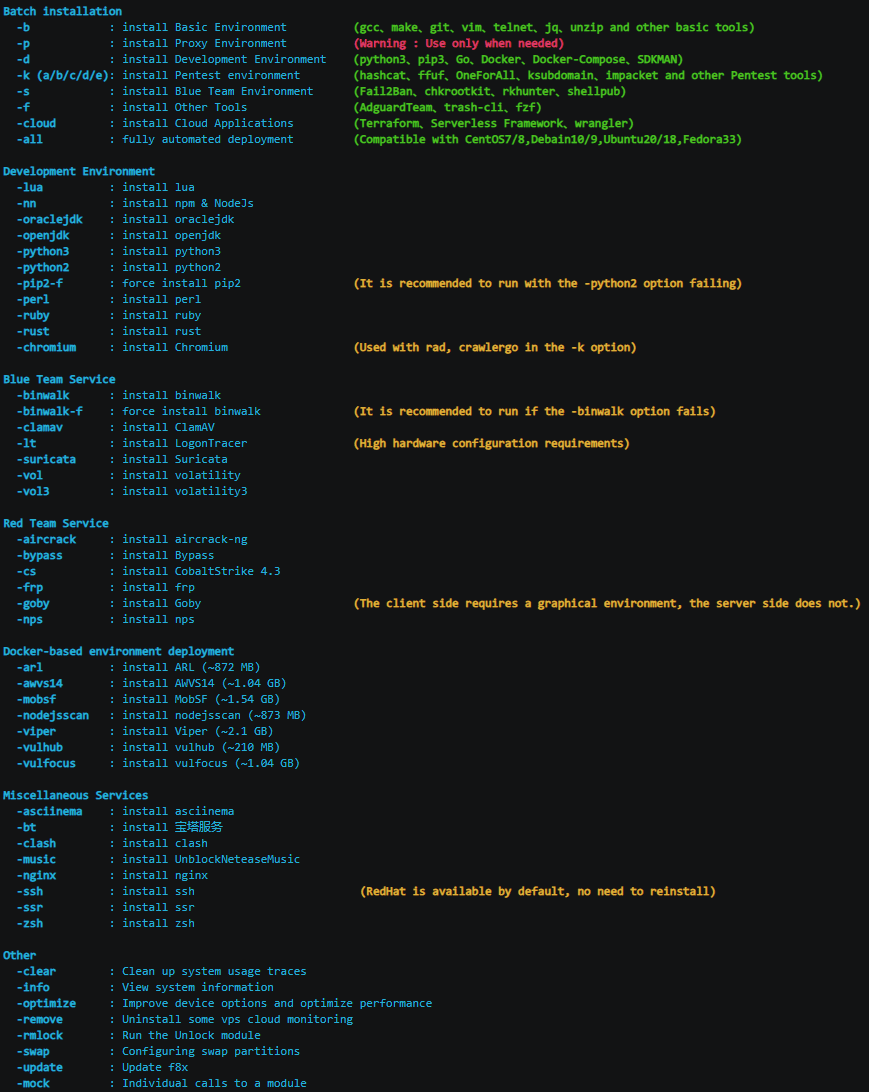 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool