
All-In-One-CyberSecurity-Resources
 vatsalgupta67/all-in-one-cybersecurity-resources
List of CyberSecurity Resources and some different Sub-Domains of CyberSecurity
ctfcurated-resourceseducation+9
610
vatsalgupta67/all-in-one-cybersecurity-resourcesList of CyberSecurity Resources and some different Sub-Domains of CyberSecurity
 hunterdii/tryhackme-roadmap
Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
 lhiebert01/network-attack-simulator
Streamlit educational dashboard that simulates port scanning, DoS, brute force and data exfiltration attacks, with visualizations, attack logs and…
 zishanadthandar/pentest
Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…
 dev-angelist/ejptv2-notes
eLearnSecurity Junior Penetration Tester (eJPT) v2 Notes
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
 abraxas/php-oom-longjmp
PHP 8.4.26 - Critical - Remote - OOM longjmp - CVE-2026-109618 PHP2Shell. Unauth chunked multipart hits memory_limit before app code on Apache…
 abraxas/php-stale-global-uaf
PHP 8.5.11 - Critical - Remote - UAF - CVE-2026-109619 PHP2Shell. Same-worker fatal backtrace then INI diagnostic on Apache mod_php. Lab vs 8.5.12.…
 horkimhab/cve-2026-109618-619
Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 ko0ler/homelab
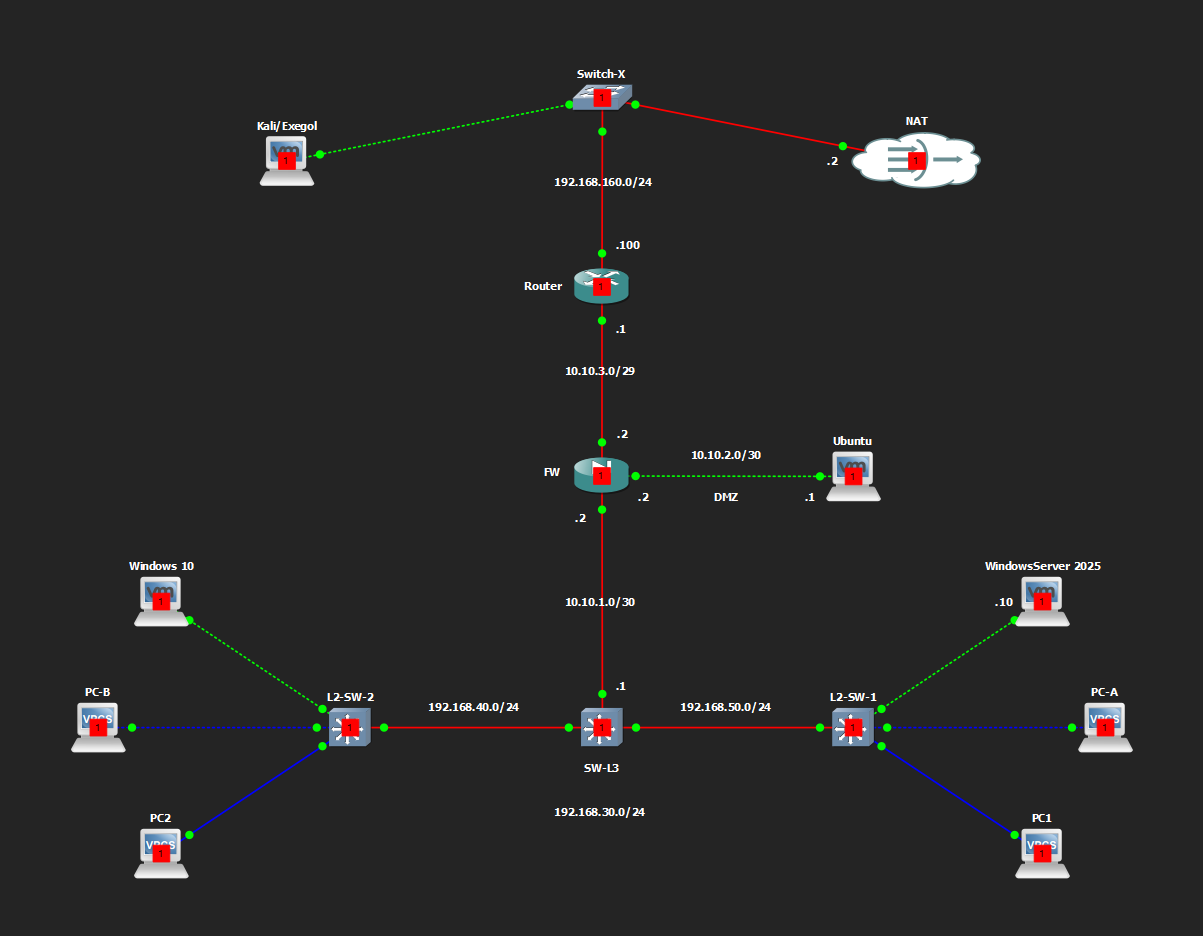
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 rdelasierra-uy/rag-seguridad
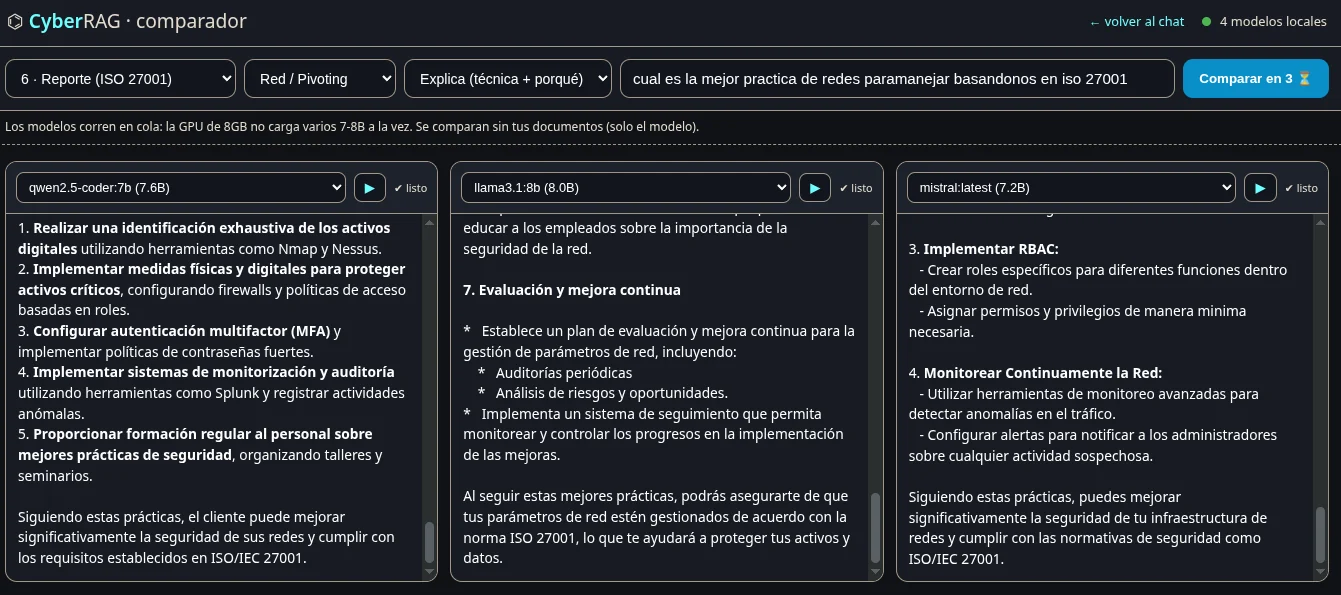
CyberRAG — RAG 100% local (Ollama) sobre apuntes y libros de ciberseguridad: recuperación híbrida, respuestas con citas, asistente de pentest por…
 liquid-sec/variatype.htb-cve-2025-66034
Python exploit script for CVE-2025-66034 in the HackTheBox Variatype machine, delivering command execution and reverse shell payloads for initial…
 horkimhab/cve-2026
Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
 vighnesh91/severitas
Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…
 saqibnet/blackbox-pentesting-infsecos
Full black-box penetration test against SecOS:1 (VulnHub) — CSRF exploitation, privilege escalation via CVE-2015-1328 (OverlayFS), post-exploitation
 nth347/struts2-cve-2013-2251
Vulnerable environment of CVE-2013-2251 (S2-016) for testing