

redStack
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
cloud-infrastructure-securitycommand-and-controleducation+8
286
devzero-security/redstackTerraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
 aniket2912/internal-network-penetration-testing
Educational module on internal network penetration testing: methodology, attack vectors, enumeration, exploitation, privilege escalation, and…
 abraxas/php-oom-longjmp
PHP 8.4.26 - Critical - Remote - OOM longjmp - CVE-2026-109618 PHP2Shell. Unauth chunked multipart hits memory_limit before app code on Apache…
 abraxas/php-stale-global-uaf
PHP 8.5.11 - Critical - Remote - UAF - CVE-2026-109619 PHP2Shell. Same-worker fatal backtrace then INI diagnostic on Apache mod_php. Lab vs 8.5.12.…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 abraxas/superset-g3-v0-import-sql-plant
Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…
 abraxas/openmeetings-kms-unauth
Apache OpenMeetings 9.1.0 - High - Remote - Unauth KMS - docs docker publishes Kurento JSON-RPC on 8888
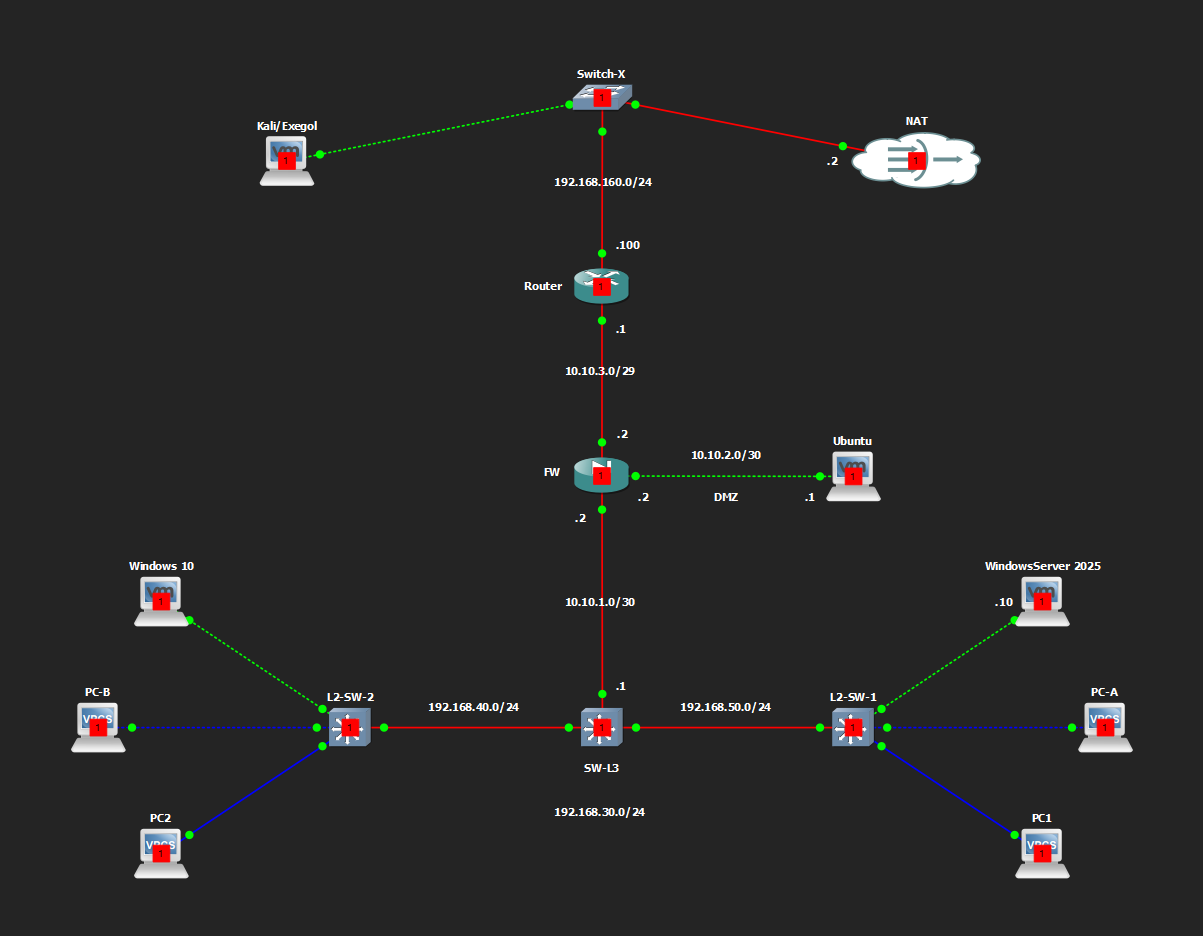 ko0ler/homelab
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 abraxas/phpmyadmin-csrf-sql
phpMyAdmin 5.2.3 - High - Remote - CSRF - token strip on /sql
 abraxas/prometheus-bearer-redirect
Prometheus v3.15.0 - High - Remote - Credential leak - remote_write google_iam/azuread forwards Bearer on cross-host 3xx
 y198nt/nginx-chain-rift-poolslip
ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 cyb3rmik3/prompt-injection-email-samples
Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…
 euph00/zoneclaw-code
Benchmark and defense code for persistent memory attacks on OpenClaw-style computer-use agents, with memory-zoning mitigation, attack scenarios, and…
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 mgiftson0/linux-env-vars-shellshock-lab
technical research & analysis on linux process execution, SUID privilege escalation, LD_PRELOAD hooking, and CVE-2014-6271 (shellshock).