
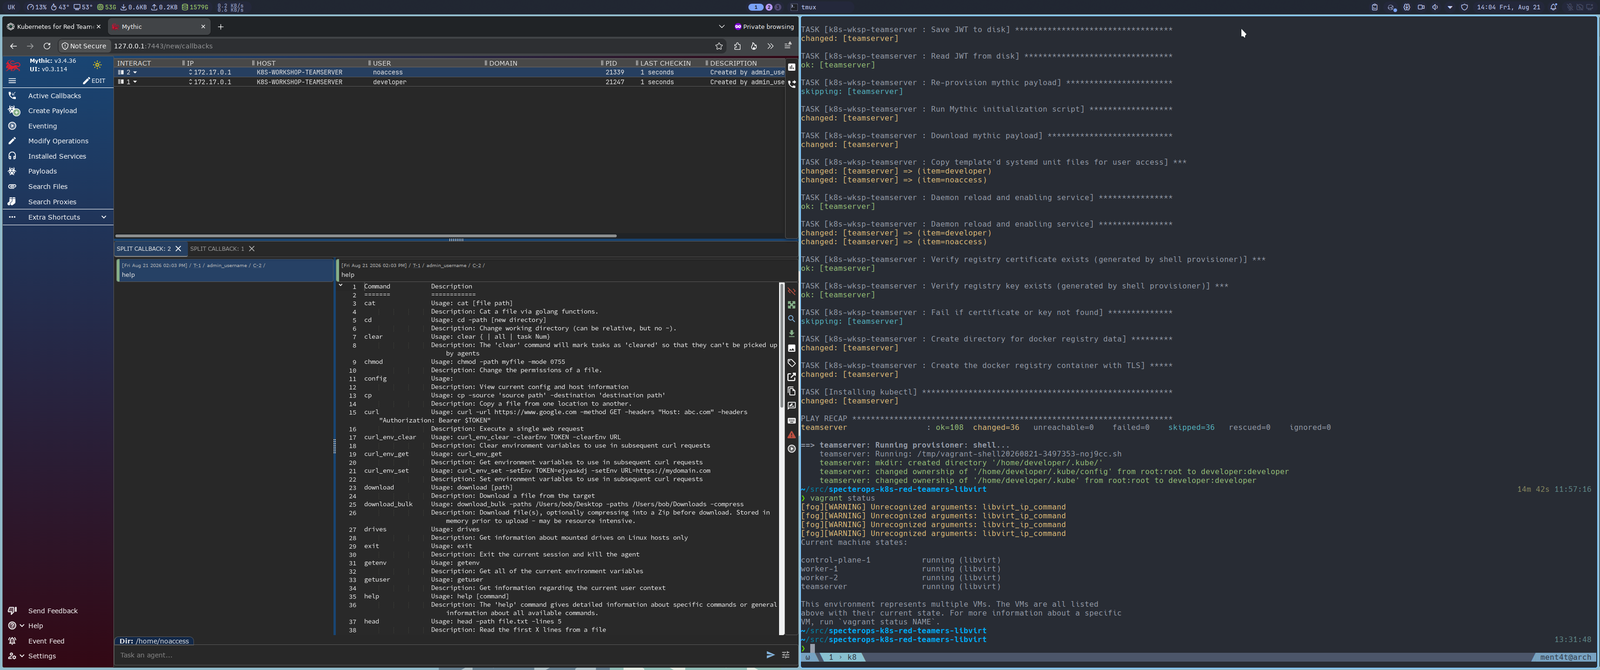
specterops-k8s-red-teamers-libvirt-patch
 gregdurys/specterops-k8s-red-teamers-libvirt-patch
Unofficial libvirt patch for the free SpecterOps Kubernetes for Red Teamers lab
cloud-securityeducationlabs-practice+1
gregdurys/specterops-k8s-red-teamers-libvirt-patchUnofficial libvirt patch for the free SpecterOps Kubernetes for Red Teamers lab
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
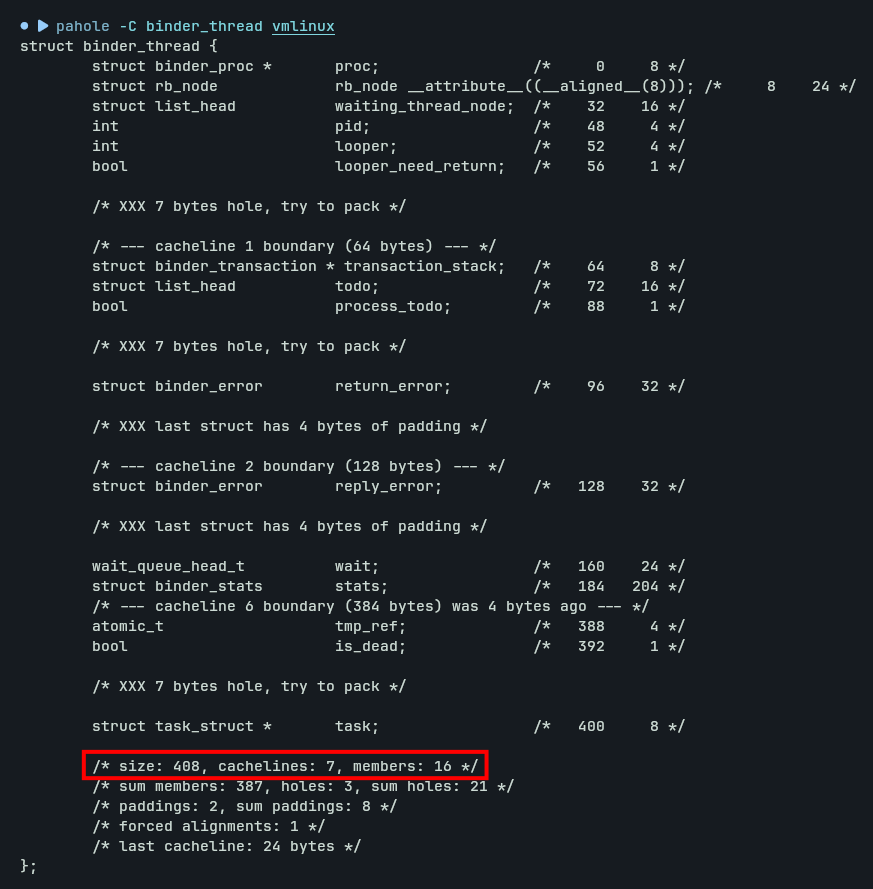 0xbinder/cve_2019_2215
Proof-of-concept LPE exploit for Android Binder UAF that uses iovec spraying and addr_limit overwrite to achieve arbitrary kernel read/write.
 joe-shenouda/awesome-cyber-skills
A curated list of hacking environments where you can train your cyber skills legally and safely
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 why-success/fastjson-rce-lab
Fastjson 1.2.83 RCE 靶场环境 (CVE-2026-16723)
 secfigo/awesome-fuzzing
A curated list of fuzzing resources ( Books, courses - free and paid, videos, tools, tutorials and vulnerable applications to practice on ) for…
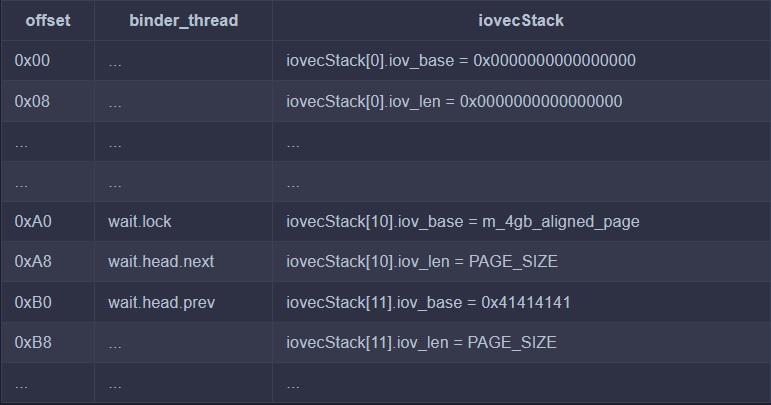 sharif-dev/androidkernelvulnerability
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
 h4r335hr/vsftpd-234-backdoor
Dependency-free interactive Python exploit for the vsftpd 2.3.4 backdoor (CVE-2011-2523).
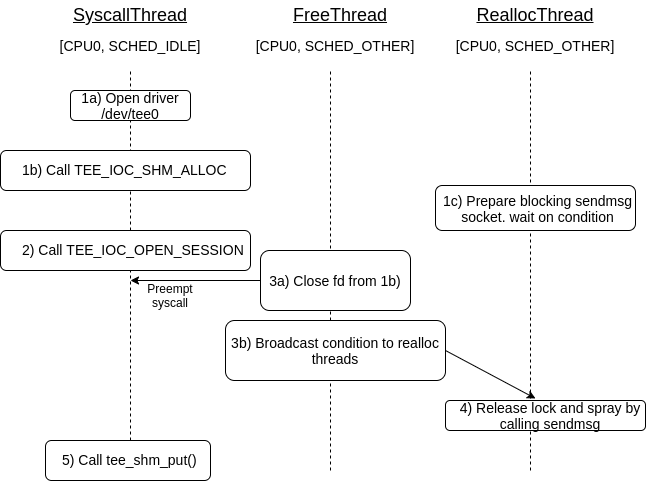 pjlantz/optee-qemu
Environment with vulnerable kernel for exploitation of the TEE driver (CVE-2021-44733)
 vn-lazyming/cve-2026-52943
This is a Linux Kernel Local Privilege Escalation PoC code for CVE-2026-52943 a use-after-free in skbuff.c, my first 0day found by me in linux kernel
 uky007/cve-2025-62215_analysis
CVE-2025-62215 exploit development using Claude Code Agent Team
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 hunt3r850/cve-2024-10924-wordpress-docker
Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…
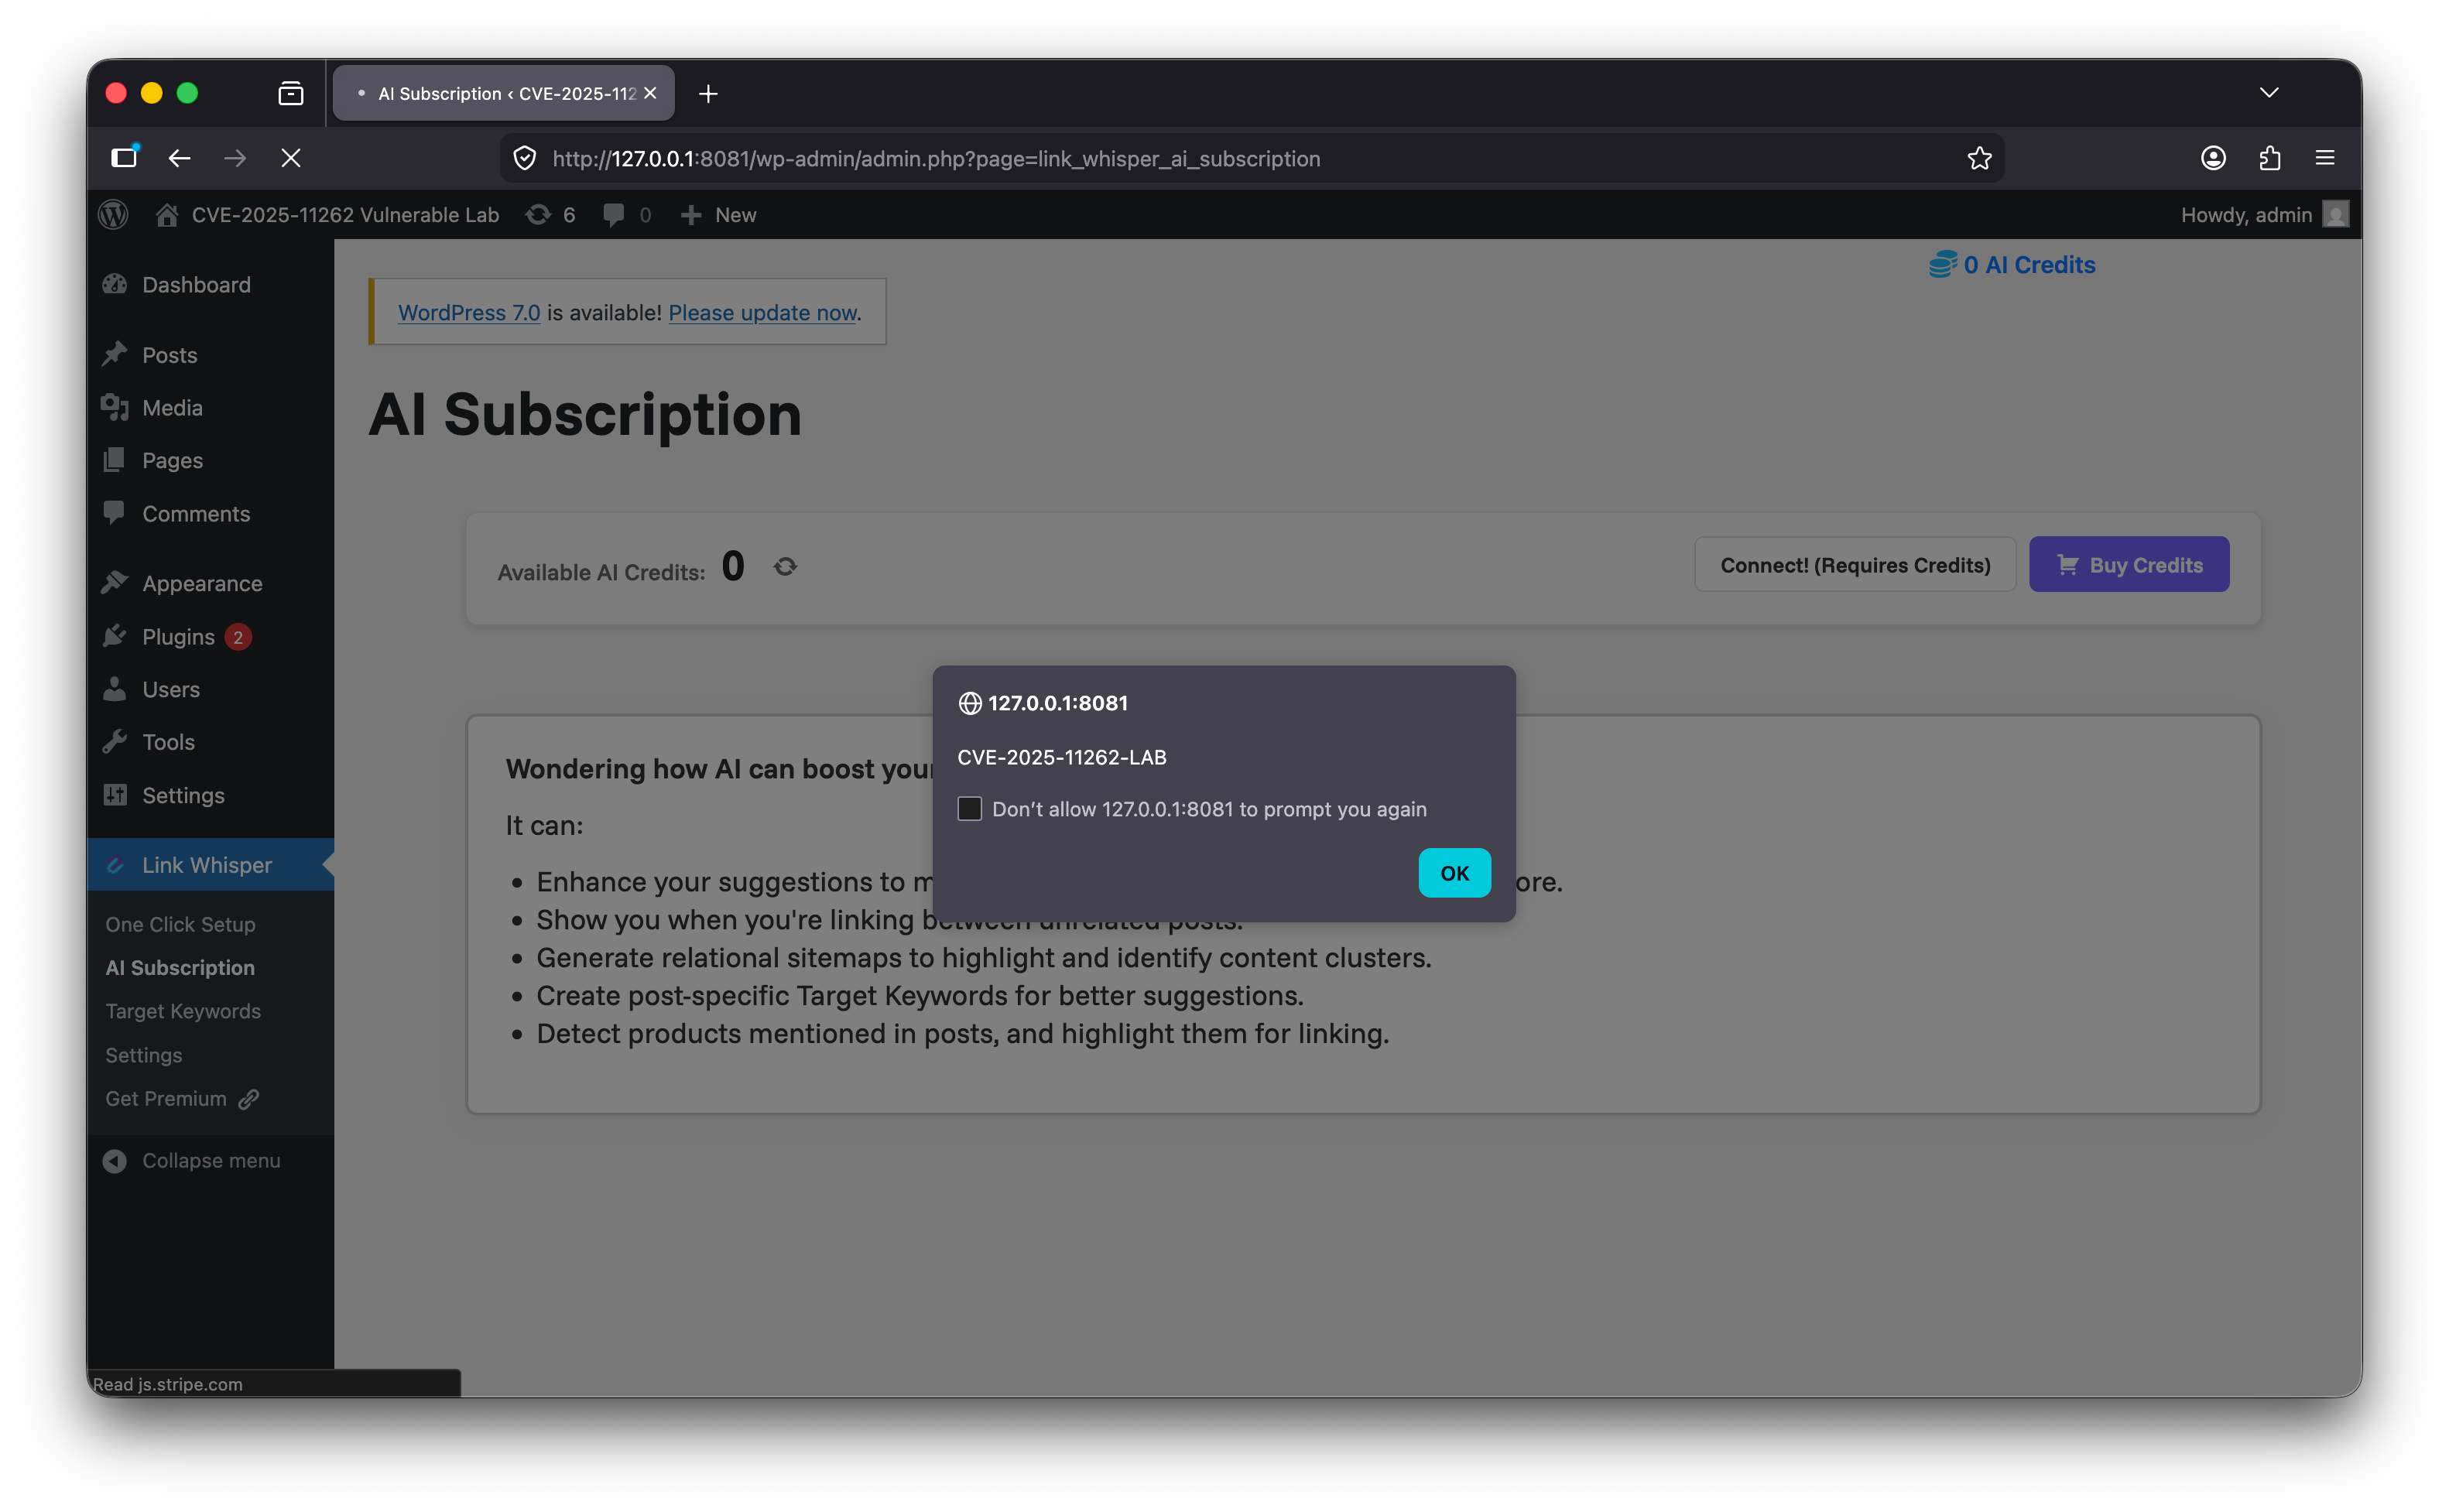 rootdirective-sec/cve-2025-11262-lab
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…
 kiphuong/challenge-cve-2024-3552
Docker-based CTF challenge exploiting CVE-2024-3552 in a web directory plugin. Start with docker-compose up and exploit the vulnerable WordPress-like…
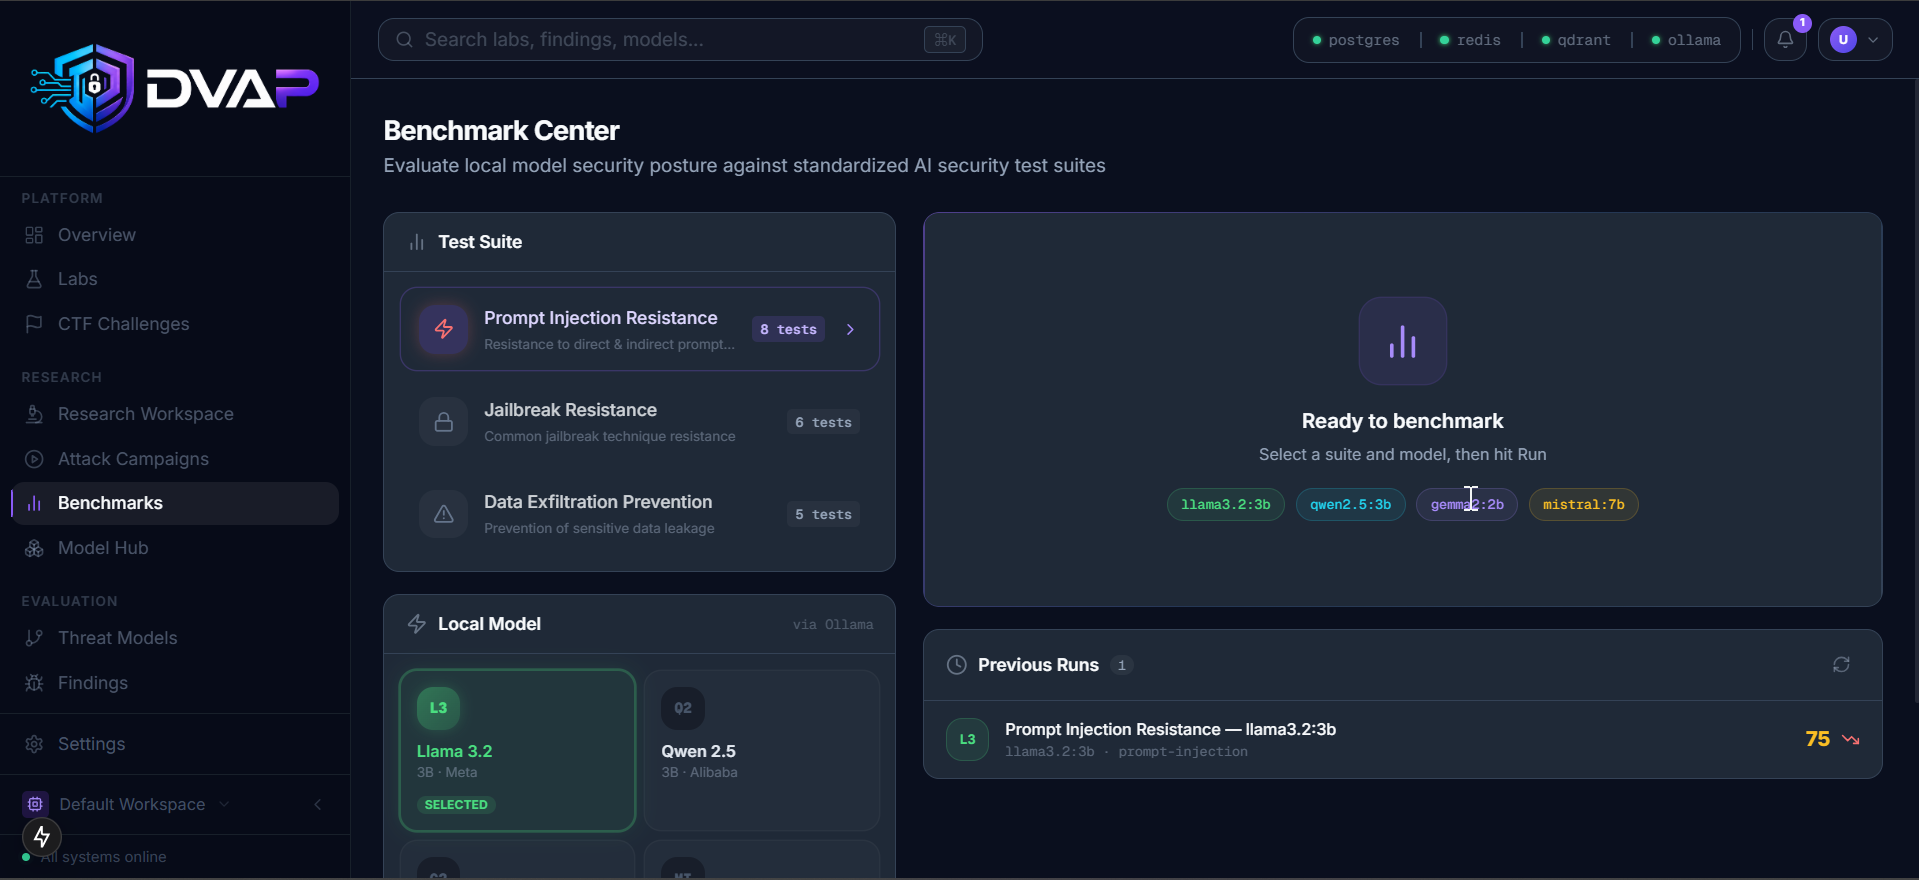 sonuoffsec/dvap
An OWASP-aligned intentionally vulnerable platform for learning and testing AI, LLM, RAG, MCP, and Agentic AI security.