CVE-2026-12227-visualcomposer-lfi-poc

Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…

Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…

WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)

Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…

Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…

Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…

Proof-of-concept exploit and lab for CVE-2026-81648, an unauthenticated arbitrary file deletion flaw in the WordPress CryptoPayment Gateway plugin.

Proof-of-concept and disclosure pack for CVE-2026-19952, an unauthenticated arbitrary file deletion in the WordPress Frontend Admin plugin, with lab…

Proof-of-concept and lab for CVE-2026-75827, a Grav arbitrary file write via Blueprint dynamic-data error_log, with reproduction script and Docker…

PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…

Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…

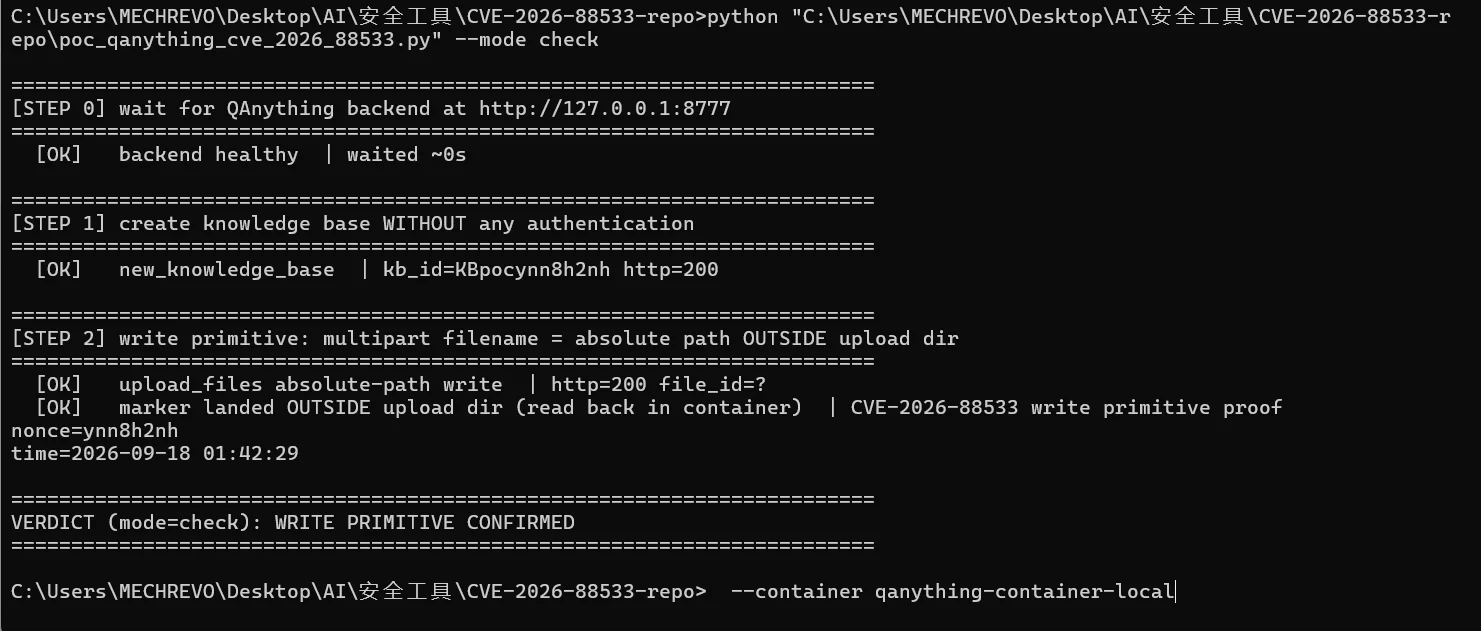
PoC and lab reproduction for CVE-2026-88533, an unauthenticated arbitrary file write leading to root RCE in QAnything via path traversal in the…

Proof-of-concept for CVE-2026-67401, a cPanel/WHM EmailTrack SQL injection enabling arbitrary file write and root RCE, with SQLi detection probes and…

Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via parser…

Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…

Reproducible Docker lab + raw-socket exploit for CVE-2015-3306 (ProFTPD mod_copy pre-auth arbitrary file copy) — a patch-diffing learning exercise

A/B Docker lab + PoC for CVE-2026-32475 (Elementor Pro Forms unauthenticated arbitrary file upload -> RCE via validation/move loop desync)

Divi Ajax Filter <= 5.1.2 Unauthenticated Local File Inclusion via 'custom_loop_template'

Proof-of-concept exploit for CVE-2026-47627, a path traversal vulnerability in NVIDIA Triton Inference Server leading to arbitrary file write via…