cve-2024-36401-security-simulator

Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…

Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…

Unauthenticated time-based blind SQL injection PoC for AWP Classifieds <= 4.4.7, with a Docker lab, full writeup, and patch diff.

Detection and proof-of-concept exploit for CVE-2026-20131, a critical unauthenticated Java deserialization RCE in Cisco Secure FMC. Includes a safe…

A vulnerable Java based REST API for demonstrating CVE-2021-44228 (log4shell).

A hands-on binary exploitation challenge based on CVE-2021-4034, designed for practicing privilege escalation techniques in a controlled environment.

Python-based mass scanner for validating a specific WordPress AJAX behavior in authorized environments, supporting URL normalization, endpoint…

Documented penetration test on an isolated Metasploitable2 VM using Metasploit and Nmap, covering remote exploitation, privilege escalation, and…

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

A font-based deception tool for red teaming, security research, and whatever else.

Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.

Lord Of Active Directory - automatic vulnerable active directory on AWS

Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…

Detection of Linux Malware C2 RedXOR - demonstration

A Python-based static patch analysis tool for studying the root cause and remediation of CVE-2021-41773 (Apache HTTP Server Path Traversal) by…

Reproduction of cve-2024-49113-ldap_nightmare_reproduction

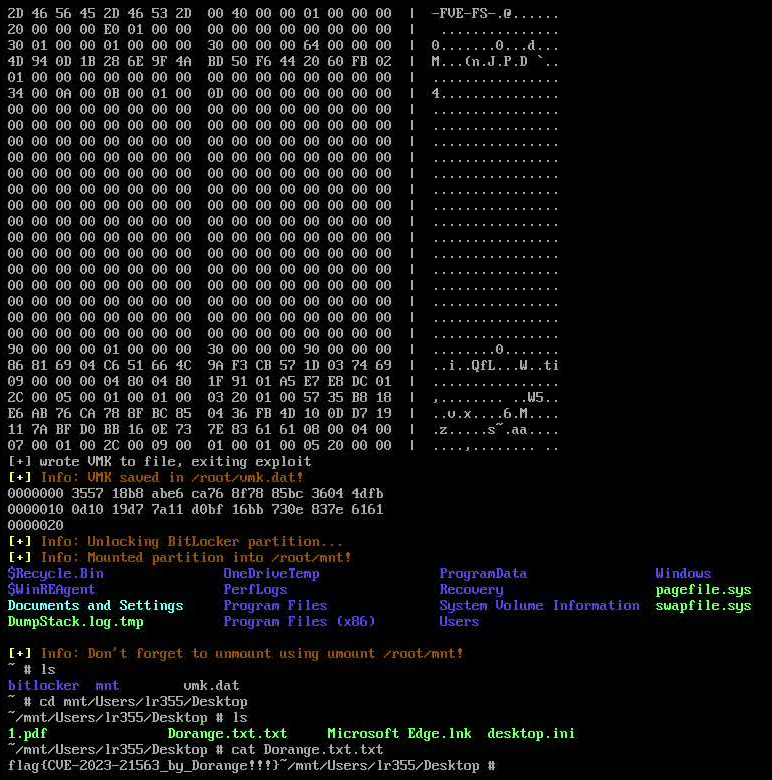
Cracking BitLocker encryption based on CVE-2023-21563 vulnerability

Docker-based vulnerable lab and detailed PoC report for CVE-2023-25157/25158 SQL injection in GeoServer & GeoTools, with 4 verified attack vectors…

Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…