
screenpipe
 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
ctfcurated-resourceseducation+8
21.8k
screenpipe/screenpipeYC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 damnvulnerablecryptoapp/damnvulnerablecryptoapp
An app with really insecure crypto. To be used to see/test/exploit weak cryptographic implementations as well as to learn a little bit more about…
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security
 dinosn/cve-2026-71362-magento-lab
Docker lab reproducing CVE-2026-71362 Magento/Adobe Commerce account takeover via customer-session identity switch, with PoC and official-patch A/B/A…
 abraxas/cve-2026-75816
Proof-of-concept and lab reproduction for CVE-2026-75816, an unauthenticated WordPress Frontend Admin account takeover via admin-ajax form submission.
 owasp/owasp-vwad
⚠️ This repo is no longer in use. Please refer to https://github.com/OWASP/www-project-vulnerable-web-applications-directory
 sofianehamlaoui/pentest-bookmarkz
A collection of useful links for Pentesters
 liamromanis101/cve-2025-55182
Python exploit for CVE-2025-55182, a server-side JavaScript injection in Next.js/React enabling remote code execution via malformed multipart form…
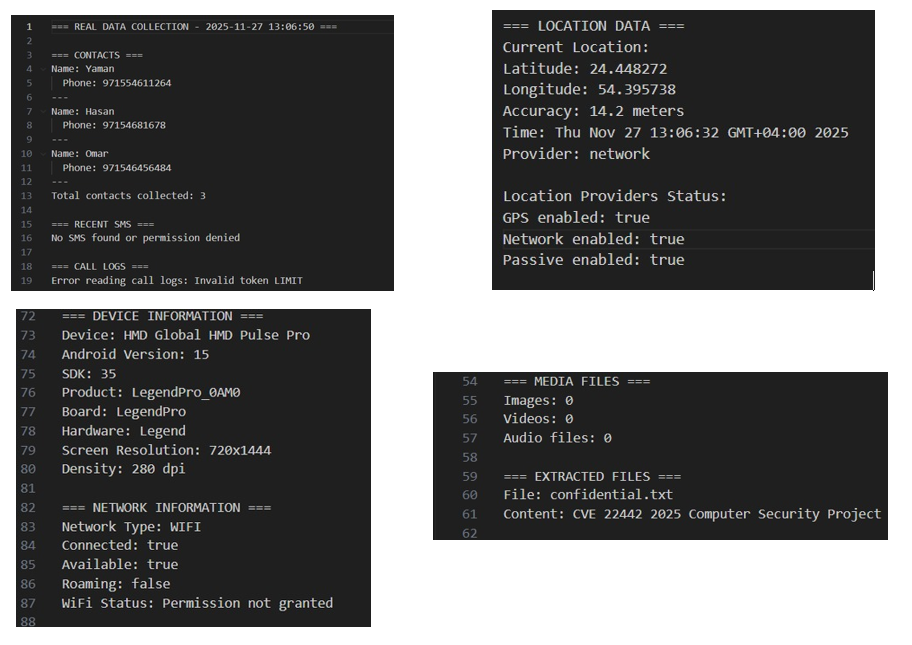 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 arkha-corvus/letsdefend-soc173-follina-0-day-detected
We are presented with a security alert indicating the detection of the Follina (CVE-2022-30190) vulnerability. A malicious Word document triggered…
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…
 raytran54/cve-2018-7600
Step-by-step analysis and exploitation lab for Drupal CVE-2018-7600 remote code execution vulnerability, including debugging, exploit code, and…
 yuvalmil/parsingpeas
HTML parser for PEAS output with additional features
 doocop/cve-2022-30190
Reproduction of CVE-2022-30190 (Follina) remote code execution vulnerability in Microsoft Office Word via malicious docx/rtf files with ms-msdt…