
iam-vulnerable
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
cloud-securityeducationidentity-access-management+4
597
bishopfox/iam-vulnerableUse Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
 peach-research-lab/authorizationbench
[🎖️ Honorable Mention in HAIPS @COLM'26] The first benchmark to evaluate how well do LLM agents act in alignment with their assigned authorization…
 shivam-bathla/cve-2026-24061-setup
Docker setup for CVE-2026-24061
 0xnxt1me/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 that adds x-middleware-subrequest to bypass Next.js middleware authentication checks.
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
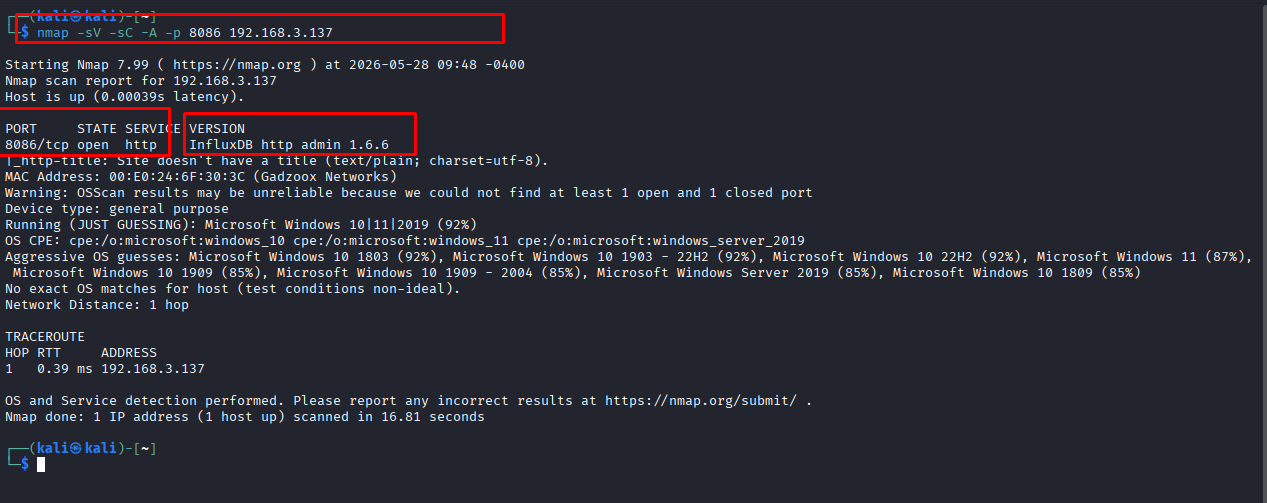 dungsocool/cve-2019-20933
Step-by-step lab writeup demonstrating CVE-2019-20933 InfluxDB authentication bypass via forged JWT tokens, including exploitation,…
 dinosn/cve-2026-71362-magento-lab
Docker lab reproducing CVE-2026-71362 Magento/Adobe Commerce account takeover via customer-session identity switch, with PoC and official-patch A/B/A…
 gkdgkd123/cve-2026-29145-everything
Reproducible PoC environment for CVE-2026-29145 Apache Tomcat CLIENT_CERT + OCSP soft-fail bypass, including exploit scripts, mock OCSP responder,…
 george0papasotiriou/cve-2026-4444-jwt-algorithm-confusion-via-kid-injection
POC for CVE-2026-4444 demonstrating JWT algorithm confusion via untrusted kid injection, including vulnerable Node.js server and Python exploit for…
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…
 dhiaelhak-rached/cve-2026-39987-lab-or-marimo-cve-lab
Educational Docker lab demonstrating CVE-2026-39987, a pre-auth RCE via WebSocket authentication bypass in marimo, with exploit script and patch…
 ricsirigu/cve-2025-29927
A deliberately Next.js app, vulnerable to CVE-2025-29927, Authorization Bypass
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 enochgitgamefied/nextjs-cve-2025-29927-docker-lab
Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…
 jweny/shiro-cve-2020-17523
Analysis of two authentication bypass techniques for Apache Shiro (CVE-2020-17523) with a reproducible exploit environment and detailed root cause…
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 yeondg/nextjs-cve-2025-29927
vulnerable-nextjs-14-CVE-2025-29927