
vuln-bank
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
ai-securityapi-securitycode-analysis+5
990
commando-x/vuln-bankIntentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 sunweb3sec/defihacklabs
Reproduce DeFi hacked incidents using Foundry.
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
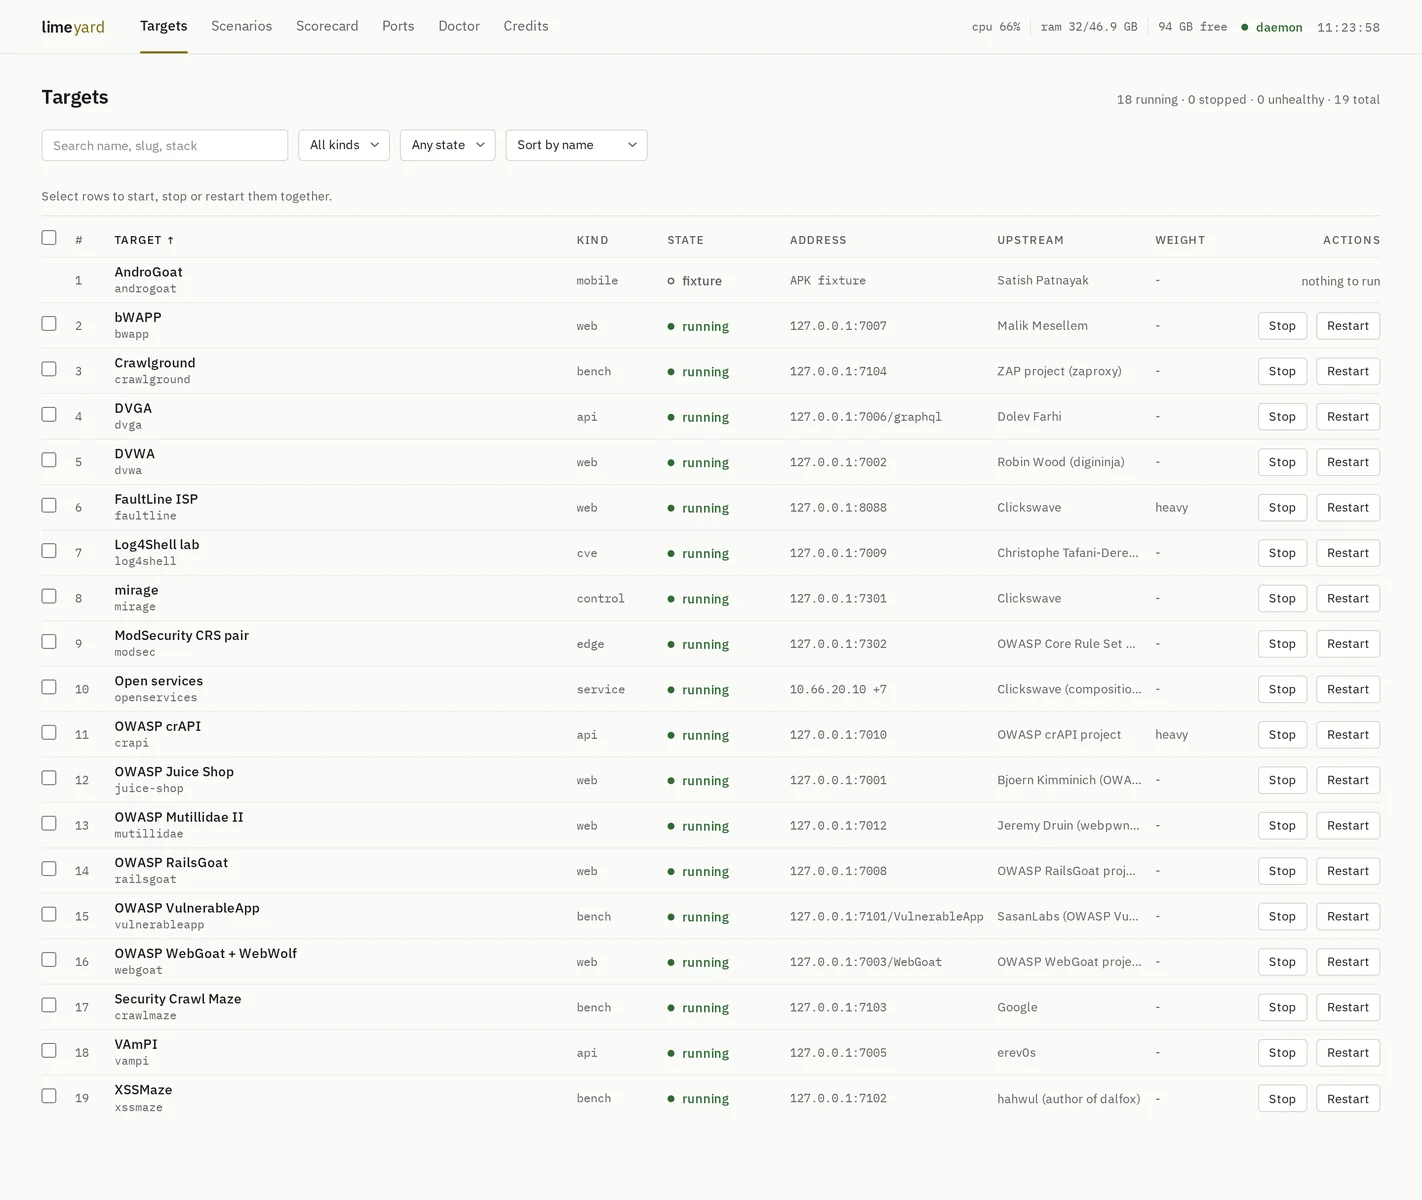 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
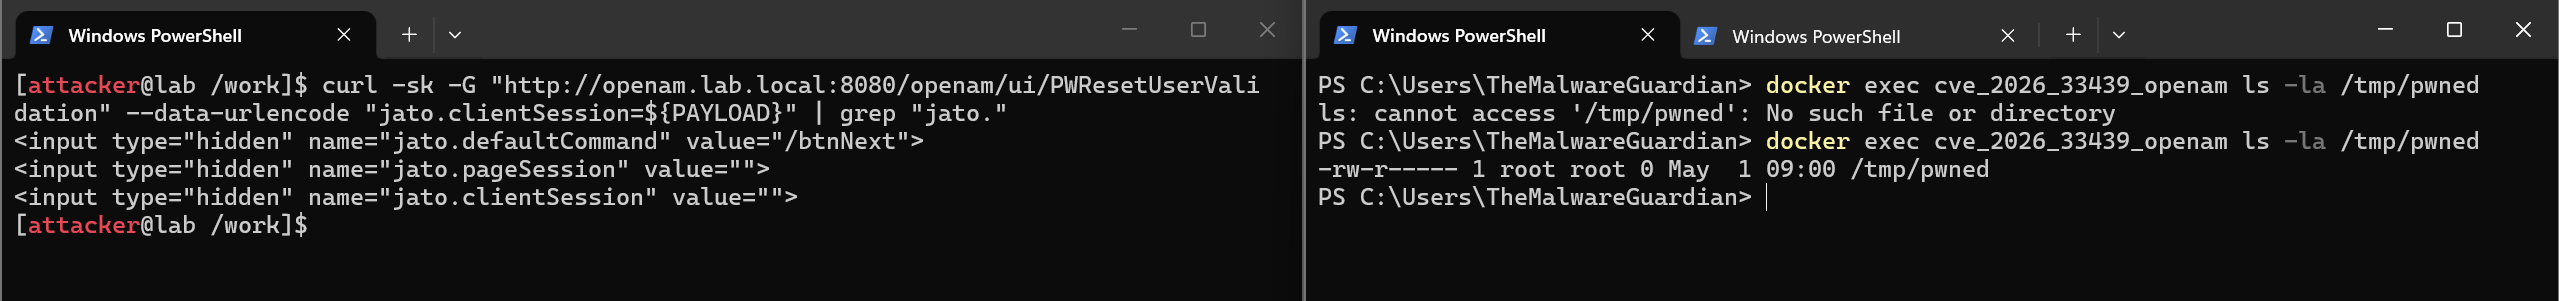 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 5kr1pt/roundcube_cve-2025-49113
Explicação + Lab no THM
 j3ssie/dynast-bench
A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 jonwiggins/xmloxide
A pure Rust reimplementation of libxml2
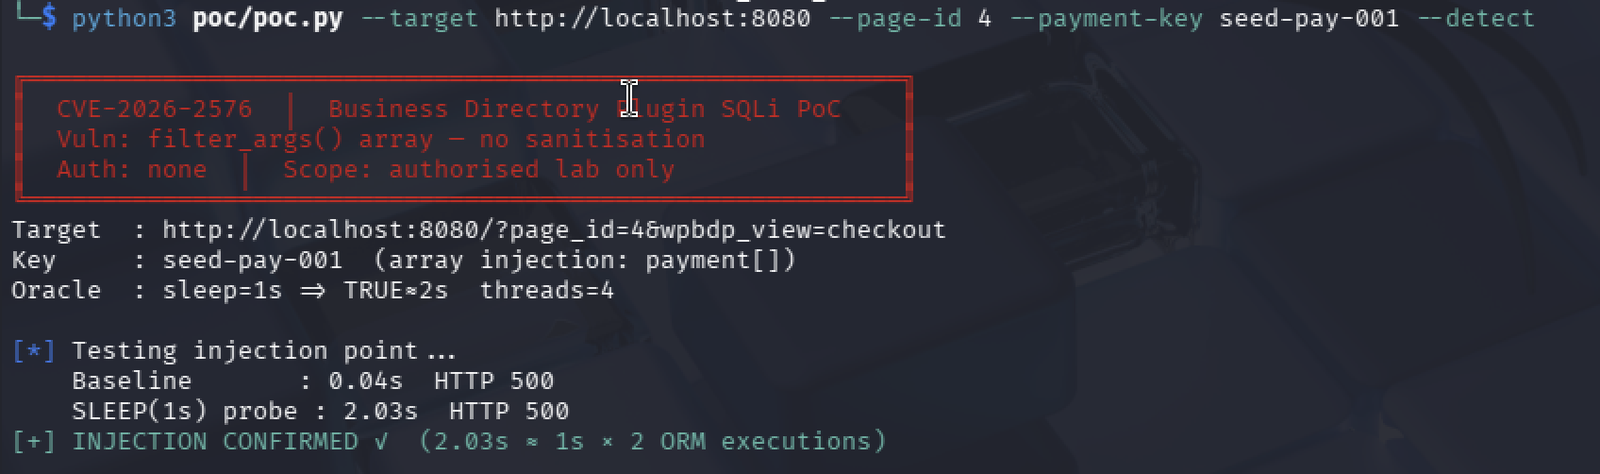 sowatkheang/cve_2026_2576_poc
CVE-2026-2576 — Business Directory Plugin SQLi PoC (Local Setup). Unauthenticated Time-Based Blind SQL Injection Business Directory Plugin for…
 veraxy00/cve-2020-8840
Jackson-databind远程代码执行漏洞(CVE-2020-8840)分析复现环境代码
 lucastran05/cve-2023-48223
Proof-of-concept demonstrating JWT algorithm confusion in fast-jwt library. Includes vulnerable server, token forging script, and verification fix…
 47cid/wp2shell-lab
Educational PoC + lab for CVE-2026-63030 + CVE-2026-60137: pre-auth SQLi in WordPress core via REST batch-route confusion
 bhanunamikaze/cve-2026-2587-exploit-poc
CVE-2026-2587 PoC validator for Eclipse GlassFish EL Injection RCE in the admin console gadget.jsf handler. Safe authenticated vulnerability scanner…
 h3st4k3r/cve-2025-30065
Java-based research harness for studying CVE-2025-30065, an RCE vulnerability in Apache Parquet via Avro schema deserialization, intended for…