
ludus_crushftp_cve-2025-31161_sim
 rufflabs/ludus_crushftp_cve-2025-31161_sim
Ansible role that simulates a realistic CrushFTP CVE-2025-31161 exploitation scenario with rotating sensitive data files and automated defender…
ctfeducationexploitation+5
rufflabs/ludus_crushftp_cve-2025-31161_simAnsible role that simulates a realistic CrushFTP CVE-2025-31161 exploitation scenario with rotating sensitive data files and automated defender…
 rootdirective-sec/cve-2025-11262-lab
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…
 oscarbataille/cve-2025-26794
CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup
 h3raklez/cve-2025-48734
CVE-2025-48734 - Affects Apache Commons BeanUtils in versions prior to 1.11.0 (and the 2.x branch before 2.0.0-M2).
 swapnildeshpande/cve-2025-29927-lab
Reproduction lab for CVE-2025-29927 — Next.js middleware authorization bypass (CVSS 9.1)
 speinador/cve-2025-6218_winrar
Educational lab demonstrating CVE-2025-6218 path traversal in WinRAR. Includes a malicious RAR file and step-by-step guide to observe file overwrite…
 jeanback1/cve-2025-2304-exploit
Python exploit script for CVE-2025-2304, a mass assignment privilege escalation in Camaleon CMS. Automates CSRF token parsing and role parameter…
 0xnxt1me/cve-2025-29927
Proof-of-concept exploit for CVE-2025-29927 that adds x-middleware-subrequest to bypass Next.js middleware authentication checks.
 x3nt4ur0/cve-2025-5548
Laboratorio para el análisis y explotación del CVE-2025-5548
 danielw98/zero-click-exploit-analysis
CVE-2025-55177 + CVE-2025-43300: reverse-engineering the WhatsApp-ImageIO zero-click iOS chain, with interactive labs.
 wh0am123/cve-2025-54918-poc
POC for CVE-2025-54918 and a technical demonstration.
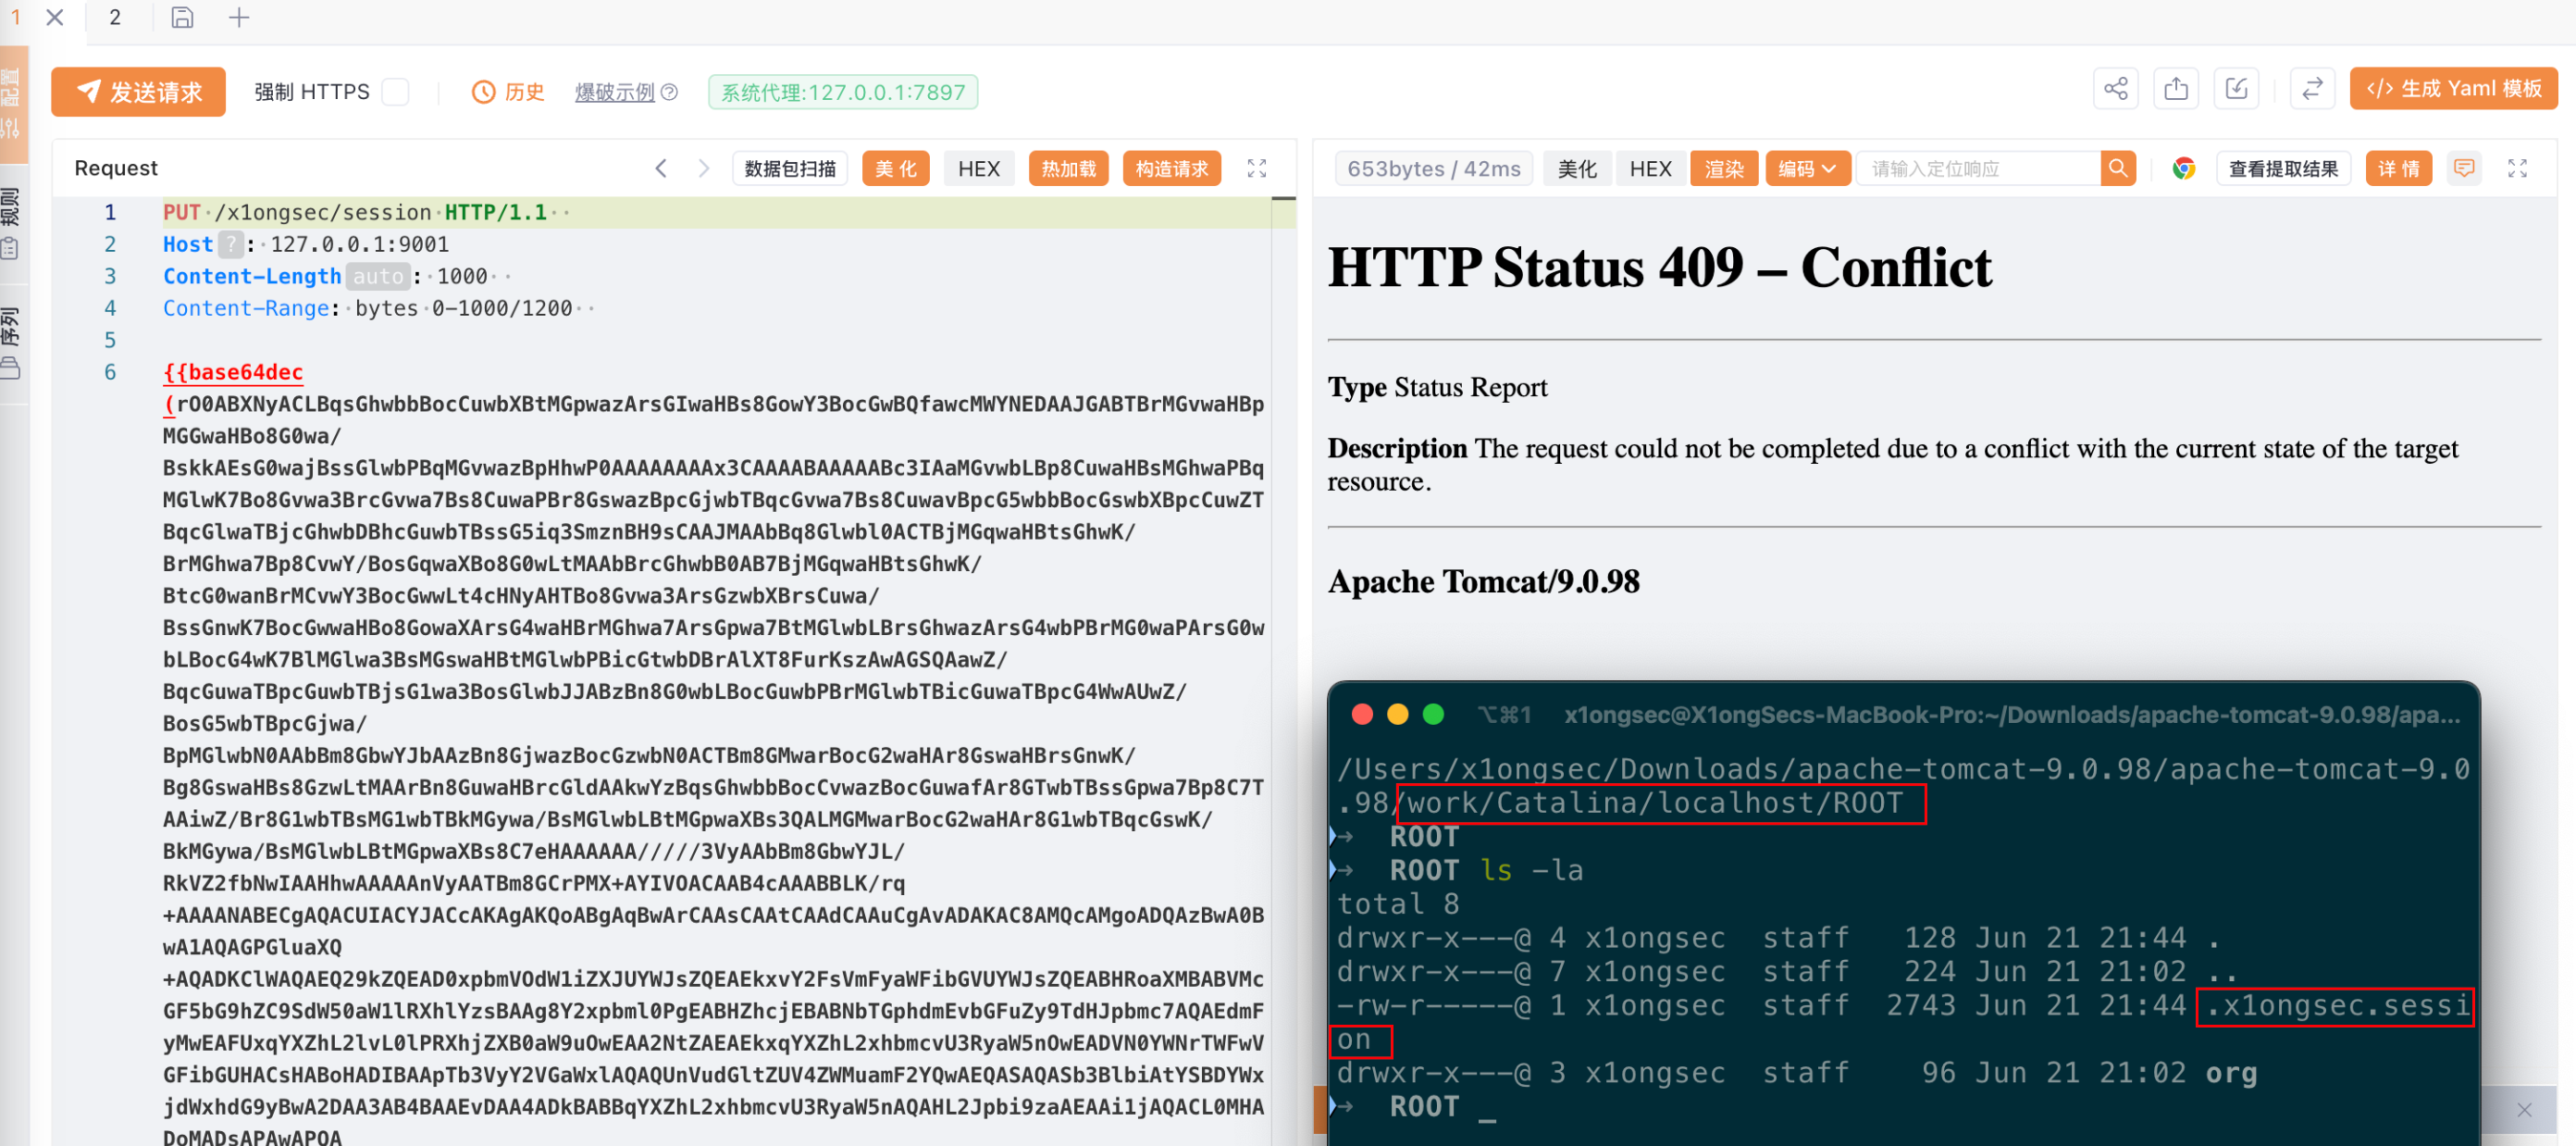 x1ongsec/cve-2025-24813
tomcat CVE-2025-24813 反序列化RCE环境
 kso4more/cve-2025-0108
Reproduces CVE-2025-0108 path confusion vulnerability in Nginx/Apache stacks. Includes a vulnerable PoC and a patched implementation demonstrating…
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
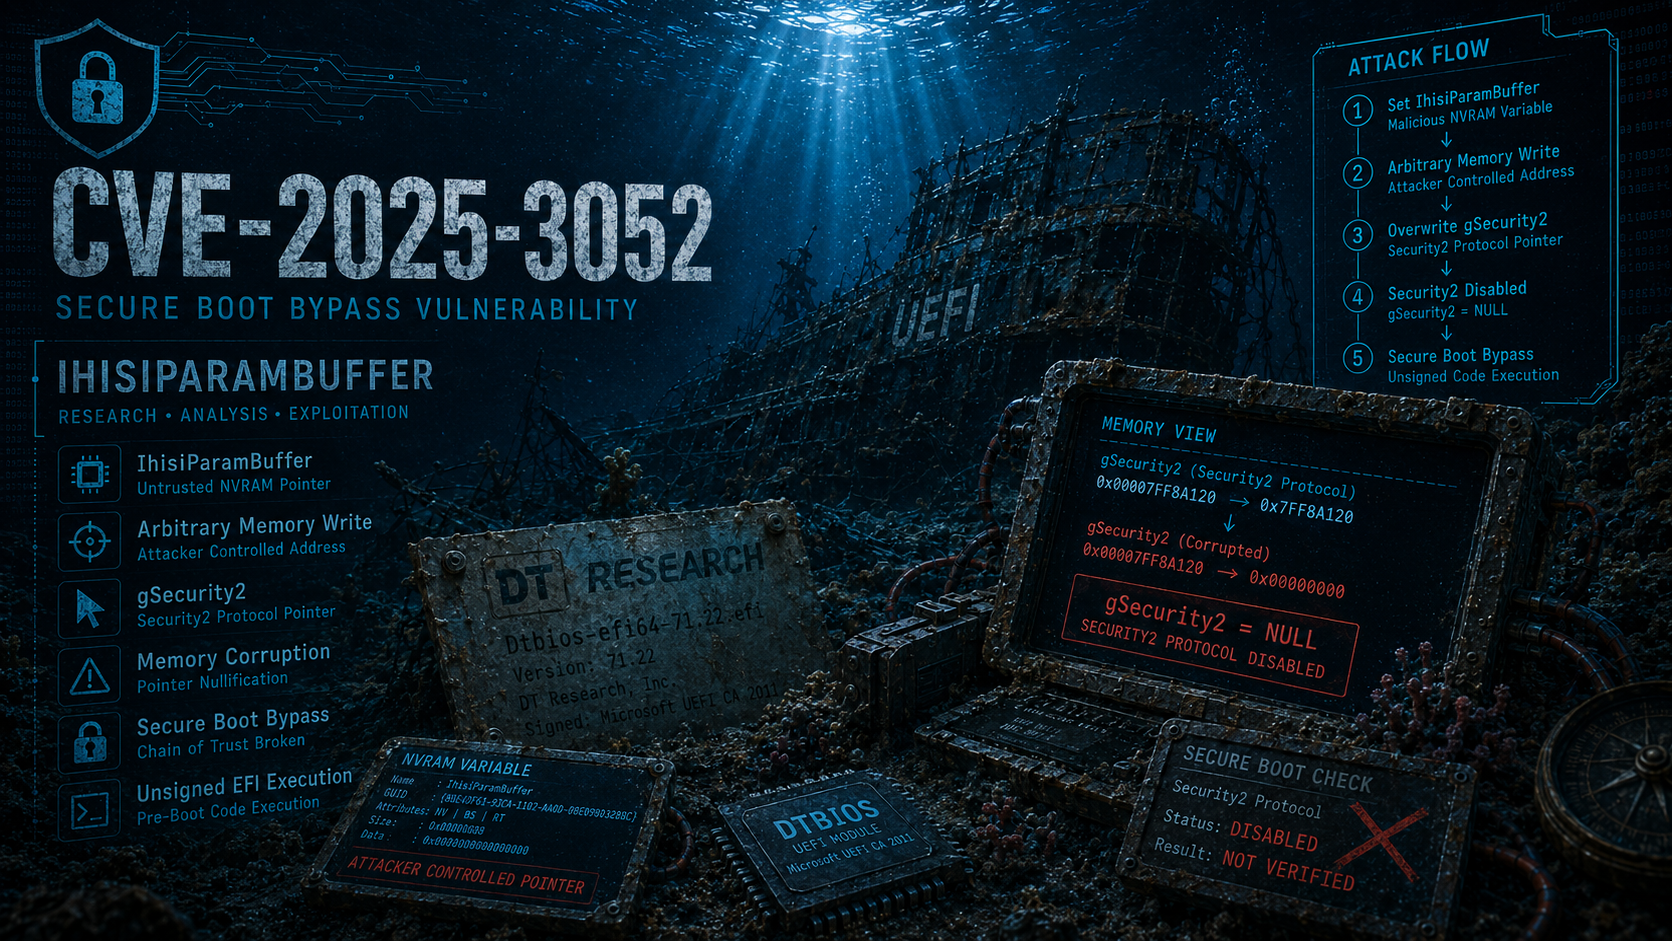 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 dhananjayasj/cve-2025-24813-apache-tomcat-partial-put-deserialization-rce-
Proof-of-concept exploit for CVE-2025-24813, an unauthenticated RCE in Apache Tomcat via partial PUT and deserialization. Includes Docker lab for…
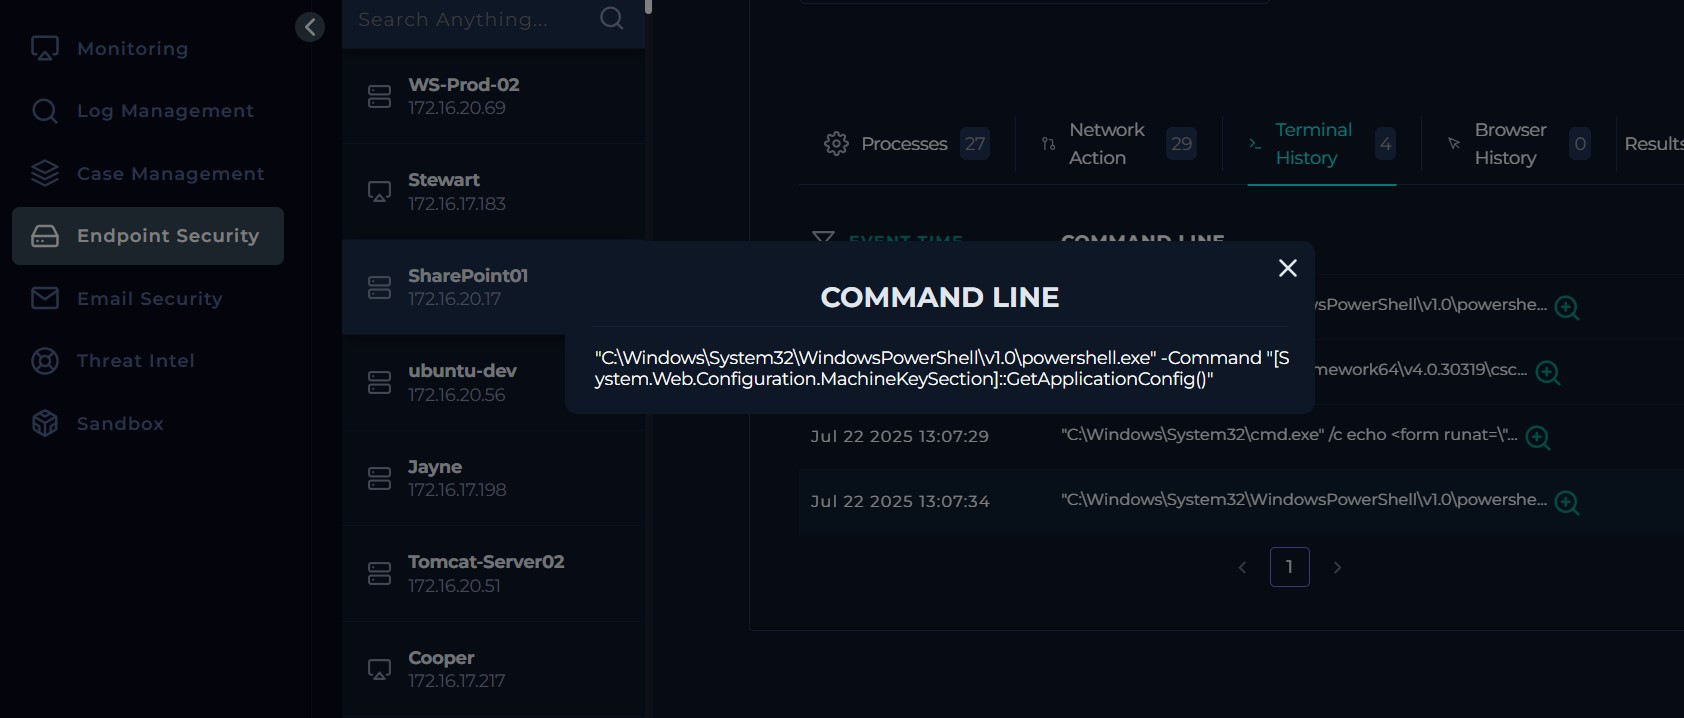 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…