
CVE-2024-10914
 verylazytech/cve-2024-10914
POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
command-and-controlexploitationiot-security+3
48
verylazytech/cve-2024-10914POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 george0papasotiriou/cve-2026-21009-ecdsa-nonce-reuse-in-iot-firmware-signing
Educational Python simulation demonstrating ECDSA nonce reuse in IoT firmware signing, showing how an attacker can recover private keys from two…
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 lodi-g/cve-2019-13361
Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
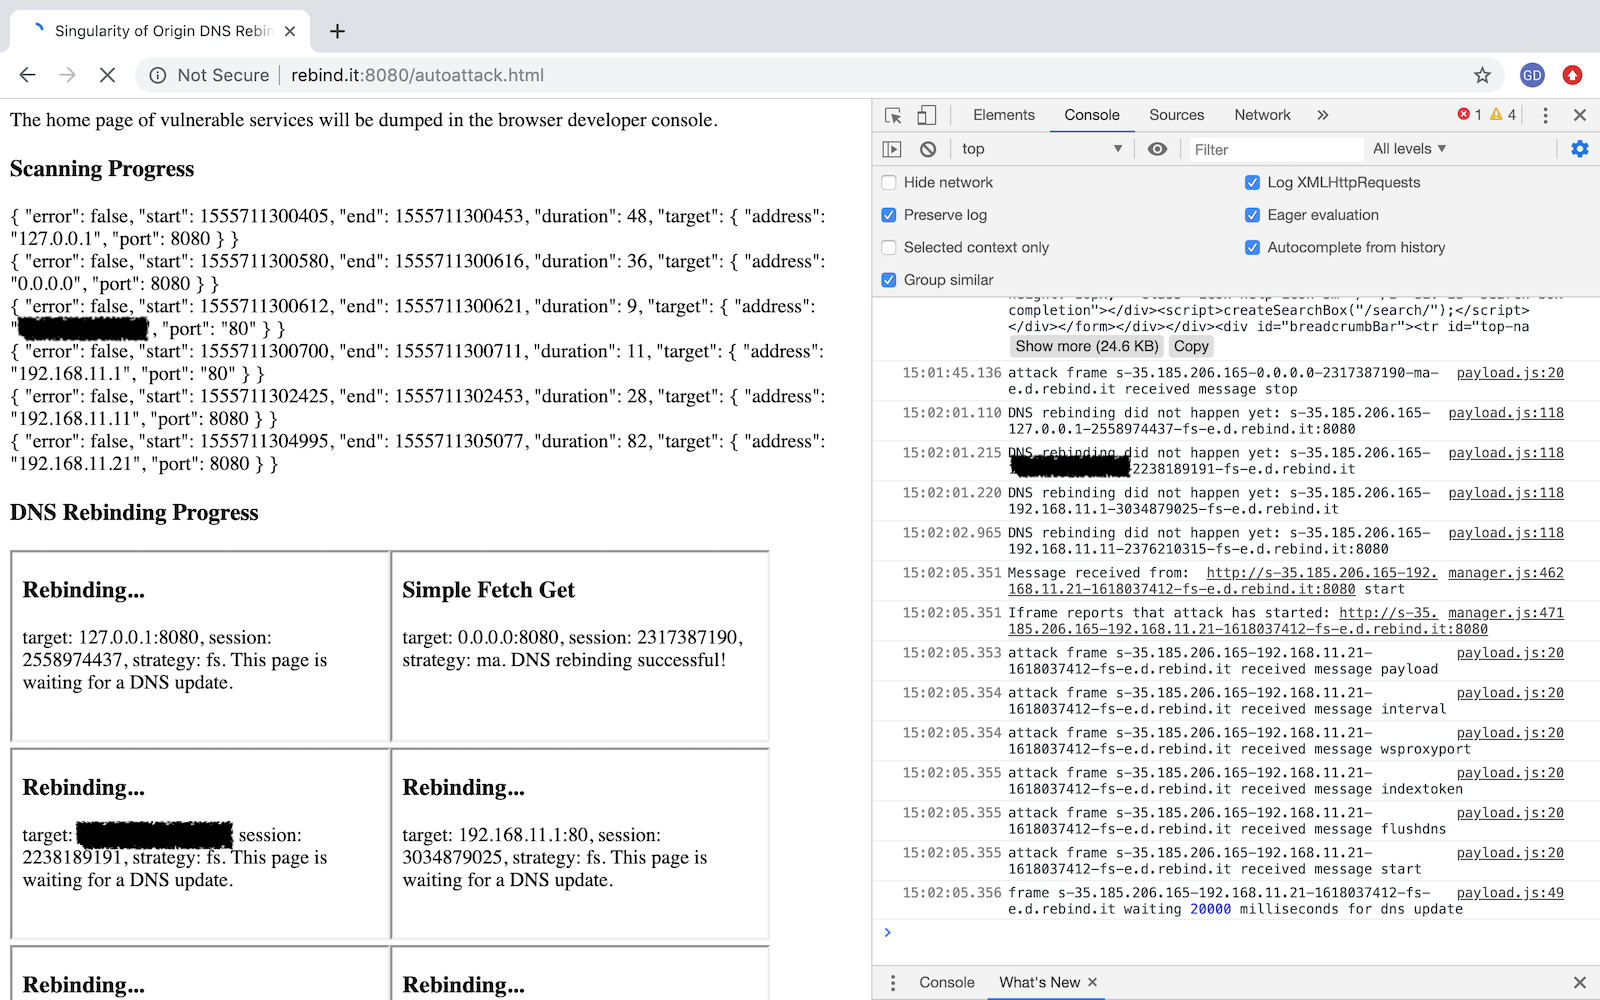 nccgroup/singularity
A DNS rebinding attack framework.
 boginw/zyxel-vmg8825-keygen
A key generator for Zyxel VMG8825-T50
 applied-risk/loracrack
LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
 cyberaz0r/gl.inet-multiple-vulnerabilities
Exploits for GL.iNet CVE-2023-46454, CVE-2023-46455 and CVE-2023-46456
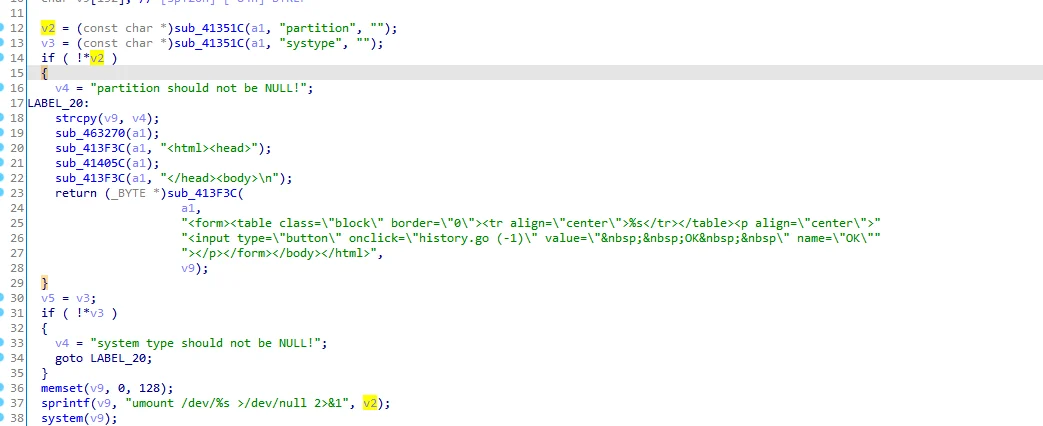 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 ayushman4/tp-link-archer-cr-700-xss-exploit
Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)
 george0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser
Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 jianchun-ding/cve-poc-update
CVE-2023-46371 and CVE-2023-46527 update
 chinayozz/cve-2020-25078
Batch exploit script for CVE-2020-25078 targeting D-Link DCS series cameras to extract account credentials via information disclosure vulnerability.