
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
26 results
CVE-2019-7642 preview

CVE-2019-7642

GitHubxw77cve/cve-2019-7642

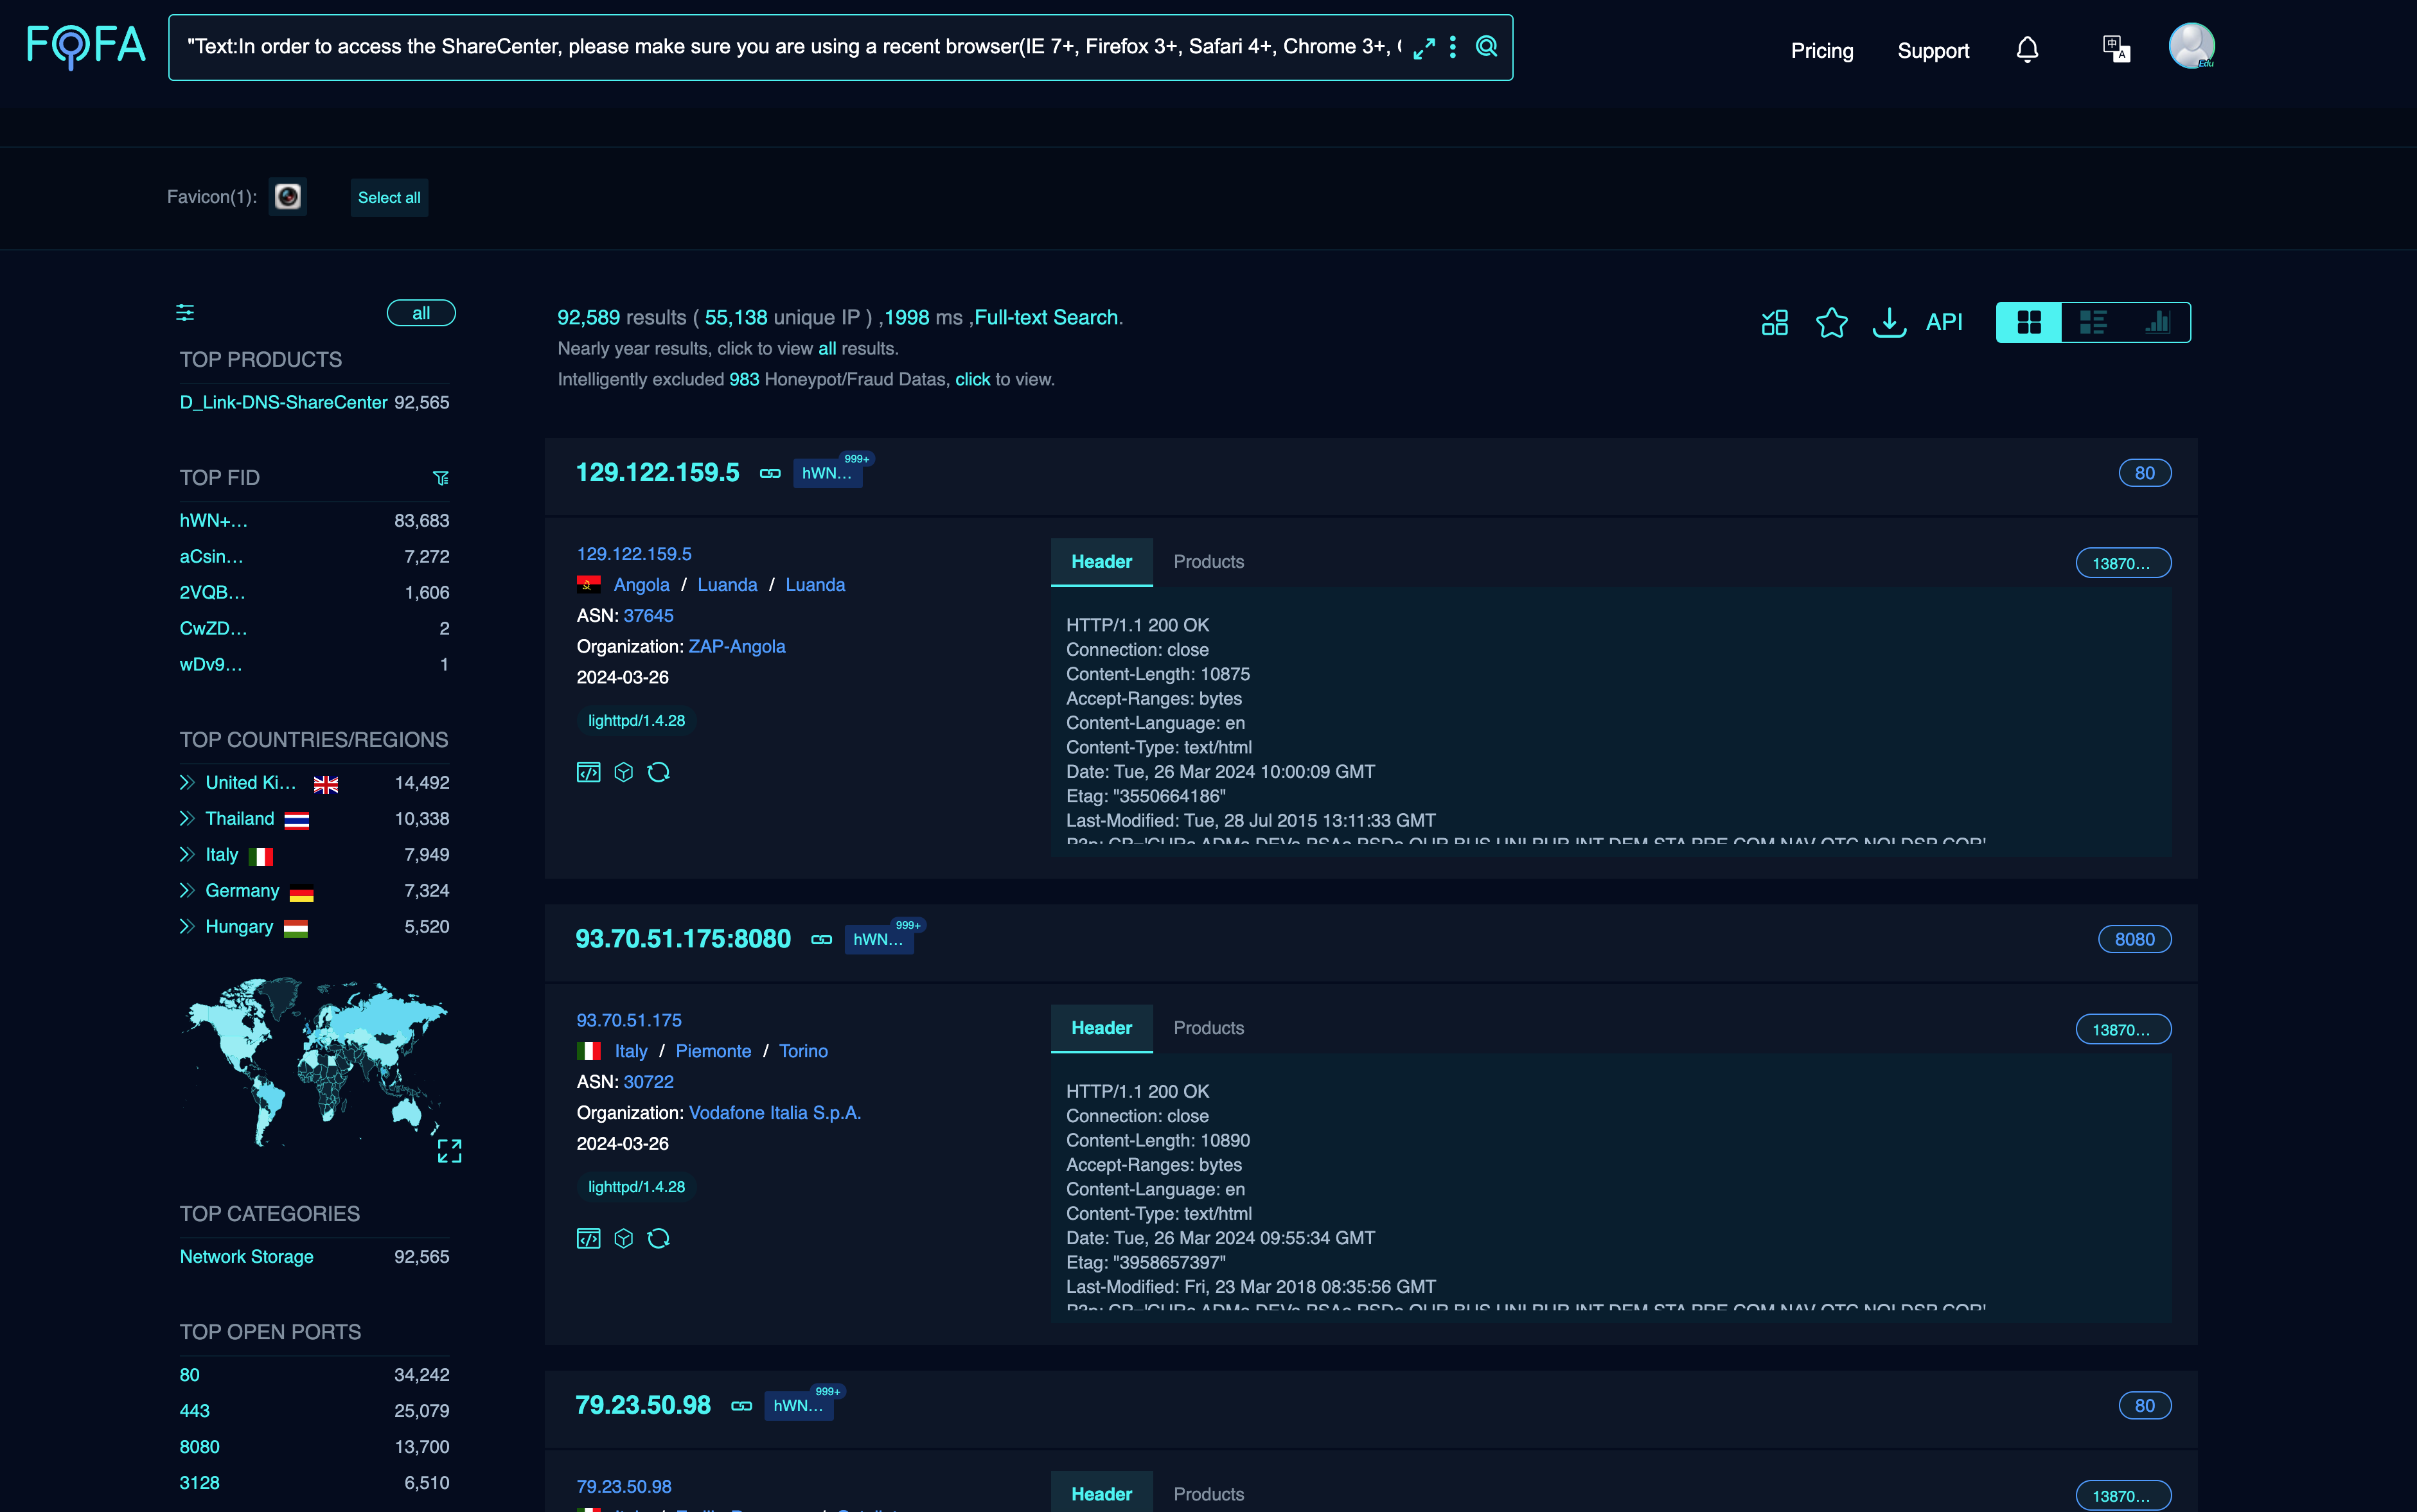
Proof-of-concept exploit for CVE-2019-7642 demonstrating unauthenticated access to DNS query logs and login history on vulnerable D-Link routers via…
exploitationinformation-gatheringiot-security+3
16
7 years ago
dlink preview

dlink

GitHubnetsecfish/dlink

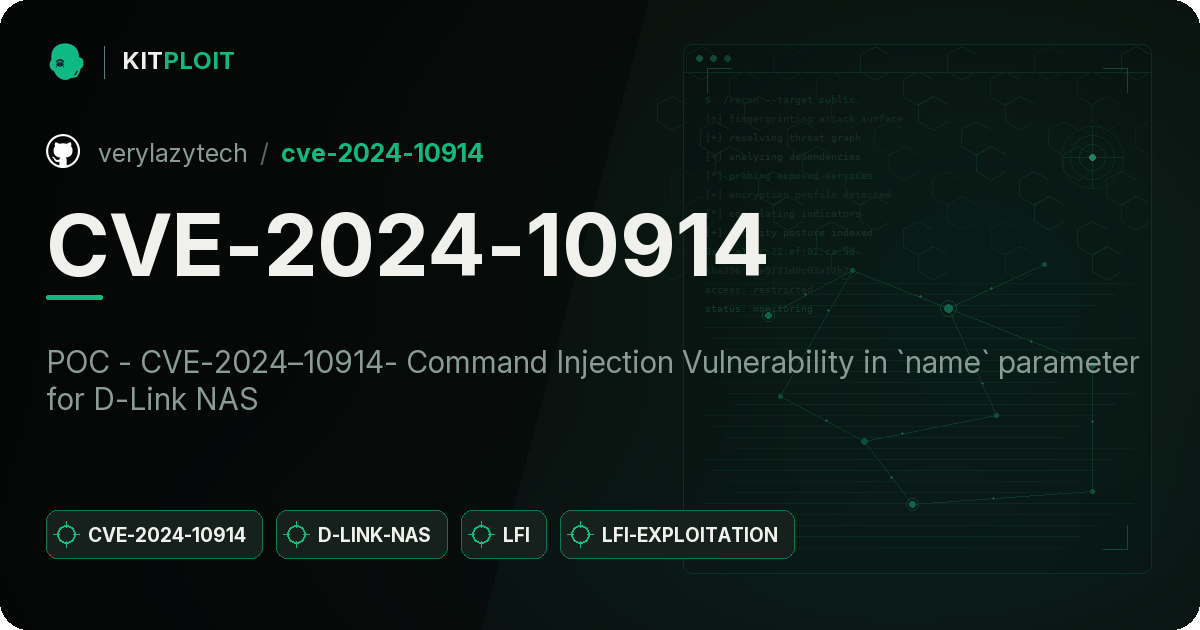
Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…
authenticationexploitationiot-security+3
992 years ago
CVE-2024-10914 preview

CVE-2024-10914

GitHubverylazytech/cve-2024-10914

POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
command-and-controlexploitationiot-security+3
481 year ago
CVE-2024-9570_D-Link-DIR-619L-bof preview

CVE-2024-9570_D-Link-DIR-619L-bof

GitHubdylvie/cve-2024-9570_d-link-dir-619l-bof

Remote buffer overflow exploit for D-Link DIR-619L router (CVE-2024-9570) targeting the formEasySetTimezone function for penetration testing and…
binary-exploitationexploitationiot-security+3
62 years ago
CVE-2025-22968 preview

CVE-2025-22968

GitHubcrunzex/cve-2025-22968

Unauthenticated access in the default configuration of the D-Link DWR-M972V
embedded-systems-securityexploitationiot-security+3
61 year ago
d_link_880_bug preview

d_link_880_bug

GitHubbadnack/d_link_880_bug

CVE-2017-14948 for D-Link 880 Firmware
binary-analysisembedded-systems-securityexploitation+4
37 years ago
CVE-2026-82592 preview

CVE-2026-82592

GitHubhackspeak/cve-2026-82592

Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
binary-exploitationexploitationhardware-iot-security+4
21 month ago
CVE-2018-18441-exploit preview

CVE-2018-18441-exploit

GitHubbayazid-bit/cve-2018-18441-exploit

D-Link DCS series Wi-Fi camera expose sensitive information.
exploitationinformation-gatheringiot-security+3
35 months ago
CVE-2024-33113 preview

CVE-2024-33113

GitHubfallenskill1/cve-2024-33113

D-LINK DIR-845L is vulnerable to information disclosure via the bsc_sms_inbox.php file.
exploitationinformation-gatheringiot-security+3
42 years ago
blogpost_cve-2018-19987-analysis preview

blogpost_cve-2018-19987-analysis

GitHubnahueldsanchez/blogpost_cve-2018-19987-analysis

This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
educationexploitationfirmware-analysis+4
25 years ago
cve-2024-10914 preview

cve-2024-10914

GitHubyenyangmjaze/cve-2024-10914

Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…
command-and-controlexploitationiot-security+3
11 year ago
CVE-2023-51119 preview

CVE-2023-51119

GitHuboscarakaelvis/cve-2023-51119

Improper Access Control on D-Link DIR-605L router
exploitationiot-securitypenetration-testing+3
12 years ago
D-Link-NAS-CVE-2024-10914- preview

D-Link-NAS-CVE-2024-10914-

GitHubbu0ucat/d-link-nas-cve-2024-10914-

这是一个D-Link rce漏洞 检测程序
embedded-systems-securityexploitationiot-security+3
11 year ago
D-Link preview

D-Link

GitHubaymankhalfatni/d-link

CVE-2017-12943

exploitationhardware-iot-securityiot-security+3
9 years ago
CVE-2024-33113 preview

CVE-2024-33113

GitHubtekua/cve-2024-33113

Le routeur D-LINK DIR-845L est vulnérable à un problème de divulgation d'informations. Plus précisément, le fichier bsc_sms_inbox.php sur l'appareil…
embedded-systems-securityexploitationinformation-gathering+3
2 years ago
CVE-2024-22853 preview

CVE-2024-22853

GitHubfallenskill1/cve-2024-22853

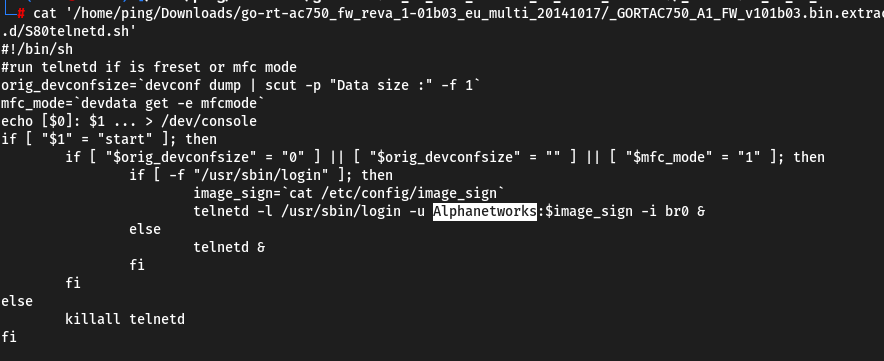
D-LINK Go-RT-AC750 GORTAC750_A1_FW_v101b03 has a hardcoded password for the Alphanetworks account, which allows remote attackers to obtain root…
embedded-systems-securityexploitationfirmware-analysis+5
2 years ago
-cve-2021-46381 preview

-cve-2021-46381

GitHubjcppeiqi/-cve-2021-46381

Python exploit for CVE-2021-46381 targeting D-Link DAP-1620 arbitrary file read vulnerability with FOFA-based device discovery.
exploitationinformation-gatheringiot-security+3
4 years ago
CVE-2021-46108 preview

CVE-2021-46108

GitHubg-rubert/cve-2021-46108

Proof-of-concept for stored cross-site scripting (XSS) vulnerability in D-Link DSL-2730E routers via the username parameter on the maintenance…

exploitationiot-securitypenetration-testing+3
4 years ago
Previous12Next