cve-2015-1187-dir820l-firmware-reverse-engineering

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…

Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)

Analysis and PoC for D-Link DIR-890L RCE (CVE-2022-29778)

Tool for especially scanning nearby devices and execute a given command on its own system while the target device comes in range.

Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…

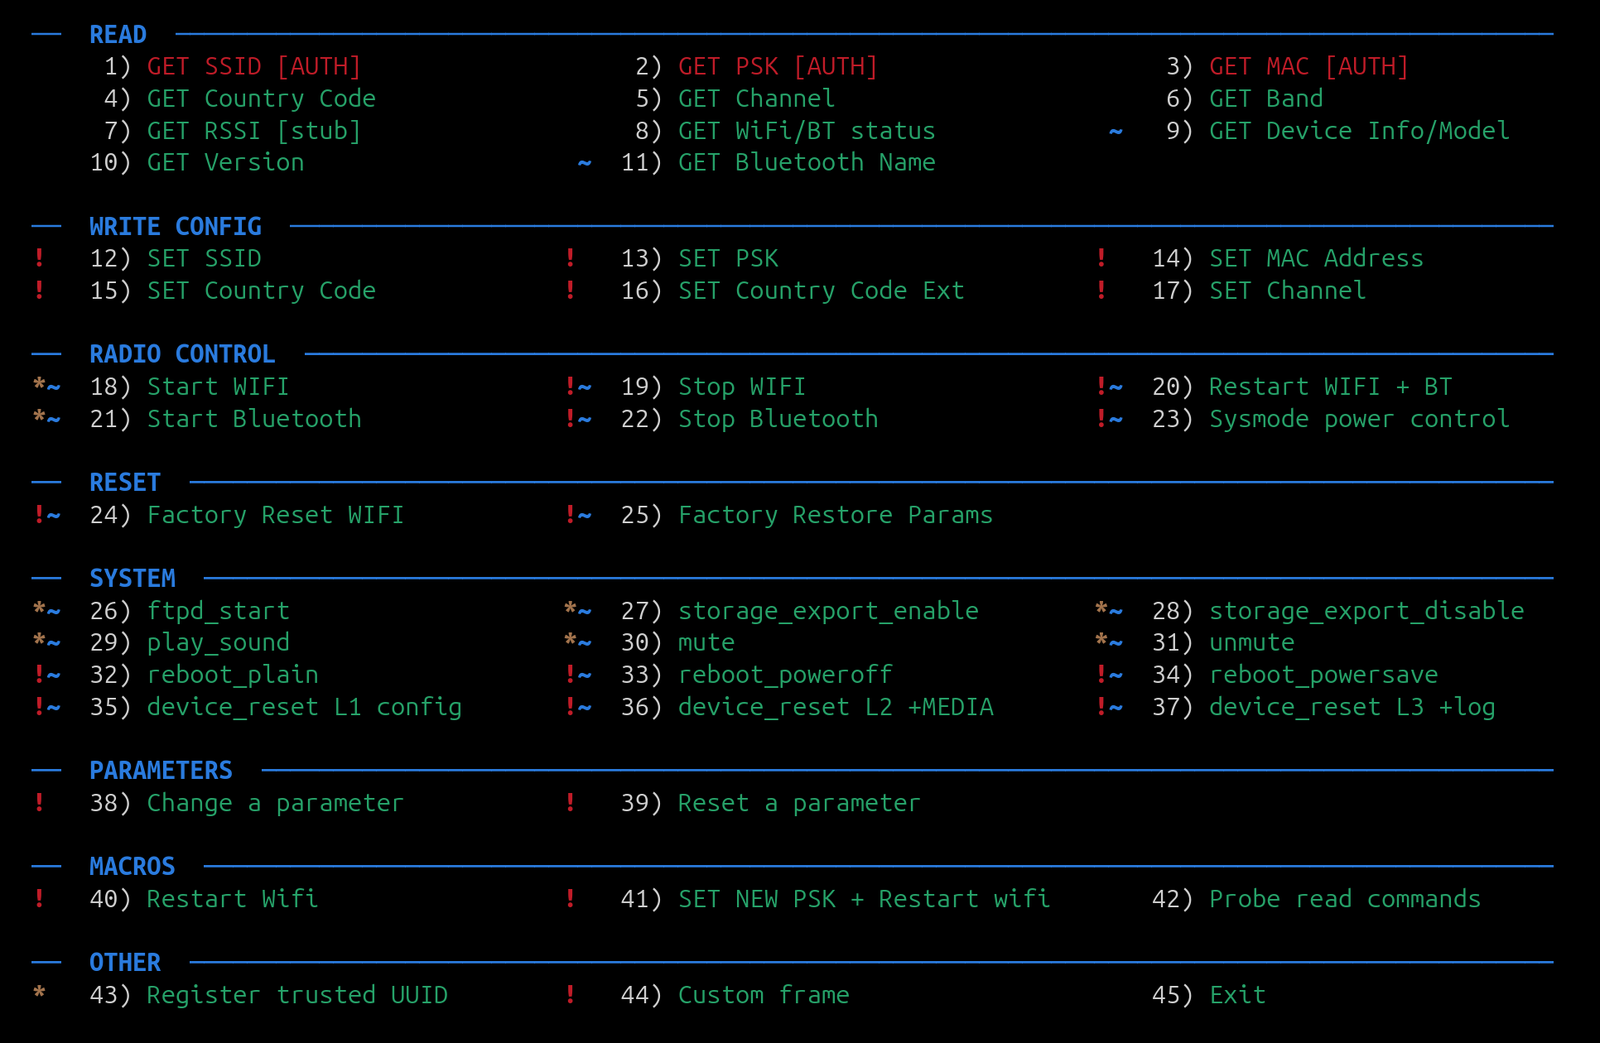
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…

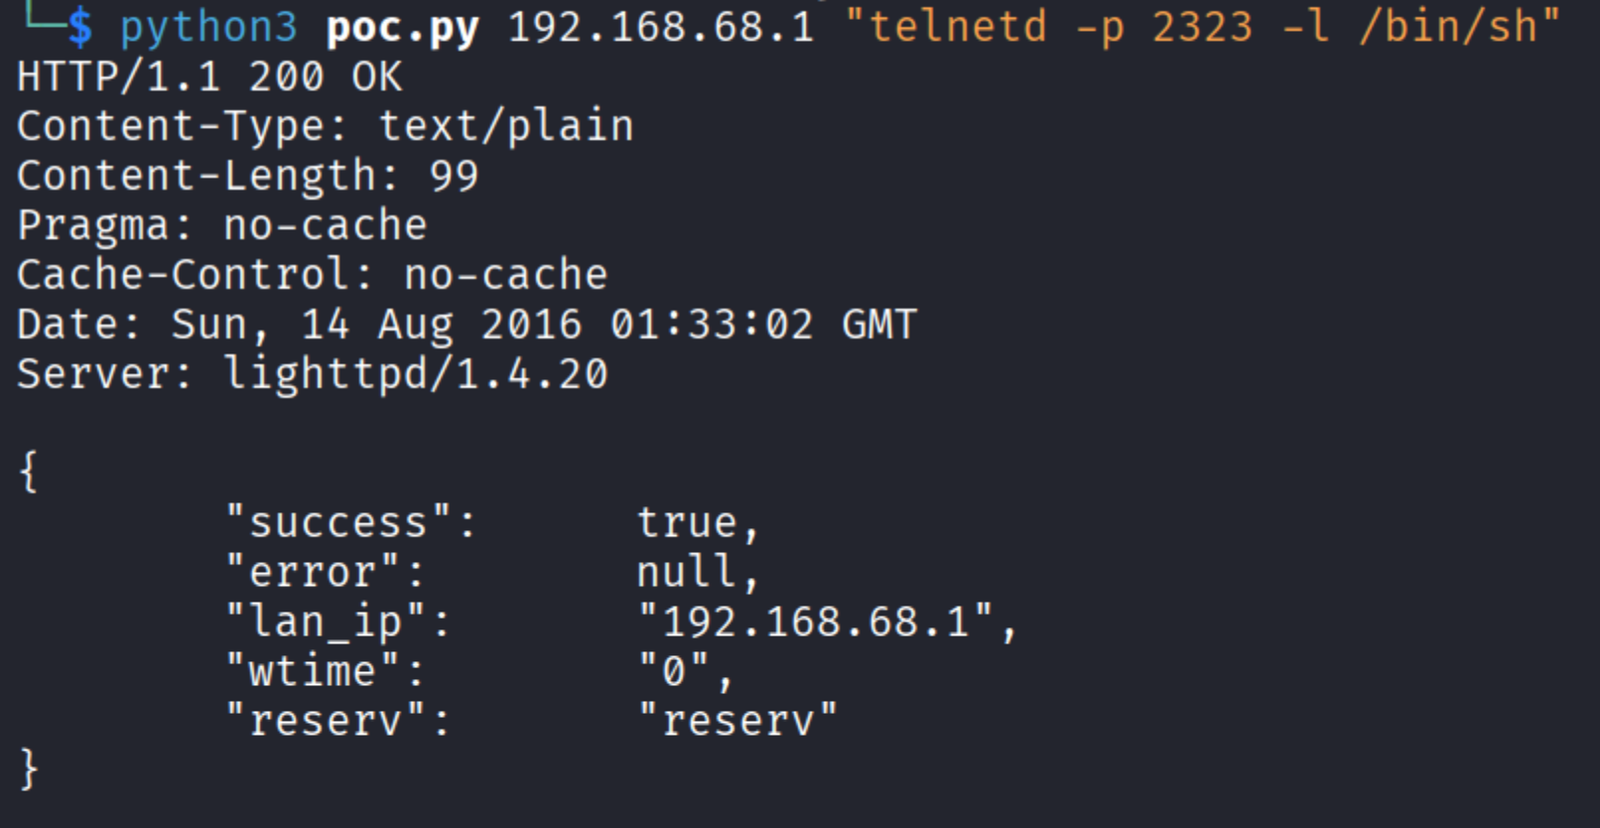
Proof of concept for the command injection vulnerability affecting the ZTE MF286R router, including an RCE exploit.

Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…

ASUS Router infosvr UDP Broadcast root Command Execution

DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306

Proof of concept for arbitrary OS command execution on Guangzhou/V-SOL 1GE ONU devices (CVE-2020-8958)

Proof-of-concept and technical analysis for CVE-2025-11142, an authenticated OS command injection in AXIS VAPIX mediaclip.cgi, with time-based and…

Proof-of-concept exploit for CVE-2026-2670, a command injection vulnerability in Advantech WISE-6610 routers, allowing authenticated attackers to…

Proof of Concept for the CVE-2026-22226

Proof of Concept for CVE-2025-15545

Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…

Toolkit for implant attack of IoT devices

Maxprint Maxlink 1200G v3.4.11E has an OS command injection vulnerability in the "Diagnostic tool" functionality of the device.