CVE-2026-19586
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
command-and-controlcryptographyembedded-systems-security+6
1
mattgsys/cve-2026-19586Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 khaleedbt/netis-cve-2026-36539
Python script that checks Netis routers for CVE-2026-36539, detecting vulnerable devices on a network.
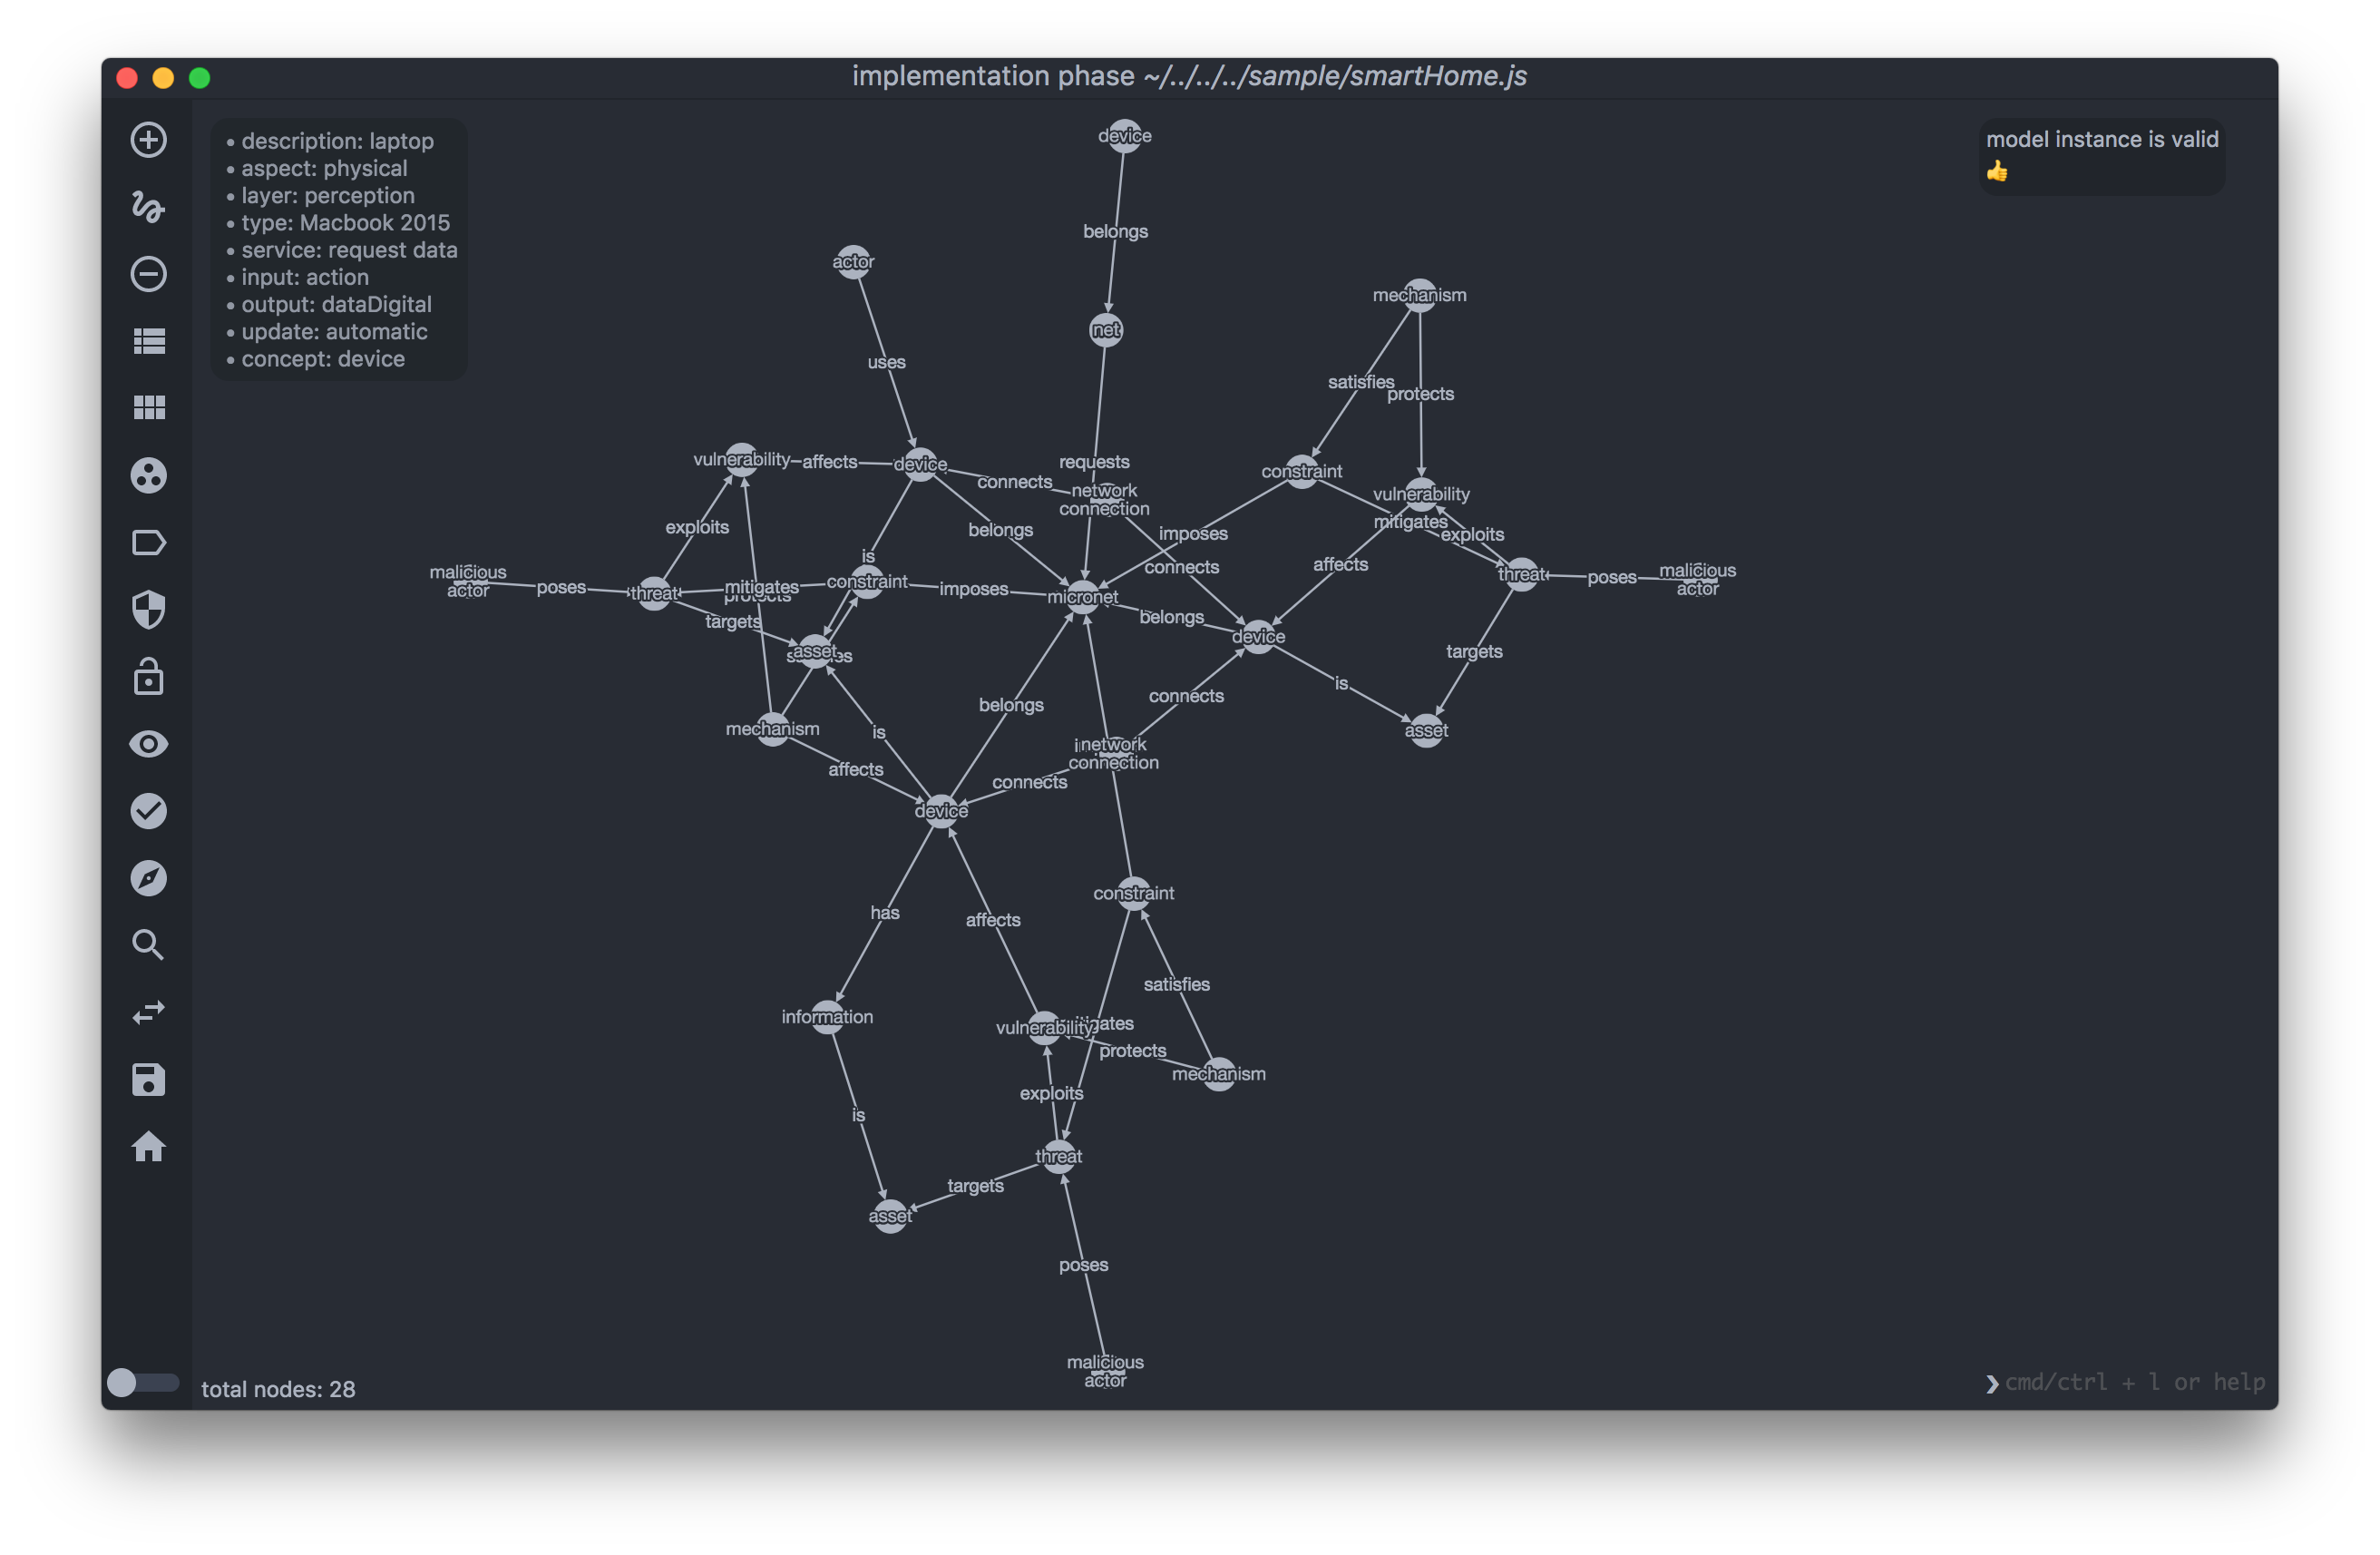 or3stis/apparatus
A graphical security analysis tool for IoT networks
 batchmcnulty/uberscan
Security program for recovering passwords and pen-testing servers, routers and IoT devices using brute-force password attacks.
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 k3ystr0k3r/routeglass
Multi-threaded router fingerprinting tool that identifies web-exposed network devices by analyzing HTTP responses, headers, and favicon hashes for…
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
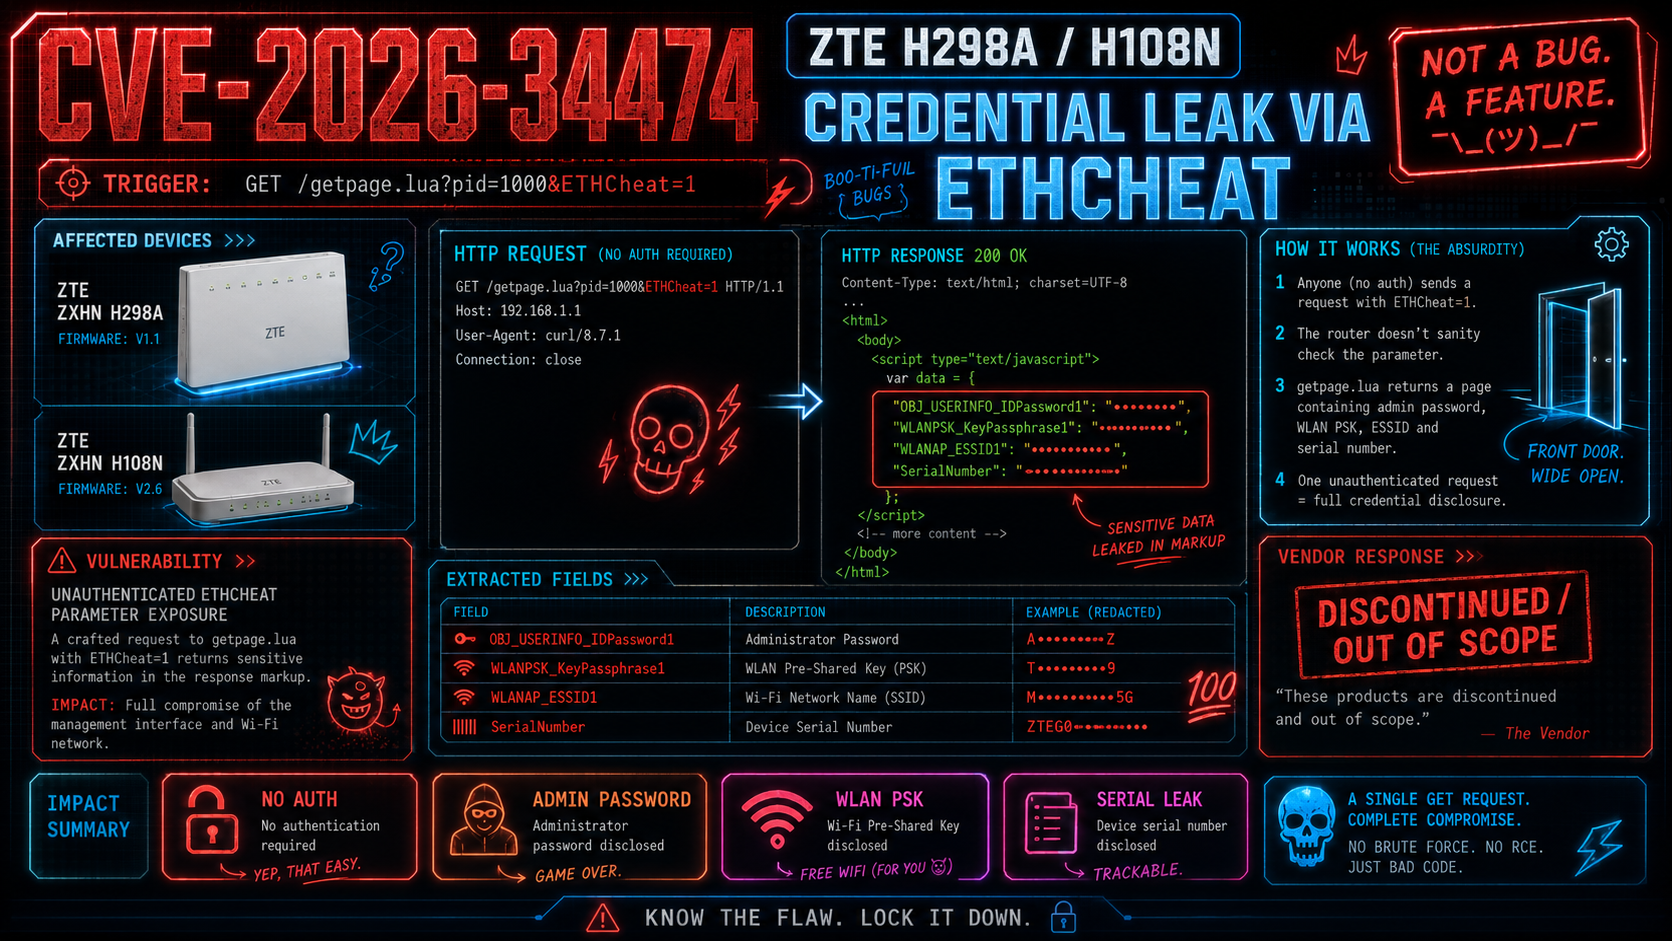 minanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure
CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.