

SirepRAT
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
command-and-controlexploitationiot-security+4
389
safebreach-labs/sirepratRemote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
 bp2008/dahualoginbypass
Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 hacefresko/cve-2021-4045
Exploit for command injection vulnerability found in uhttpd binary from TP-Link Tapo c200 IP camera
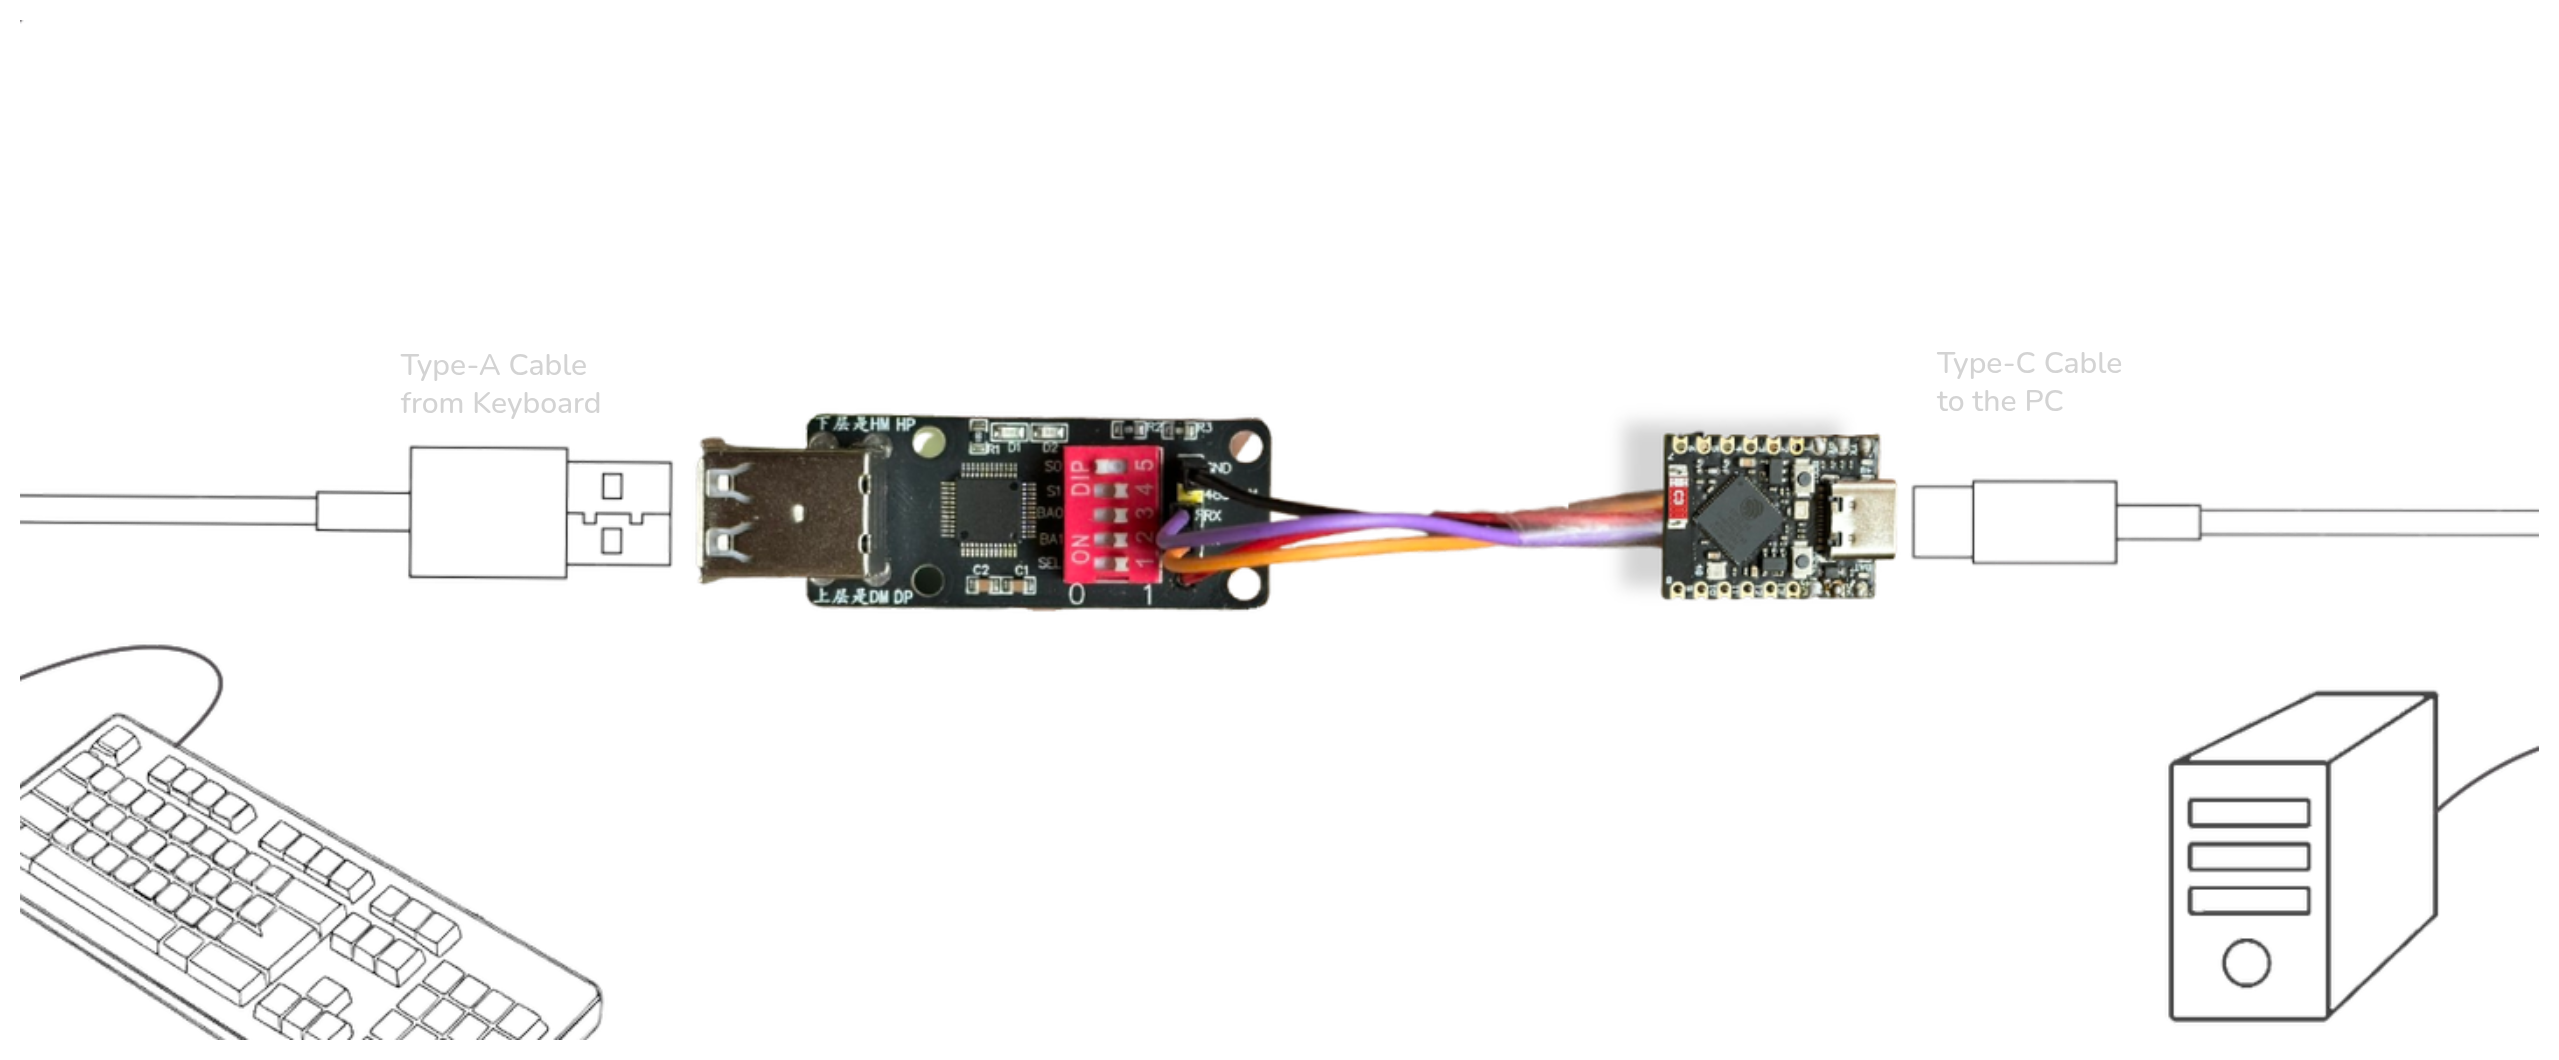 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 golioth/signy
Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…
 verylazytech/cve-2024-10914
POC - CVE-2024–10914- Command Injection Vulnerability in `name` parameter for D-Link NAS
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
 gigaryte/cve-2022-31898
Proof-of-concept exploit for CVE-2022-31898, a command injection vulnerability in GL-iNet routers (firmware < 3.215). Provides reverse shell via…
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
 v0lp3/cve-2022-39073
Proof of concept for the command injection vulnerability affecting the ZTE MF286R router, including an RCE exploit.
 gh-ost00/cve-2024-7120
Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…
 0xbinder/cve-2021-4045
🔐 "PWNTAPO: Unveiling Command Injection in TP-Link Tapo C200 Cameras (<= v1.1.16 Build 211209)" 🔓
 0xnslabs/cve-2022-36267-poc
PoC Script for CVE-2022-36267: Exploits an unauthenticated remote command injection vulnerability in Airspan AirSpot 5410 antenna.
 haniwa0x01/cve-2022-30023
Authenticated command injection exploit for Tenda HG9 routers. Provides interactive remote shell access via Python script for penetration testing and…
 spy0x7/cve-2021-33044
Dahua IPC/VTH/VTO devices auth bypass exploit