

ghidra-mtk-loader
 nccgroup/ghidra-mtk-loader
Ghidra loader for the MediaTek md1img modem firmware image format
binary-analysisembedded-systems-securityfirmware-analysis+3
7
nccgroup/ghidra-mtk-loaderGhidra loader for the MediaTek md1img modem firmware image format
 babyshen/routeros-cve-2018-14847-bytheway
By the Way is an exploit that enables a root shell on Mikrotik devices running RouterOS versions:
 absholi7ly/poc-cve-2024-57040
CVE-2024-57040 is a security vulnerability found in certain TP-Link TL-WR845N router models. Specifically, it involves a "hardcoded" password for the…
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
 thorat-shubham/jxl_infotainment_cve-2025-69515
Proof-of-concept exploit for CVE-2025-69515 demonstrating static GPS spoofing on JXL 9-inch Android infotainment units via SDR-based signal…
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
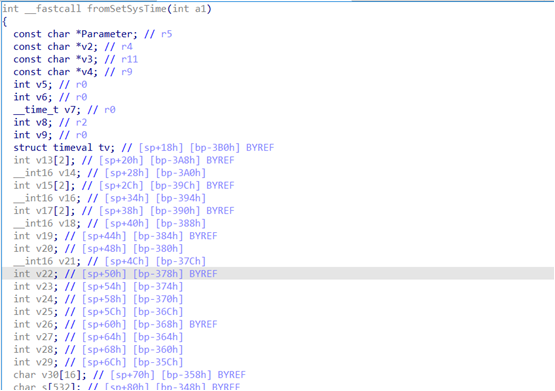 le1a/cve-2022-30040
Proof-of-concept exploit for CVE-2022-30040, a stack buffer overflow in Tenda AX1803 router firmware causing denial-of-service via the SetSysTimeCfg…
 trinadh465/device_renesas_kernel_aosp10_r33_cve-2021-33034
Kernel source tree for Renesas AOSP10 R33 with a patch for CVE-2021-33034, addressing a use-after-free vulnerability in the Bluetooth HCI event…
 i12bp8/tagtinker
Flipper Zero app for infrared electronic shelf-label (ESL) protocol research, featuring custom image transmission, NFC tag scanning, and a web-based…
 nishantjoshi00/flipper-template
Zig development template for Flipper Zero with automated build pipeline, SDK integration, and cross-compilation for ARM Cortex-M4. Supports Sub-GHz,…
 sahilmgandhi/iotshark
IotShark - Monitoring and Analyzing IoT Traffic
 minanagehsalalma/zyxel-cve-2021-35036-super-admin-password-leak
Zyxel super-admin credential exposure write-up across CPE/ONT/LTE/5G firmware, with an adapted VMG8825-B50B genpass lab.
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
 crimsonfiedofficial/cve-2026-29114
Dahua CVE-2026-29114
 themalwareguardian/cve-2021-27289
CVE-2021-27289: Playback Protection Bypass on Ksix Zigbee devices
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 jaden-bowers/tenda-router-vr-and-exploit
Writeup for Tenda AC15 router firmware rehosting and remote command execution (CVE-2020-10987) exploit replication.
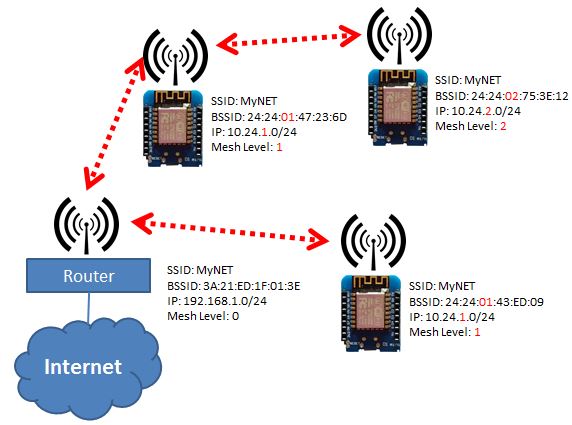 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)