
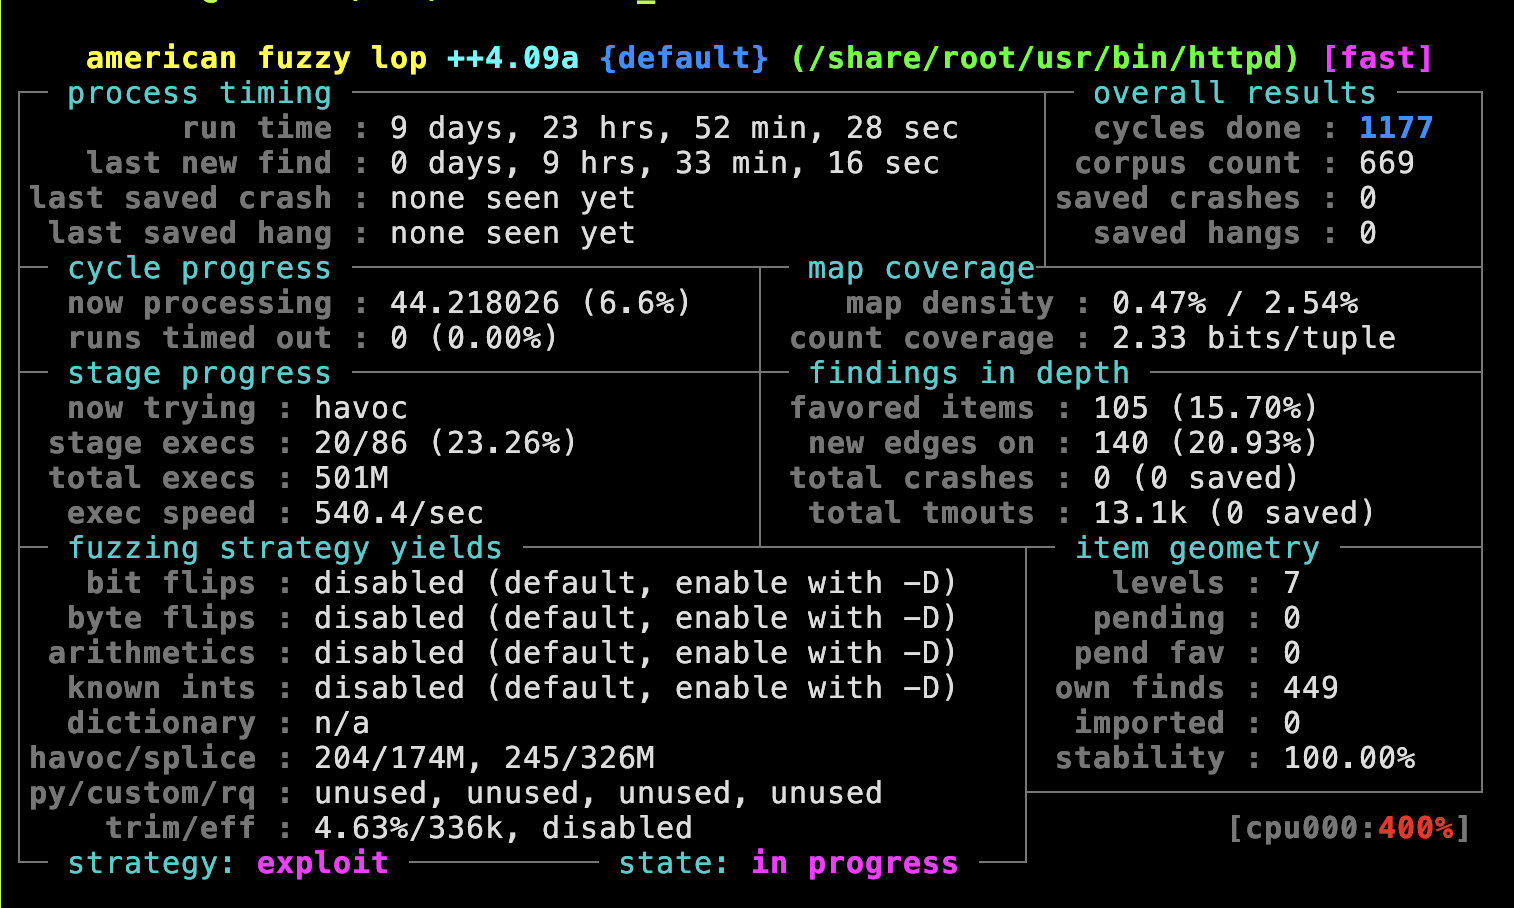
blackbox-fuzzing
 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
binary-analysiseducationexploitation+6
13310 months ago
otsmr/blackbox-fuzzingFuzzing IoT Devices Using the Router TL-WR902AC as Example
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 0ldev/politician
Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…
 runzeroinc/vulns-2026-fatfs-chance
Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.
 hacefresko/cve-2025-40634
Exploit for stack-based buffer overflow found in the conn-indicator binary in the TP-Link Archer AX50 router
 nccgroup/cecster
A GUI-based tool to perform security testing against the HDMI CEC (Consumer Electronics Control) and HEC (HDMI Ethernet Channel) protocols

 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 tin-z/cve-2023-35086-poc
POC of CVE-2023-35086 only DoS
 expliot-framework/expliot
Read only mirror - No pull requests
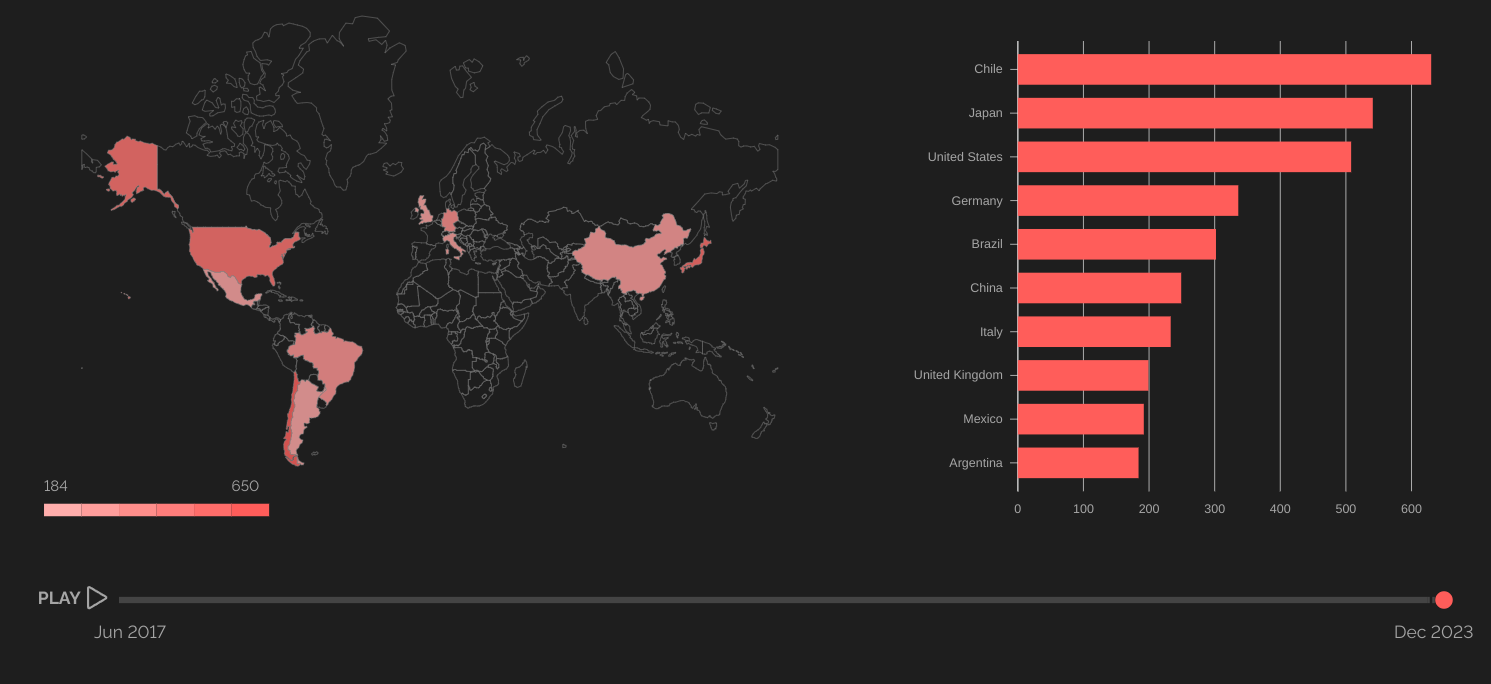 maximilianljungblut/hipcam-rtsp-format-validation-vulnerability
This POC exploits a format validation vulnerability in the RTSP service of the Hipcam RealServer/V1.0, inducing a crash for approximately 45 seconds…
 j4ck3lsyn-gen2/cve-2026-39047
Epson Printer RAW Protocol Exploit Framework
 dest-3/cve-2023-46012
LINKSYS AC1900 EA7500v3 IGD UPnP Stack Buffer Overflow Remote Code Execution Vulnerability
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People
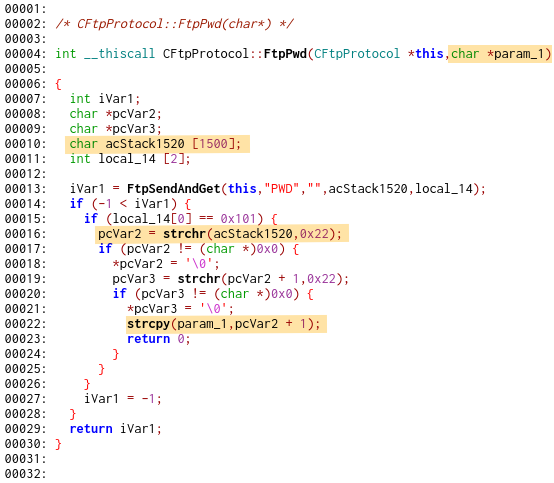 tezeb/accfly
Disclosure of Accfly camera vulnerabilities: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.