

ESP32Marauder
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
bluetooth-securitydefensive-toolsembedded-systems-security+6
12.4k
justcallmekoko/esp32marauderA suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 infobyte/cve-2022-27255
Automated firmware analysis and exploit toolkit for CVE-2022-27255, a Realtek eCos SDK SIP ALG buffer overflow affecting 30+ router models. Includes…
 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 infobyte/ezviz_lan_rce
PoC exploits and Docker build environment for CVE-2023-34551 and CVE-2023-34552 targeting EZVIZ IP cameras, with DEF CON 31 Hardware Hacking Village…
 virtualabs/btlejuice
BLE Man-in-the-Middle framework that intercepts, replays, and modifies GATT traffic between Bluetooth Smart devices and mobile apps via a web-based…
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 wallyschag/cve-2025-41656
This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656
 istaarkk/cve-2025-65817
Here is the CVE-2025-65817
 db44k/cve-2018-5767-ac9
An implementation of a proof-of-concept for CVE-2018-5767 (https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-5767)
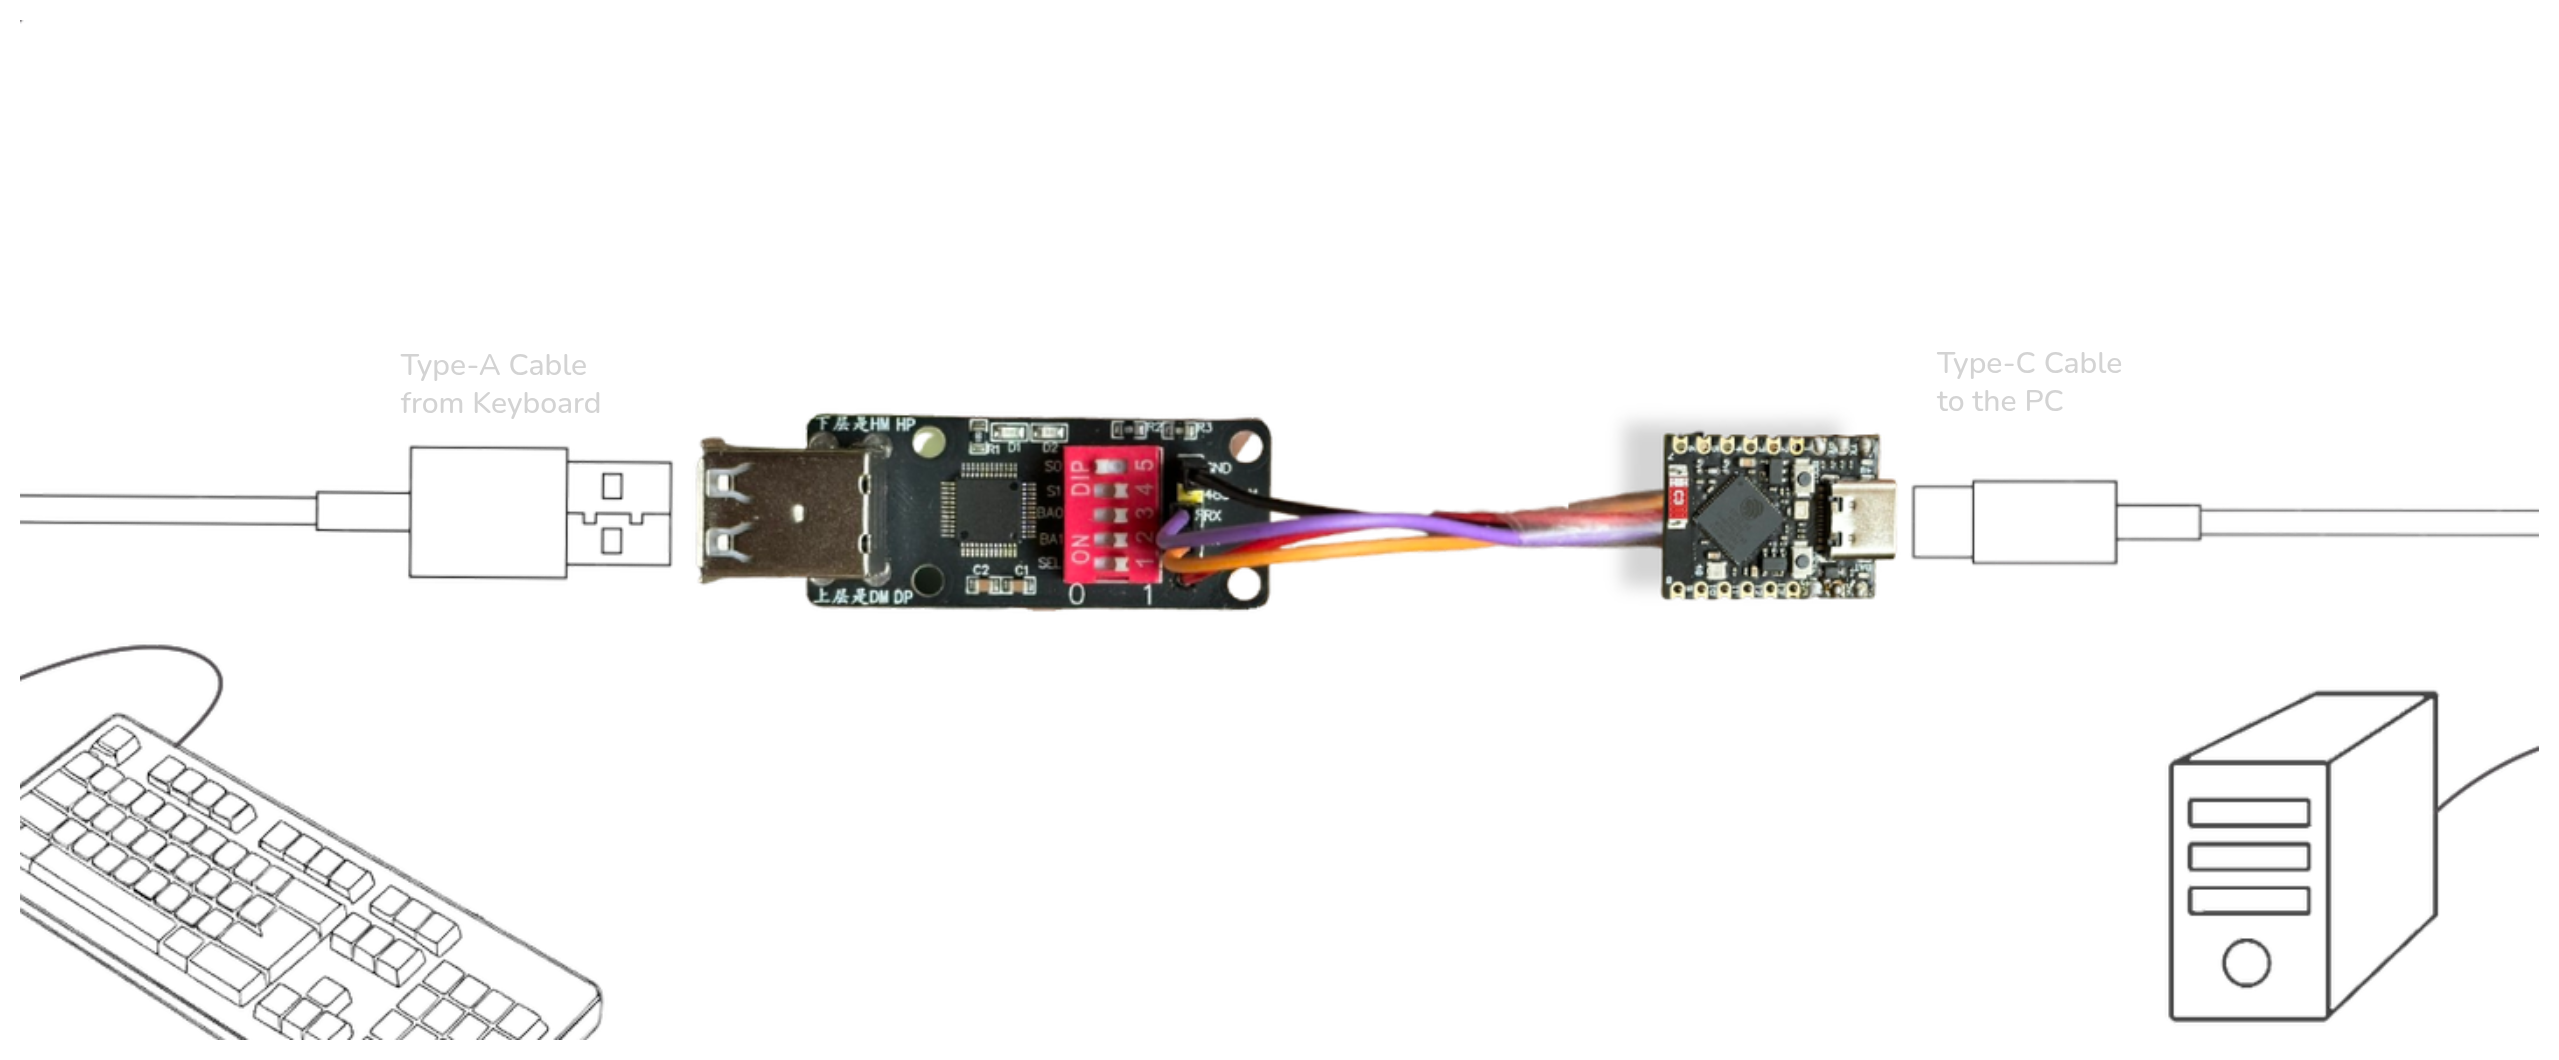 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 spiralbl0ck/iot_hacking_camera_0day
Iot Camera 0day
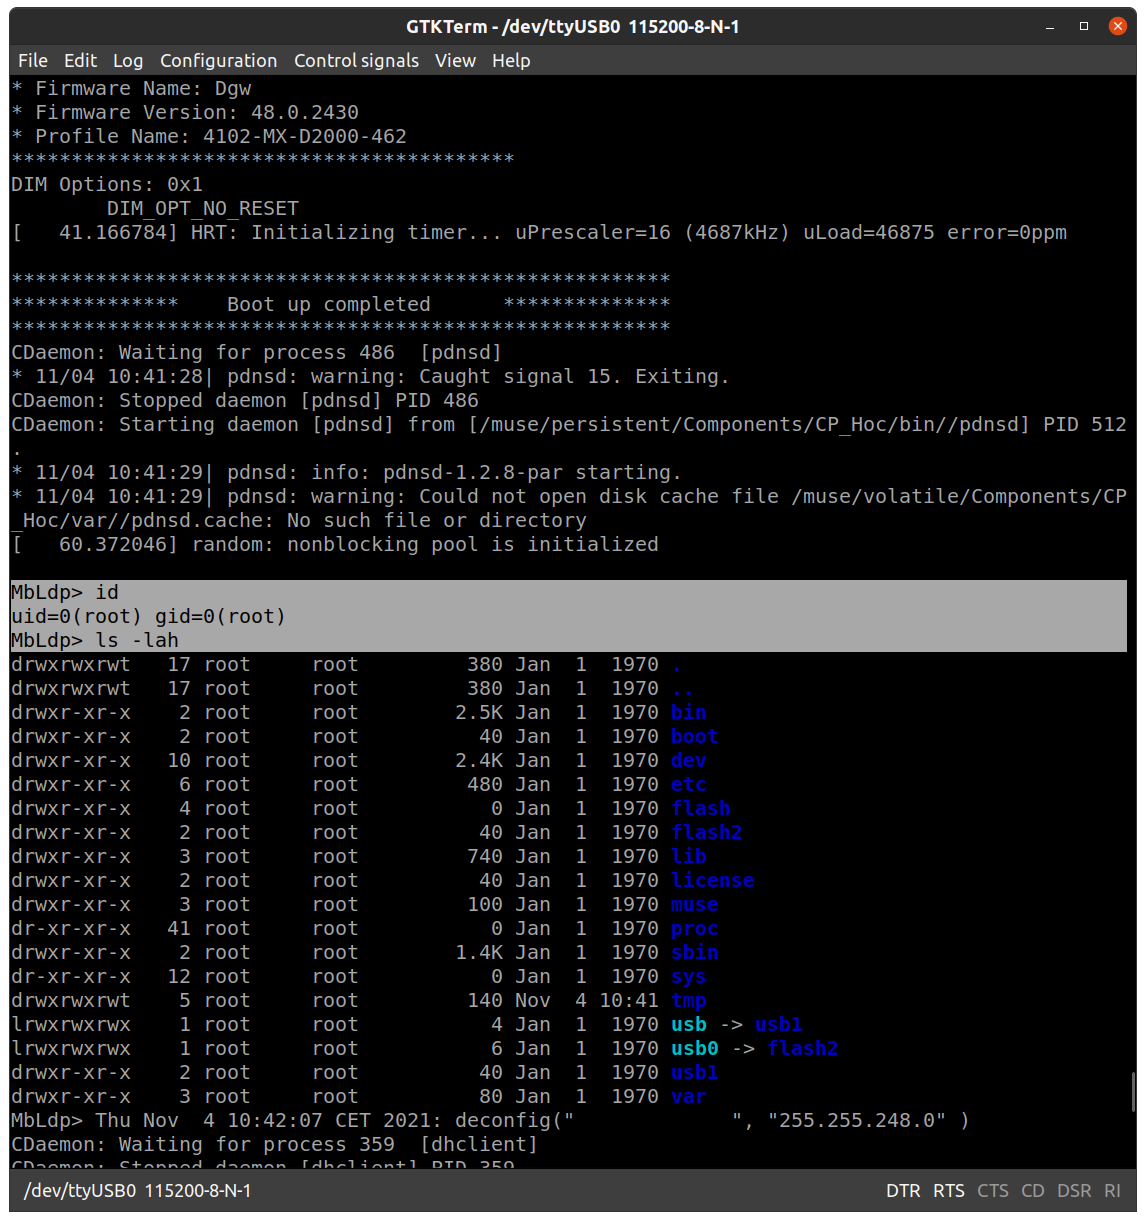 proxystaffy/mediatrix-cve-2022-43096
Proof-of-concept exploit for CVE-2022-43096, demonstrating local root access via UART port on Mediatrix 4102 devices before v48.5.2718.
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 george0papasotiriou/cve-2026-21009-ecdsa-nonce-reuse-in-iot-firmware-signing
Educational Python simulation demonstrating ECDSA nonce reuse in IoT firmware signing, showing how an attacker can recover private keys from two…
 redr0nin/code-27-companion-hub-exploits
Proof of concept for CVE-2026-36027 and CVE-2026-36028
 hacefresko/cve-2025-40634
Exploit for stack-based buffer overflow found in the conn-indicator binary in the TP-Link Archer AX50 router
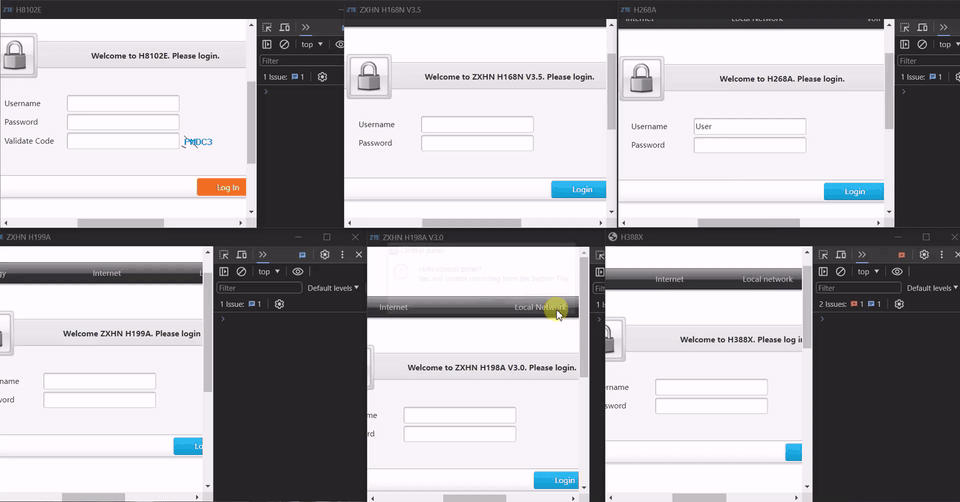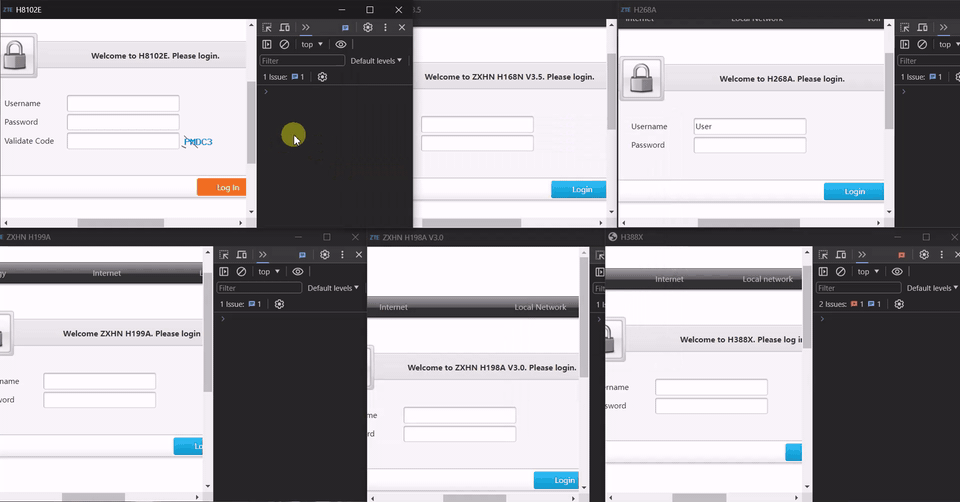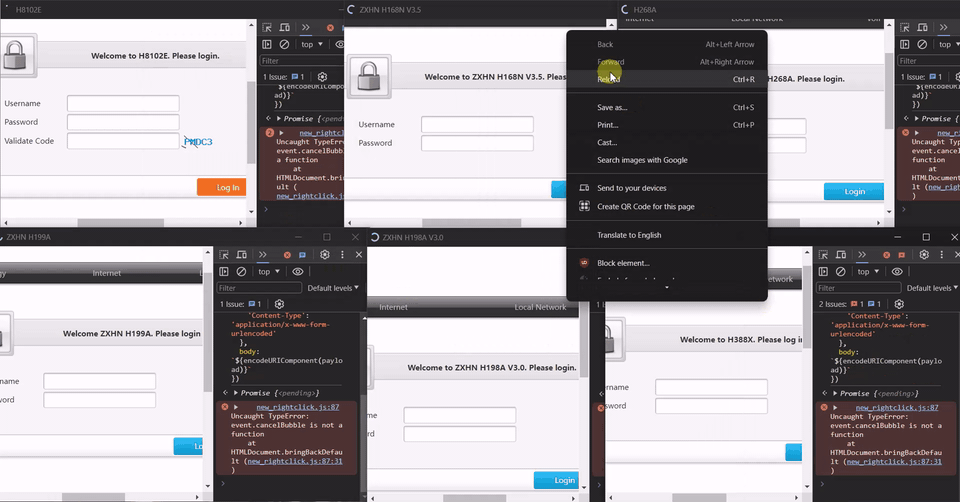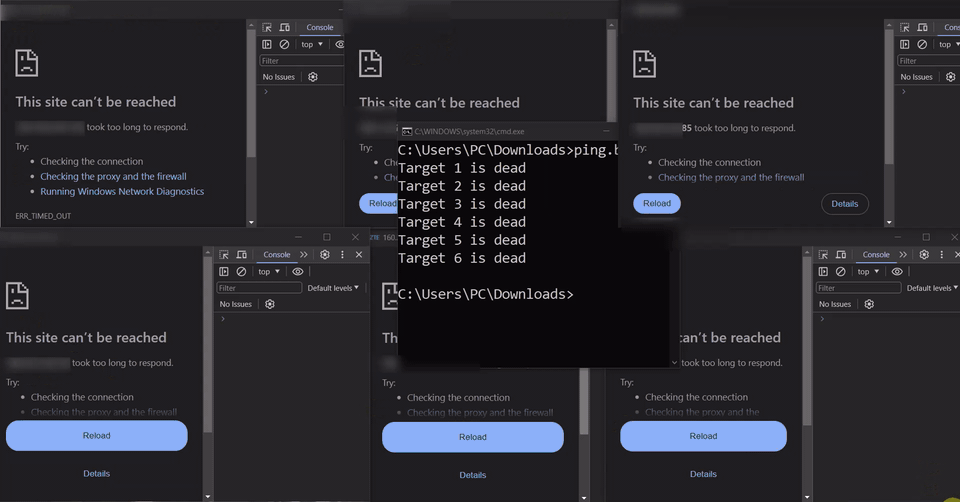 minanagehsalalma/cve-2026-34473-unauthenticated-dos-zte-routers
Technical breakdown of CVE-2026-34473, an unauthenticated denial of service affecting 17+ ZTE router models.
 yashodhanvivek/agatsa-easytouch-plus---cve-2025-56019
This report is for CVE-2025-56019 reserved for Easytouch+product for BLE authentication vulnerability assigned to Discoverer Yashodhan Vivek Mandke.…