Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
428 results
obike preview

obike

GitHubantoinet/obike

Reverse engineering of the oBike protocol communication (BLE and HTTP)
api-securitybluetooth-securitycryptography+4
427 years ago
CVE-2022-39066 preview

CVE-2022-39066

GitHubv0lp3/cve-2022-39066

Proof of concept of the SQL injection vulnerability affecting the ZTE MF286R router.
embedded-systems-securityexploitationiot-security+3
113 years ago
CVE-2025-22968 preview

CVE-2025-22968

GitHubcrunzex/cve-2025-22968

Unauthenticated access in the default configuration of the D-Link DWR-M972V
embedded-systems-securityexploitationiot-security+3
61 year ago
ShiningAppMask-ReverseEngineering preview

ShiningAppMask-ReverseEngineering

GitHubadrihd/shiningappmask-reverseengineering

Reverse Engineering of the Shining App Mask

bluetooth-securityembedded-systems-securityfirmware-analysis+5
67 months ago
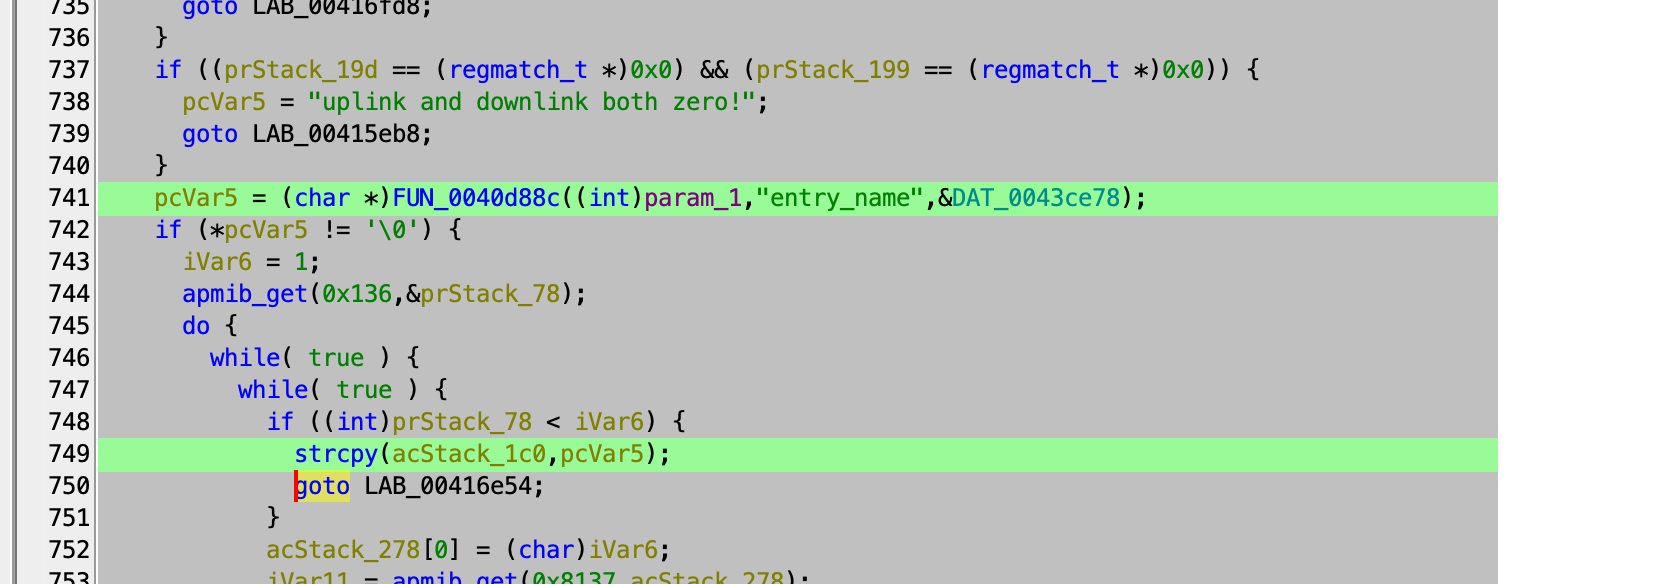
esp32-cve-2025-27840-power-trace-experiment preview

esp32-cve-2025-27840-power-trace-experiment

GitHubjasonw88/esp32-cve-2025-27840-power-trace-experiment

Firmware for getting a power trace of the behavior of the bluetooth module on the ESP32 when the ESP32 is sent the undocumented hci bluetooth…
bluetooth-securityembedded-systems-securityhardware-hacking+2
1 month ago
CVE-2018-14847 preview

CVE-2018-14847

GitHubthemalwareguardian/cve-2018-14847

Analysis and PoC for CVE-2018-14847, MikroTik RouterOS Winbox information disclosure vulnerability allowing unauthenticated read access to the…
embedded-systems-securityexploitationinformation-gathering+3
4 months ago
CVE-2018-12633-TPLink-Auth-Bypass preview

CVE-2018-12633-TPLink-Auth-Bypass

GitHubwiliam227user/cve-2018-12633-tplink-auth-bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
data-exfiltrationeducationembedded-systems-security+8
8 months ago
CVE-2024-35106-POC preview

CVE-2024-35106-POC

GitHublaskdjlaskdj12/cve-2024-35106-poc

Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

binary-exploitationembedded-systems-securityexploitation+5
1 year ago
ripple20 preview

ripple20

GitHubcorelight/ripple20

A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
anomaly-detectionintrusion-detectioniot-security+3
324 years ago
bd-alaris-firmware-analysis preview

bd-alaris-firmware-analysis

GitHubnadafarafat/bd-alaris-firmware-analysis

Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…
cryptographyeducationembedded-systems-security+5
3 months ago
TP-Link-TL-WR820N-CVE-2025-14175 preview

TP-Link-TL-WR820N-CVE-2025-14175

GitHubcybervinner/tp-link-tl-wr820n-cve-2025-14175

Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.
cryptographyeducationembedded-systems-security+3
8 months ago
CMF-Watch-Pro-2-BLE-Protocol preview

CMF-Watch-Pro-2-BLE-Protocol

GitHubjoshuapassos/cmf-watch-pro-2-ble-protocol

Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
bluetooth-securitycryptographyembedded-systems-security+6
51 month ago
CVE-2026-32707-PX4-Autopilot-tattu_can-Stack-Buffer-Overflow-DoS- preview

CVE-2026-32707-PX4-Autopilot-tattu_can-Stack-Buffer-Overflow-DoS-

GitHubmbanyamer/cve-2026-32707-px4-autopilot-tattu_can-stack-buffer-overflow-dos-

Proof-of-concept exploit for CVE-2026-32707, a stack buffer overflow in the PX4-Autopilot tattu_can driver, causing denial of service via crafted CAN…
binary-exploitationembedded-systems-securityexploitation+4
4 months ago
cve-2026-8697 preview

cve-2026-8697

GitHubitzmetanjim/cve-2026-8697

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…
educationexploitationhardware-iot-security+7
13 months ago
CVE-2025-63587 preview

CVE-2025-63587

GitHubnrtlox/cve-2025-63587

CVE-2025-63587

authenticationhardware-securityinformation-gathering+3
6 months ago
aziot-cctv-cve-2025-50777 preview

aziot-cctv-cve-2025-50777

GitHubveereshgadige/aziot-cctv-cve-2025-50777

CVE-2025-50777: Root Access and Plaintext Credential Exposure in AZIOT Smart CCTV
educationembedded-systems-securityexploitation+8
1 year ago
CVE-2021-37740 preview
Archived

CVE-2021-37740

GitHubrobertguetzkow/cve-2021-37740

PoC for DoS vulnerability CVE-2021-37740 in firmware v3.0.3 of SCN-IP100.03 and SCN-IP000.03 by MDT. The bug has been fixed in firmware v3.0.4.
embedded-systems-securityexploitationhardware-iot-security+2
64 years ago
chipwhisperer preview

chipwhisperer

GitHubnewaetech/chipwhisperer

Open-source hardware security toolchain for power trace capture, side-channel analysis, and glitching/fault-injection attacks on embedded devices and…

cryptographyembedded-systems-securityfirmware-analysis+5
1.6k17 days ago
Previous1…121314…24Next