

XSS-CVE-2022-30489
 badboycxcc/xss-cve-2022-30489
Proof-of-concept exploit for CVE-2022-30489, a stored XSS vulnerability in WAVLINK WN535G3 routers, demonstrating a POST-based attack via the…
exploitationiot-securitypenetration-testing+3
2
badboycxcc/xss-cve-2022-30489Proof-of-concept exploit for CVE-2022-30489, a stored XSS vulnerability in WAVLINK WN535G3 routers, demonstrating a POST-based attack via the…
 wmasday/htc
Hack The CCTV | DVRs; Credentials Exposed | CVE-2018-9995
 kh4sh3i/cve-2025-34152
Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…
 lodi-g/cve-2019-13361
Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
 exploitwritter/cve-2022-25064
This script exploits a remote command execution vulnerability in the TPLink WR840N router, using the configure function IPv6 protocol.
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 netsecfish/dlink
Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 gh-ost00/cve-2024-7120
Proof-of-concept exploit for CVE-2024-7120 command injection vulnerability in RAISECOM gateway devices. Provides exploitation details, affected…
 shadowgatt/cve-2019-19356
Netis router RCE exploit ( CVE-2019-19356)
 vakzz/tplink-cve-2017-11519
POC for TP-Link Archer C9 - Admin Password Reset and RCE (CVE-2017-11519)
 bayazid-bit/cve-2018-18441-exploit
D-Link DCS series Wi-Fi camera expose sensitive information.
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 bytereaper77/cve-2025-9090
Command Injection in Tenda AC20 16.03.08.12 (/goform/telnet)
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…
 otsmr/internet-of-vulnerable-things
The results of my small term paper on the topic of the Internet of Vulnerable Things and the exploit for CVE-2022-48194.
 taxanehh/cve-2025-34037
Python port of the Linksys tmUnblock.cgi RCE exploit
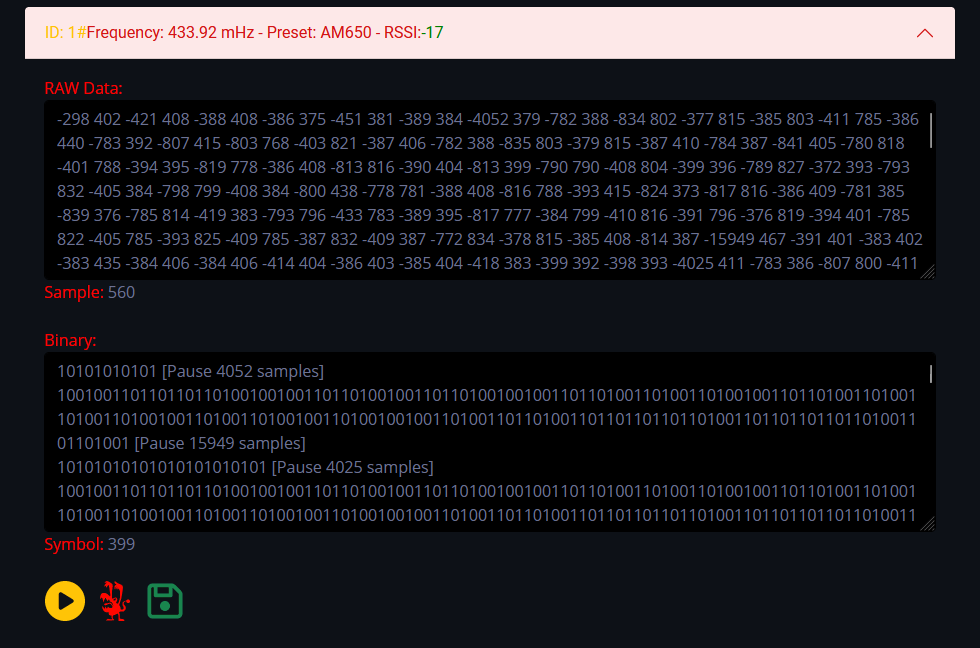 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.