
openwisp-controller
Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…

Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…

C++ implementation of SIP, ICE, TURN and related protocols.

A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…

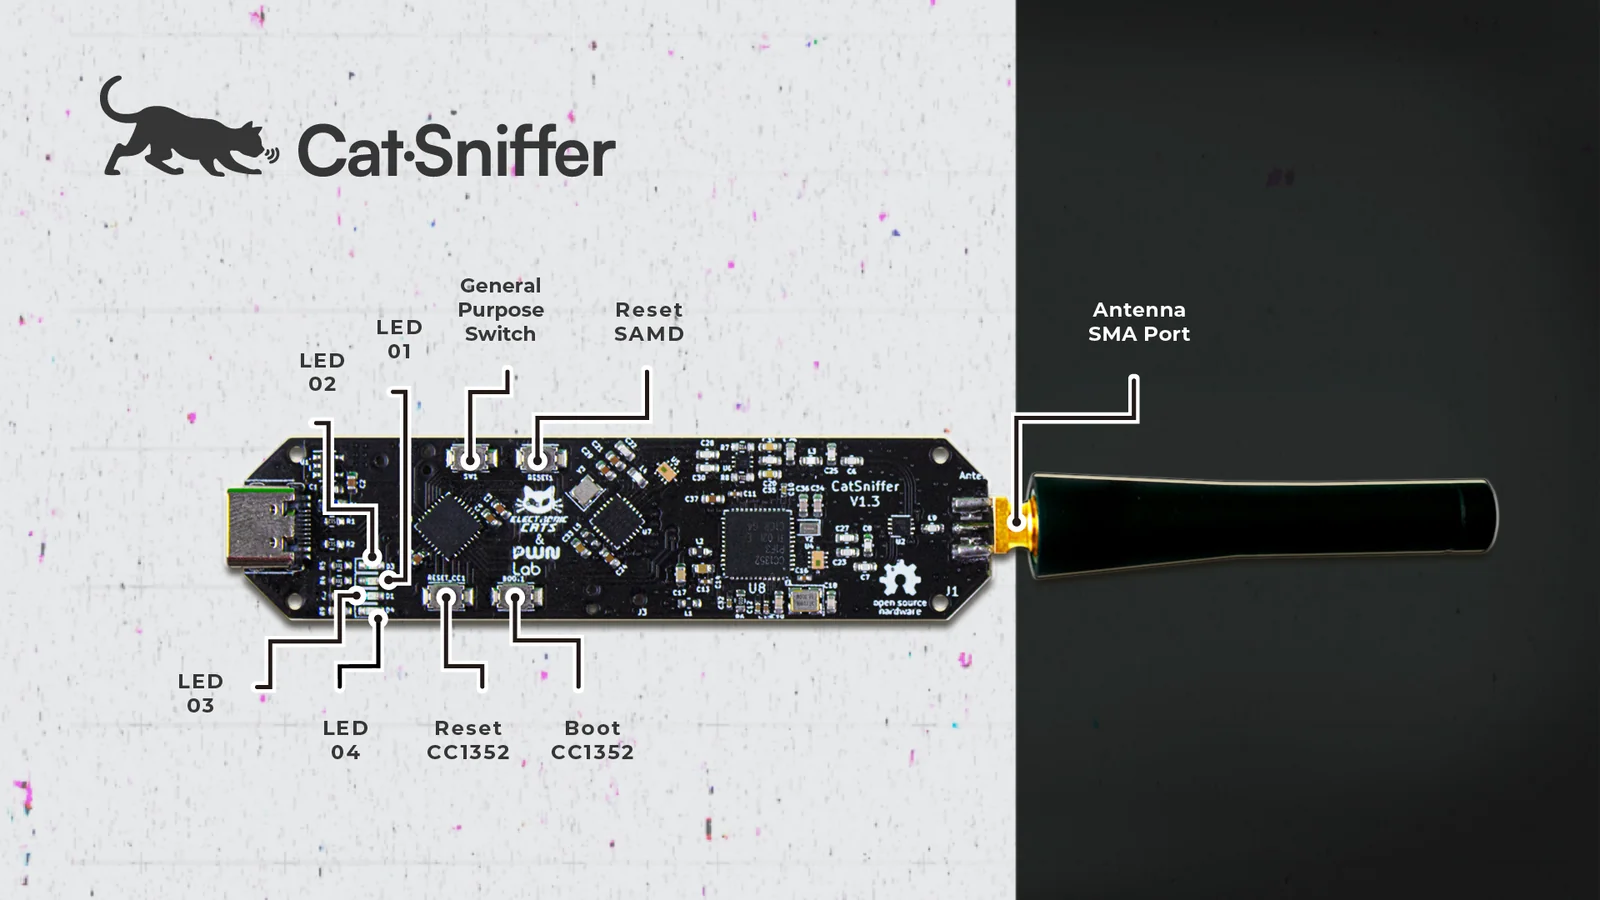
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…


CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)

CVE-2026-25197: Authorization Bypass via IDOR — Gardyn Home Kit (ICSA-26-055-03)

CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…

BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…

Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…

Reolink Duo 2 WiFi v1.0.280 - Account Enumeration Vulnerability

POC VIDEO - https://youtu.be/hNzmkJj-ImM?si=NF0yoSL578rNy7wN

The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)

Exploit for CVE-2017-7921 targeting Hikvision devices with improper authentication. Retrieves user lists, camera snapshots, and configuration files…