
zephyr
 zephyrproject-rtos/zephyr
Primary Git Repository for the Zephyr Project. Zephyr is a new generation, scalable, optimized, secure RTOS for multiple hardware architectures.
bluetooth-securitycurated-resourceseducation+4
16.9k
zephyrproject-rtos/zephyrPrimary Git Repository for the Zephyr Project. Zephyr is a new generation, scalable, optimized, secure RTOS for multiple hardware architectures.
 stratosphereips/aip
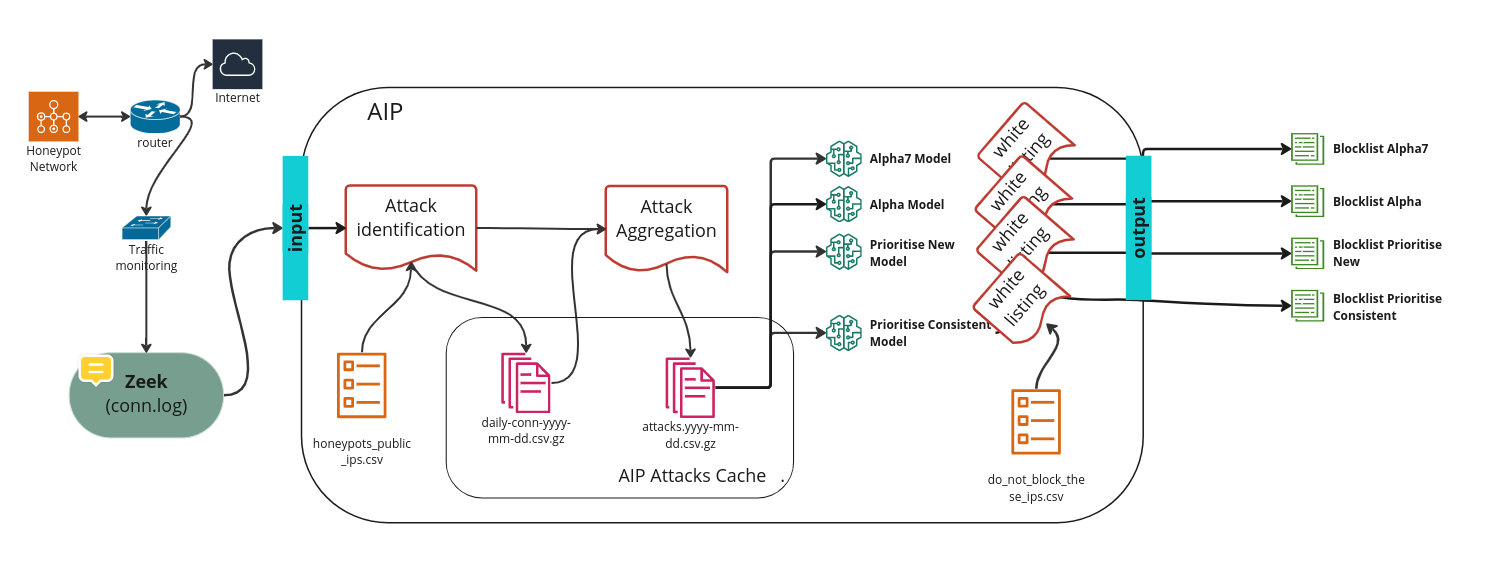
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 roxanne_ardary/ai-and-the-automobile
Curated collection of open specifications for AI-integrated vehicle systems, covering autonomy, perception, navigation, energy management, safety,…
 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
 pwnonu/t3-technology-cpe-advisories
CVE-2026-35904 / CVE-2026-35905 / CVE-2026-35906 — Unauth RCE, Hardcoded Root Creds & Telnet Enable in T3 Technology CPE
 eagle-nett/dahua_auth-bypass-cve-2021-33044
PoC exploit for Dahua authentication bypass (CVE-2021-33044). Scans subnets, tests multiple CVEs, and dumps device configs via crafted cookies…
 remenis/cve-2025-67160
Vatilon-based IP cameras expose internal web directories without authentication, leading to information disclosure.
 luismirandaacebedo/cve-2025-65855
Security advisory for CVE-2025-65855 - Multiple vulnerabilities in HelpFlash IoT OTA update mechanism
 0xf3d0rq/cve-2017-7921
CVE-2017-7921 is a critical vulnerability (CVSS score: 9.8) affecting multiple Hikvision IP camera and DVR models, first disclosed in 2017. It stems…
 joelczk/cve-2025-52688
Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…
 sfewer-r7/brothervulnerabilities
Multiple Brother Devices: Multiple Vulnerabilities (CVE-2024-51977, CVE-2024-51978, CVE-2024-51979, CVE-2024-51980, CVE-2024-51981, CVE-2024-51982,…
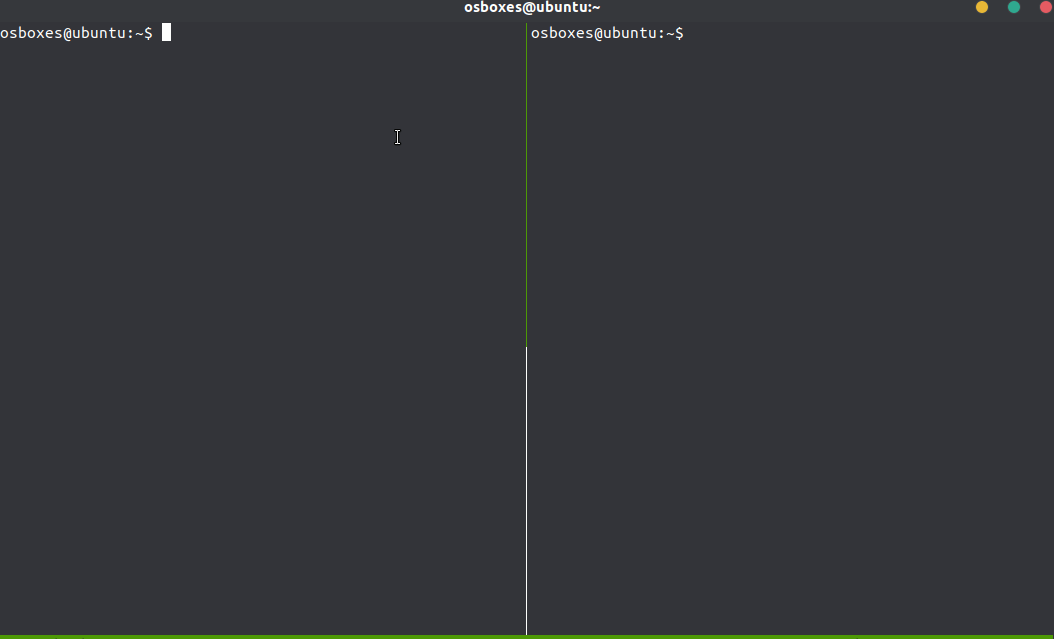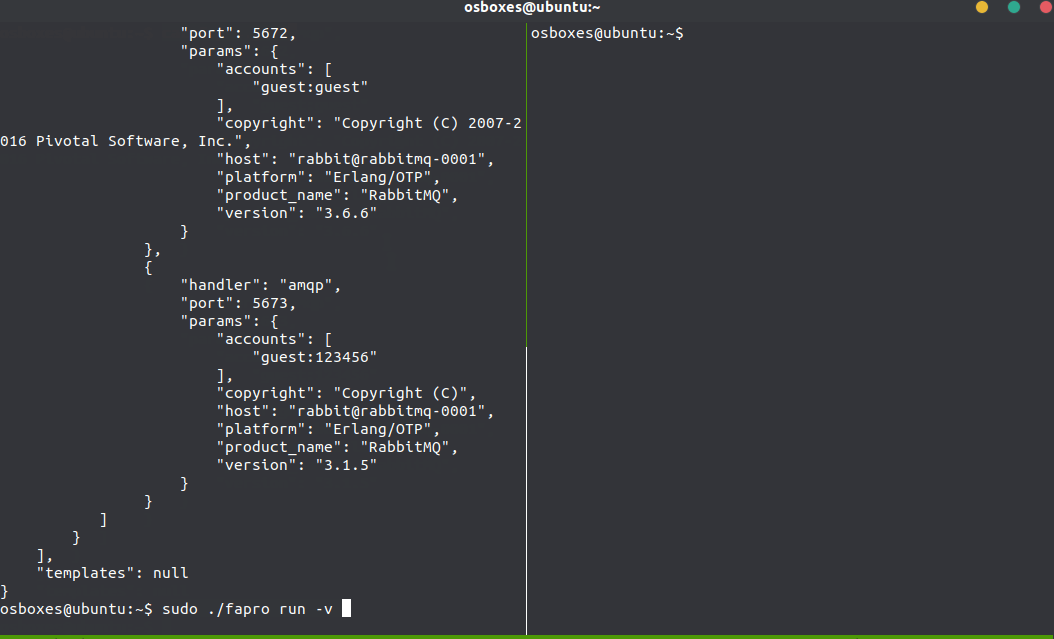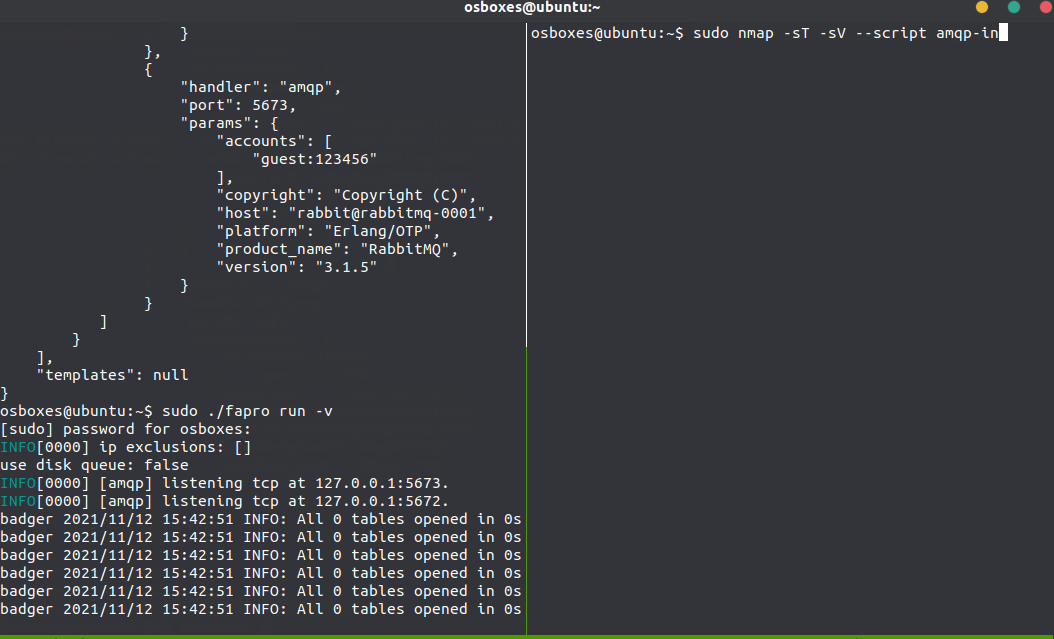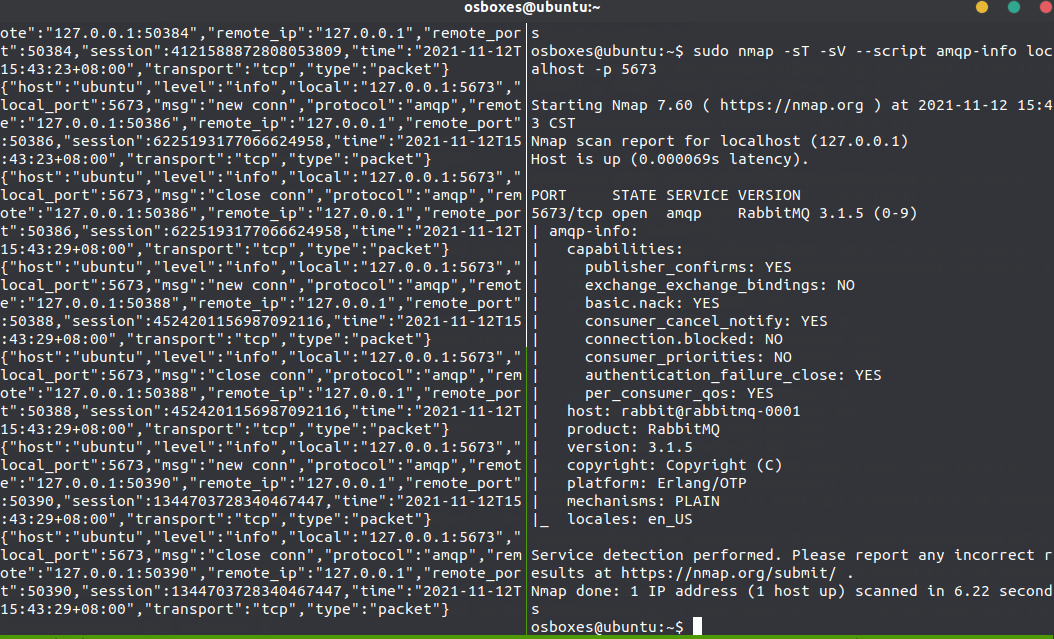 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
 batmoshka55/cve-2018-9995_dvr_credentials
Exploit tool for CVE-2018-9995 that retrieves DVR credentials via crafted HTTP request, targeting multiple DVR vendors for security testing.
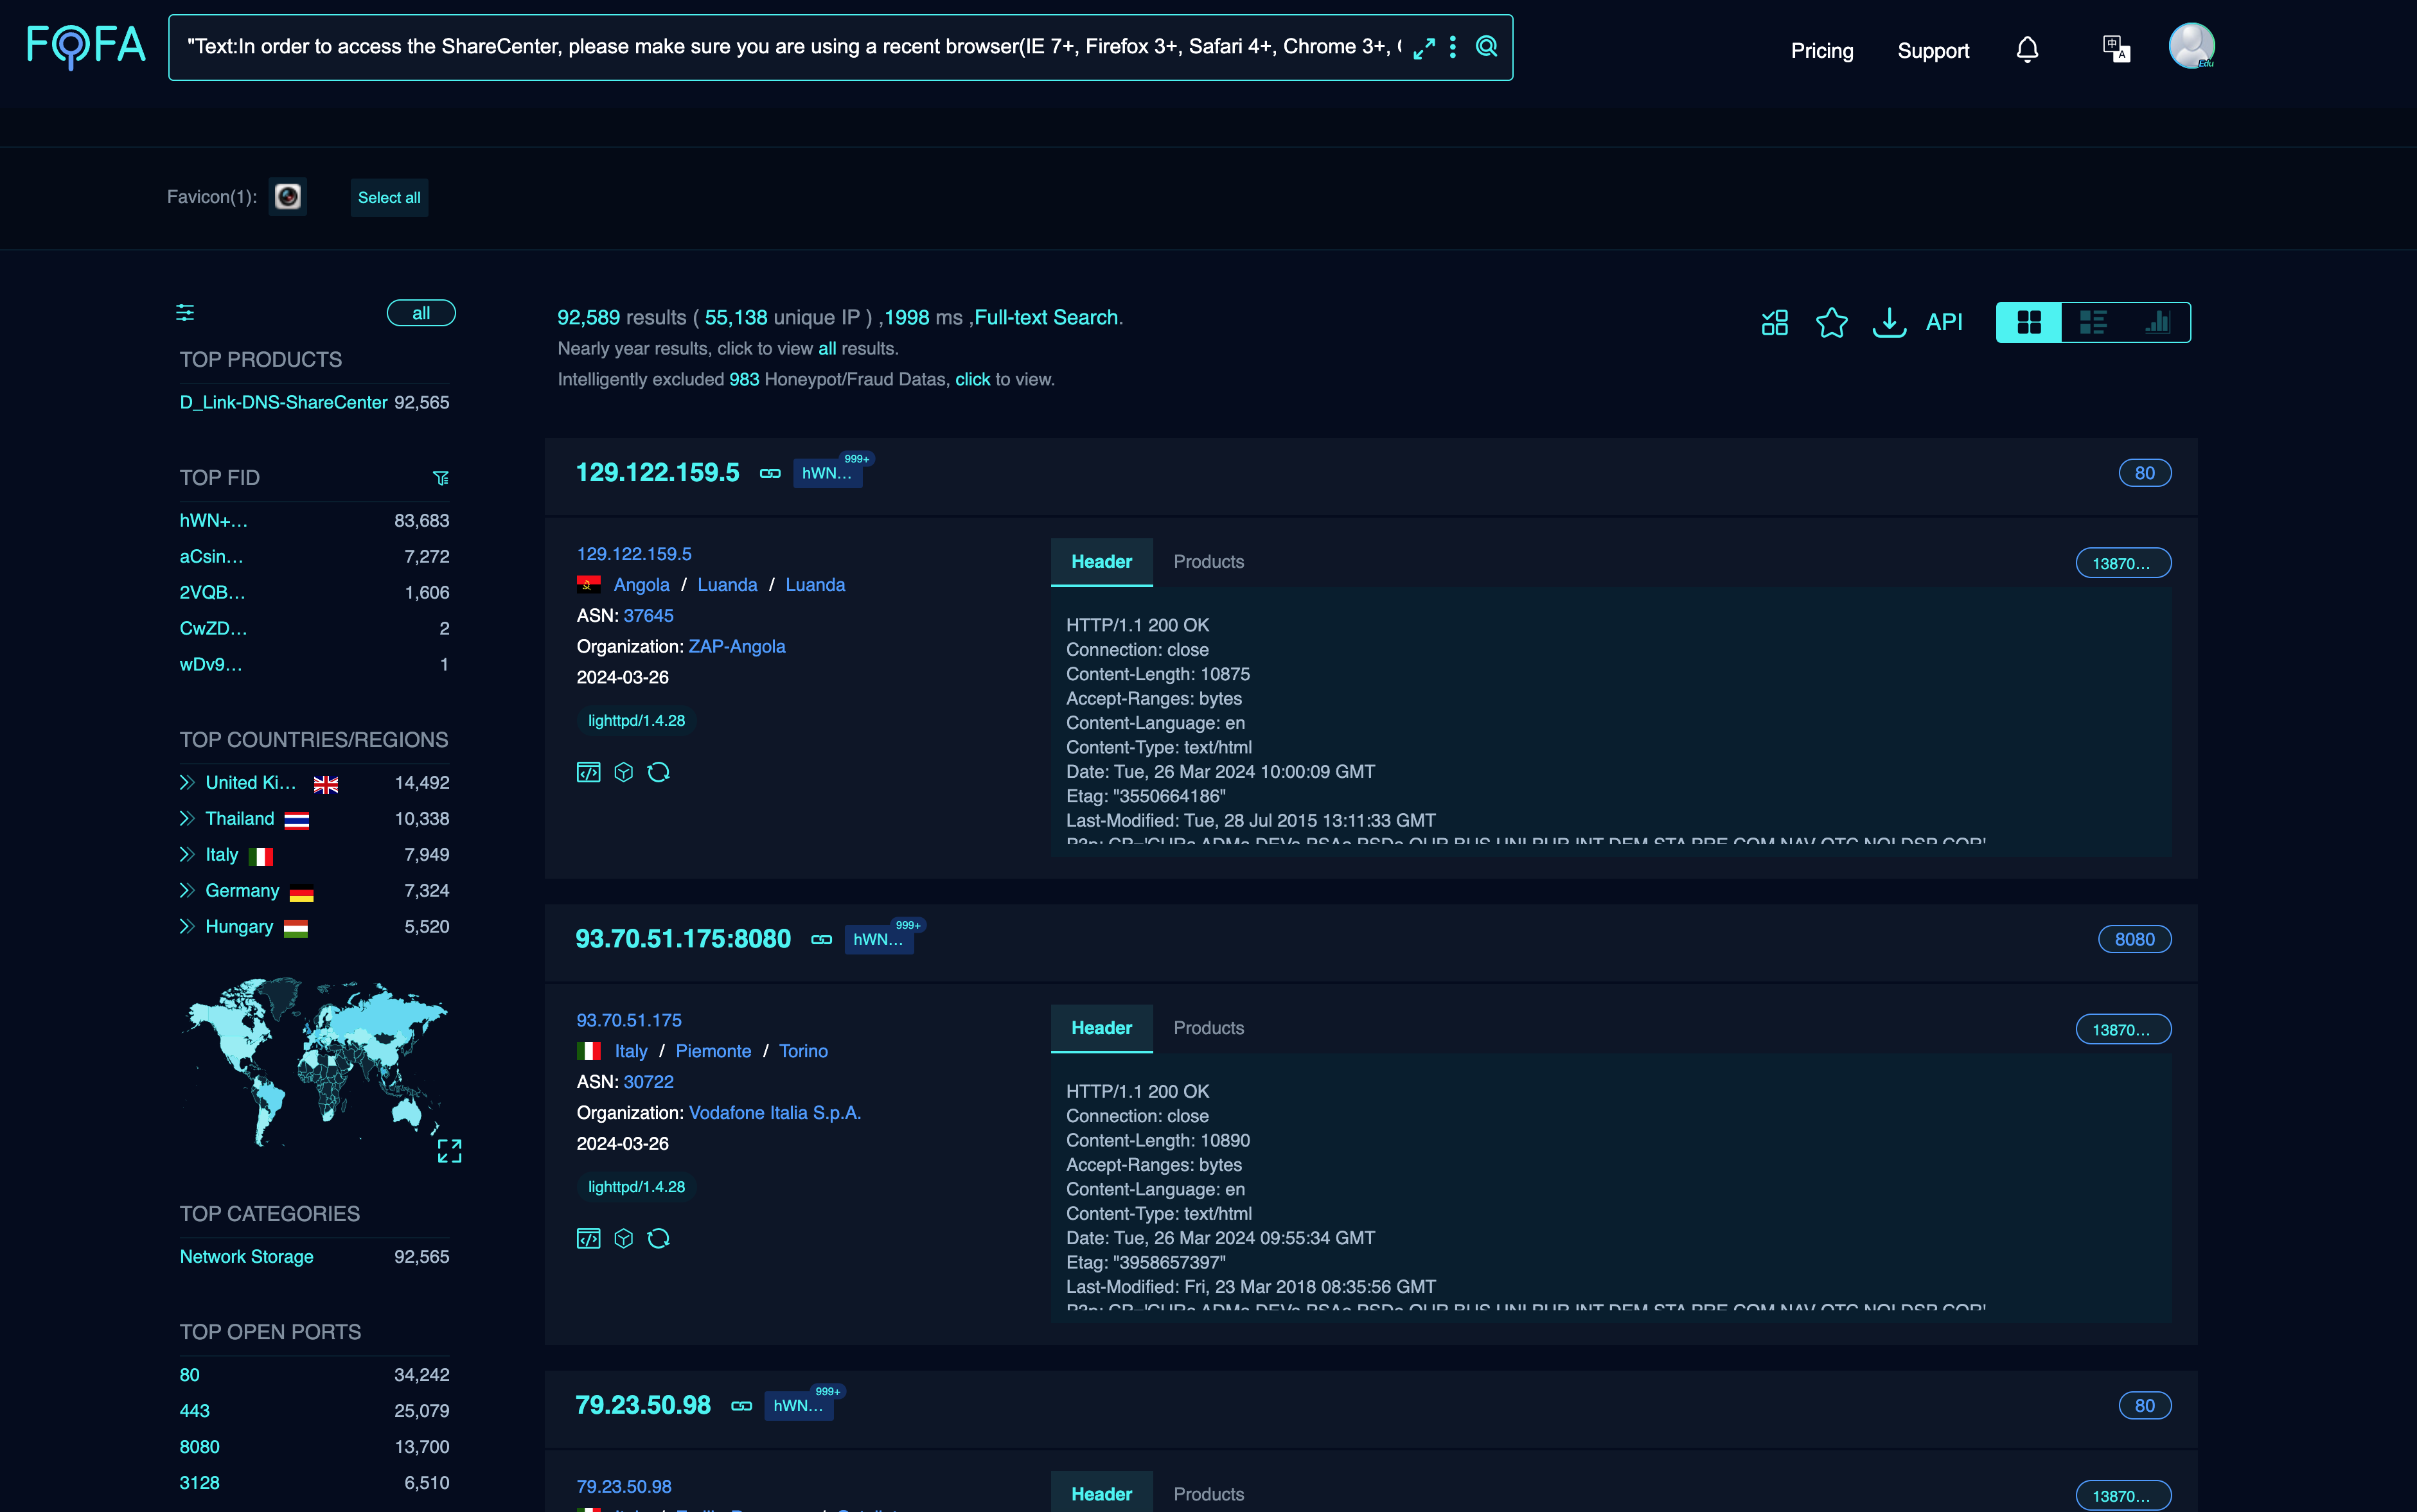 netsecfish/dlink
Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers